prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…

Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…

Privilege Escalation Project - Windows / Linux / Mac

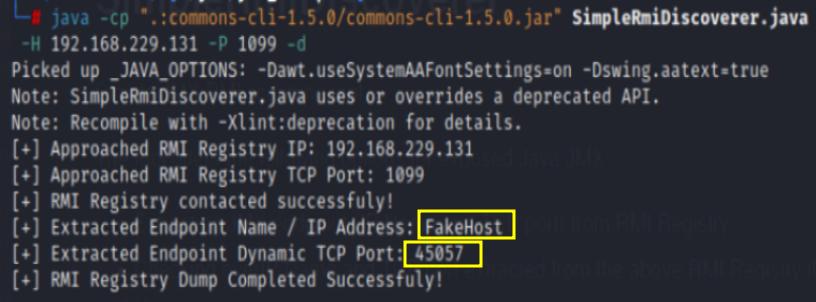
Simple JMX RMI scanning tool

Useful Google Dorks for WebSecurity and Bug Bounty

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

Hunt for security weaknesses in Kubernetes clusters

🛡️ Open-source and cloud-native Web Application Firewall (WAF)

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

The format of various s3 buckets is convert in one format. for bugbounty and security testing.

Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…

Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…

Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)

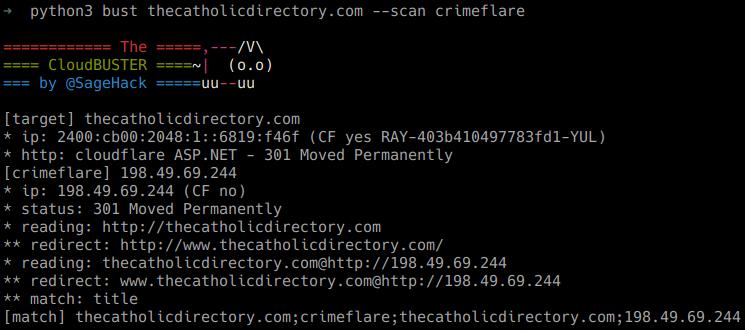
A Cloudflare resolver that works