
CVE-2018-16373
 snappyjack/cve-2018-16373
Frog CMS 0.9.5 has an Upload > vulnerability that can create files via > /admin/?/plugin/file_manager/save
exploitationmisconfigurationpenetration-testing+2
snappyjack/cve-2018-16373Frog CMS 0.9.5 has an Upload > vulnerability that can create files via > /admin/?/plugin/file_manager/save
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
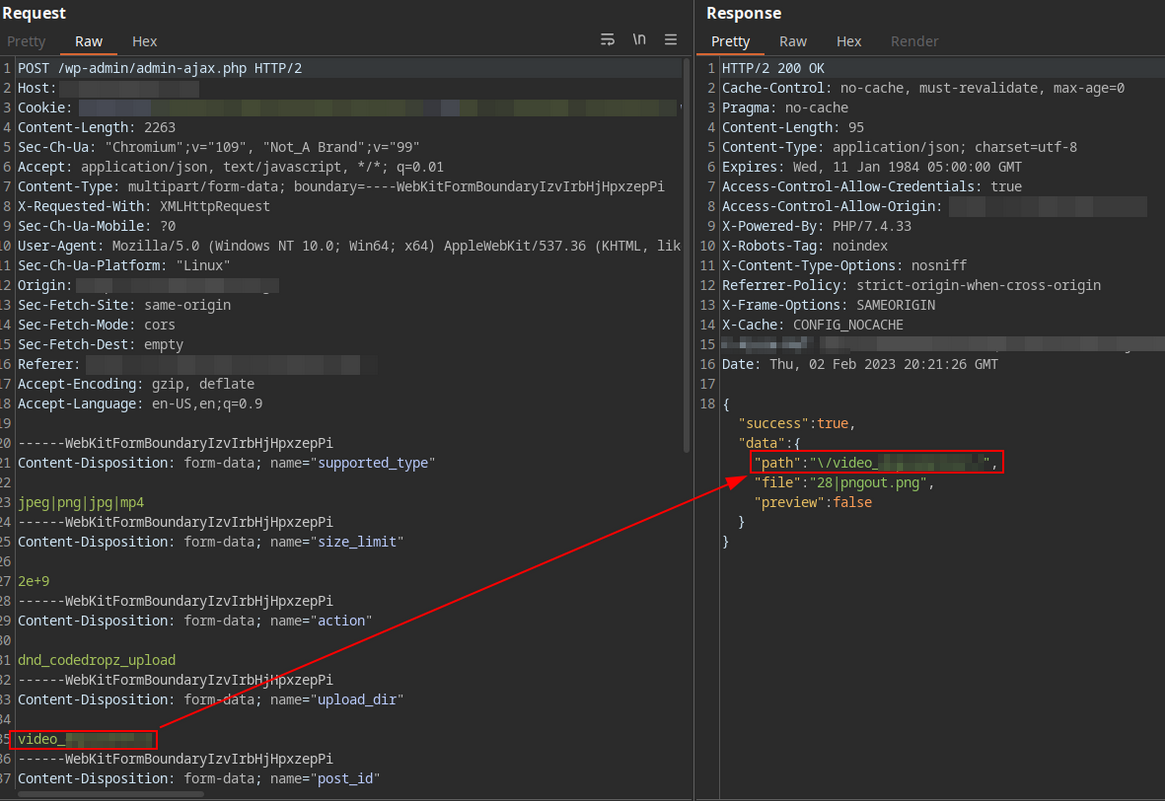 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 trackflaw/cve-2023-25202
CVE-2023-25202: Insecure file upload mechanism