
google-dorks
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
curated-resourcesinformation-gatheringmisconfiguration+5
1.3k17 days ago
proviesec/google-dorksUseful Google Dorks for WebSecurity and Bug Bounty
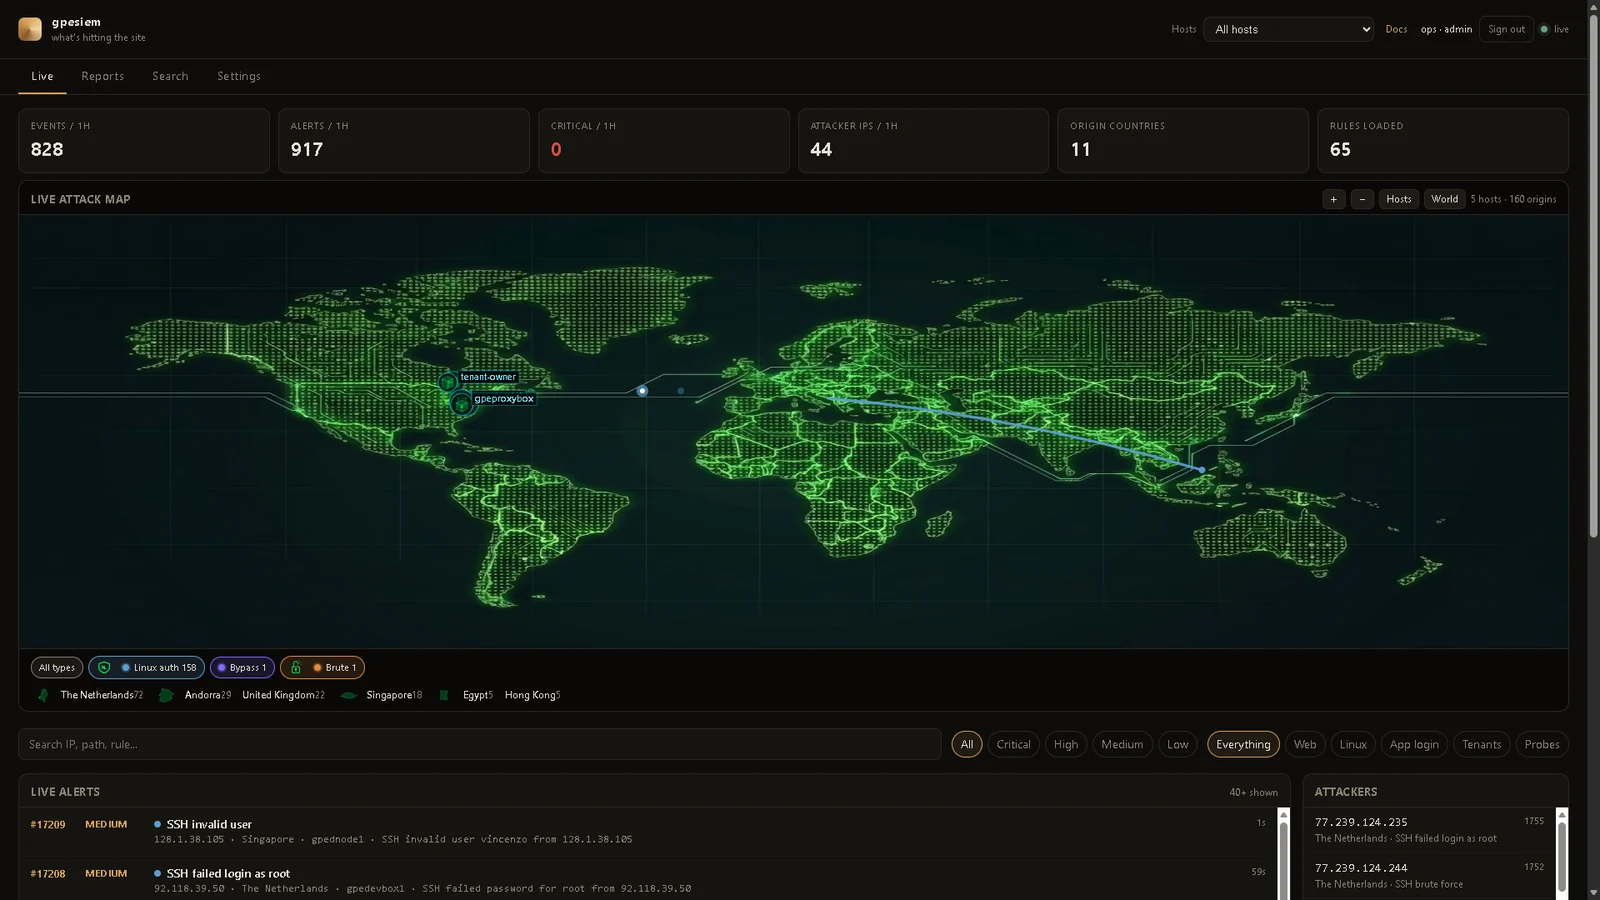 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 hahwul/s3reverse
The format of various s3 buckets is convert in one format. for bugbounty and security testing.
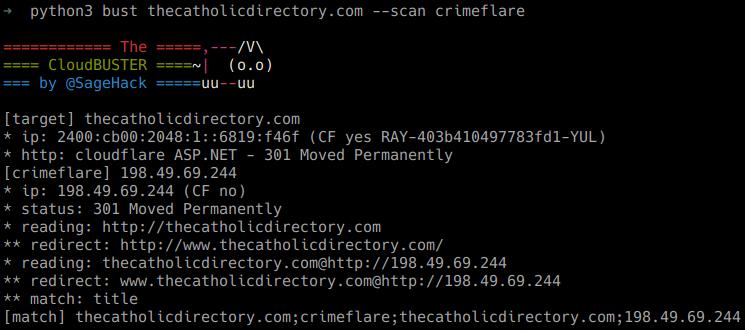 sagehack/cloud-buster
A Cloudflare resolver that works
 stark0de/nginxpwner
Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.
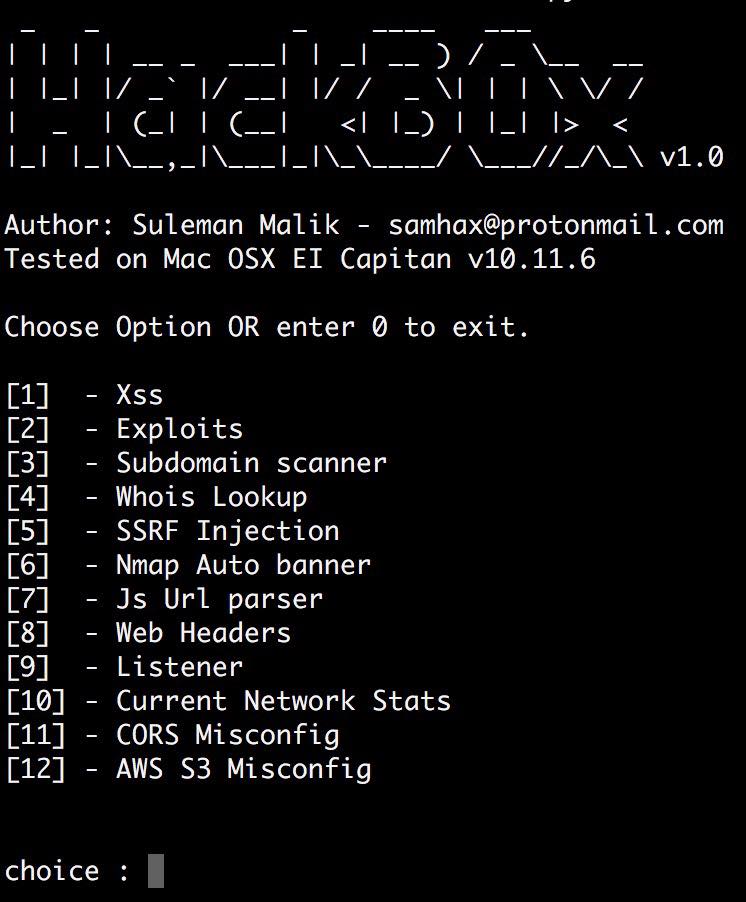 samhaxr/hackbox
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
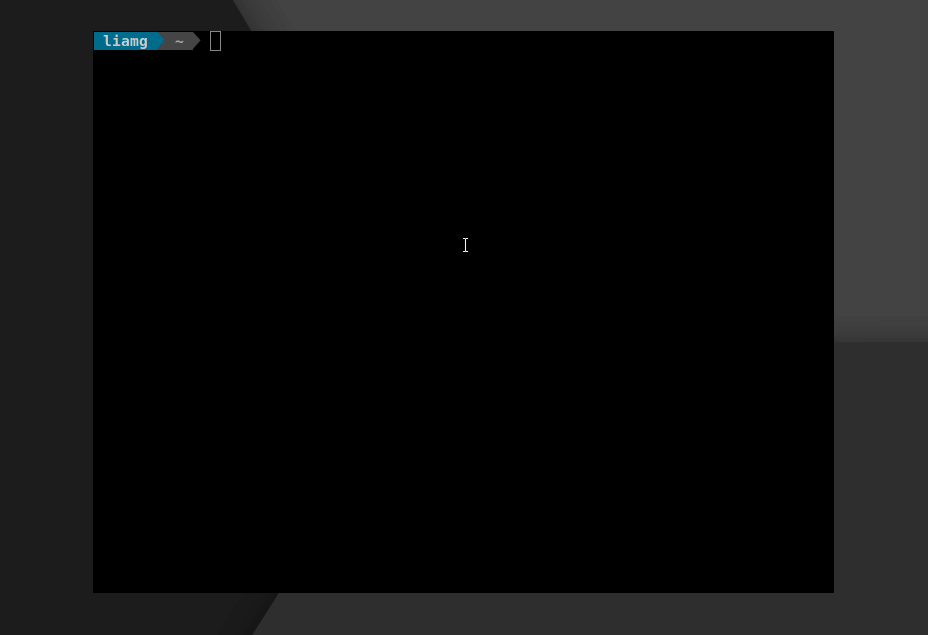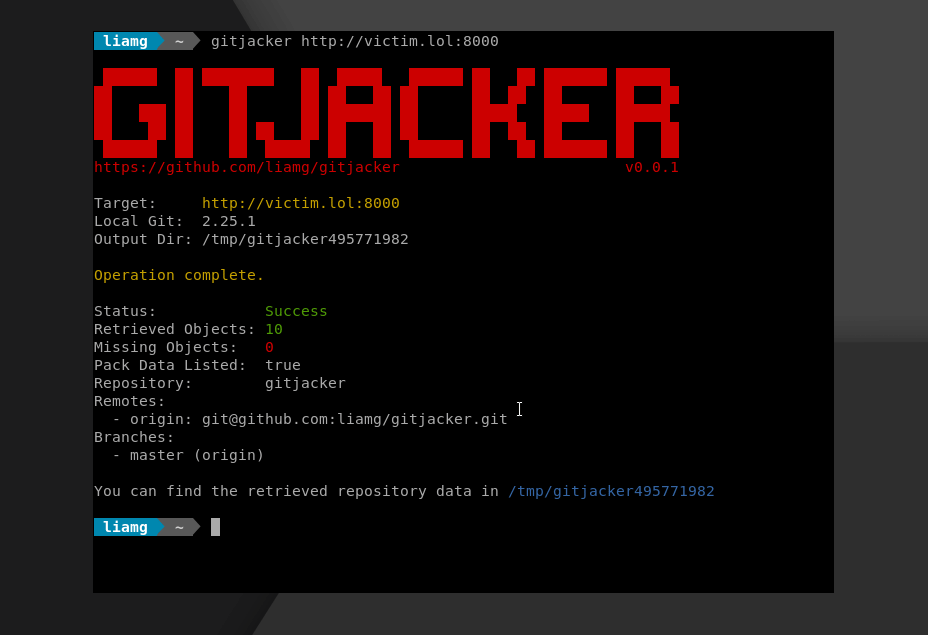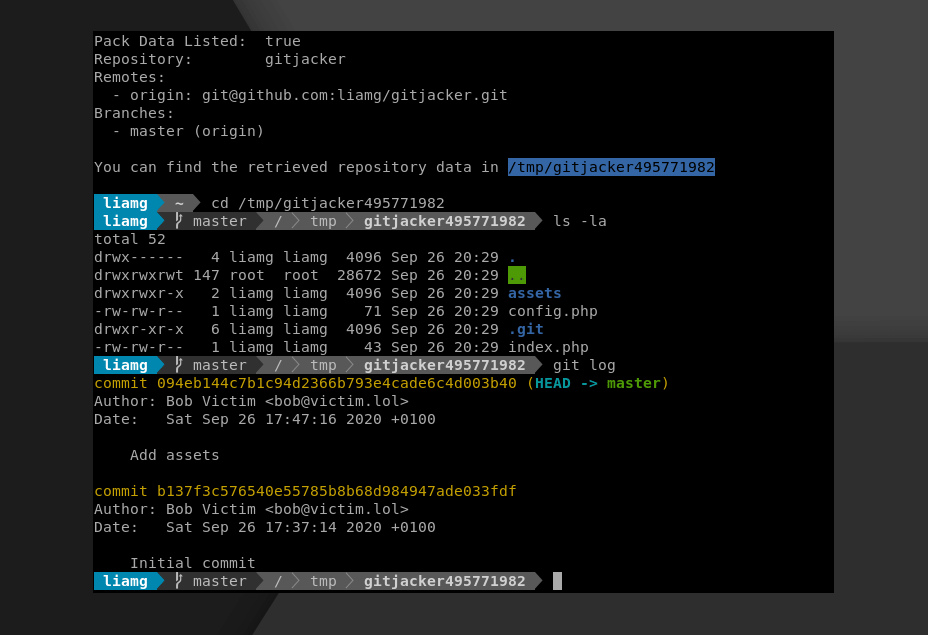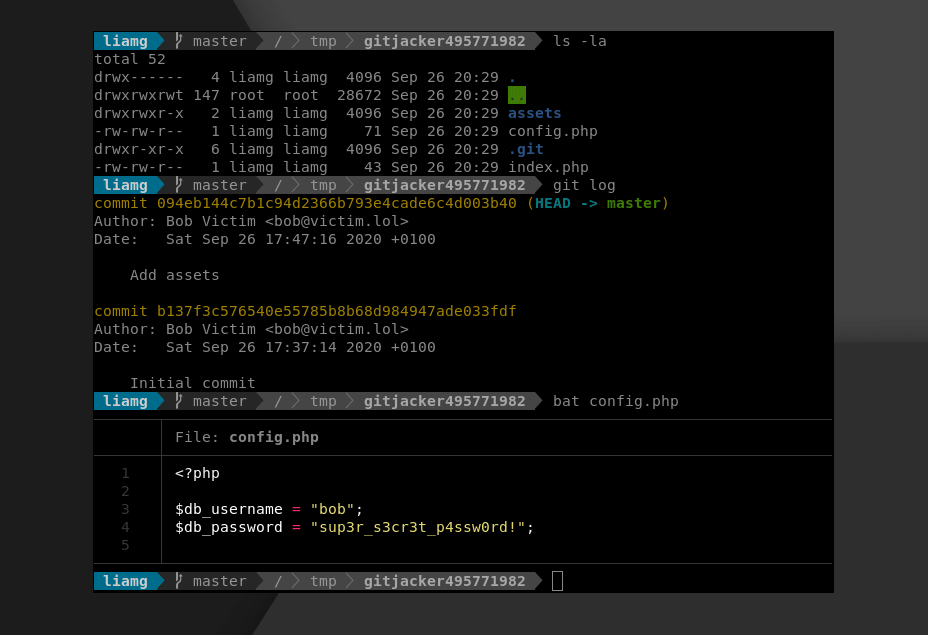 liamg/gitjacker
🔪 :octocat: Leak git repositories from misconfigured websites
 ianxtianxt/mongodb-redis-scan
mongodb-redis匿名扫描脚本,支持mongodb和redis的匿名扫描
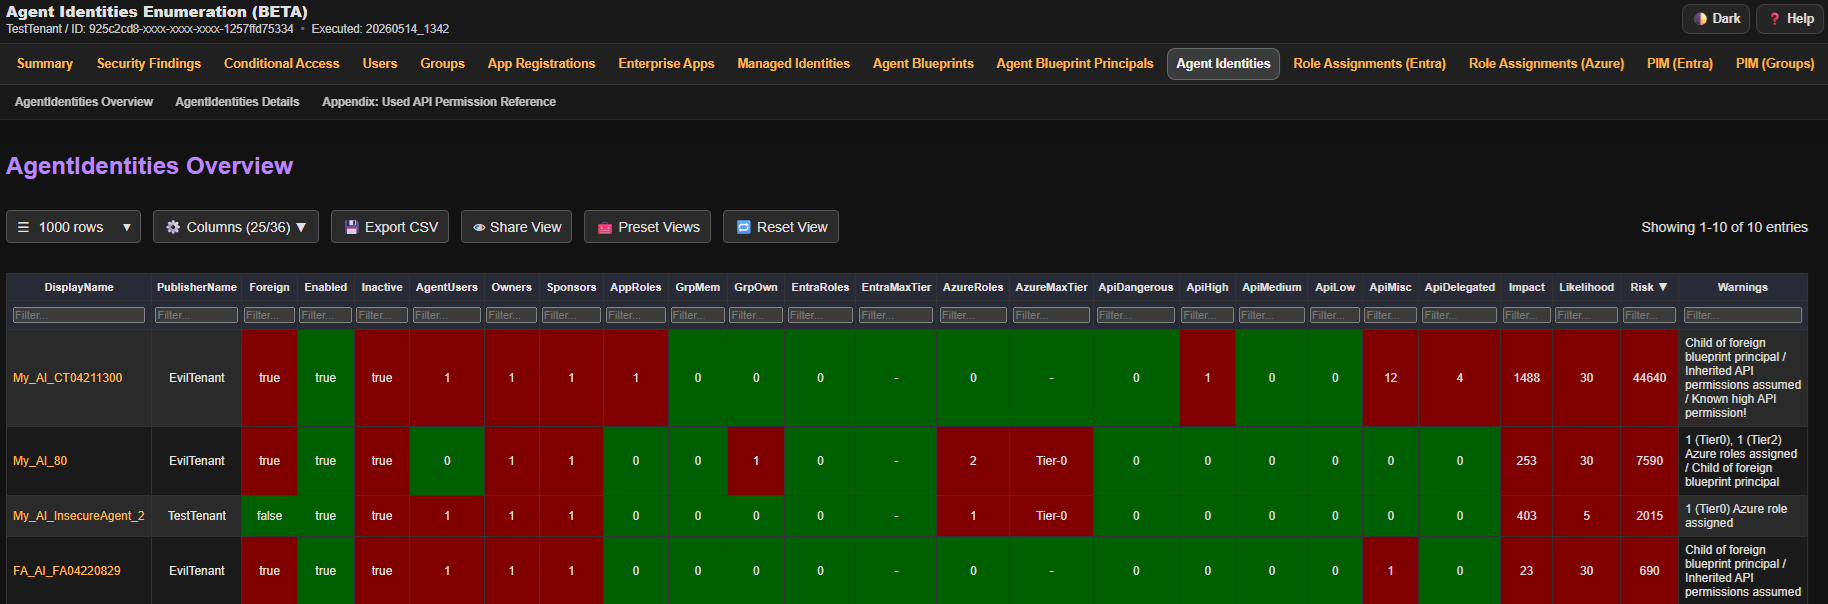 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 jimywork/djangohunter
Tool designed to help identify incorrectly configured Django applications that are exposing sensitive information.
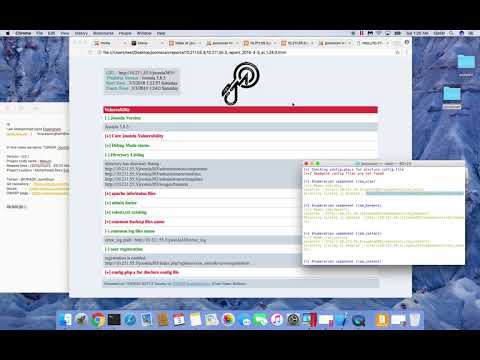 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
 diegoalbuquerque/cve-2024-38063
mitigation script by disabling ipv6 of all interfaces
 woj-ciech/leaklooker
Find open databases - Powered by Binaryedge.io
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 kuangxiaotu/cve-h3c-report
PoC exploit for CVE-2023-5142 targeting H3C GR series routers with an unauthenticated directory traversal vulnerability to extract sensitive…
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…