
audit_couchdb
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
configuration-auditingdatabase-securityinformation-gathering+3
1612 years ago
jhs/audit_couchdbDetect security issues in an Apache CouchDB server
 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 emomeni/simple-ansible-for-cve-2023-20198
Ansible playbook to detect and disable HTTP/HTTPS servers on Cisco IOS XE devices, mitigating CVE-2023-20198 vulnerability with automated…
 iriscouch/audit_couchdb
Detect security issues, large or small, in a CouchDB server
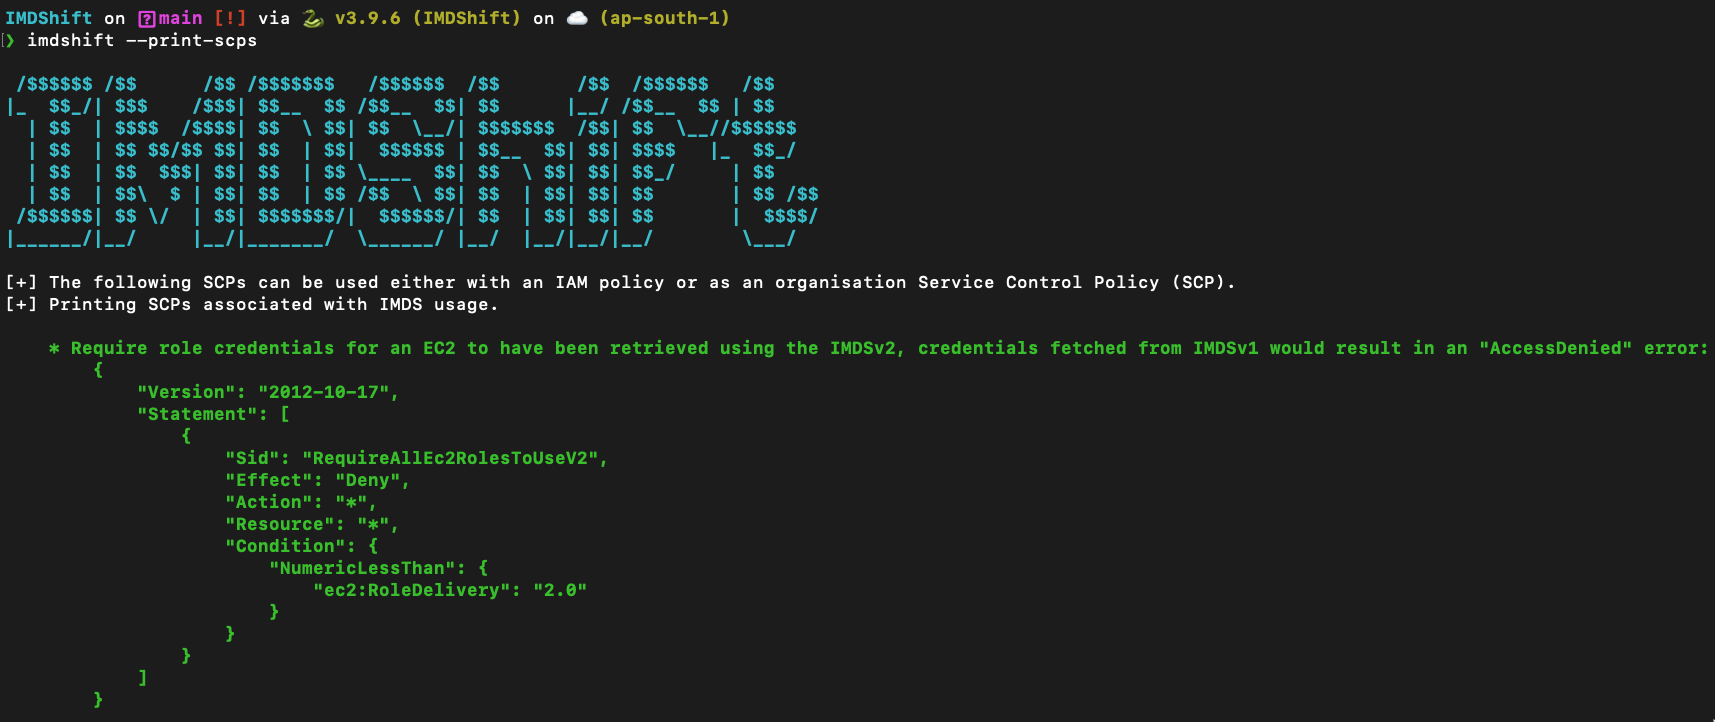 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 olafhartong/mde-auditcheck
MDE relies on some of the Audit settings to be enabled
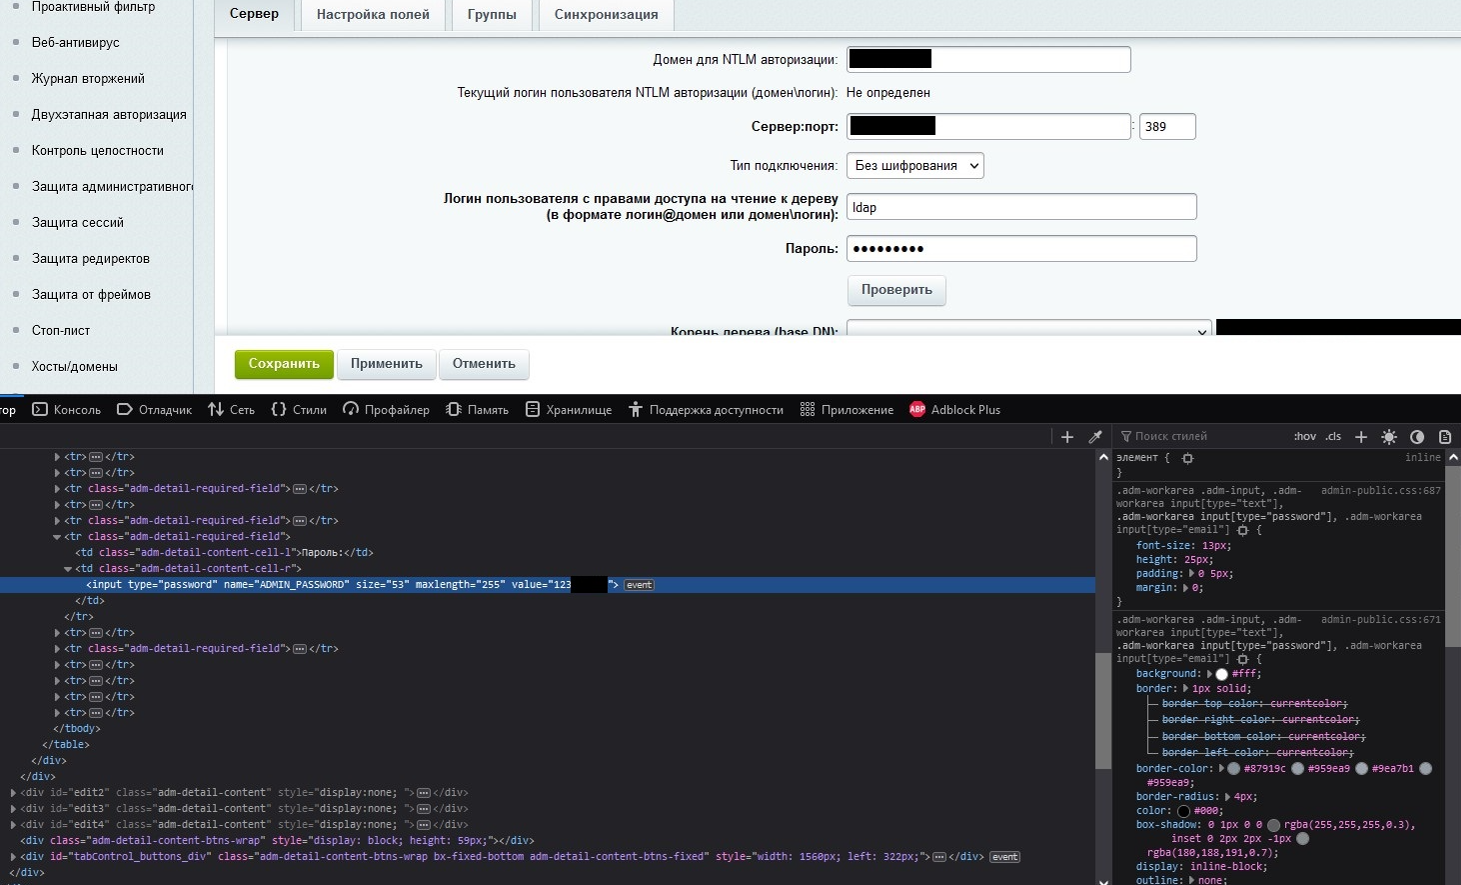 secware-ru/cve-2022-43959
Bitrix Vulnerability CVE-2022-43959
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 immunit/cve-2018-11759
Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…
 fazmin/vcenter-server-workaround-script-cve-2021-44228
Script - Workaround instructions to address CVE-2021-44228 in vCenter Server
 helleflo1312/orchestrated-powershell-for-cve-2023-24932
Automated PowerShell orchestrator for applying Secure Boot mitigations against CVE-2023-24932 (BlackLotus). Handles registry changes, reboots,…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.