
lynis
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
configuration-auditingdatabase-securitydefensive-tools+5
16.4k
cisofy/lynisAgentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…

 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 snoopopsec/vulnerability-cve-2013-3900
Remediation for CVE-2013-3900
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
 indoushka/context-aware-offensive-intelligence
Research framework redefining post-exploitation through decision intelligence.
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
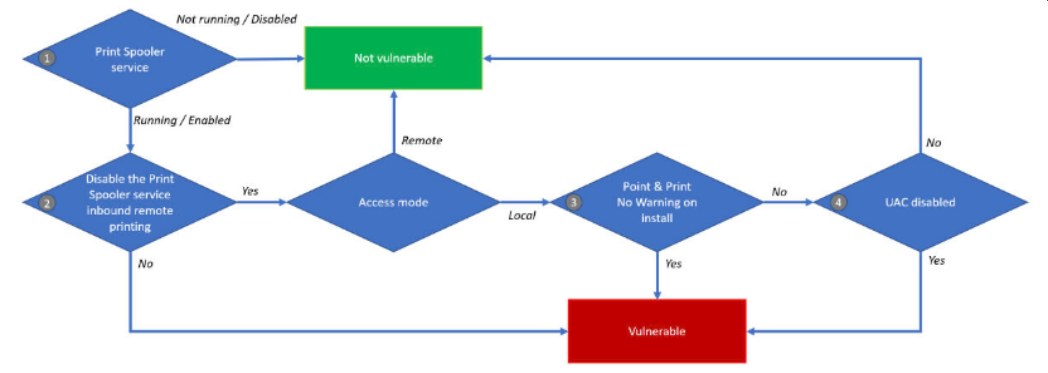 eutectico/printnightmare
Fix for PrintNightmare CVE-2021-34527
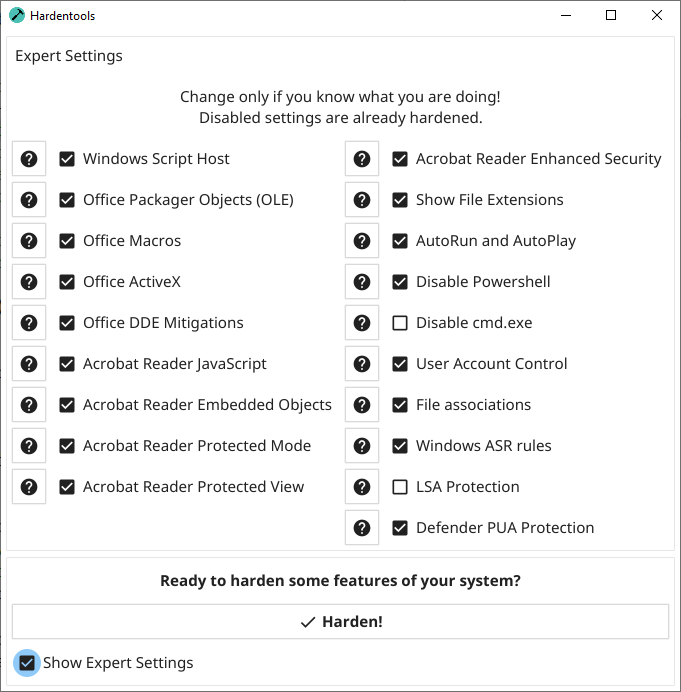 hardentools/hardentools
Hardentools simply reduces the attack surface on Microsoft Windows computers by disabling low-hanging fruit risky features.
 jackdpeterson/imagick_secure_puppet
Puppet module to harden ImageMagick policy.xml against CVE-2016-3714 by restricting dangerous image processing directives.
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…