

linuxprivchecker
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
ctfeducationinformation-gathering+3
1.8k
sleventyeleven/linuxprivcheckerLocal Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 snappyjack/cve-2018-16373
Frog CMS 0.9.5 has an Upload > vulnerability that can create files via > /admin/?/plugin/file_manager/save
 kuangxiaotu/cve-h3c-report
PoC exploit for CVE-2023-5142 targeting H3C GR series routers with an unauthenticated directory traversal vulnerability to extract sensitive…
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
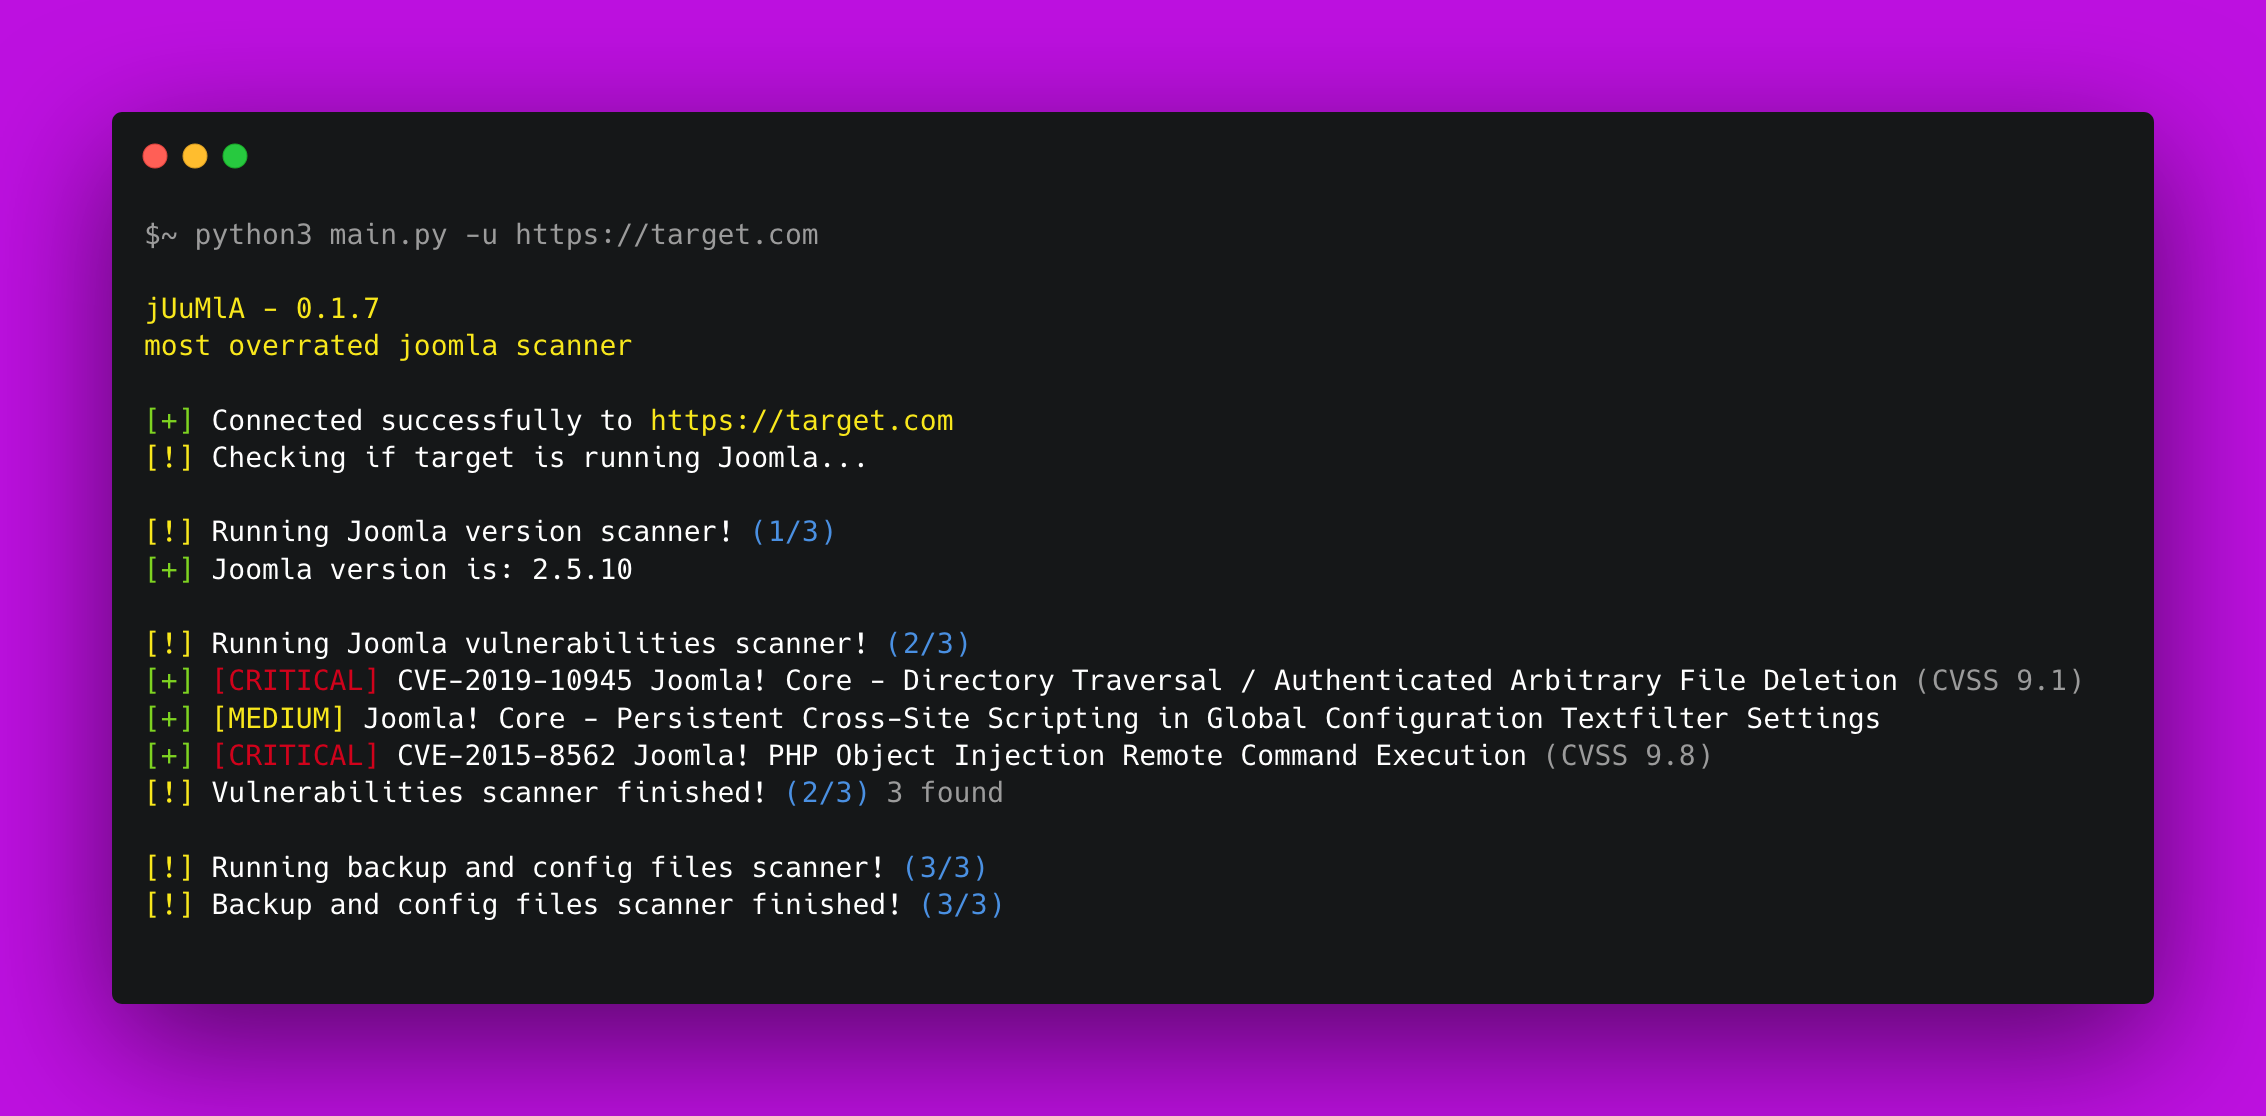 0xdsm/juumla
🦁 Python project to identify and scan for vulnerabilities related to the Joomla CMS project. It scans for common misconfigurations and public…
 badsectorlabs/sccm-http-looter
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) shares via HTTP(s)
 nccgroup/s3_objects_check
Whitebox evaluation of effective S3 object permissions, to identify publicly accessible files.
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 realityone/cve-2026-42945-scan
Scan your NGINX configuration to determine whether it is affected by CVE-2026-42945.
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]
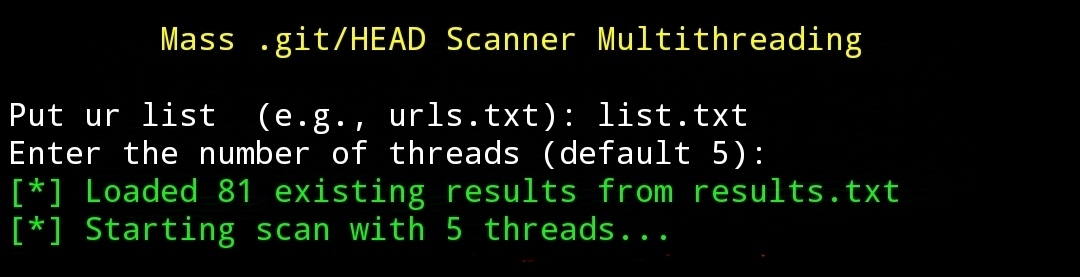 jenderal92/git-scan
This tool is designed to scan and identify whether a website has an exposed ".git" directory, which may contain sensitive information such as source…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 jenderal92/git-dump
This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)