
milvus-auth-audit
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
api-security-testingauthentication-authorizationdatabase-security+4
qianlijaingshan/milvus-auth-auditMilvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
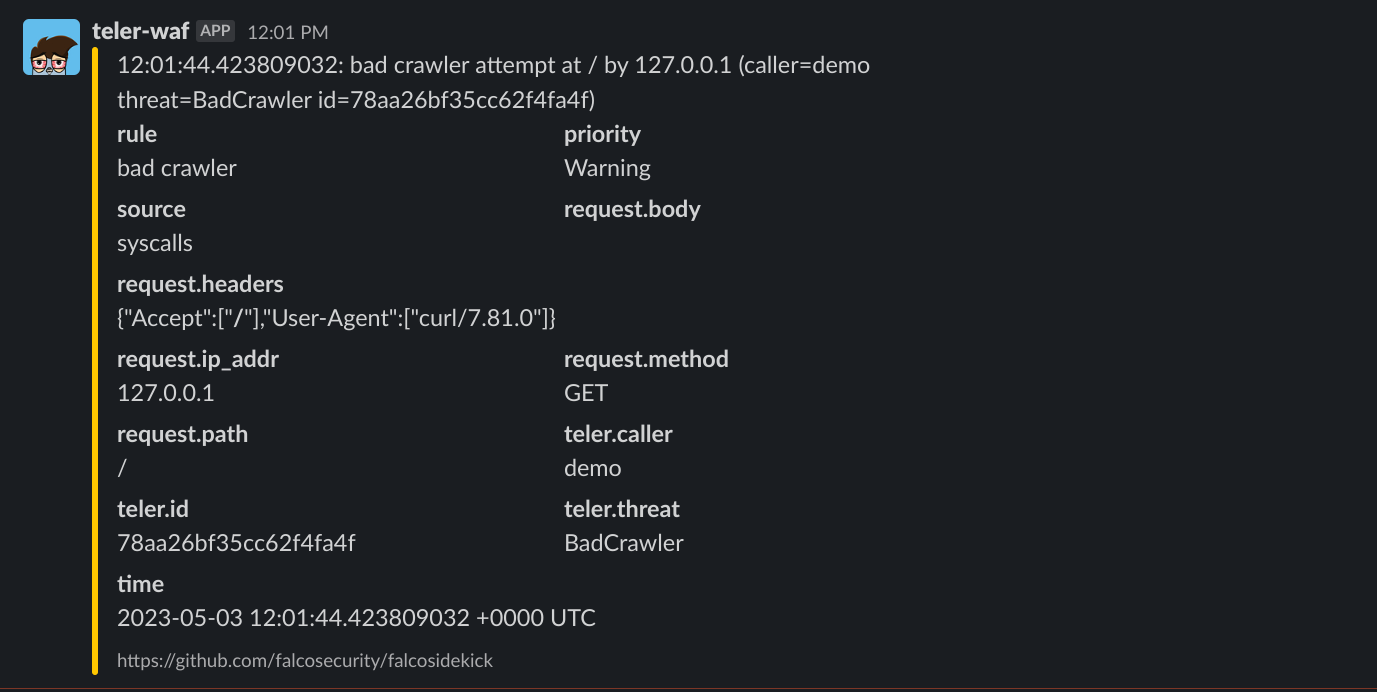 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 lstudlo/nextjs-cve-demo
演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。
 xuwu-xuwu/cve-2026-68004
Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
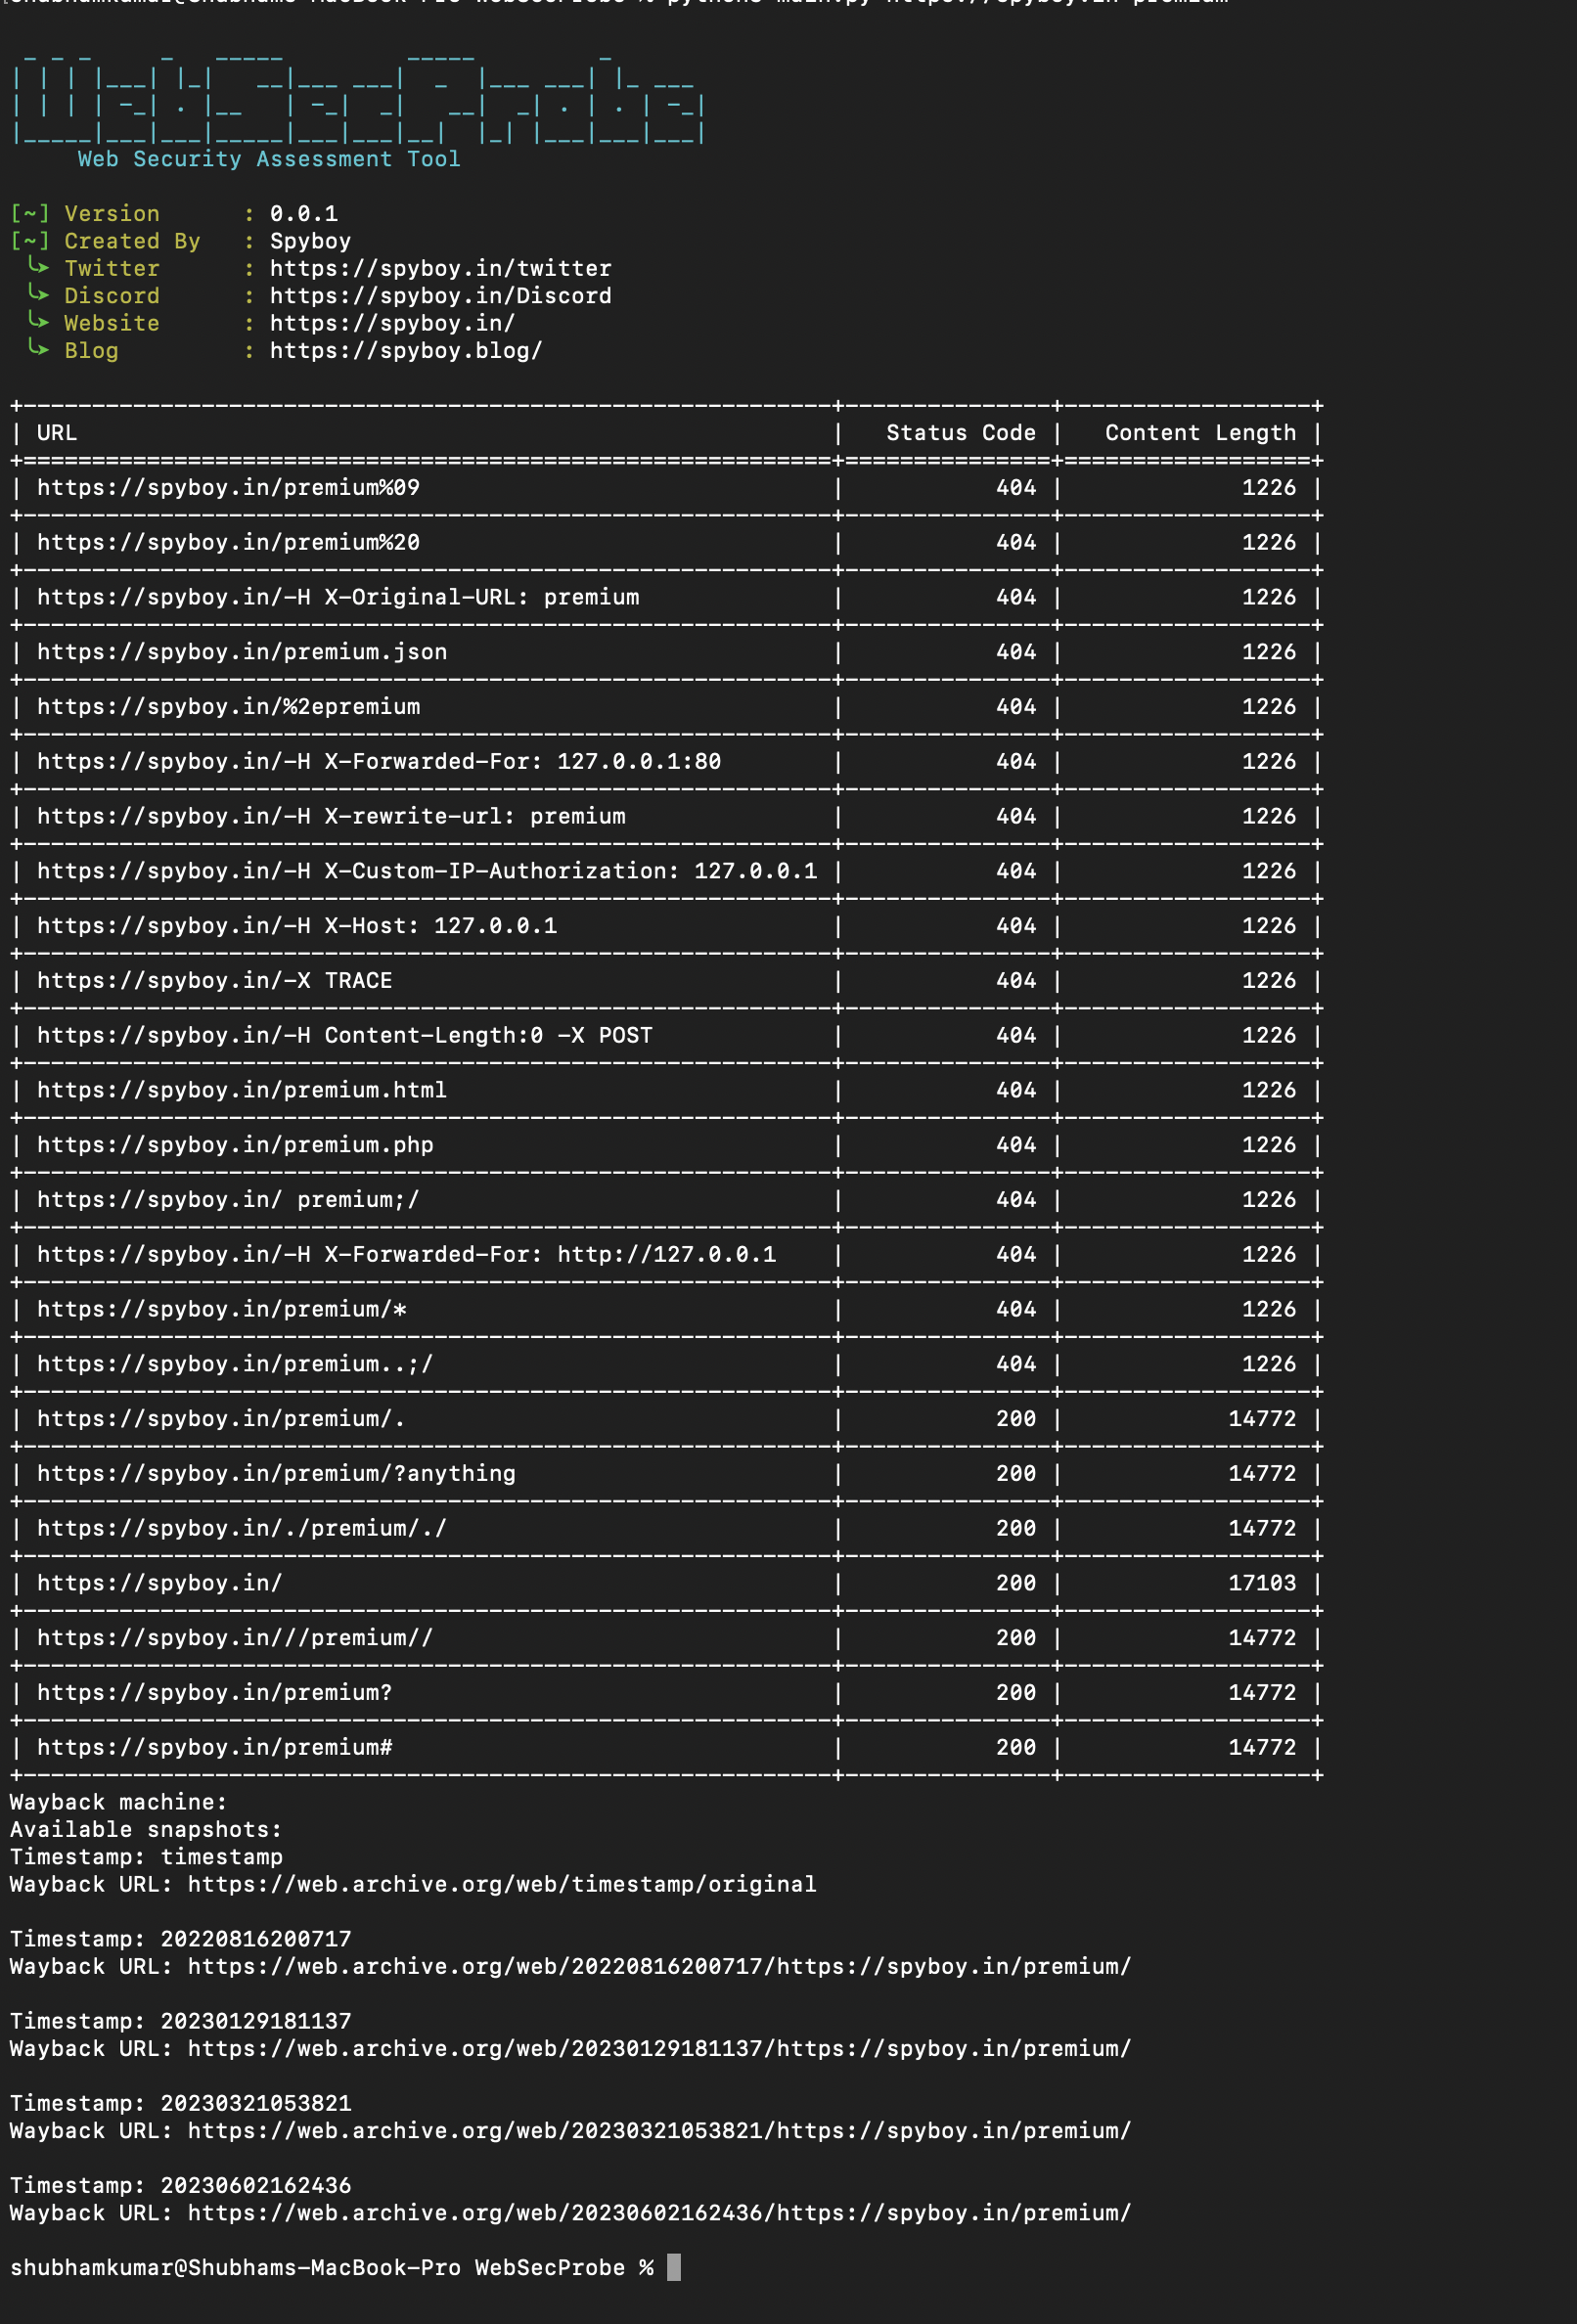 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 0xdevrel/easyscan
Python-based web security scanner that analyzes HTTP headers, SSL/TLS, DNS records, and common misconfigurations to generate a scored security report…
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
 friparia/nginx_rift_scan_cve_2026_42945
Nginx Rewrite CVE Scan(CVE-2026-42945 nginx-rift CVE-2026-9256)
 caffeinated-labs/cve-2023-36643
Proof-of-concept for CVE-2023-36643: an incorrect access control vulnerability in ITB-GmbH TradePro v9.5 that allows remote attackers to enumerate…
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 yousseflahouifi/dbdtct
Python-based scanner that detects debug mode misconfigurations in web applications using multiple HTTP methods and fingerprinting techniques to…
 niandy/nginx-patch
nginx 1.15.10 patch against cve-2021-23017 (ingress version)
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths