
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
truegaze preview

truegaze

GitHubnightwatchcybersecurity/truegaze

Static analysis tool for Android/iOS apps focusing on security issues outside the source code

android-securityios-securitymisconfiguration+3
132
5 years ago
s3reverse preview

s3reverse

GitHubhahwul/s3reverse

The format of various s3 buckets is convert in one format. for bugbounty and security testing.
cloud-securityinformation-gatheringmisconfiguration+1
913 years ago
CVE-2018-16373 preview

CVE-2018-16373

GitHubsnappyjack/cve-2018-16373

Frog CMS 0.9.5 has an Upload > vulnerability that can create files via > /admin/?/plugin/file_manager/save

exploitationmisconfigurationpenetration-testing+2
8 years ago
CVE-2026-37071 preview

CVE-2026-37071

GitHubjfs-jfs/cve-2026-37071

Proof-of-concept exploit for CVE-2026-37071: arbitrary file rename in Veno File Manager 4.4.9 enabling privilege escalation to super administrator…
exploitationmisconfigurationprivilege-escalation+2
3 months ago
CVE-2026-37067 preview

CVE-2026-37067

GitHubjfs-jfs/cve-2026-37067

Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
exploitationinformation-gatheringmisconfiguration+2
3 months ago
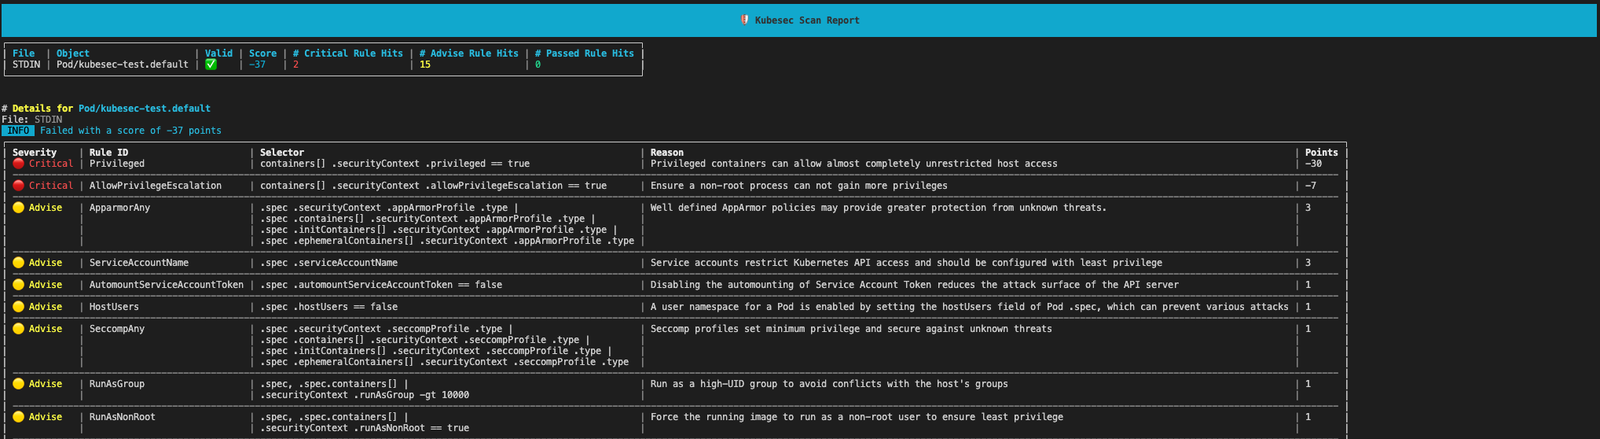
kubesec preview

kubesec

GitHubcontrolplaneio/kubesec

Security risk analysis for Kubernetes resources
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
1.5k3 months ago
CVE-2021-27187 preview

CVE-2021-27187

GitHubjet-pentest/cve-2021-27187

Proof-of-concept for CVE-2021-27187: cleartext credential storage in FX Aggregator terminal client login.sav file, enabling local credential theft…
data-exfiltrationexploitationinformation-gathering+3
5 years ago
mcafee-sitelist-pwd-decryption preview

mcafee-sitelist-pwd-decryption

GitHubfunoverip/mcafee-sitelist-pwd-decryption

Password decryption tool for the McAfee SiteList.xml file
encryption-decryption-toolsmisconfigurationpassword-attacks+1
1742 years ago
CVE-2017-9798 preview
Archived

CVE-2017-9798

GitHubnitrado/cve-2017-9798

Checks a shared hosting environment for CVE-2017-9798

misconfigurationscripting-automationvulnerability-analysis+1
38 years ago
CVE-2025-61686-PoC preview

CVE-2025-61686-PoC

GitHubboroeurnprach/cve-2025-61686-poc

React Router's createFileSessionStorage() in certain versions allows unsigned cookies to be manipulated, enabling file system access outside the…
exploitationmisconfigurationvulnerability-analysis+1
7 months ago
vibegate preview

vibegate

GitHubthemiddleblue/vibegate

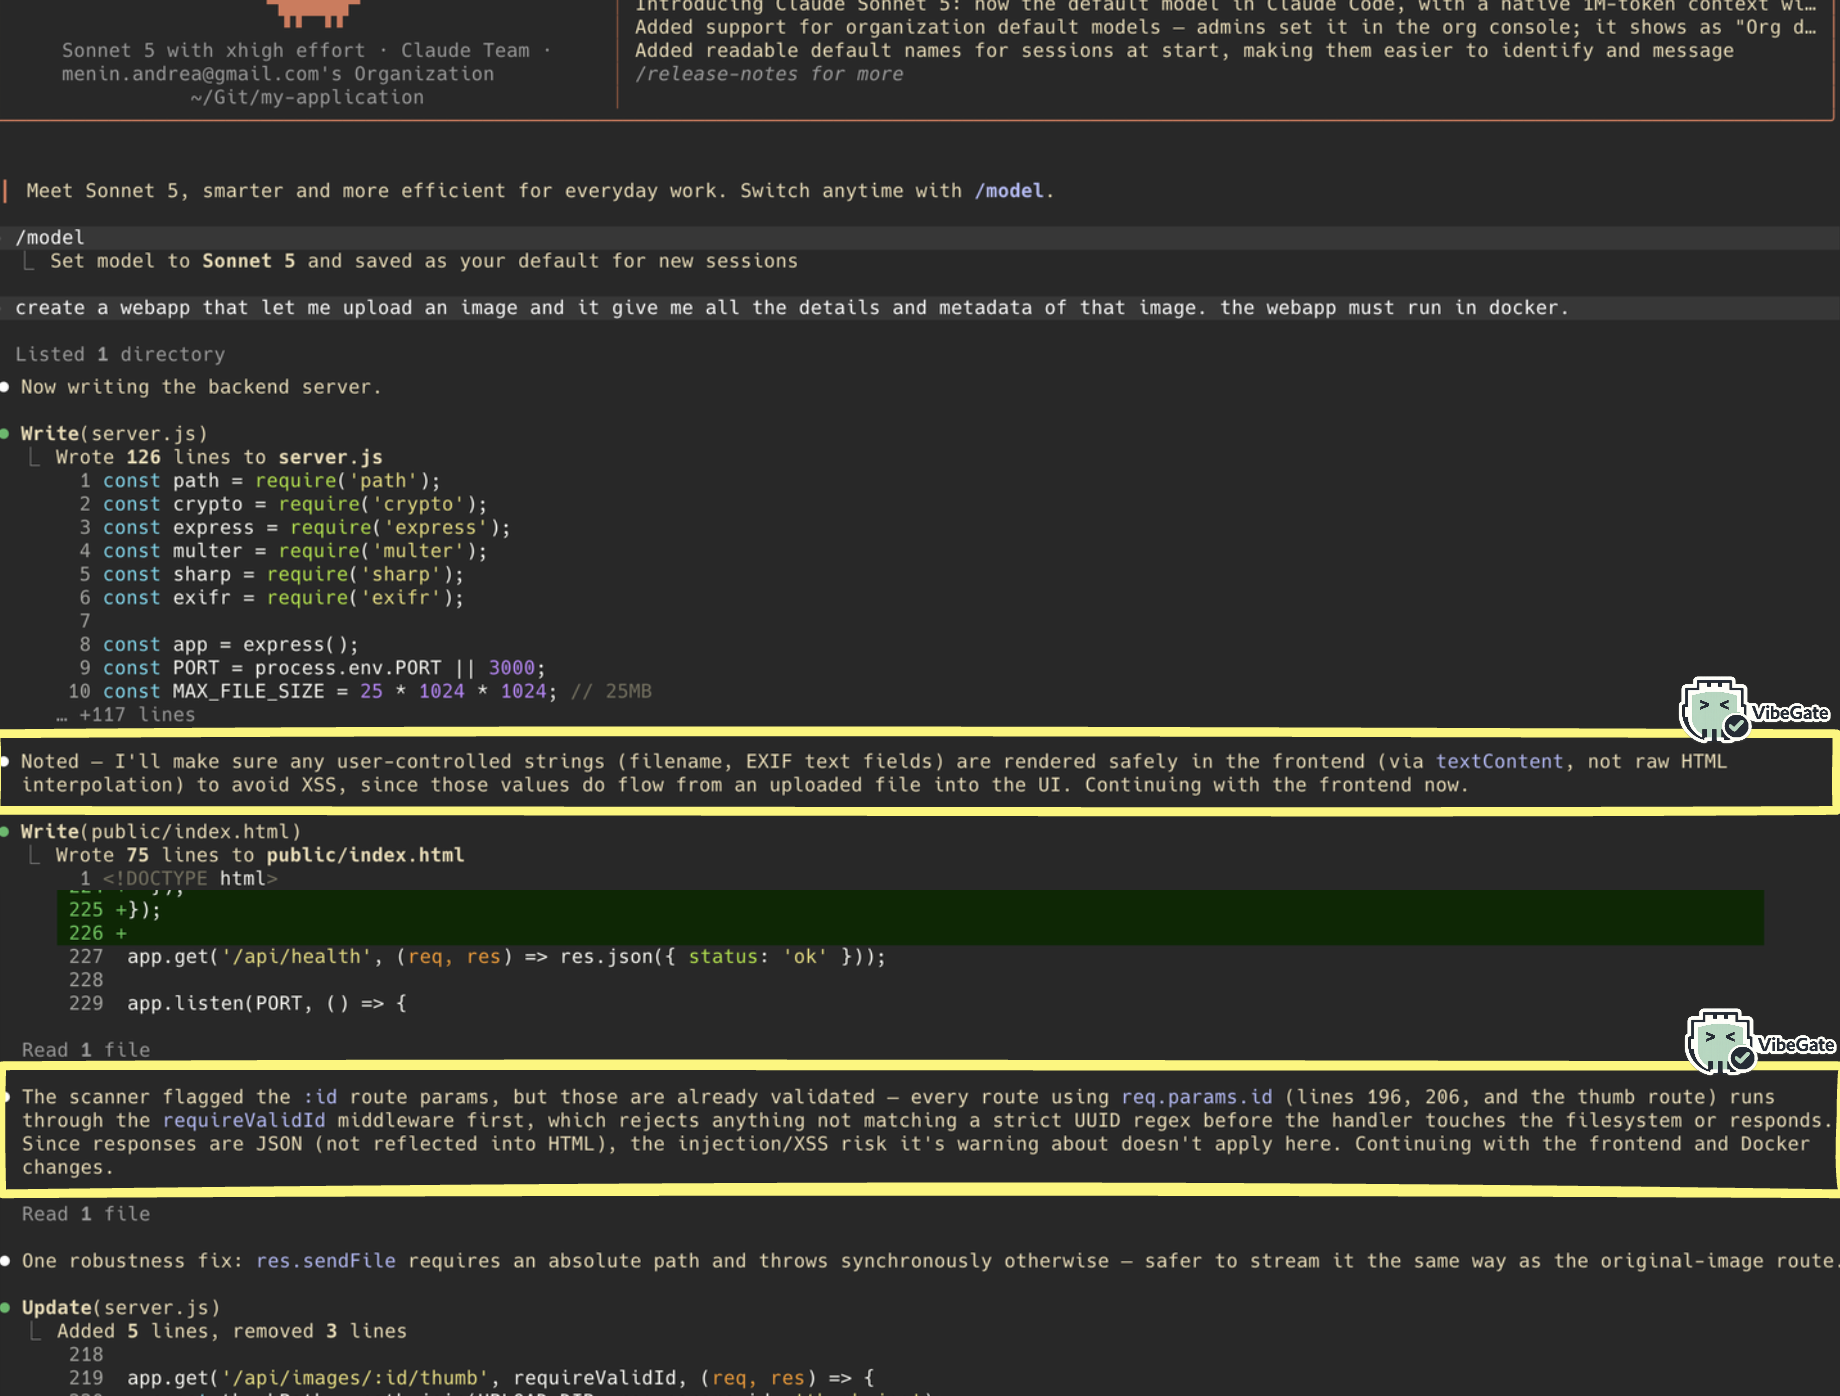
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
ai-securitycode-analysisdevsecops+5
82 months ago
behat-config-leaks preview

behat-config-leaks

GitHubcappricio-securities/behat-config-leaks

BeHat Configuration file leaking
information-gatheringmisconfigurationsecret-detection+3
12 years ago
CVE-2024-39210 preview

CVE-2024-39210

GitHubkrookiesec/cve-2024-39210

Best house rental management system Local file contains vulnerability

information-gatheringmisconfigurationpenetration-testing+2
12 years ago
CVE-2026-31156 preview

CVE-2026-31156

GitHubunicorn-hyh/cve-2026-31156

There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
code-analysisexploitationinformation-gathering+3
4 months ago
CICD-Goat-Vapt-Writeup preview

CICD-Goat-Vapt-Writeup

GitHubdheeraj-jayaswal/cicd-goat-vapt-writeup

Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…

ctfdevsecopseducation+5
112 days ago
phpinfo-files-leaks preview

phpinfo-files-leaks

GitHubcappricio-securities/phpinfo-files-leaks

This tool is used to find php info page
information-gatheringmisconfigurationpenetration-testing+4
12 years ago
LeitWacht Agent preview

LeitWacht Agent

GitLableitwacht/leitwacht-agent

eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/

cloud-infrastructure-securitycloud-securitycontainer-security+4
1 month ago
CVE-2024-12252 preview

CVE-2024-12252

GitHubrandomrobbiebf/cve-2024-12252

SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)

authentication-authorizationexploitationmisconfiguration+5
1 year ago
Previous1234Next
