spring-projects__spring-framework_CVE-2022-22965_5-2-19-RELEASE

Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.

Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.

Research framework redefining post-exploitation through decision intelligence.

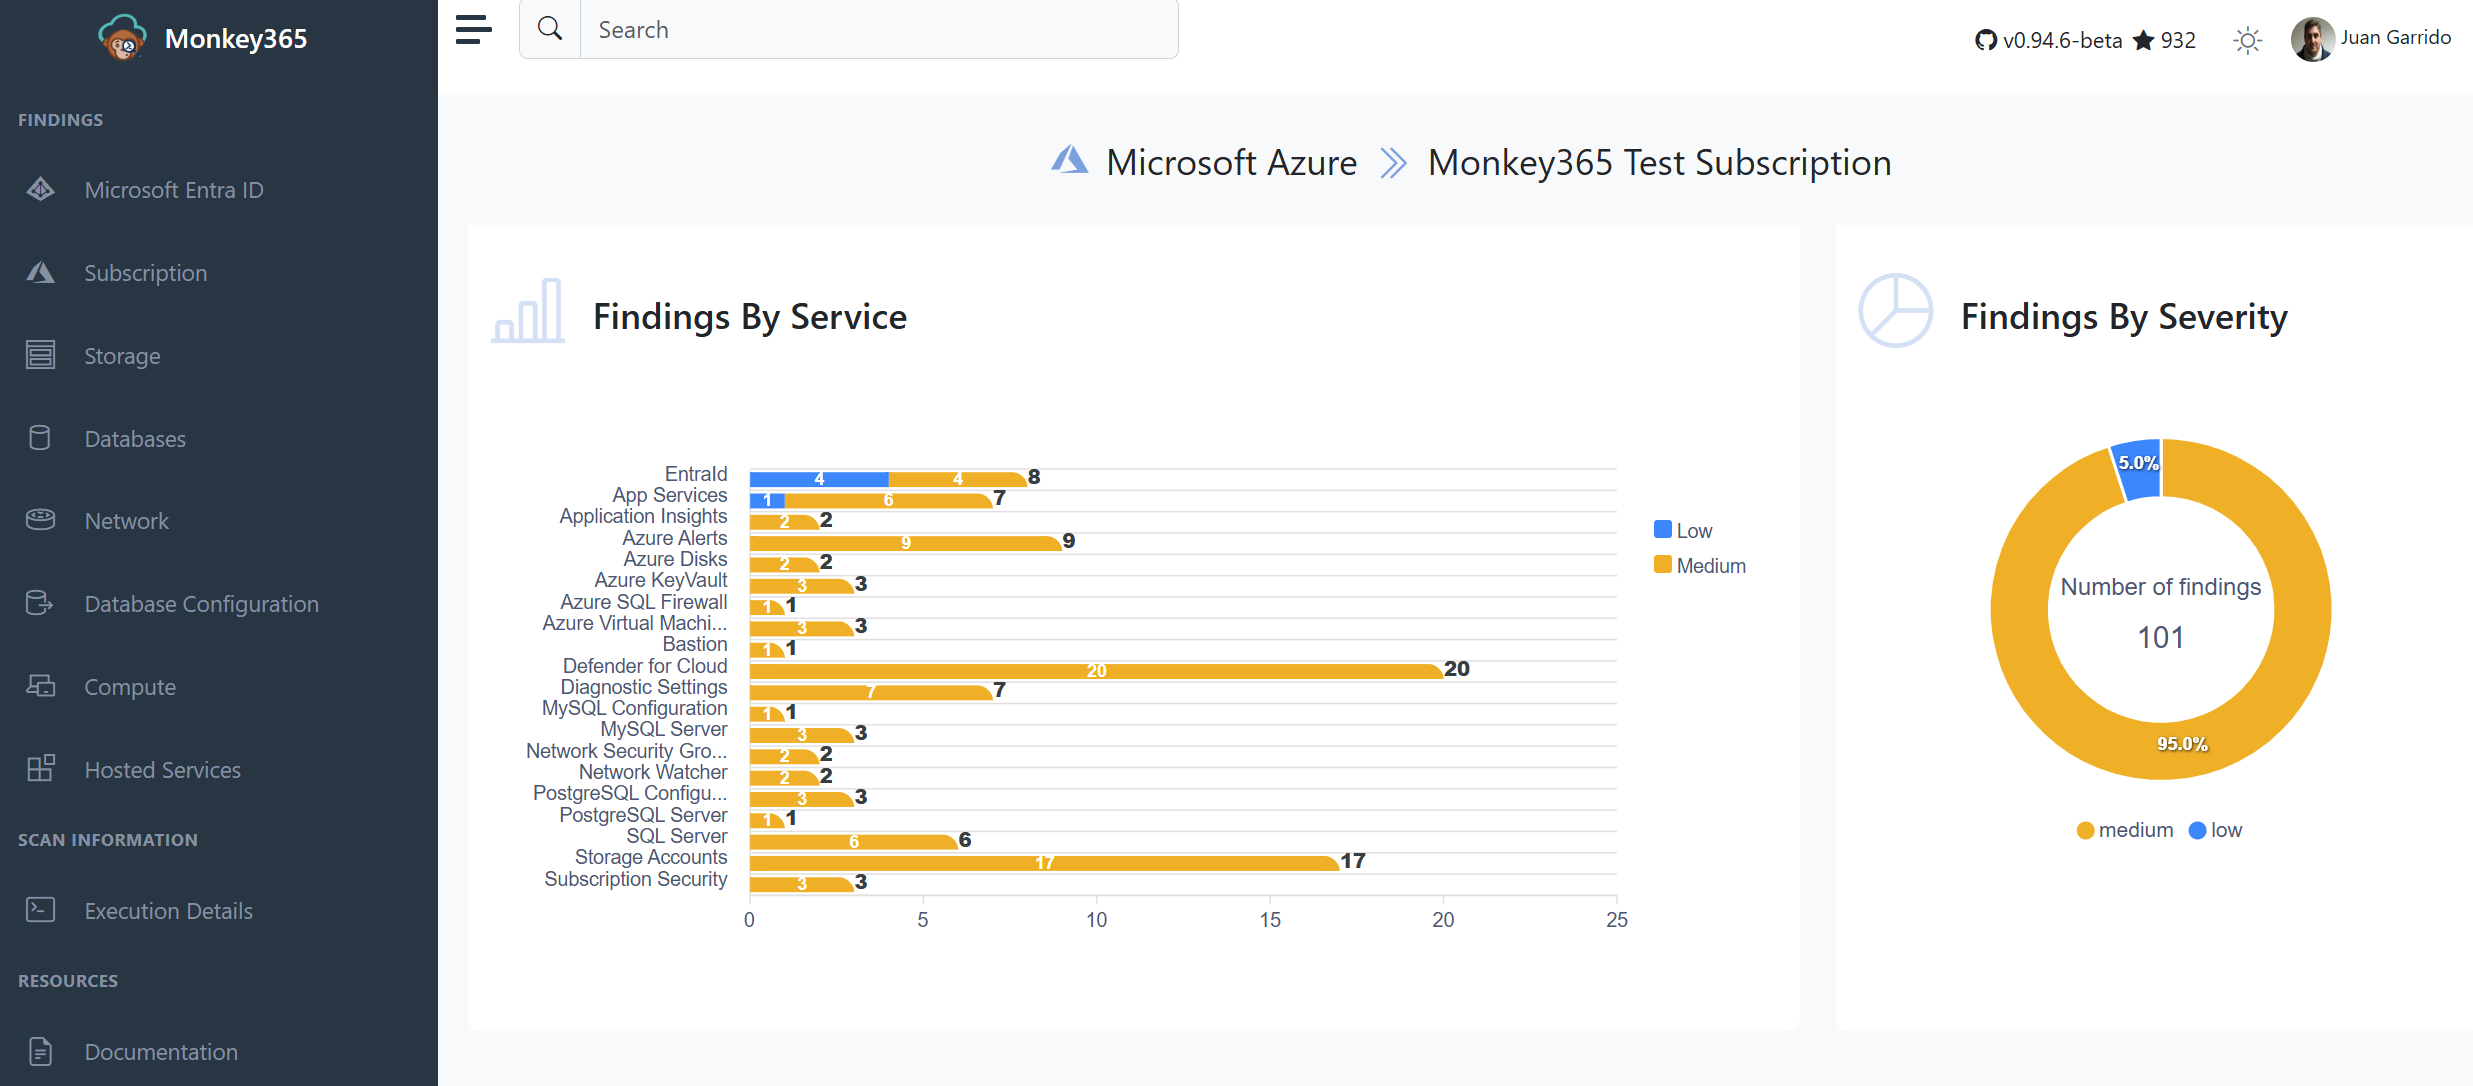
PowerShell-based security assessment framework for Microsoft 365, Azure, and Entra ID. Scans for misconfigurations, CIS benchmark compliance, and…

Security testing framework for repositories and source code

Mogwai Java Management Extensions (JMX) Exploitation Toolkit

CVE-2025-29927 is a critical vulnerability in Next.js, a popular React-based web framework. The flaw exists in how the middleware feature handles…

An RPC attack framework for Blockchain nodes.

F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…

Exploit for CVE-2020-29204 targeting XXL-JOB distributed task scheduling framework, demonstrating remote code execution via unauthenticated access to…

WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.

Technical troubleshooting repository for fixing infinite rendering vulnerability loops and resource exhaustion threats under CVE-2026-23869 cleanly.

Perforce security research and tools - CVE-2026-6043

Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…

Sensitive Data exposure

String MVC Framework Path-Traversal proof of concept. CVE-2014-3625

CVE-2023-28432 POC