
CVE-2024-3094
 yuma-tsushima07/cve-2024-3094
A script to detect if xz is vulnerable - CVE-2024-3094
general-purpose-utilitiesmisconfigurationscripting-automation+2
4
yuma-tsushima07/cve-2024-3094A script to detect if xz is vulnerable - CVE-2024-3094
 first-roman/sprig-mvc-demo-patch
This demo application partially covers the vulnerability CVE-2024-38828
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
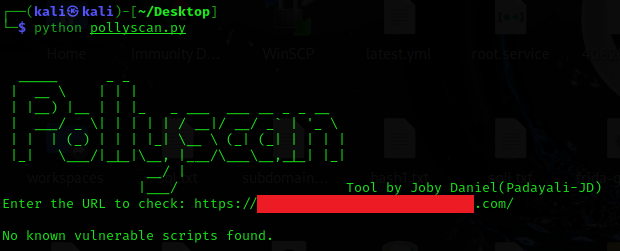 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 g-u-i-d/cve-2024-10449-patch
Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.
 avalahee/pdfjs_disable_eval
CVE-2024-4367 mitigation for Odoo 14.0
 spyata123/cve-2024-12008-information-exposure-vulnerability-in-w3-total-cache
CVE-2024-12008 information exposure vulnerability in W3 Total Cache
 pauloparopp/cve-2024-41110-scan
Python-based scanner that checks Docker hosts for CVE-2024-41110 by detecting vulnerable Docker versions and AuthZ plugin usage.
 helleflo1312/orchestrated-powershell-for-cve-2023-24932
Automated PowerShell orchestrator for applying Secure Boot mitigations against CVE-2023-24932 (BlackLotus). Handles registry changes, reboots,…
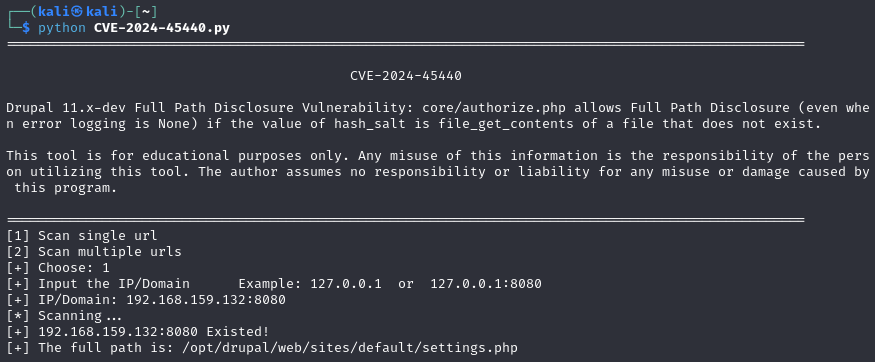 w0r1i0g1ht/cve-2024-45440
Drupal CVE-2024-45440
 castro-ian/cve-2024-4573-mitigation-script
Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 hazemkya/cve-2024-3094-checker
Bash script to detect and remediate CVE-2024-3094, a critical supply-chain vulnerability in the XZ Utils library, with automatic safe version…
 vt0x78/cve-2024-31989
Exploit for CVE-2024-31989.
 djayagit/cve-2024-5326-poc
CVE-2024-5326 Post Grid Gutenberg Blocks and WordPress Blog Plugin – PostX <= 4.1.2 - Missing Authorization to Arbitrary Options Update
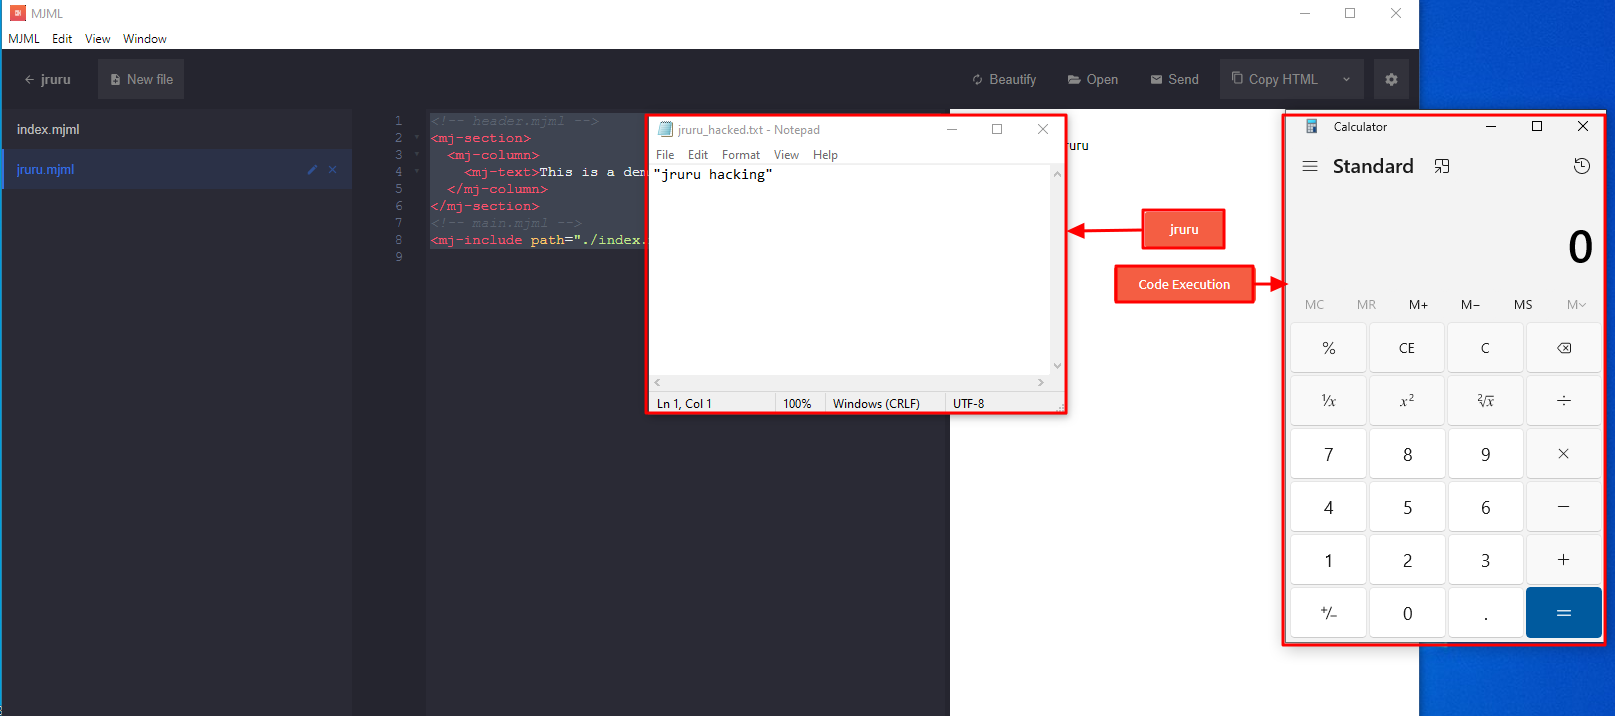 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE exploit