

lynis
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
configuration-auditingdatabase-securitydefensive-tools+5
16.5k
cisofy/lynisAgentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
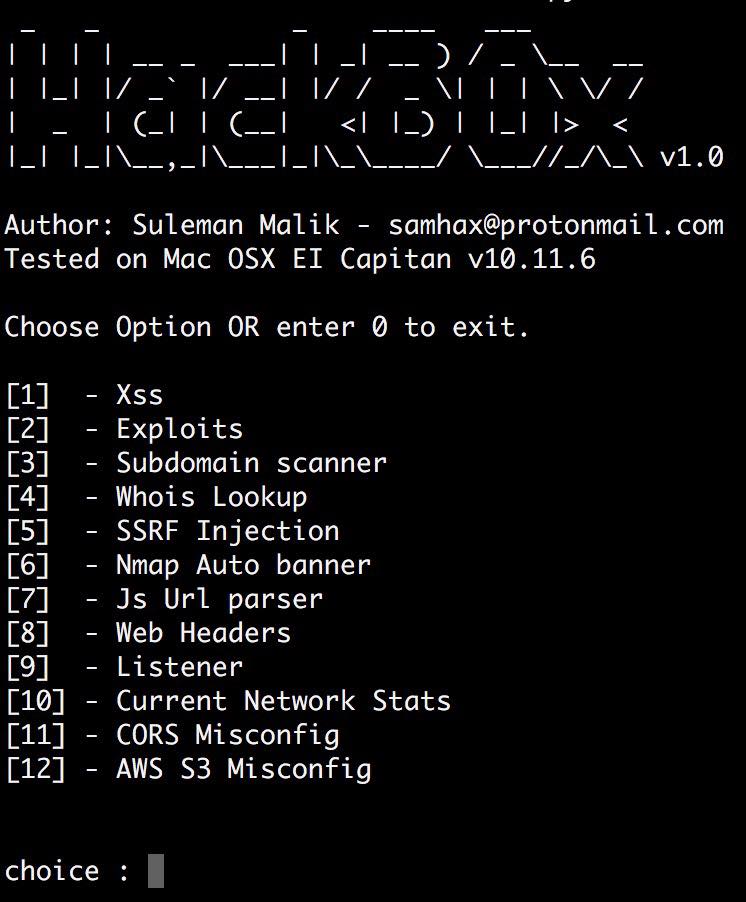 samhaxr/hackbox
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…
 first-roman/sprig-mvc-demo-patch
This demo application partially covers the vulnerability CVE-2024-38828
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
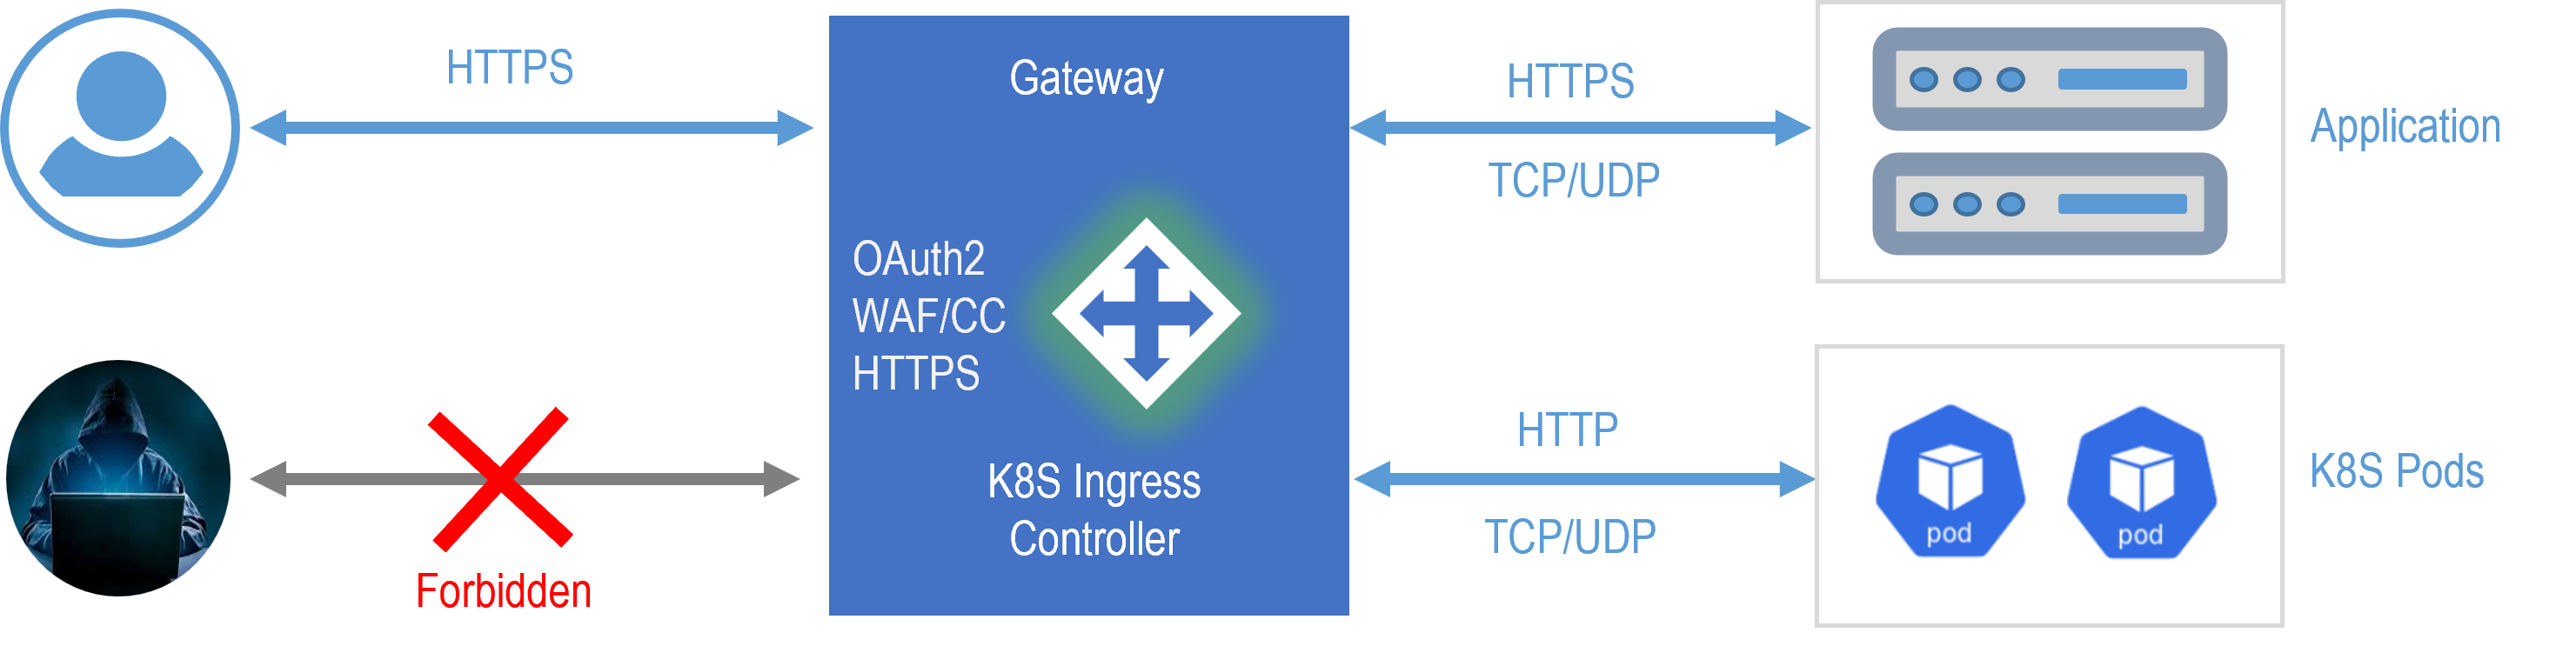 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
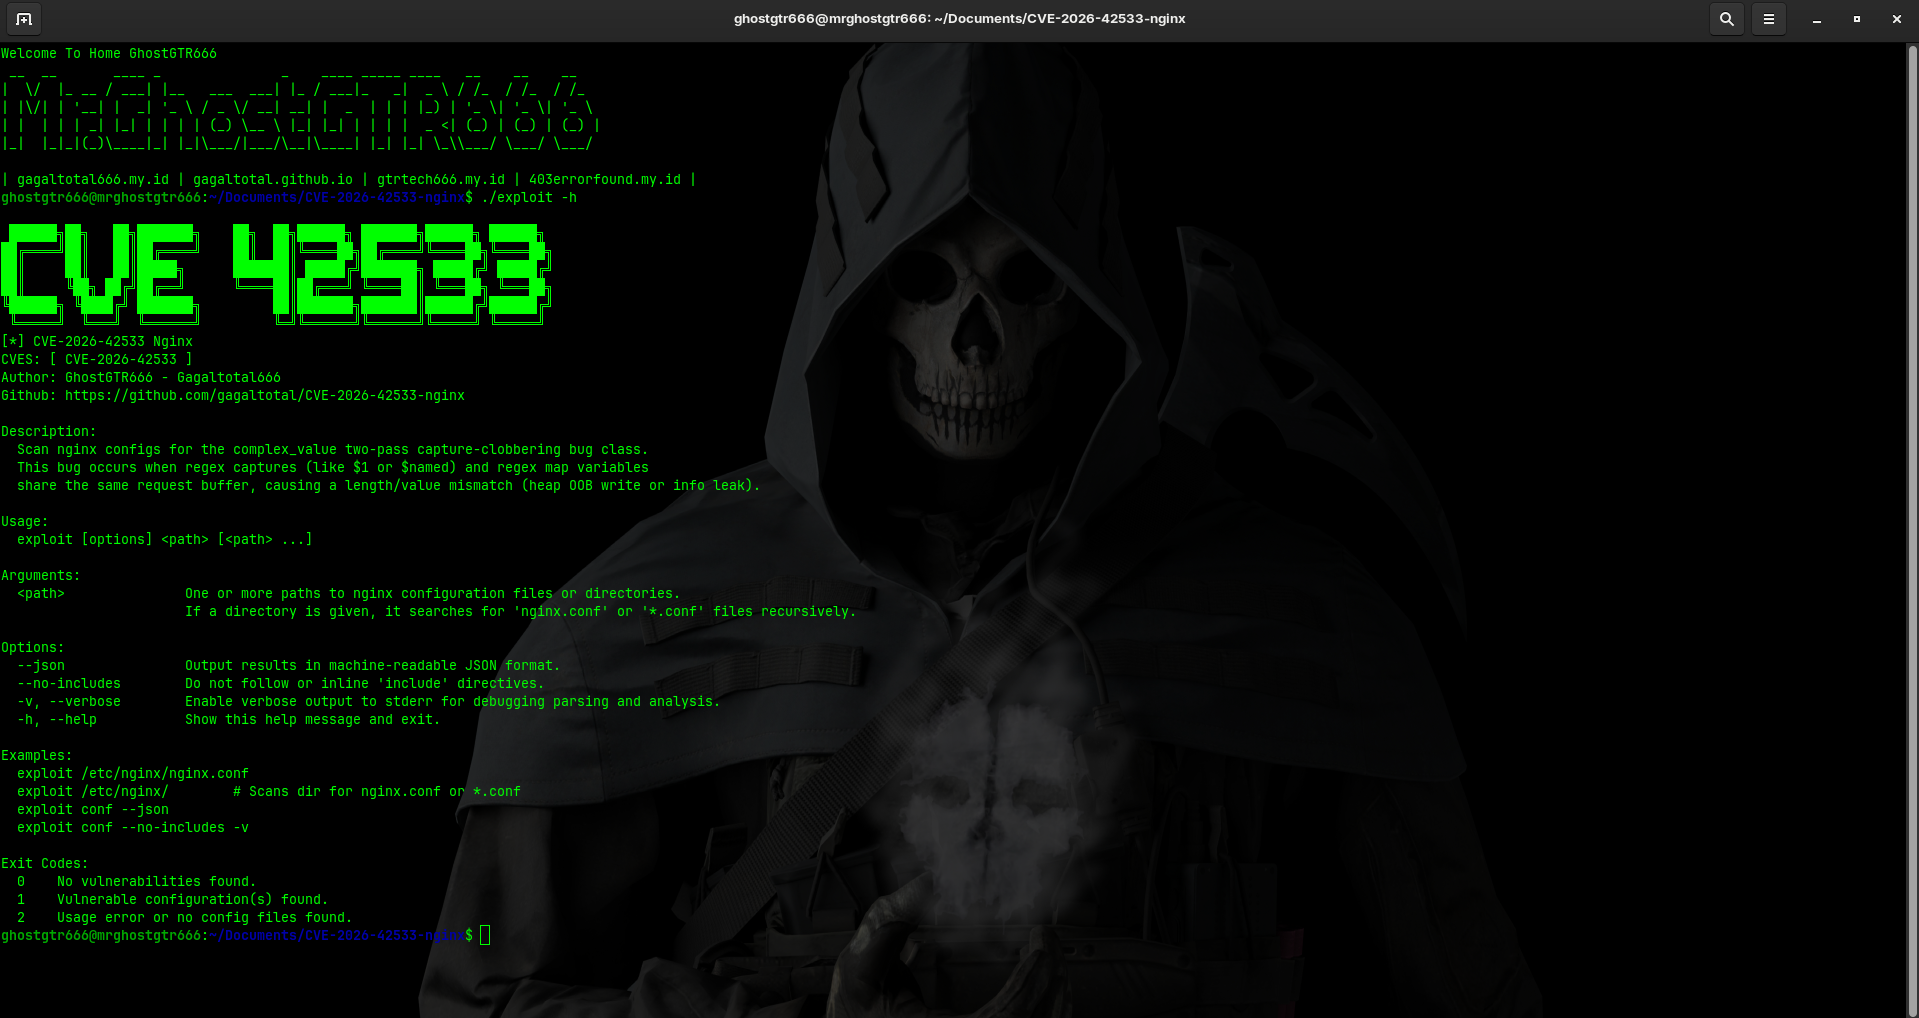 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 legit-labs/gh-legitify
GitHub CLI extension for running "legitify"
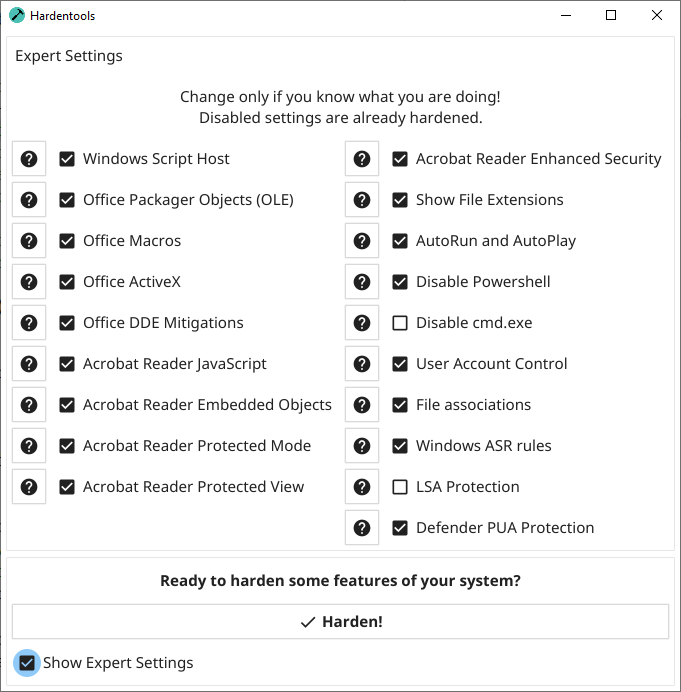 hardentools/hardentools
Hardentools simply reduces the attack surface on Microsoft Windows computers by disabling low-hanging fruit risky features.
 ltidi2000/cve-2021-45232
Proof-of-concept exploit for CVE-2021-45232, an unauthorized access vulnerability in Apache APISIX Dashboard allowing export/import of admin…
