
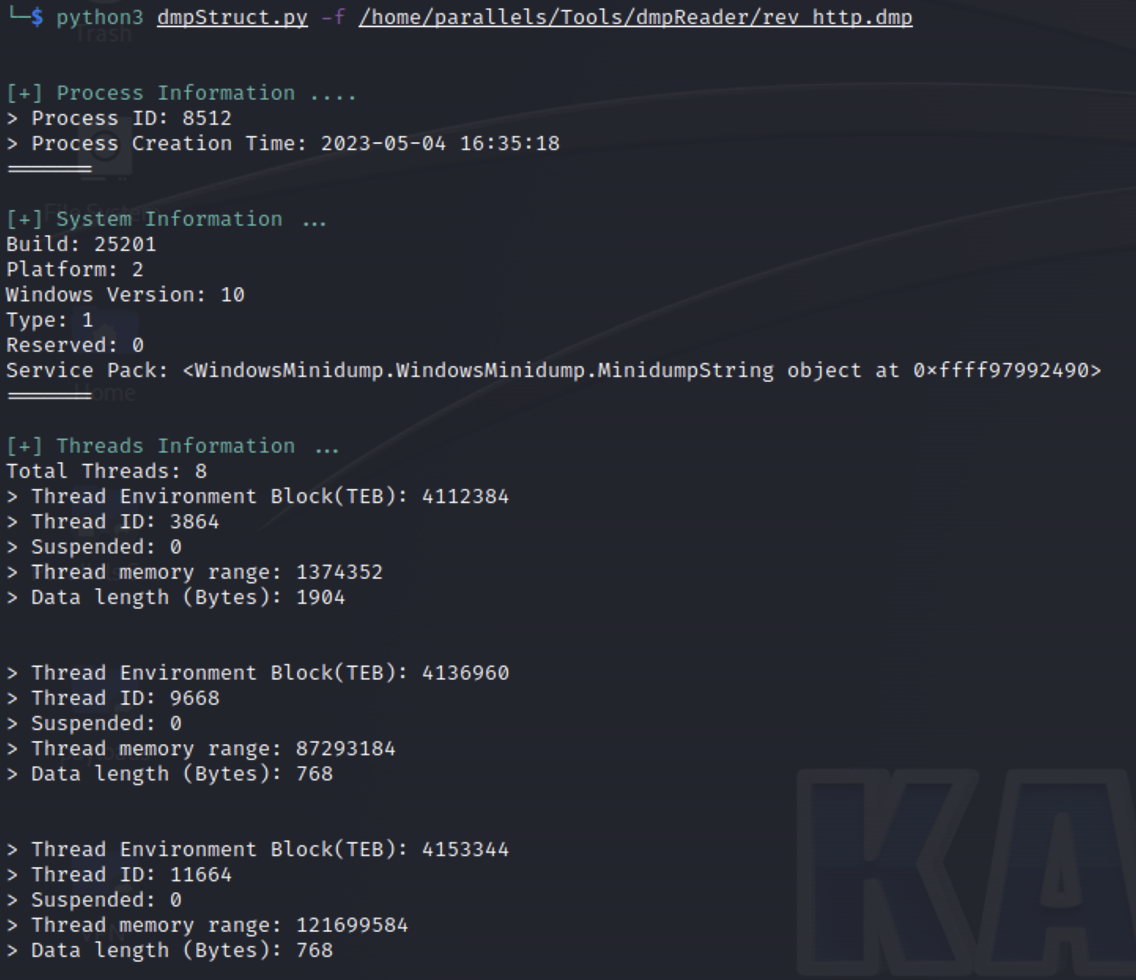
miniDumpReader
 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
binary-analysisdigital-forensicsforensics+3
gmh5225/minidumpreaderParses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
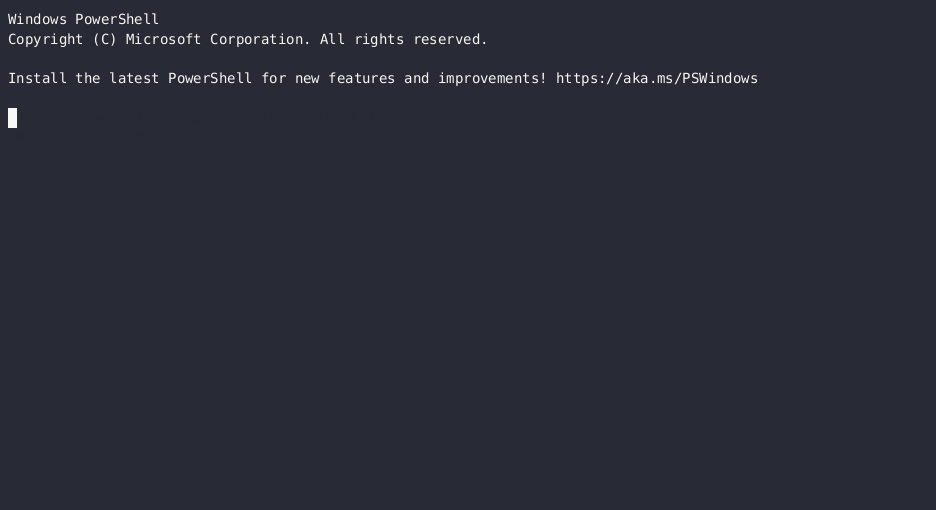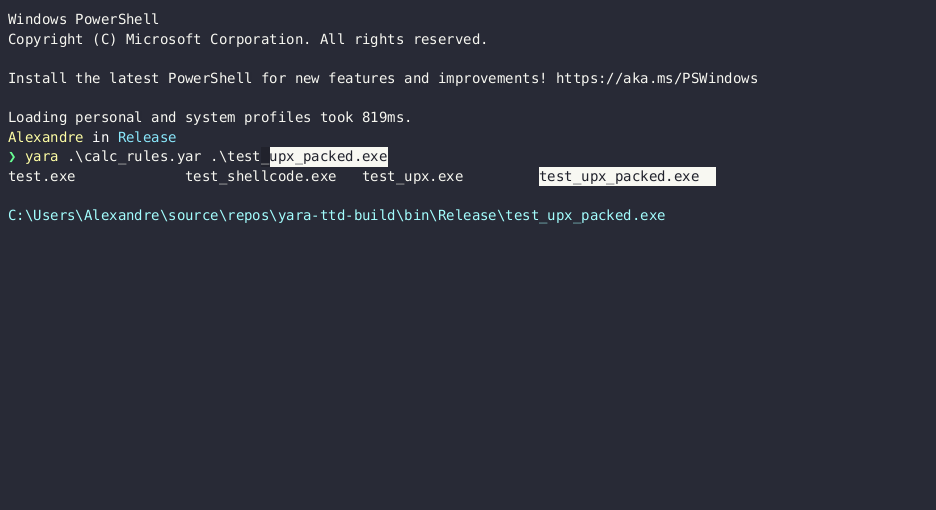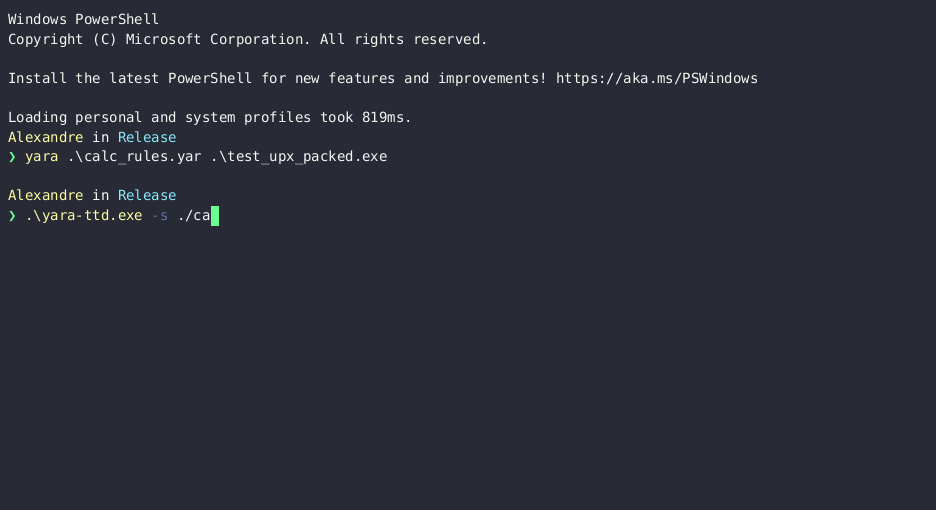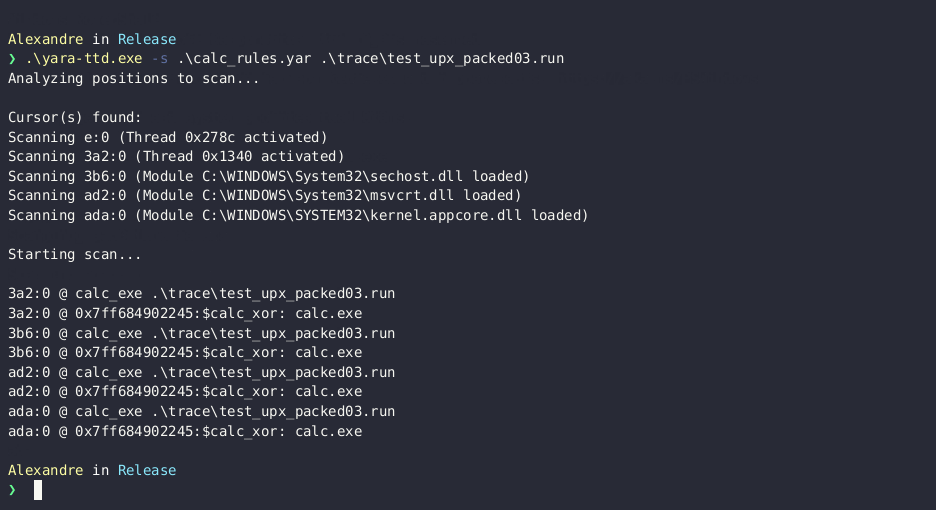 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces