

CVE-2025-7771
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
binary-exploitationexploitationmemory-forensics+3
2
lzty/cve-2025-7771Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
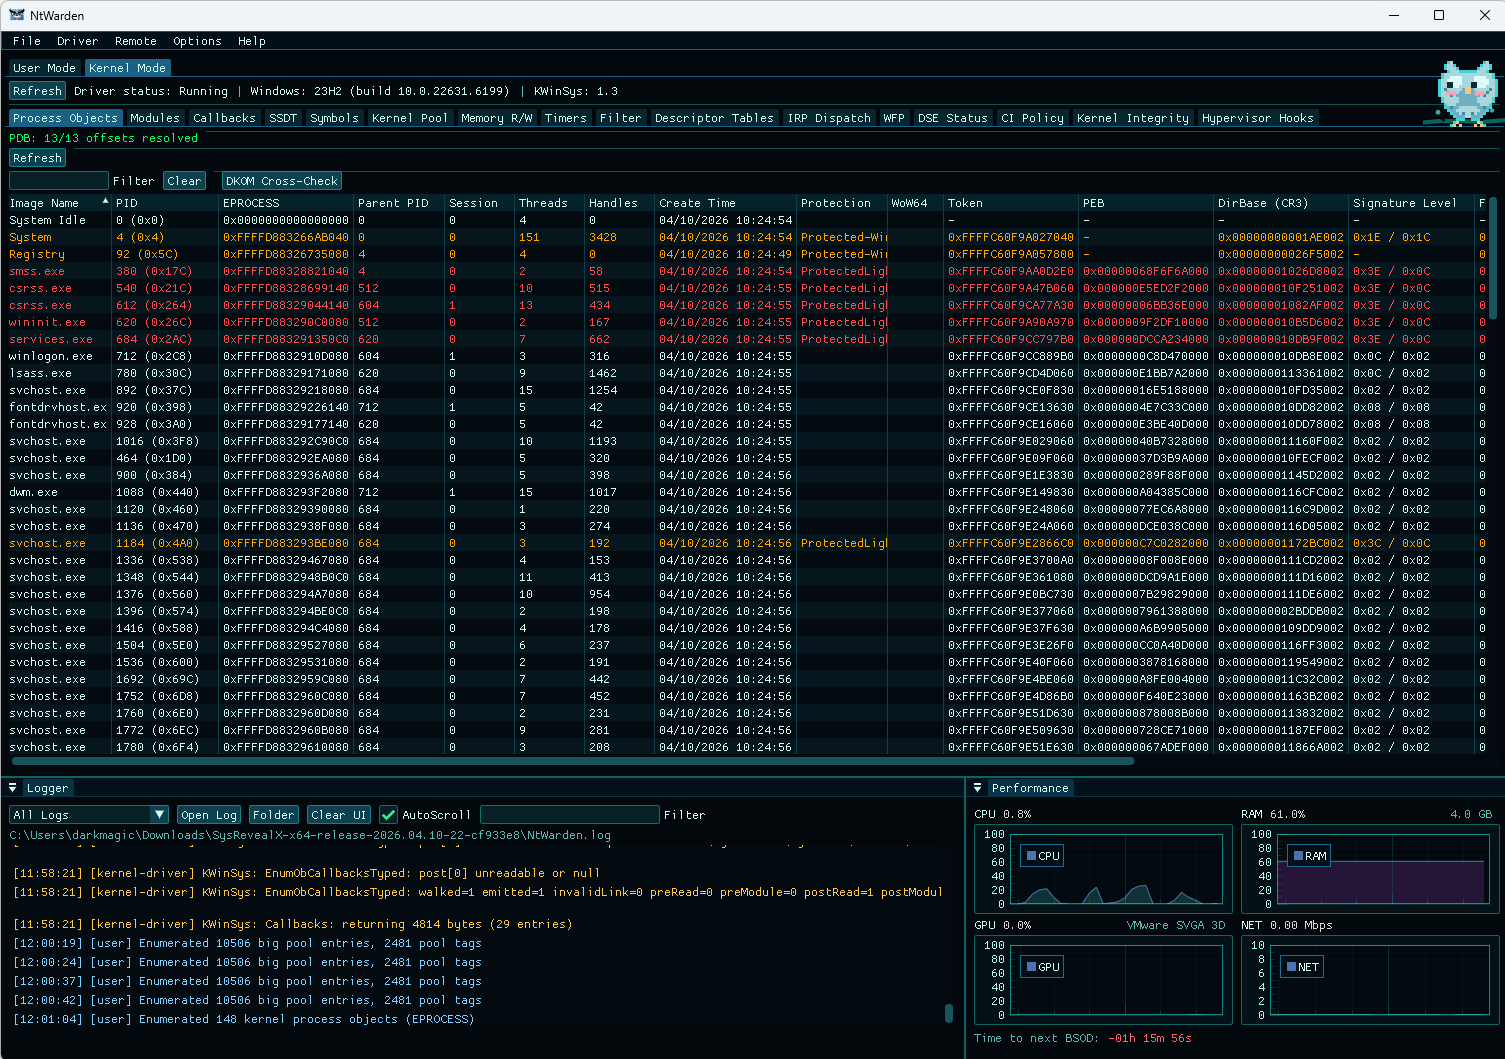 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
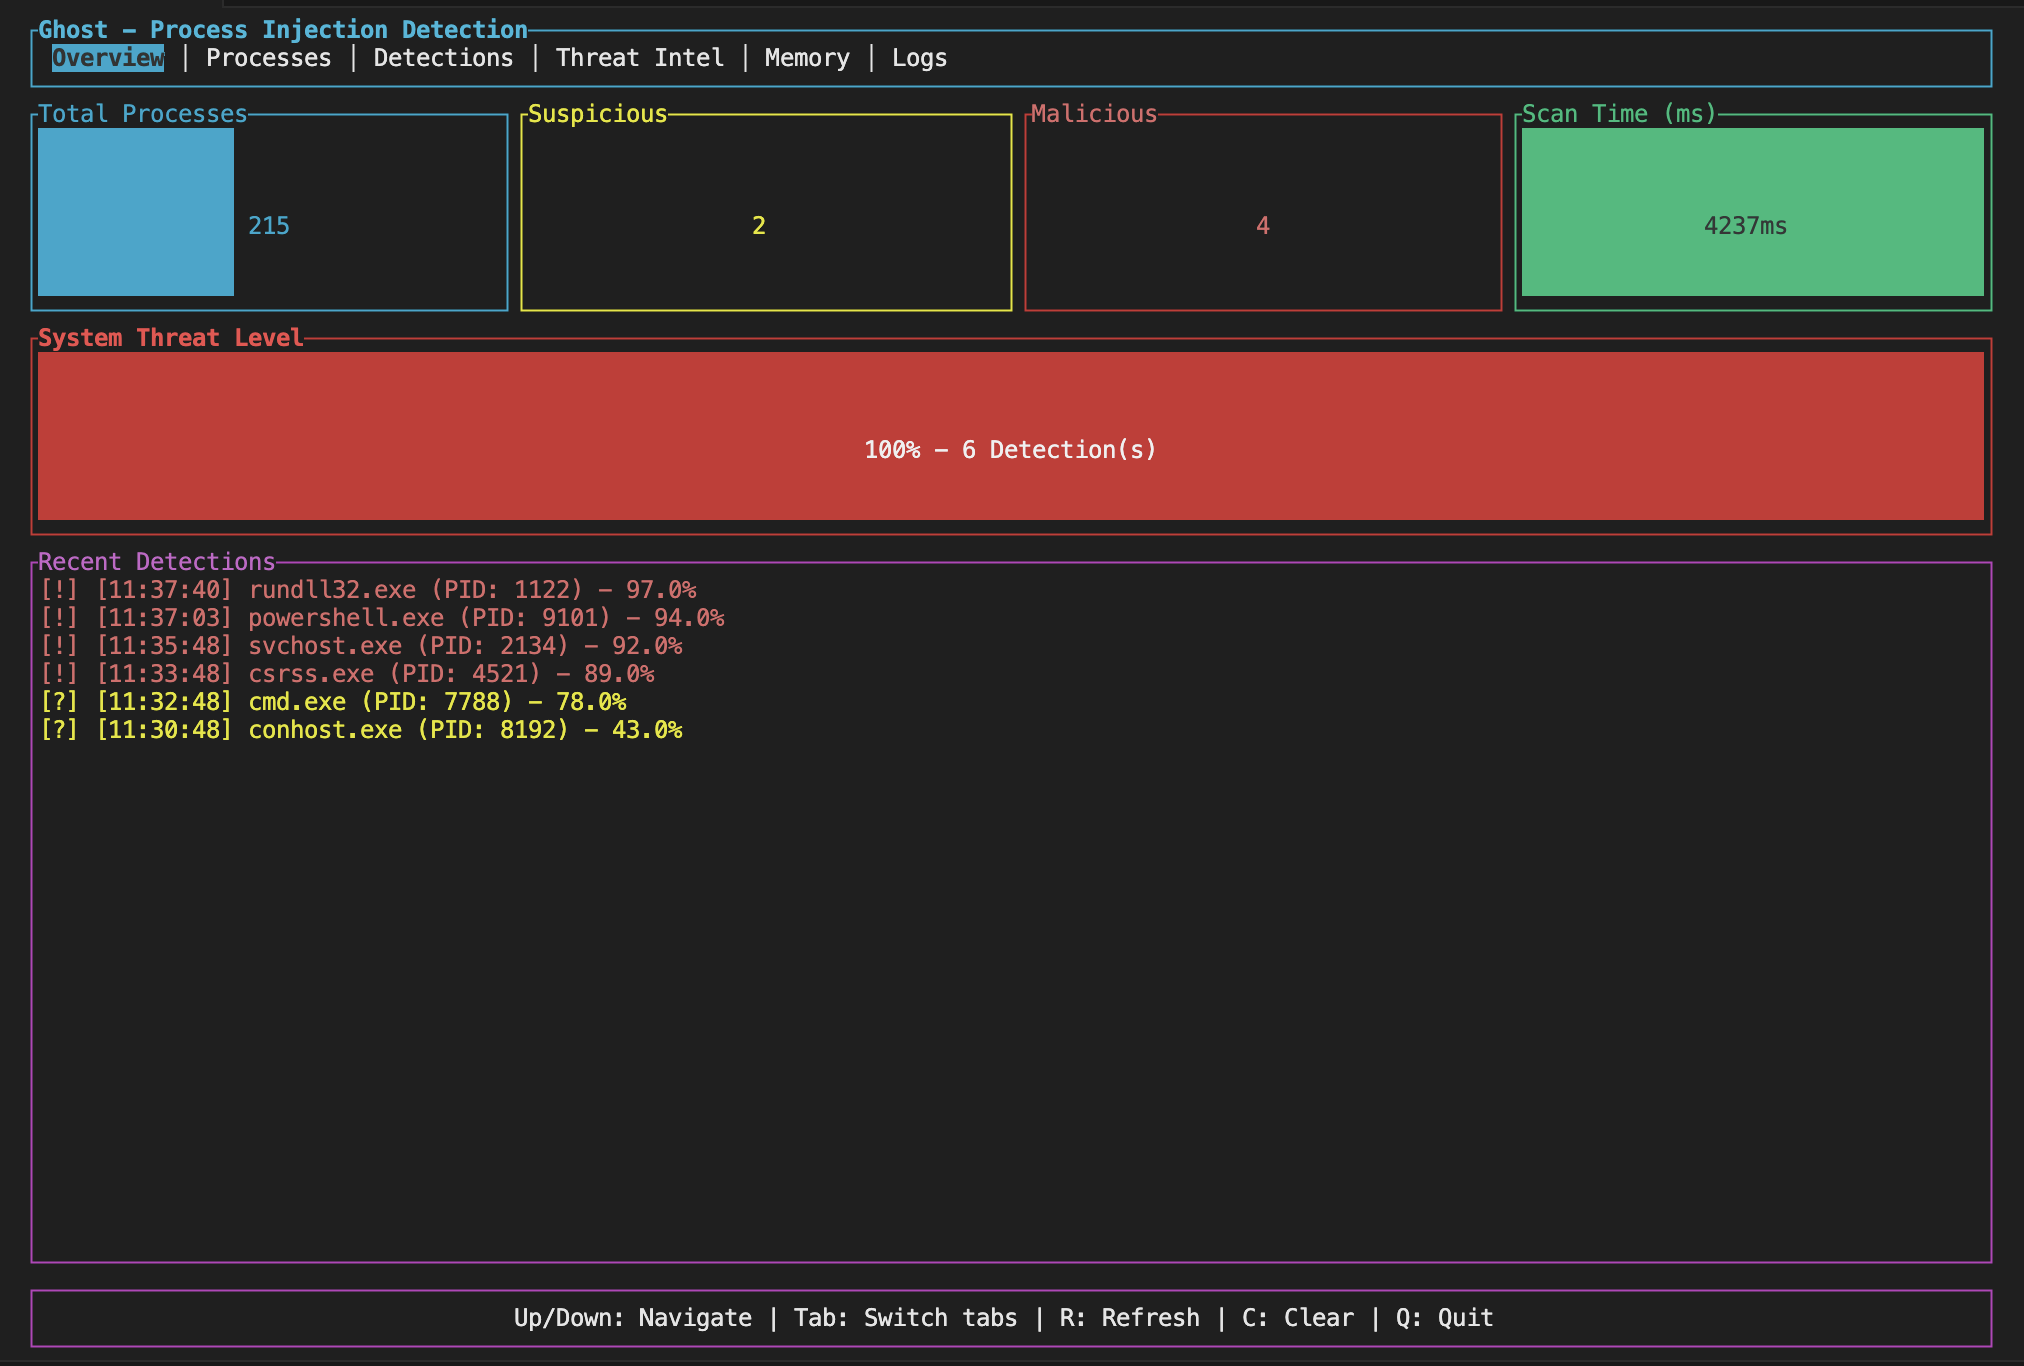 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 helpsystems/embarcadero-workaround
This is a workaround for CVE-2014-0993 and CVE-2014-0994 that patches on memory without the need to recompile your vulnerable software. This is not…
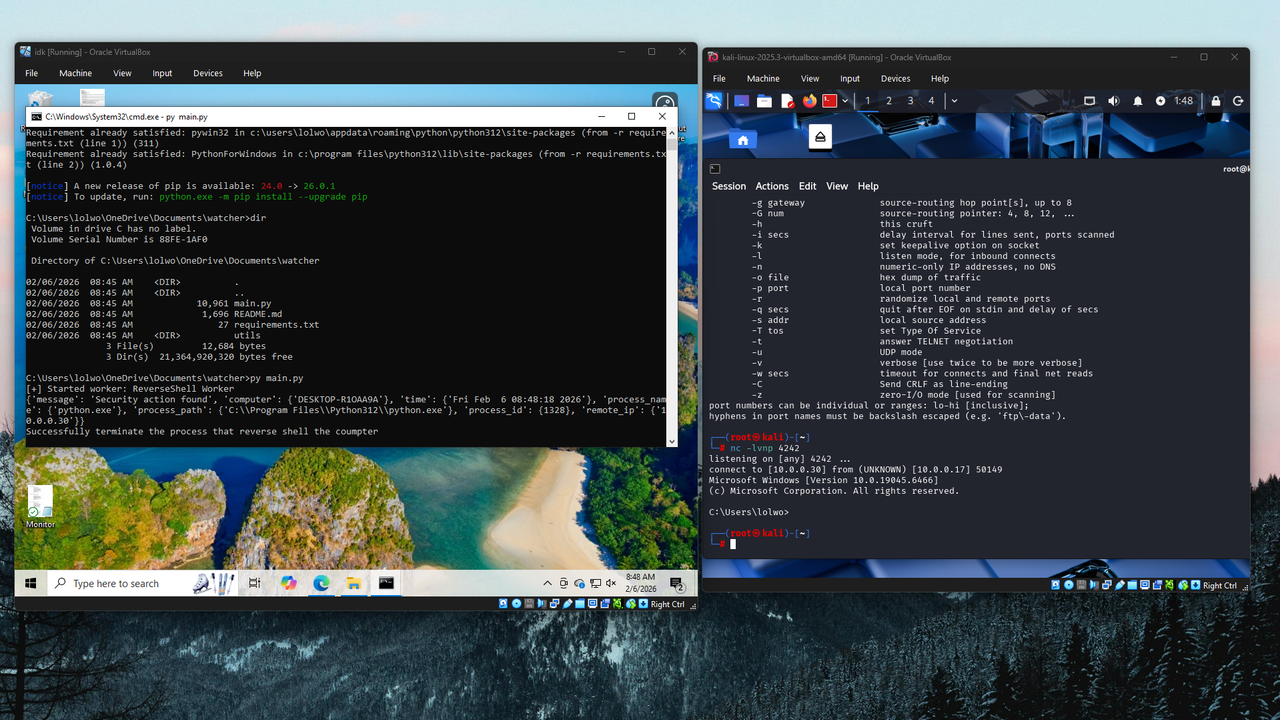 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 ping-2o/ios.cve-2026-84616-84607
research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
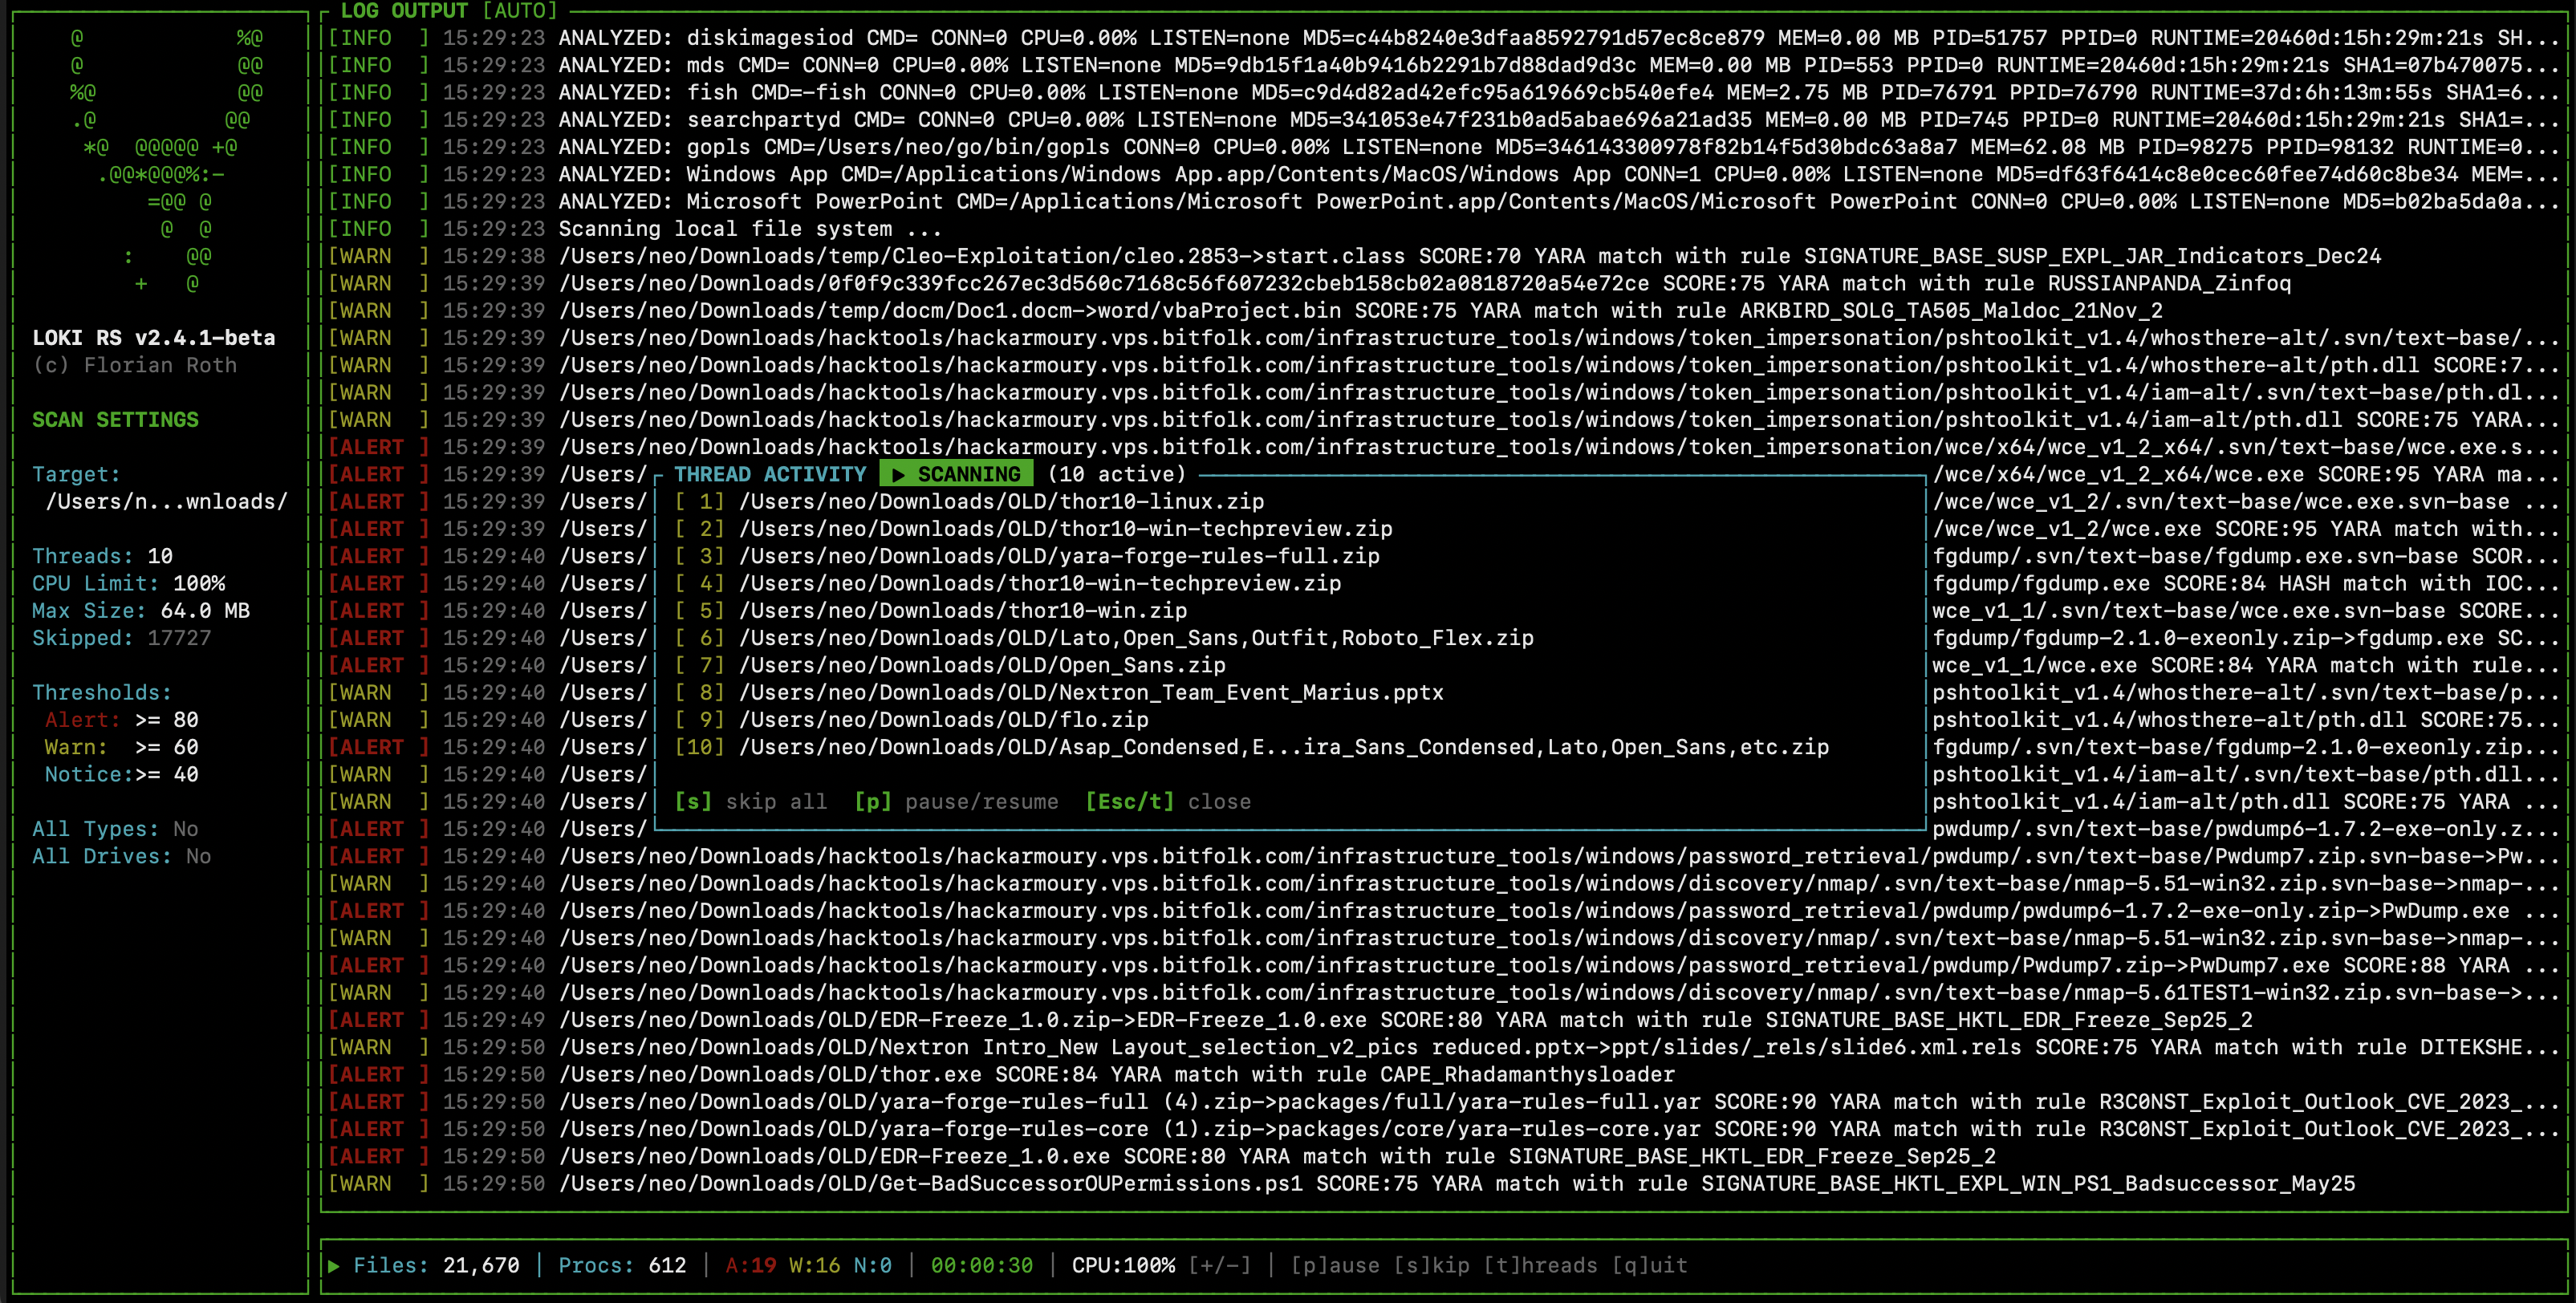 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 encrypter15/cve-2025-30400
Educational Python model demonstrating a Use-After-Free (UAF) privilege escalation vulnerability inspired by CVE-2025-30400 in Windows DWM. Simulates…
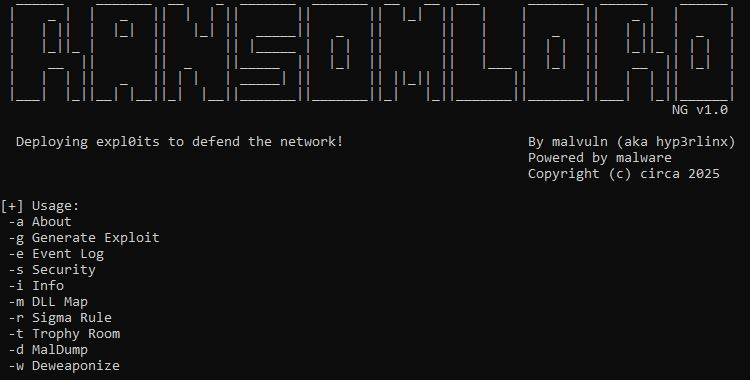 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
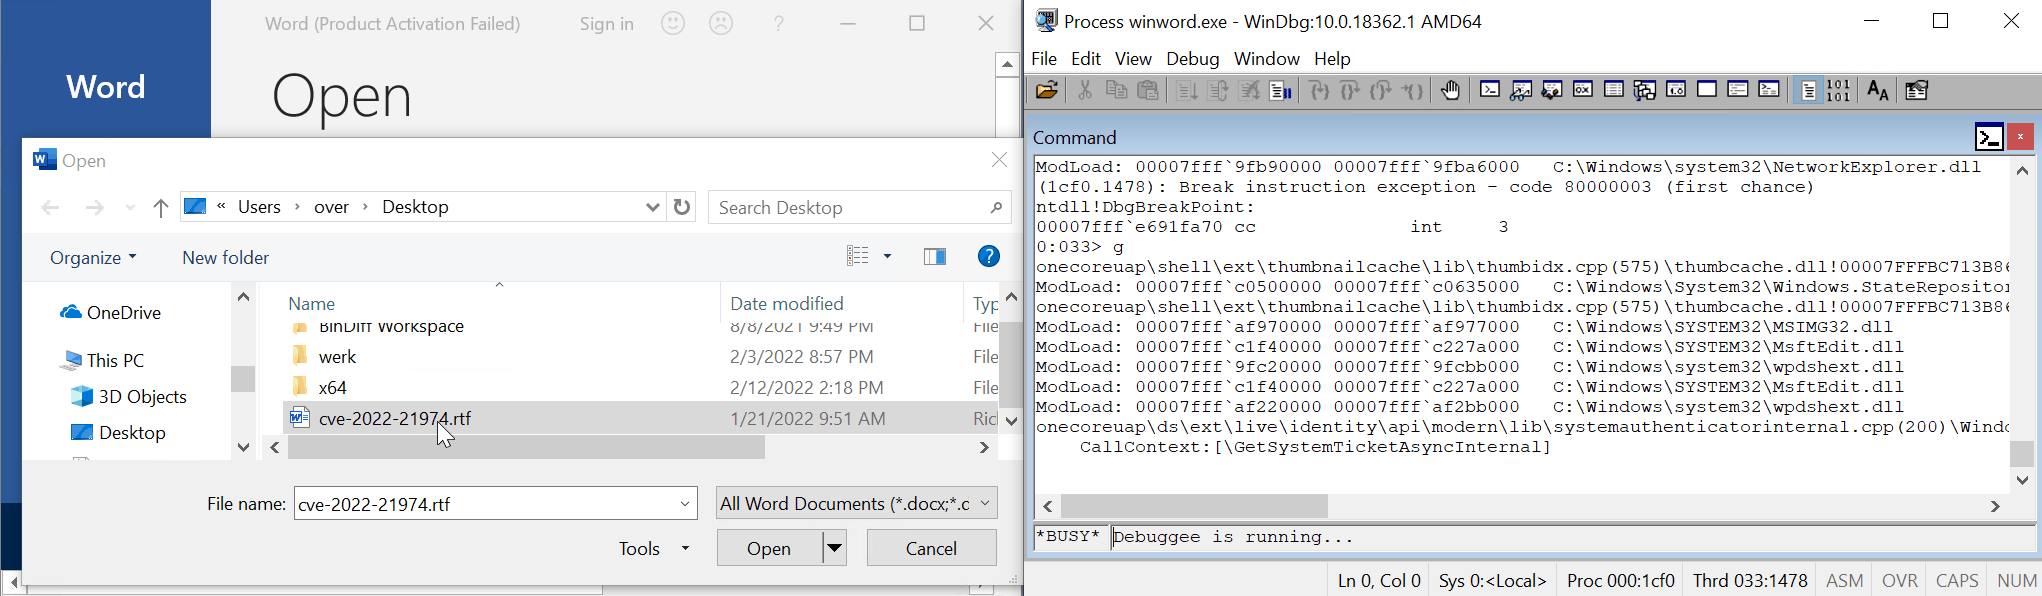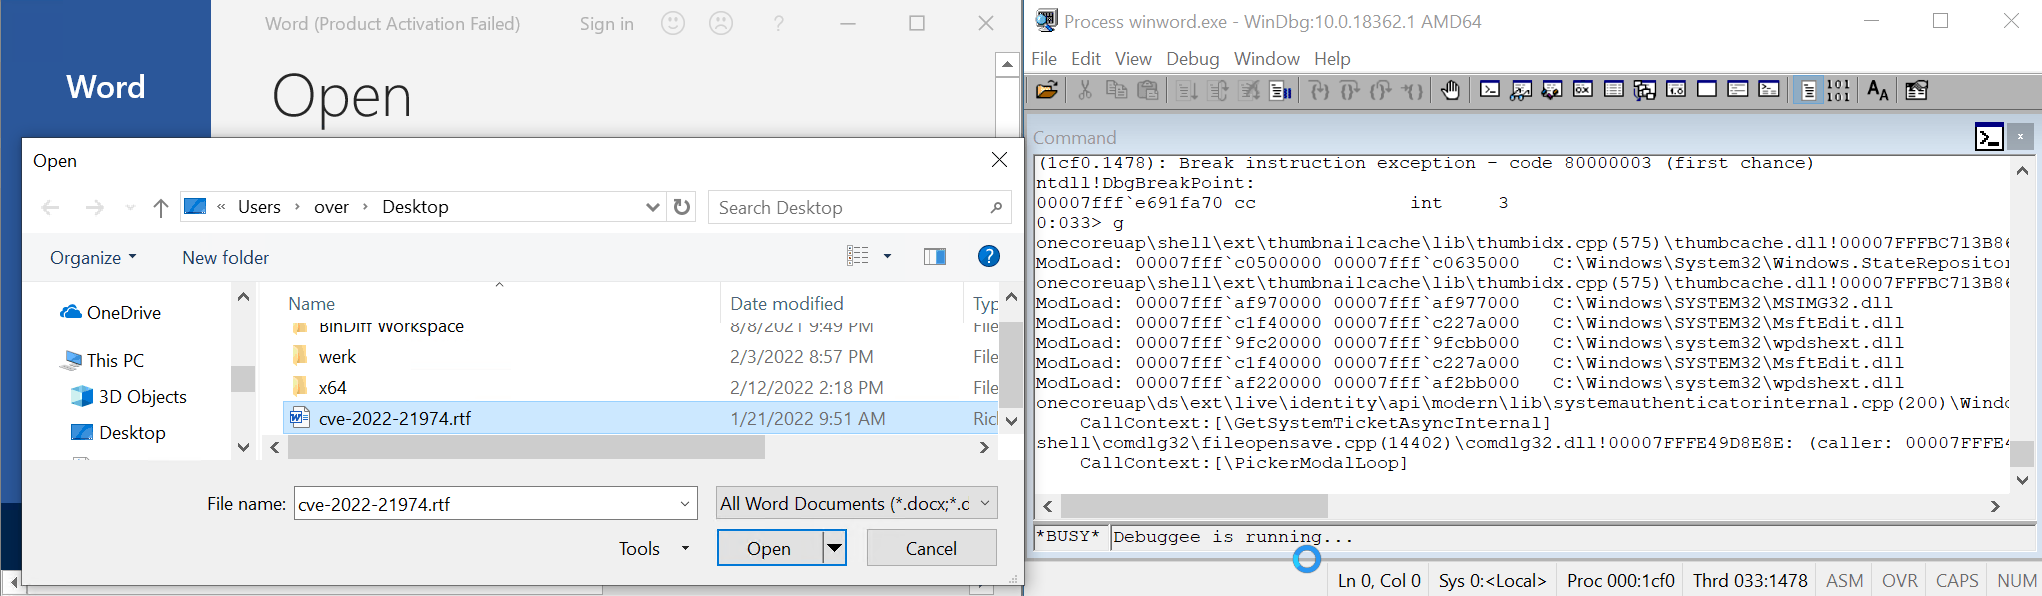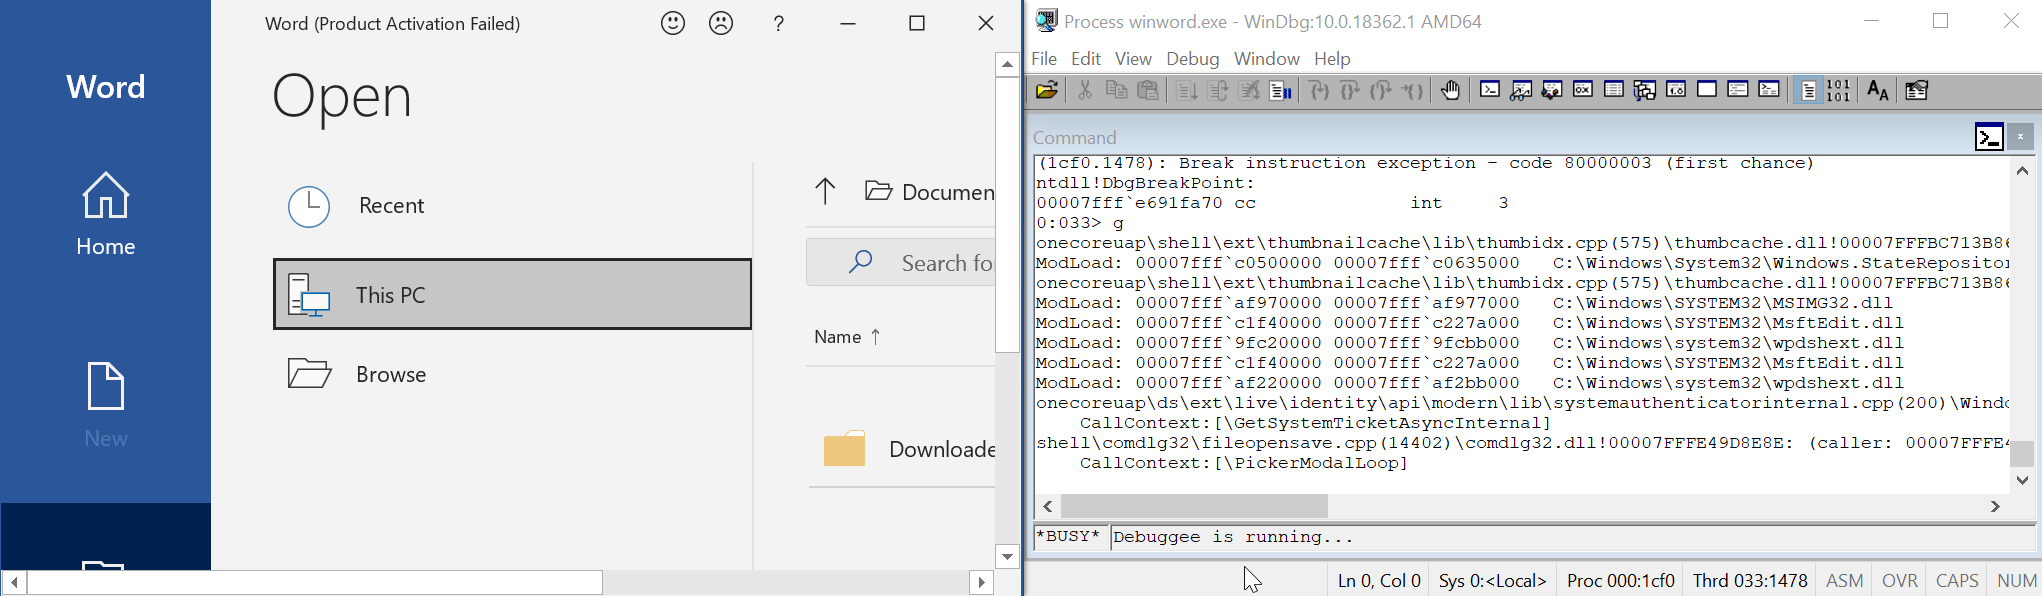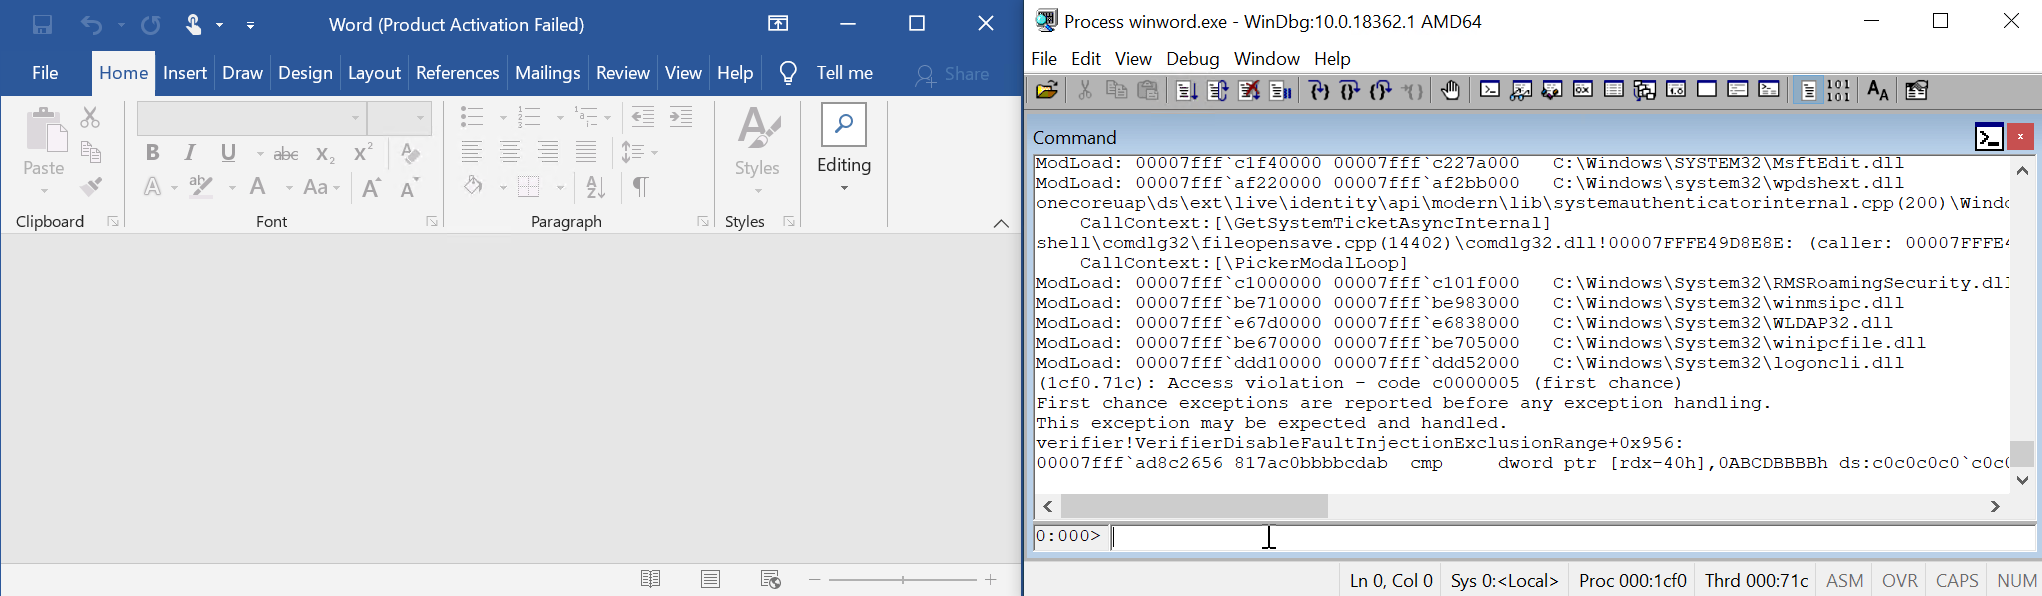 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…