
Archived
dumpscan
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
cryptographydigital-forensicsencryption-decryption-tools+4
118
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
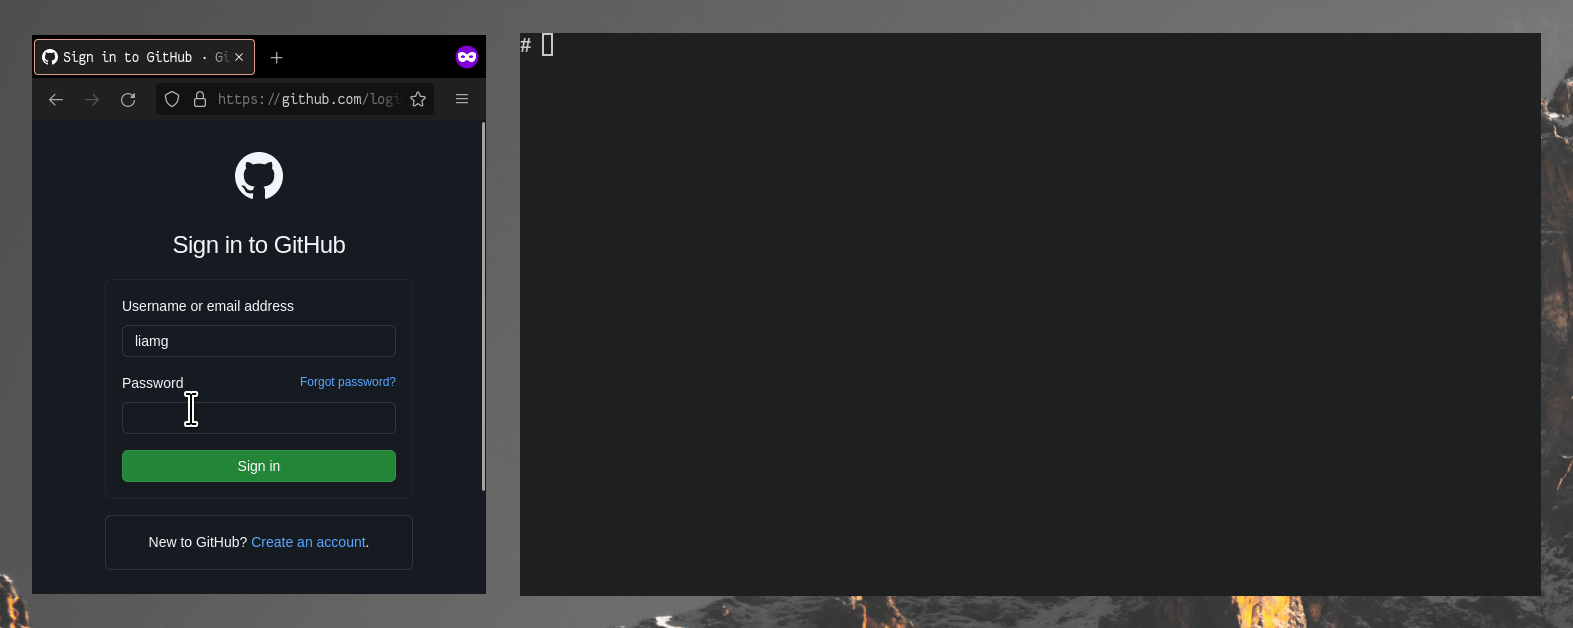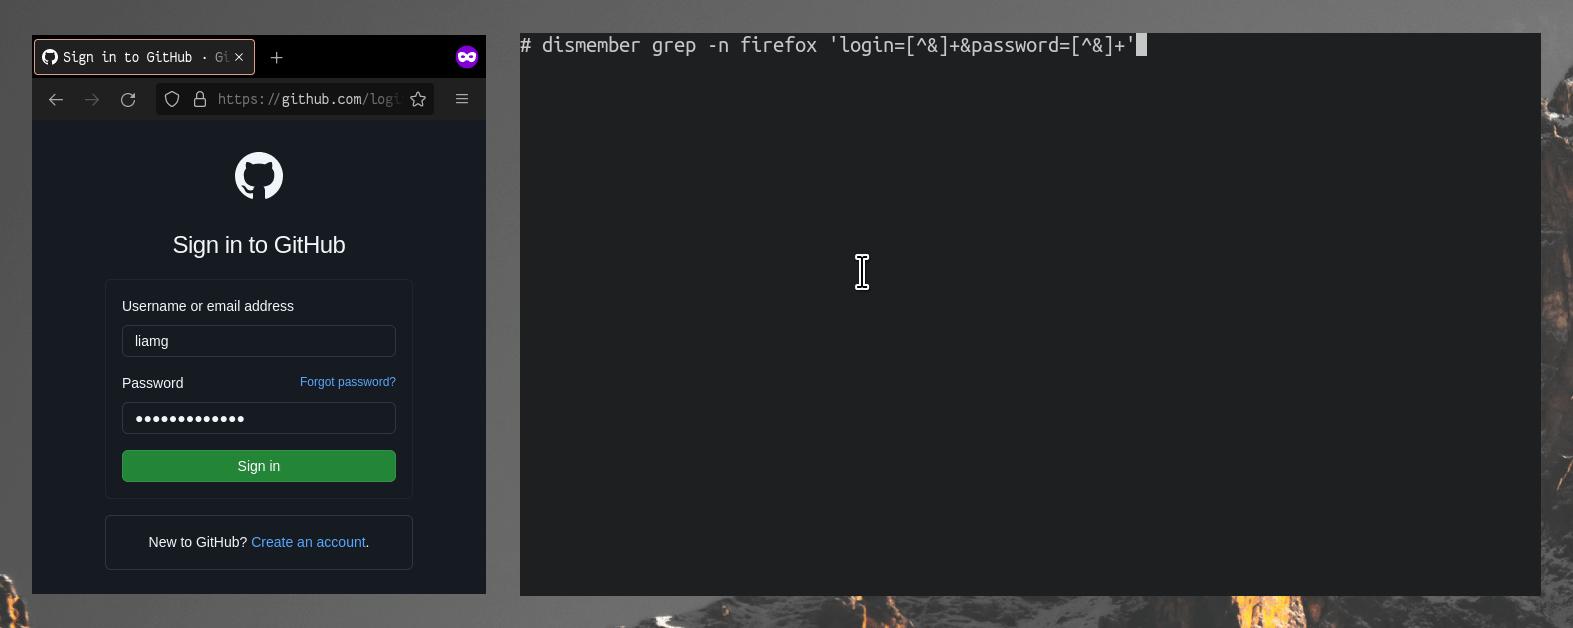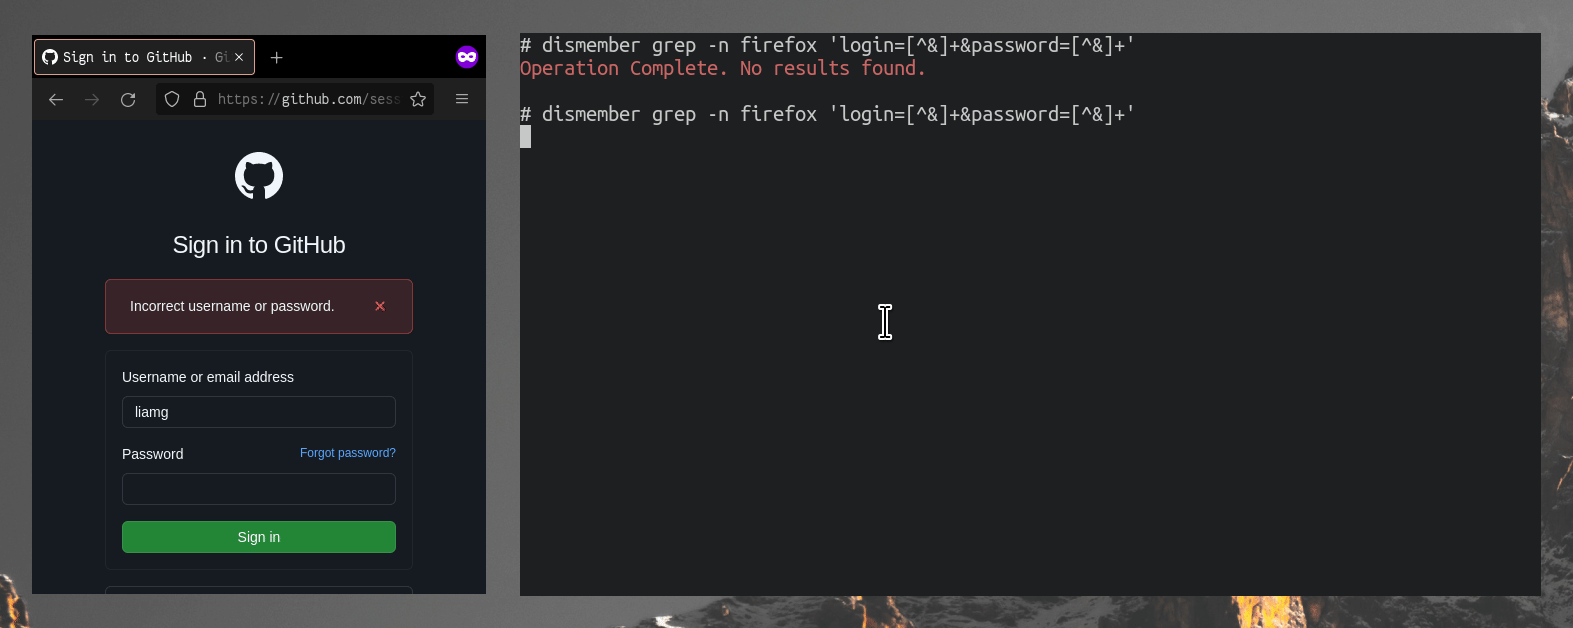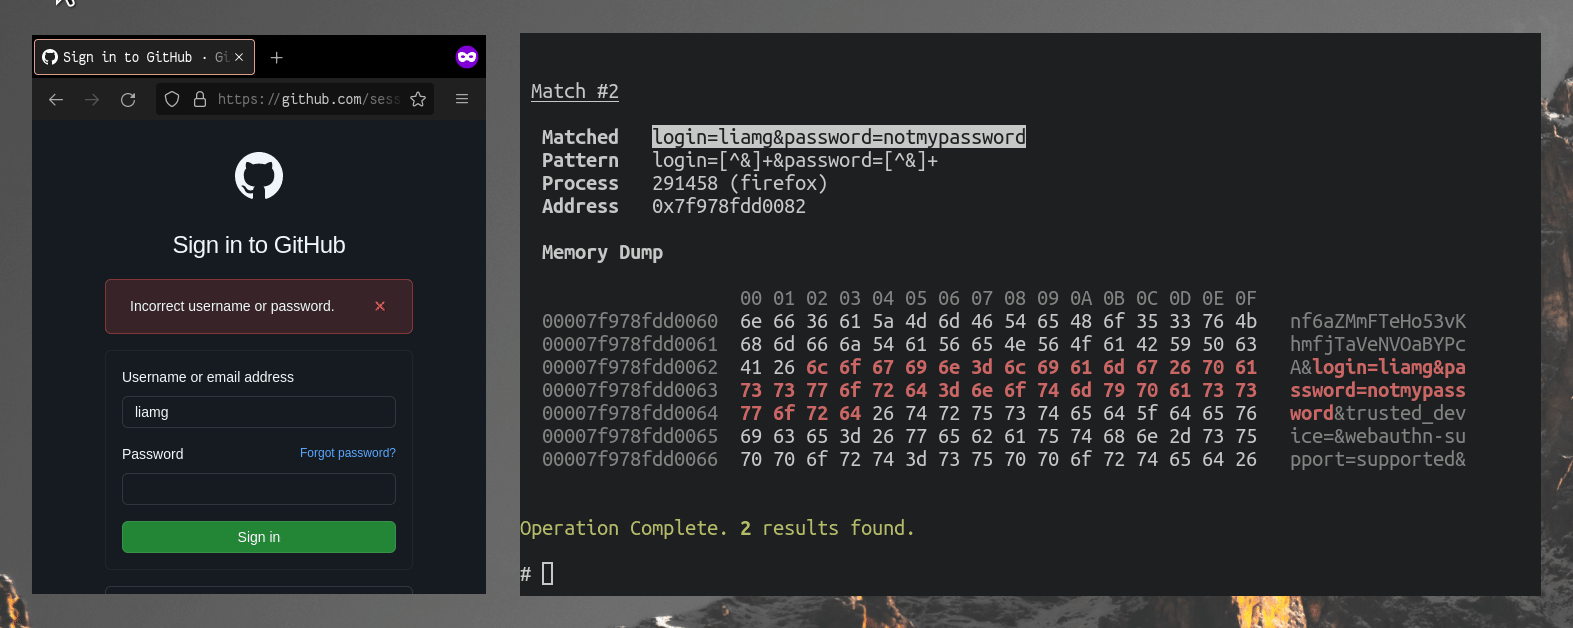 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
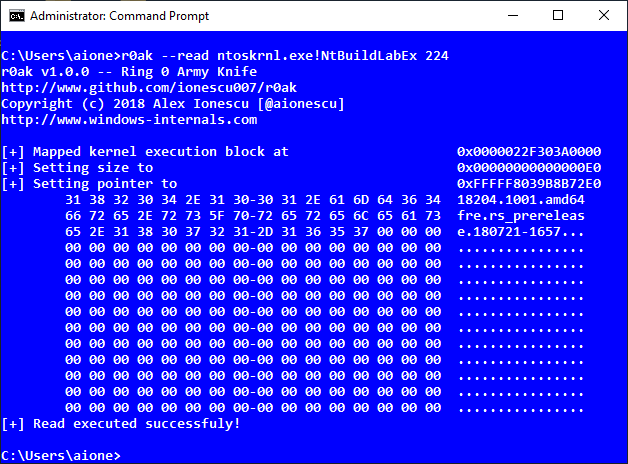 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework