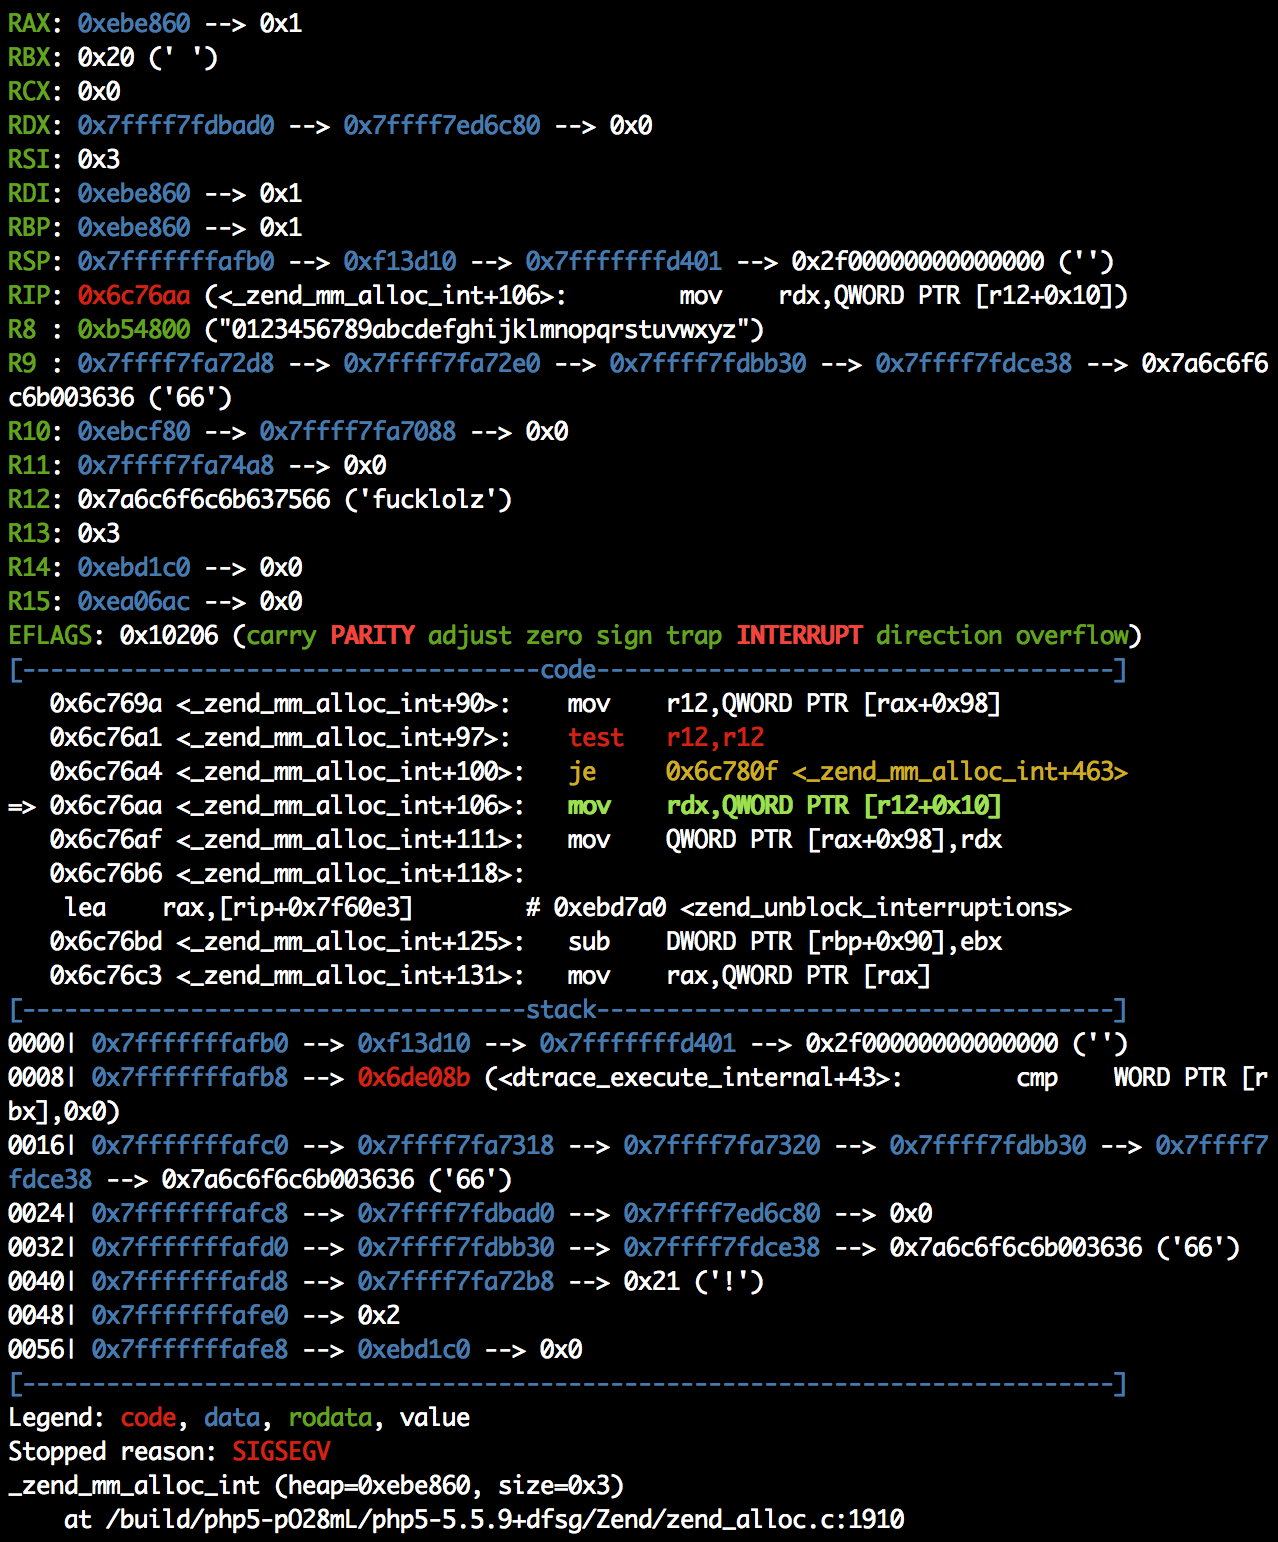
SwishDbgExt
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
debuggersdigital-forensicsincident-response+3
4017 years ago
magnetforensics/swishdbgextIncident Response & Digital Forensics Debugging Extension
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.