CVE-2026-31431-Report-Copy-fail-Vulnerability-

Detailed analysis of the Copy Fail vulnerability (CVE-2026-31431) in the Linux kernel, including memory corruption mechanism, privilege escalation…

Detailed analysis of the Copy Fail vulnerability (CVE-2026-31431) in the Linux kernel, including memory corruption mechanism, privilege escalation…

Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…

Proof-of-concept exploit for CVE-2022-37969, a Windows Common Log File System driver local privilege escalation. Demonstrates heap spray, token…

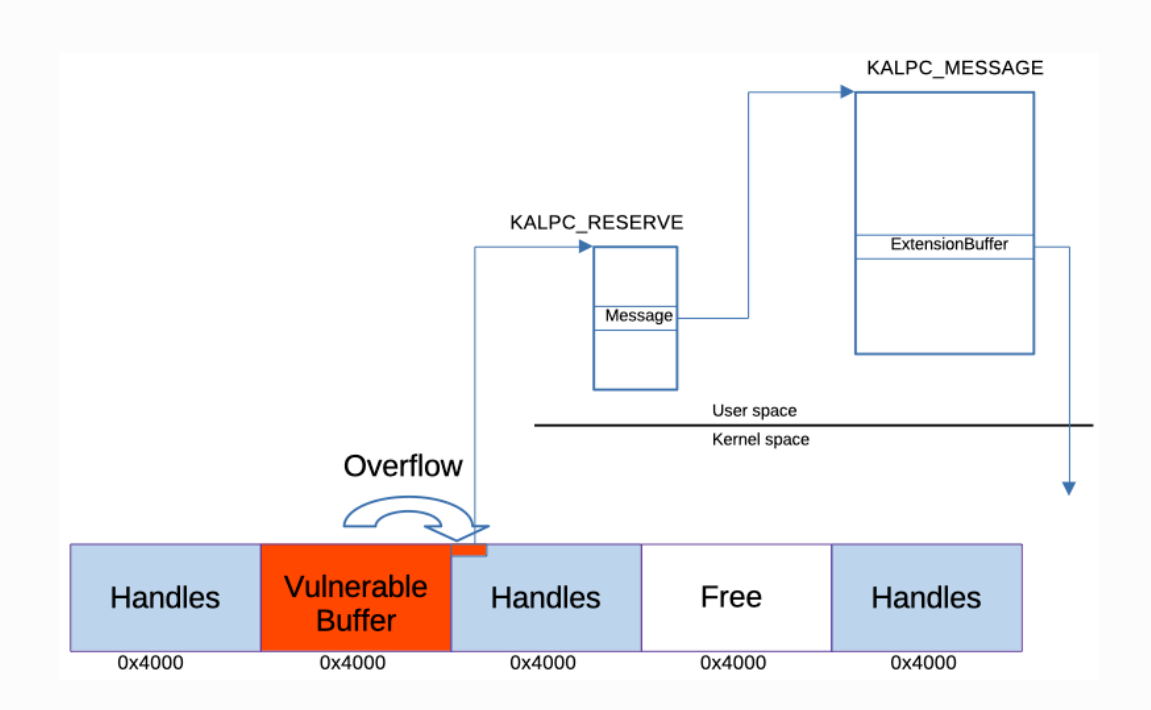
Windows Kernel Pool (clfs.sys) Corruption Privilege Escalation

Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…

Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.

Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…

Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…

Kernel memory read exploit leveraging CVE-2013-6282 for local privilege escalation on affected Linux systems.

Exploit for Exim Use-After-Free (CVE-2020-28018) achieving remote code execution via memory corruption primitives, including arbitrary read/write and…

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

Proof-of-concept exploit for CVE-2024-30085, a heap-based buffer overflow in the Windows CLDLFT driver leading to local privilege escalation on…

Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…

Proof-of-concept exploit for CVE-2021-31956, a Windows kernel NTFS elevation-of-privilege vulnerability. Demonstrates exploitation techniques…

Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…

Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…

Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…