
CVE-2022-22947
 sijido/cve-2022-22947
Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.
exploitationmemory-forensicsvulnerability-analysis+1
9
sijido/cve-2022-22947Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
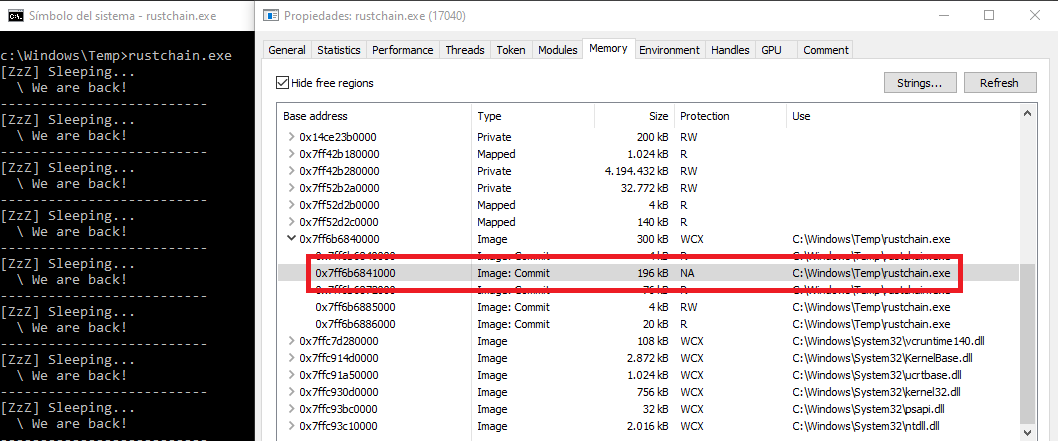 kudaes/rustchain
Hide memory artifacts using ROP and hardware breakpoints.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…