
ThreadStackSpoofer
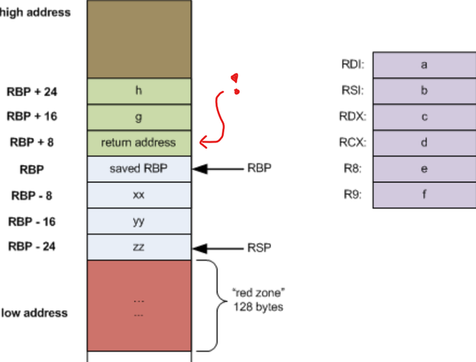
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

Cobalt Strike UDRL for memory scanner evasion.

ROP-based sleep obfuscation to evade memory scanners

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Ghidra is a software reverse engineering (SRE) framework

UNIX-like reverse engineering framework and command-line toolset

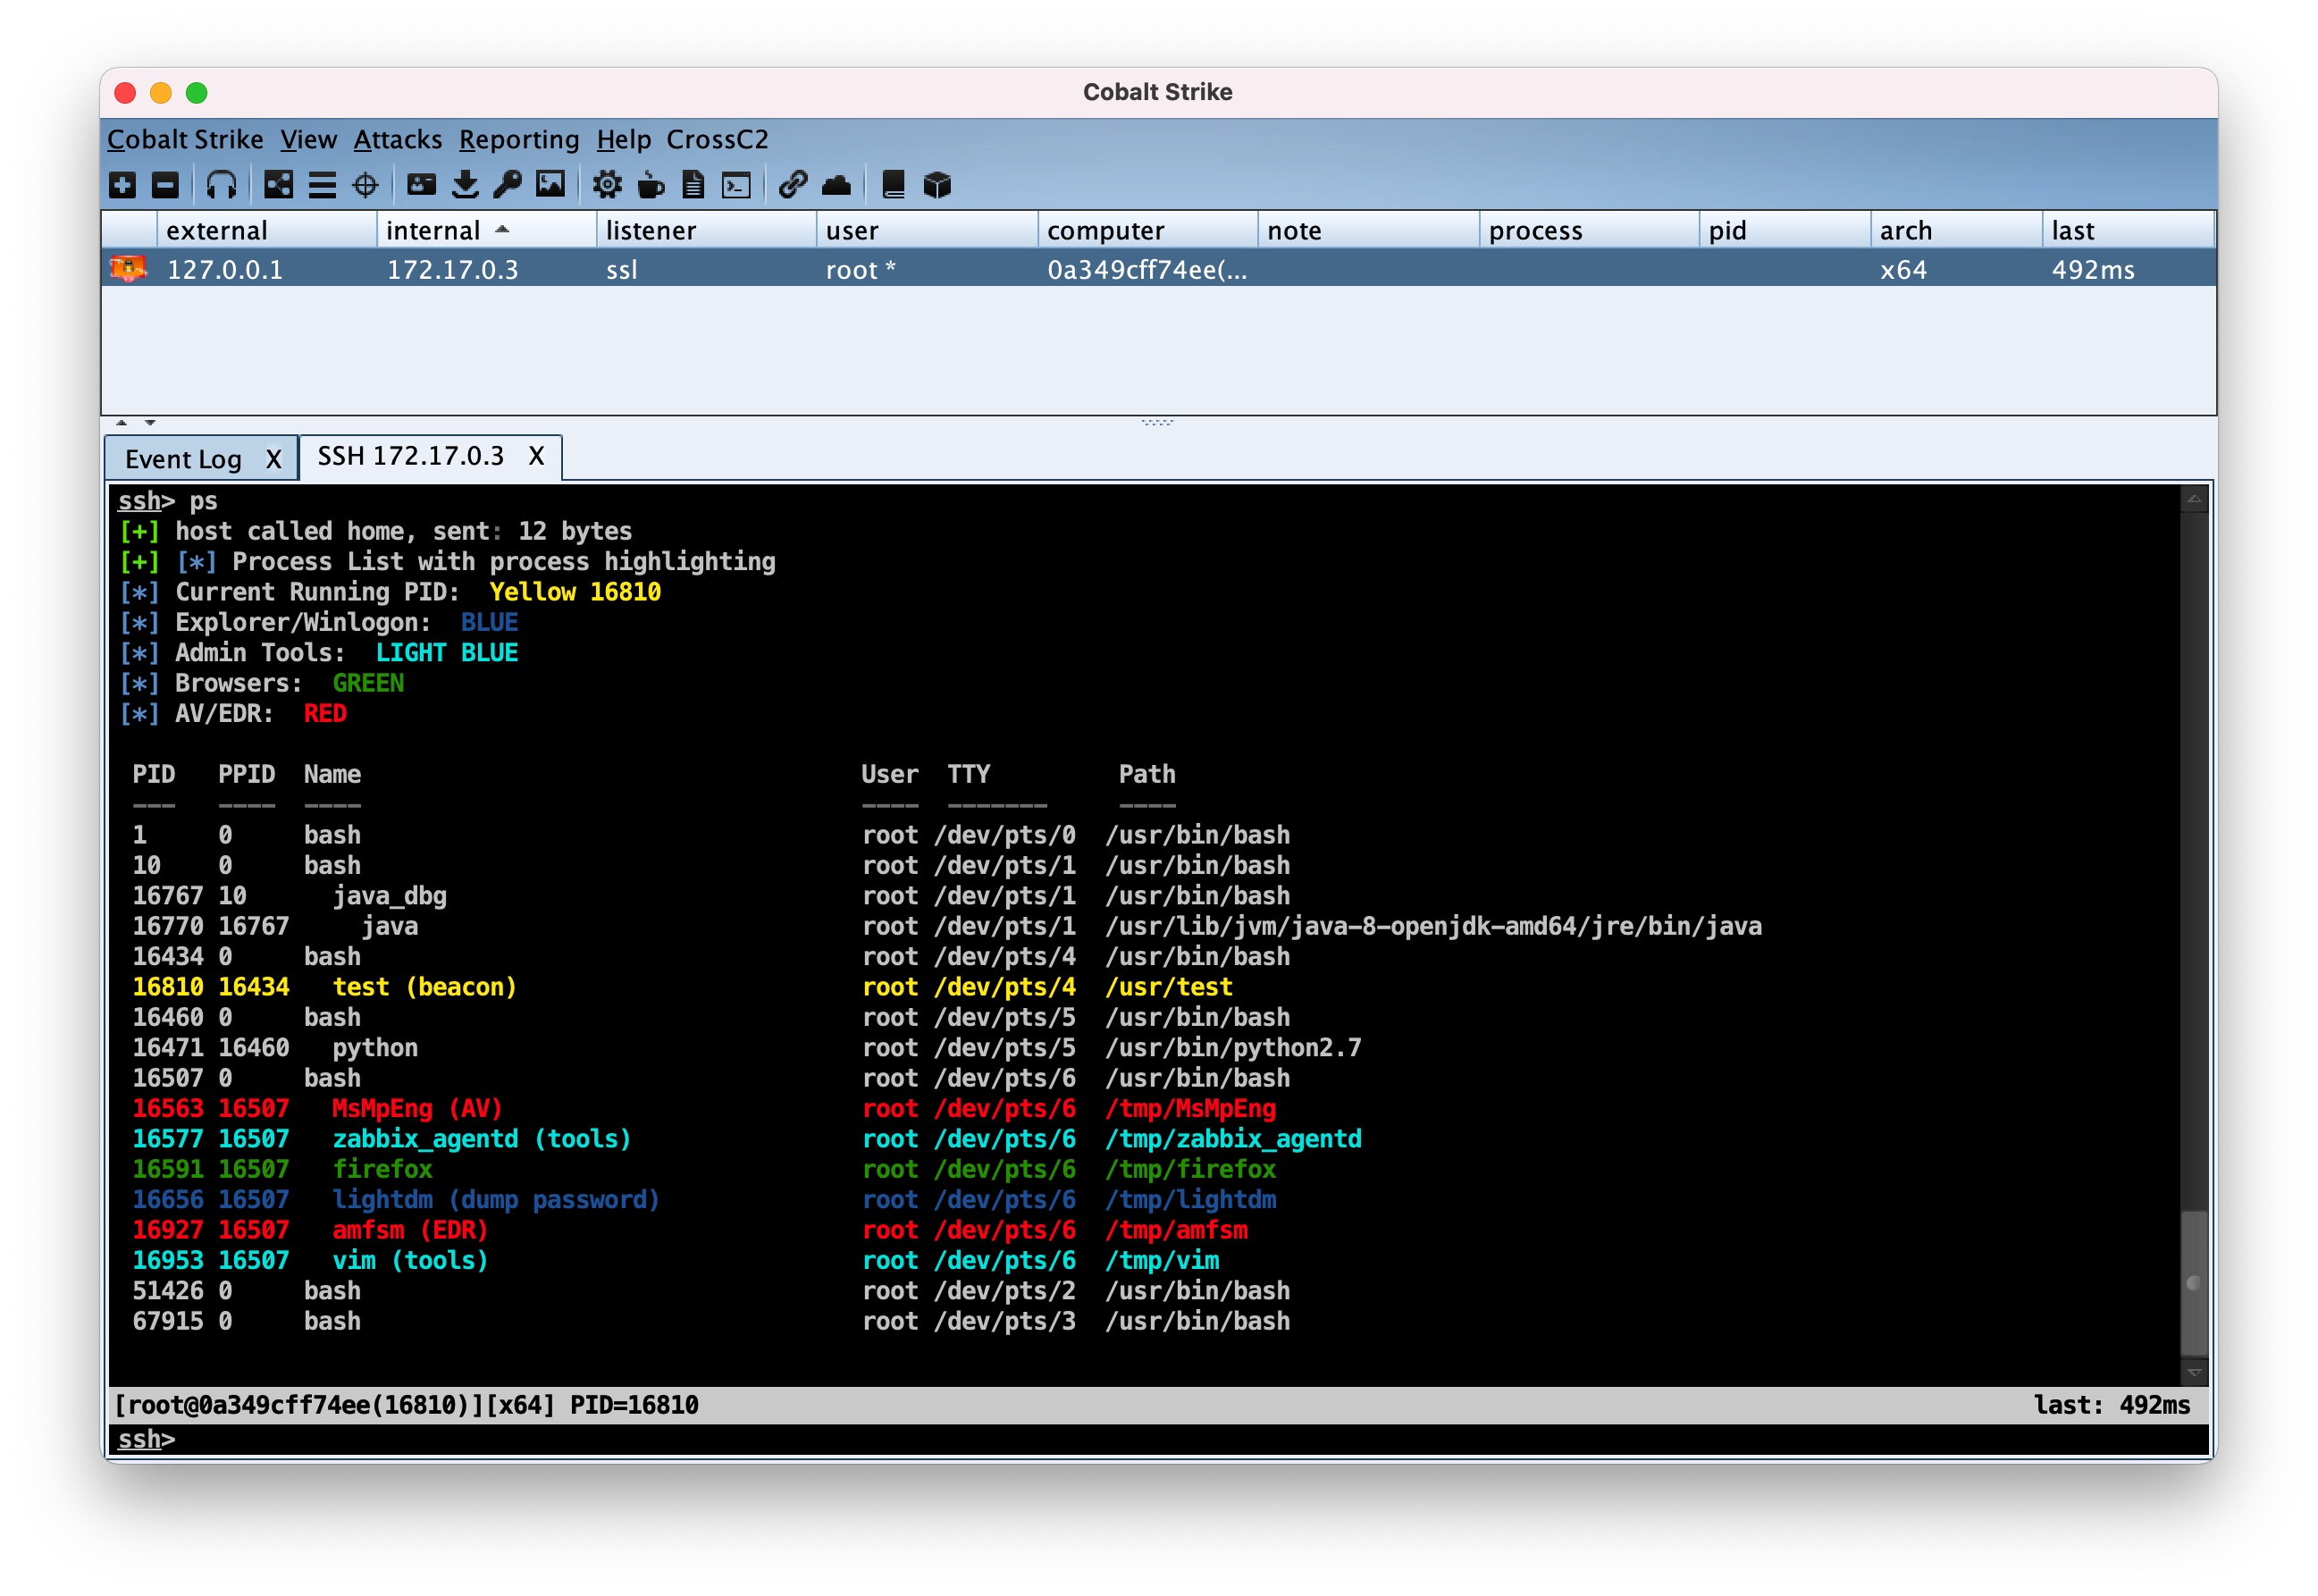
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.

Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…

Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)

CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer