
awesome-dfir-skills
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
323
tsale/awesome-dfir-skillsA curated collection of DFIR skills and workflows for InfoSec practitioners.
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
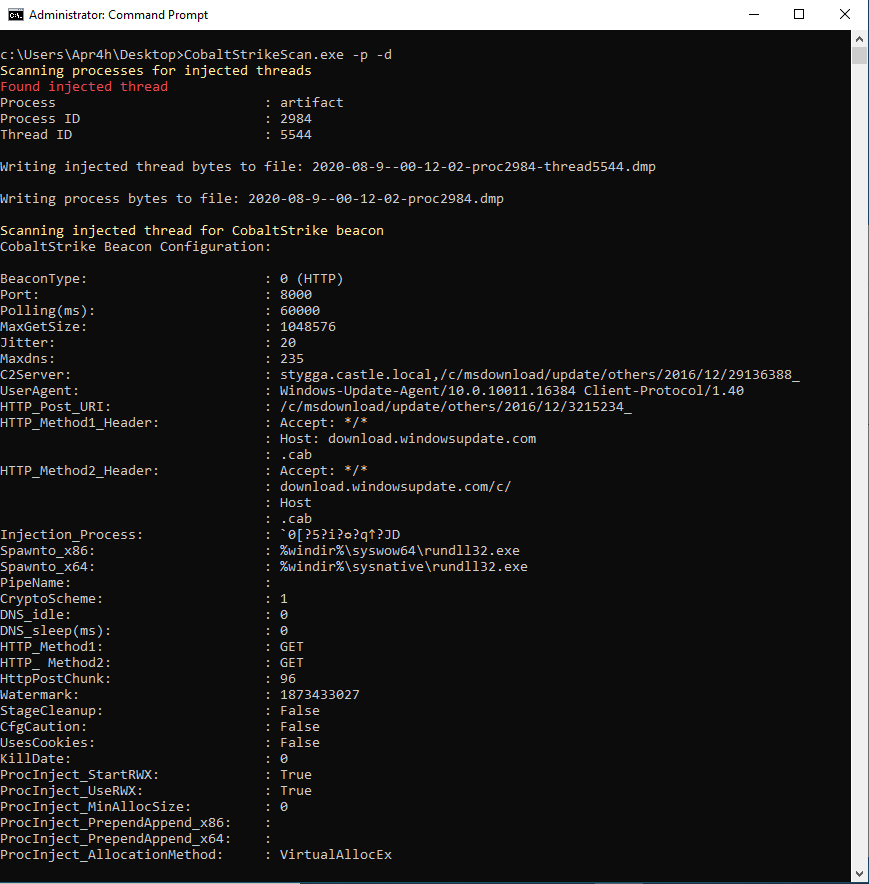 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 sandi-go/cve-2018-12798
Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd

 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 sprushed/cve-2022-30292
Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
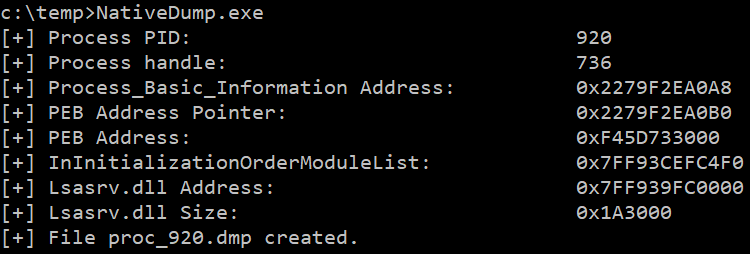 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 s1lkys/cve-2023-30367-mremoteng-password-dumper
Original PoC for CVE-2023-30367