
LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
2.0k
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 nccgroup/killedprocesscanary
A canary designed to minimize the impact from certain Ransomware actors
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 encrypter15/cve-2025-30400
Educational Python model demonstrating a Use-After-Free (UAF) privilege escalation vulnerability inspired by CVE-2025-30400 in Windows DWM. Simulates…
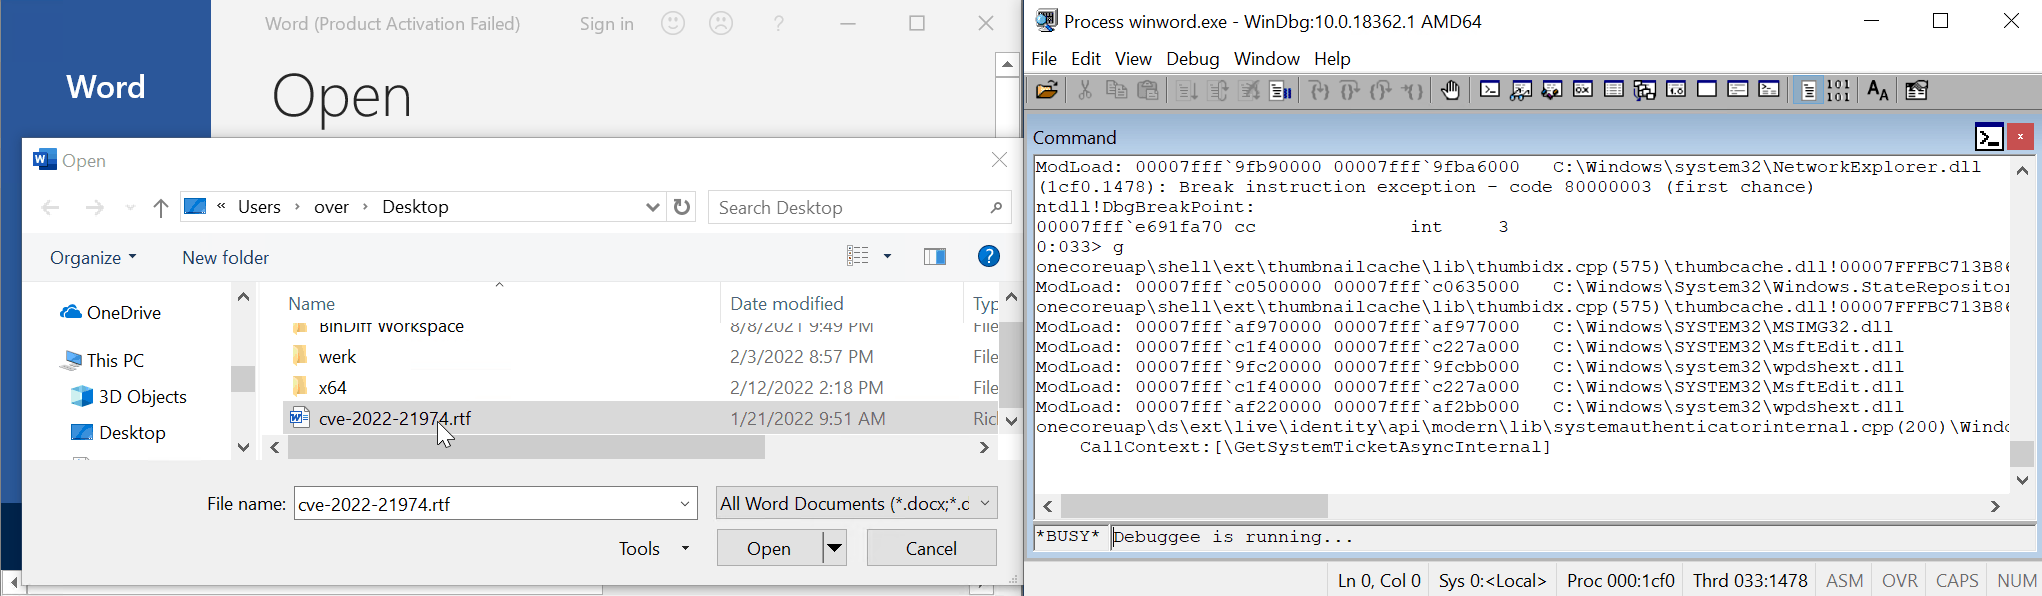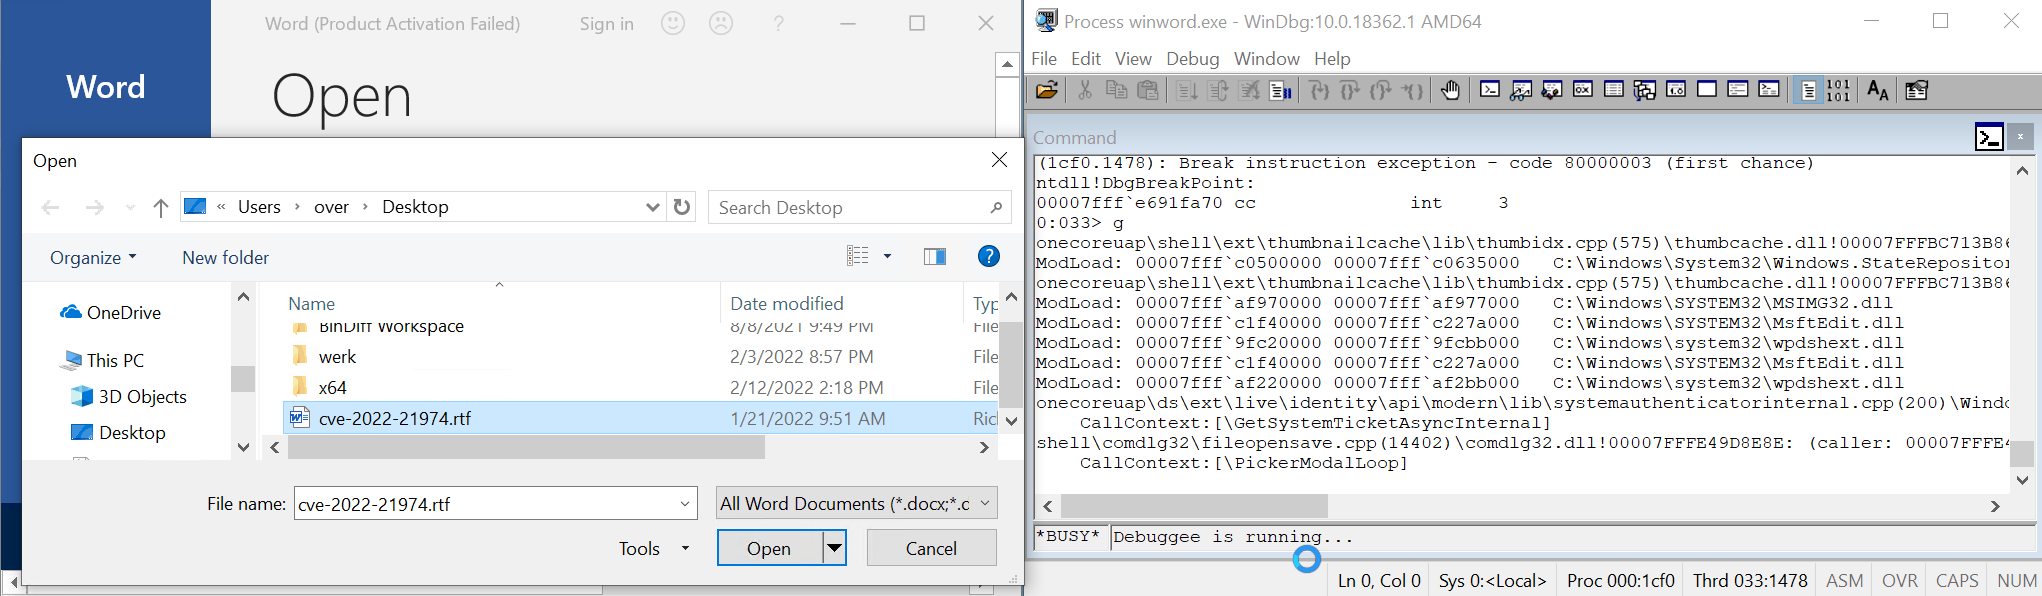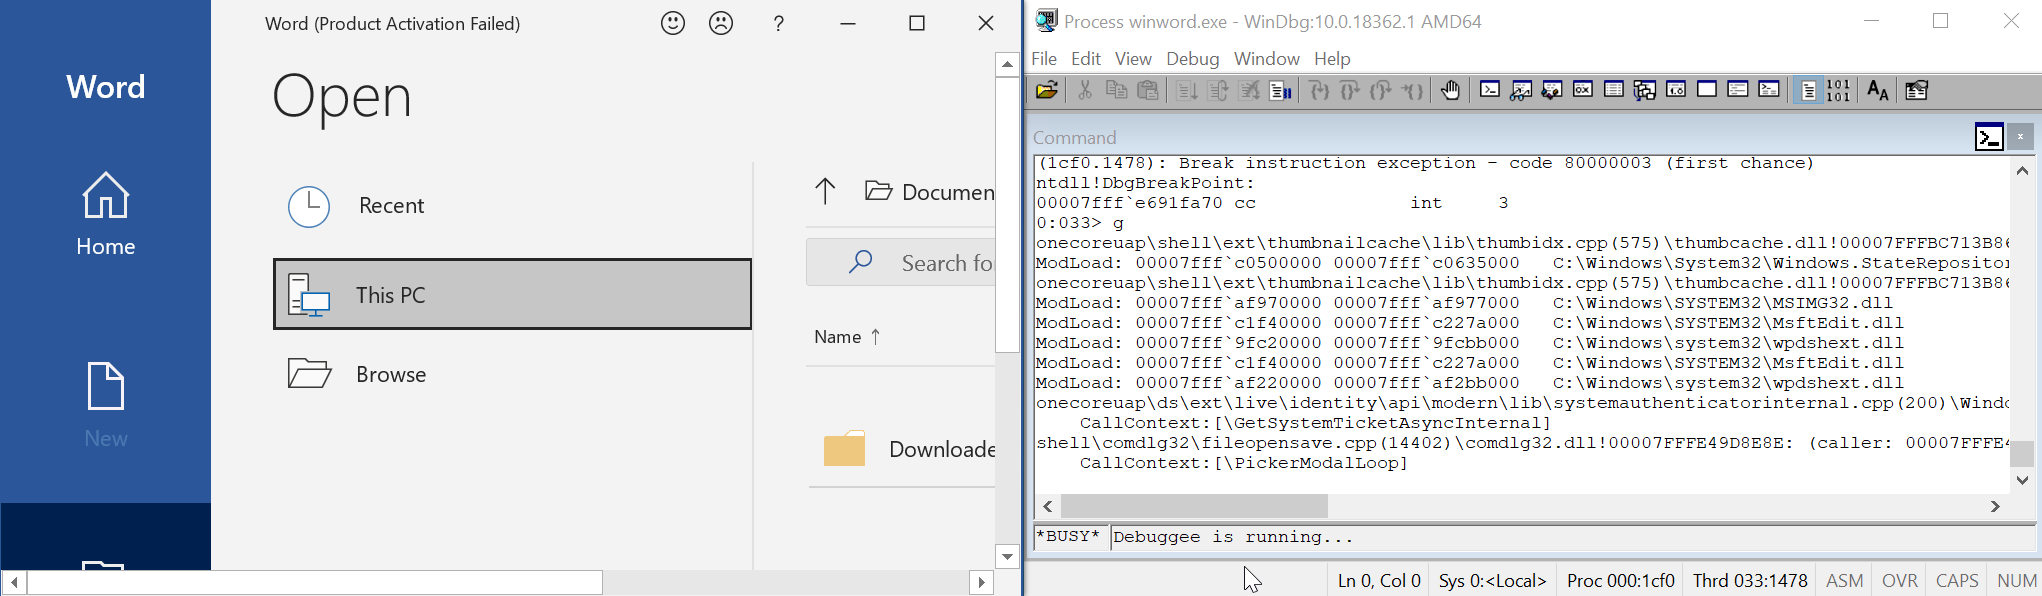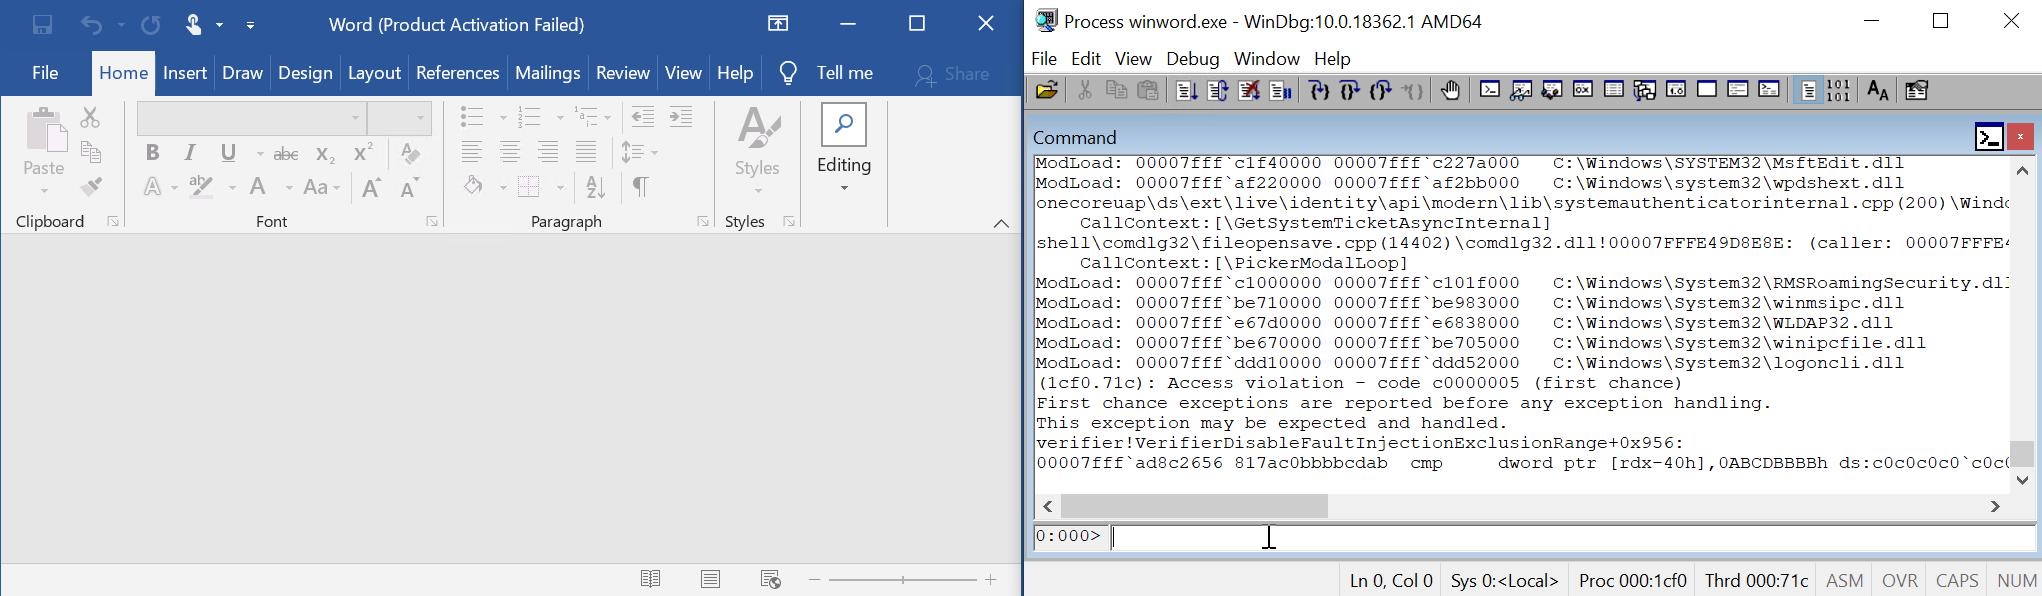 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 ping-2o/ios.cve-2026-84616-84607
research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
 parapapinho/cve-2017-12561
Reverse-engineering write-up and proof of concept for CVE-2017-12561, a use-after-free in HPE iMC dbman, covering binary diffing, ASN.1 decoding, and…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks