
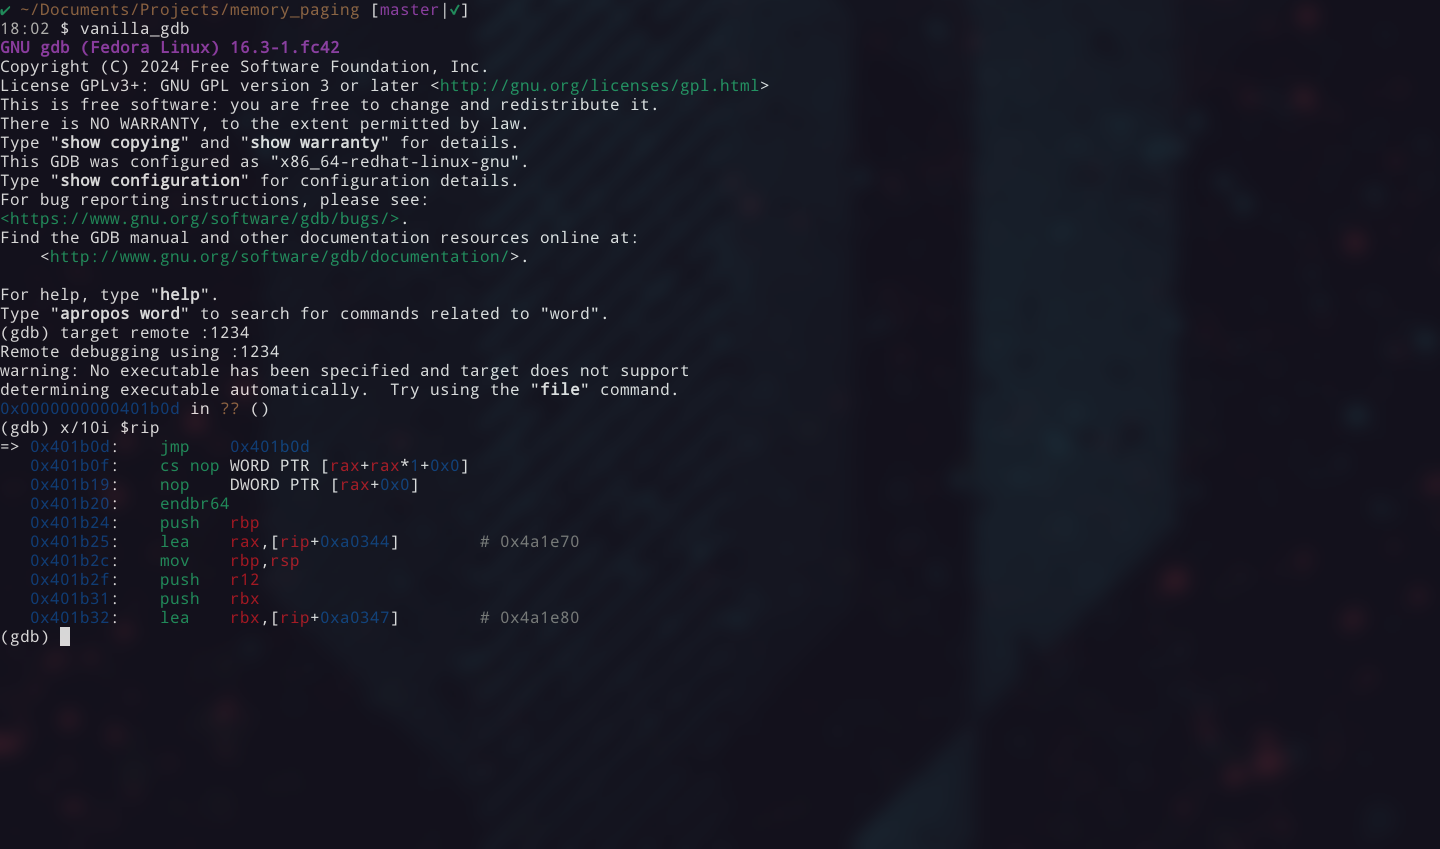
page_table_walk
 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
binary-analysisctfdebuggers+4
28
jazho76/page_table_walkWalk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 blendin/3snake
Tool for extracting information from newly spawned processes
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.