frida-il2cpp-datacollector

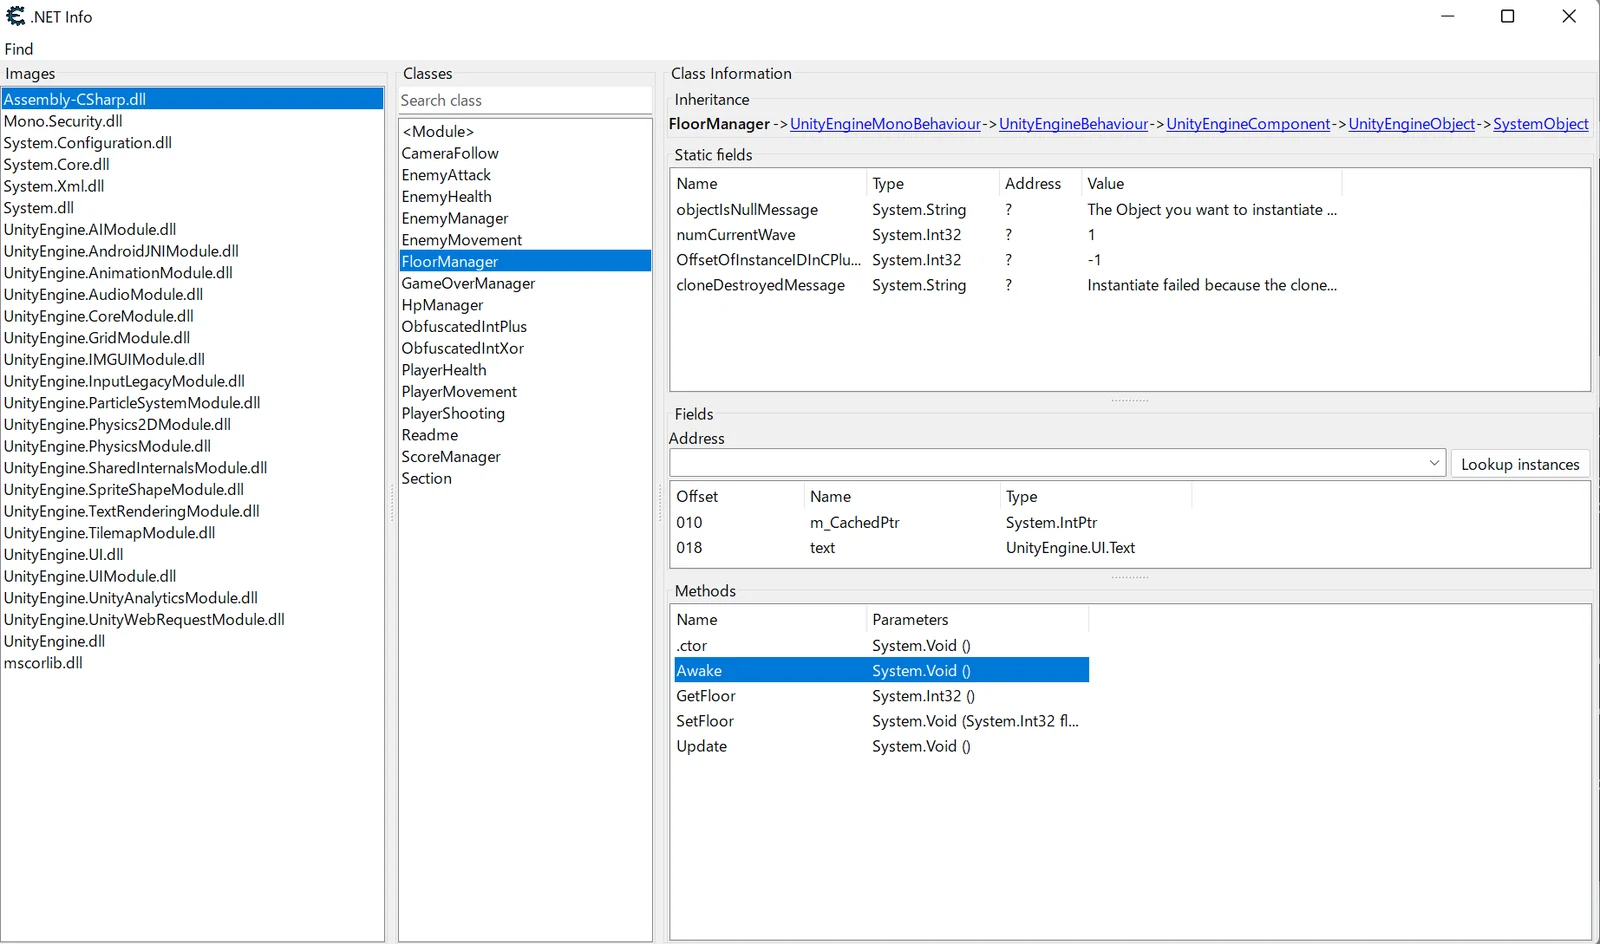
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…

This is POC for IOS 0click CVE-2025-43300

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…

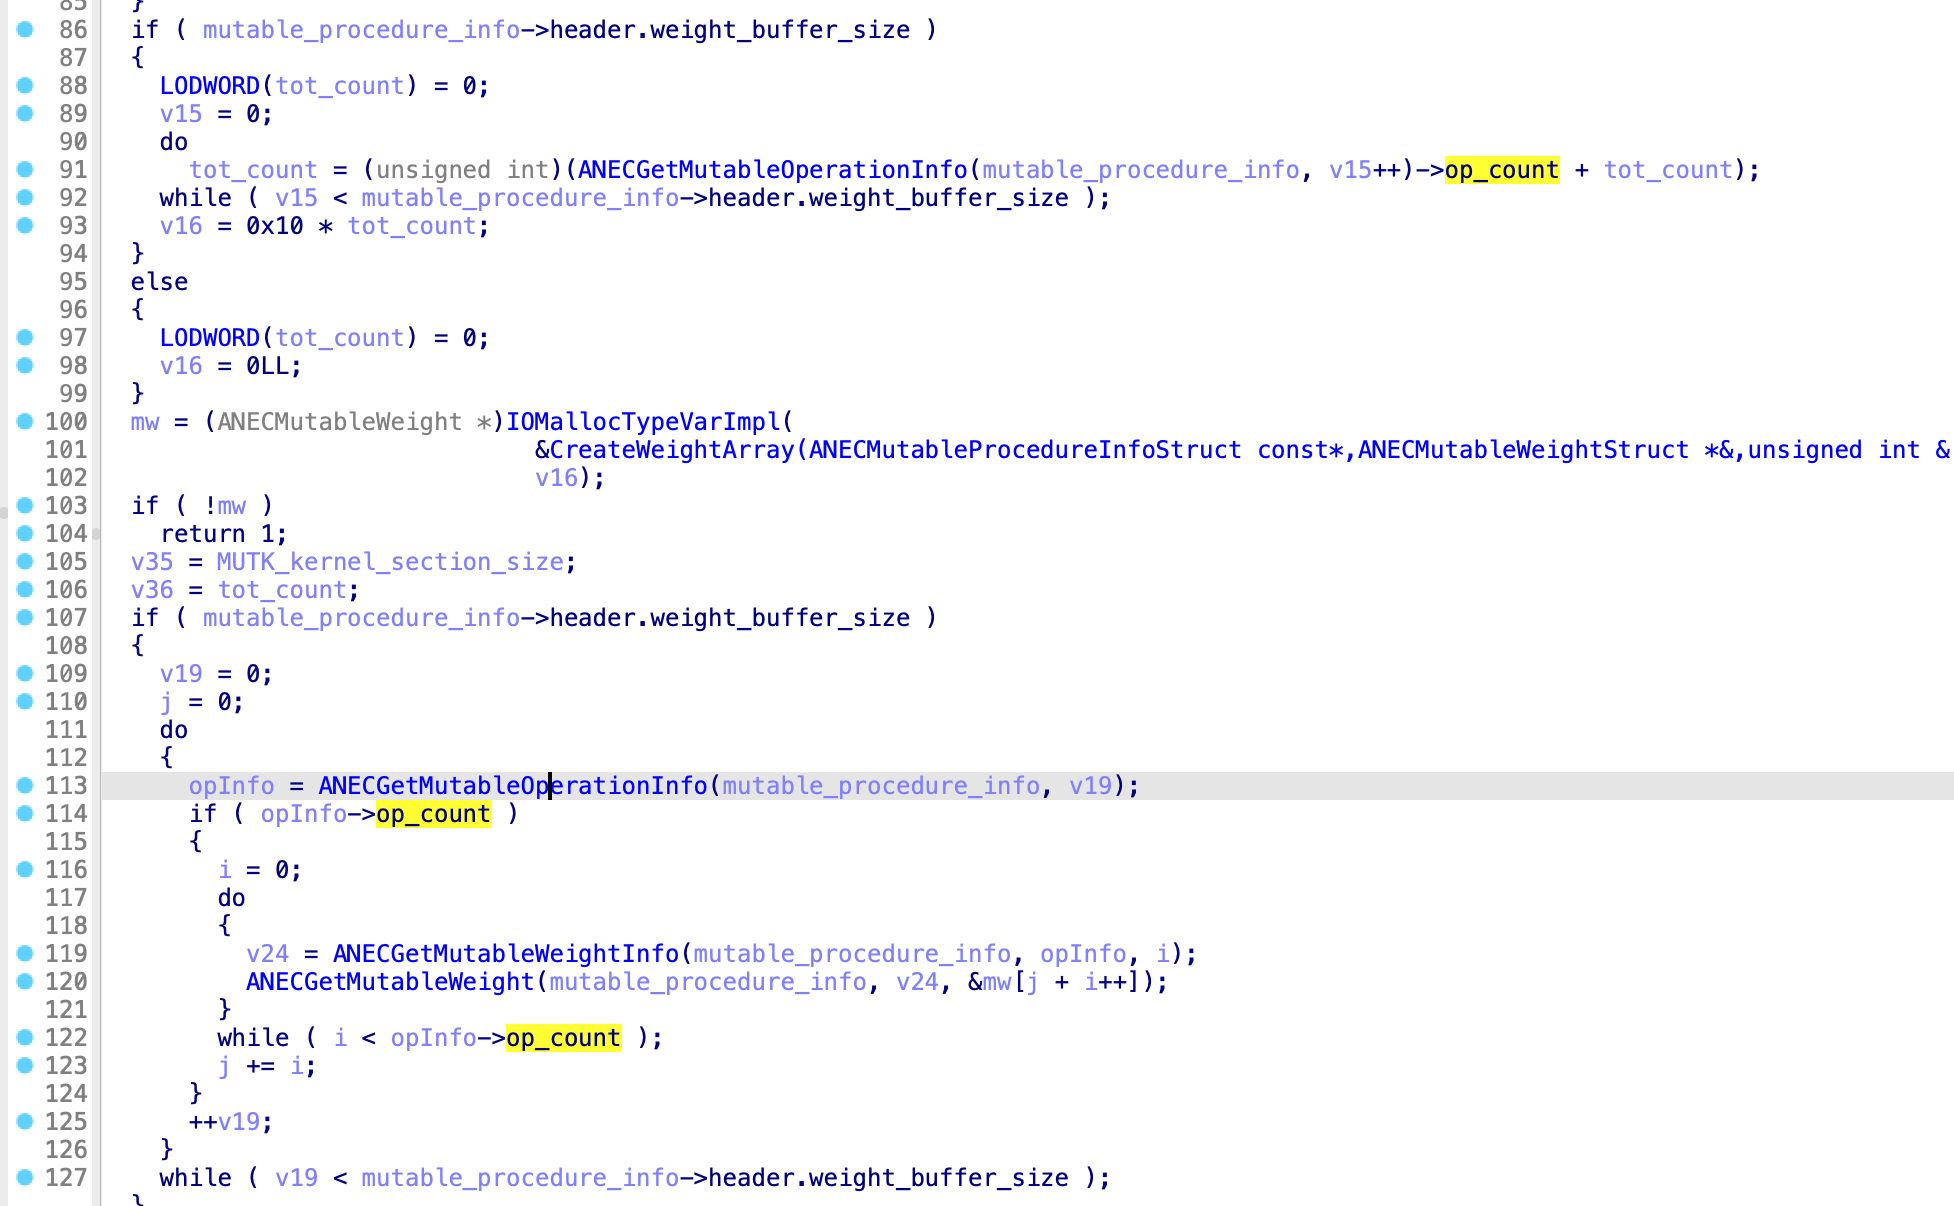
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…

iOS 14 kernel exploit for CVE-2021-30807 targeting IOMobileFramebuffer, with tunable memory allocation for jailbreak development on A11+ devices.

empty_list - exploit for p0 issue 1564 (CVE-2018-4243) iOS 11.0 - 11.3.1 kernel r/w

CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.

CVE-2026-20687: AppleJPEGDriver startDecoder Timeout UAF — iOS/macOS kernel vulnerability leading to deferred panic (A19 Pro, iOS 26.3 RC)

Ian Beer's exploit for CVE-2017-2370 (kernel memory r/w on iOS 10.2)

CVE-2025-43300: iOS/macOS DNG Image Processing Memory Corruption

Public disclosure for CVE-2026-43655 AppleM2ScalerCSCDriver use-after-free

Proof-of-concept for CVE-2023-41992, a macOS kernel vulnerability, demonstrating exploitation techniques and providing a patch analysis.

PoC for CVE-2026-28990, an ImageIO bug patched in iOS/macOS 26.5

MacOS kernel memory leak (4 bytes)