
hollows_hunter
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
defensive-toolsforensicsincident-response+2
2.4k
hasherezade/hollows_hunterScans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
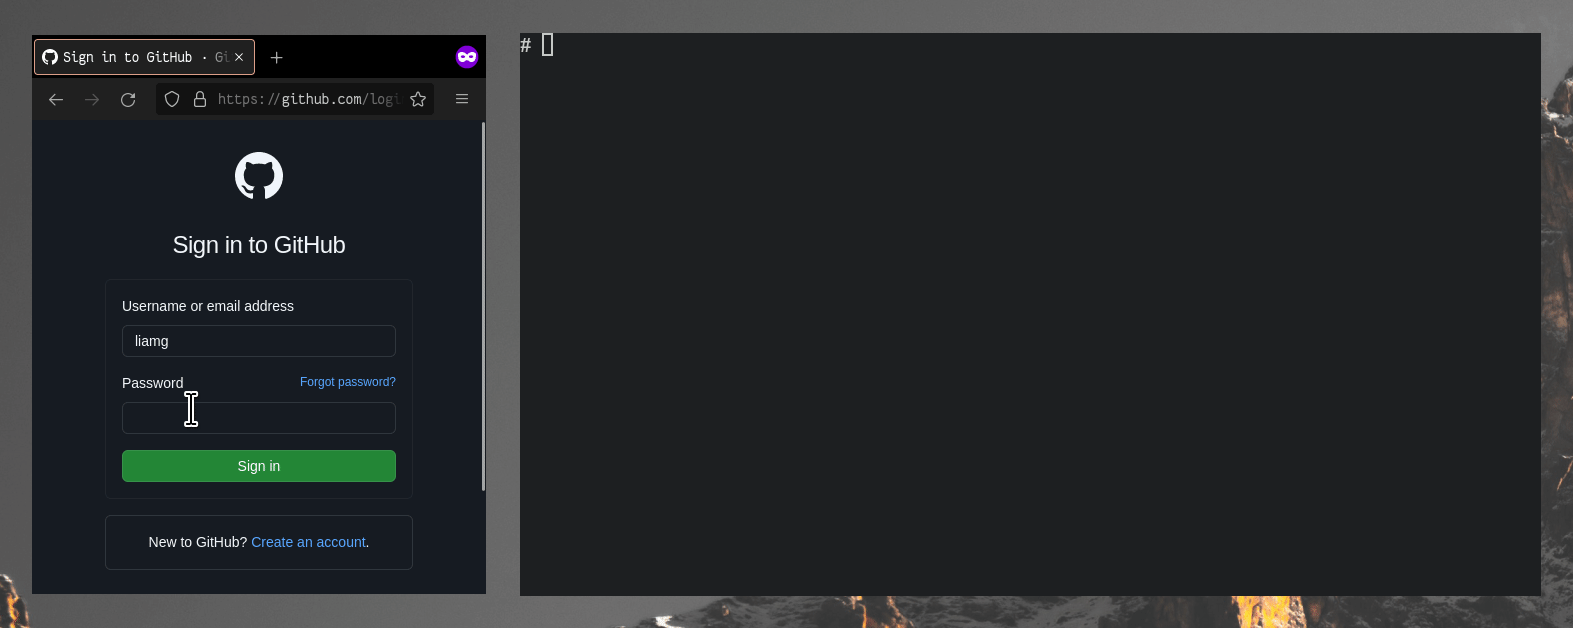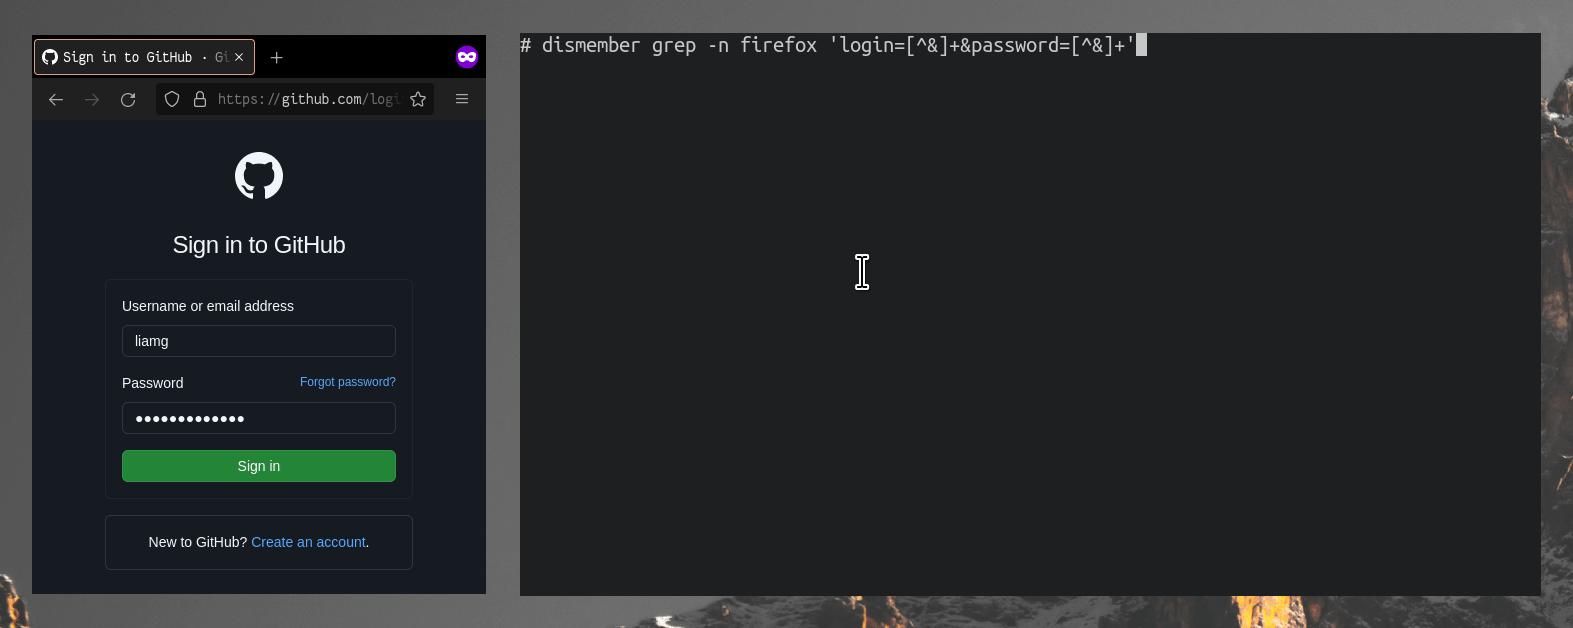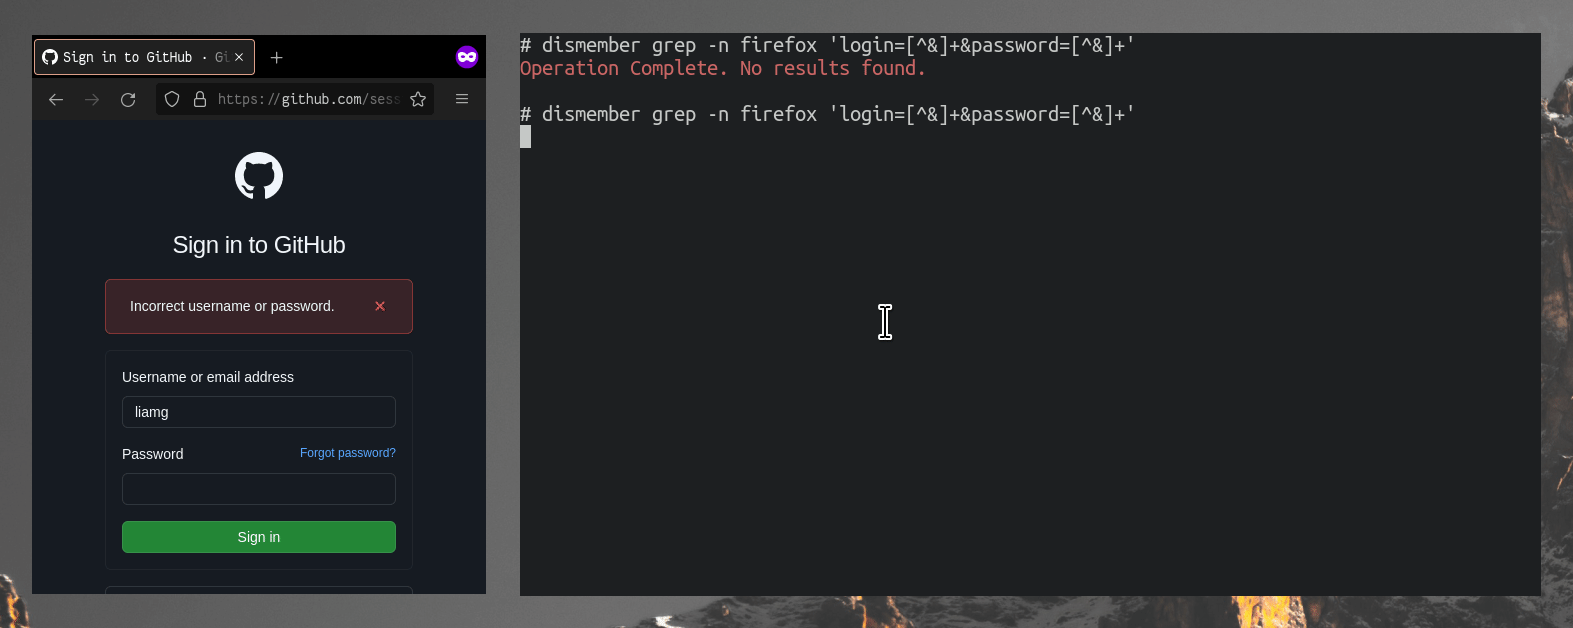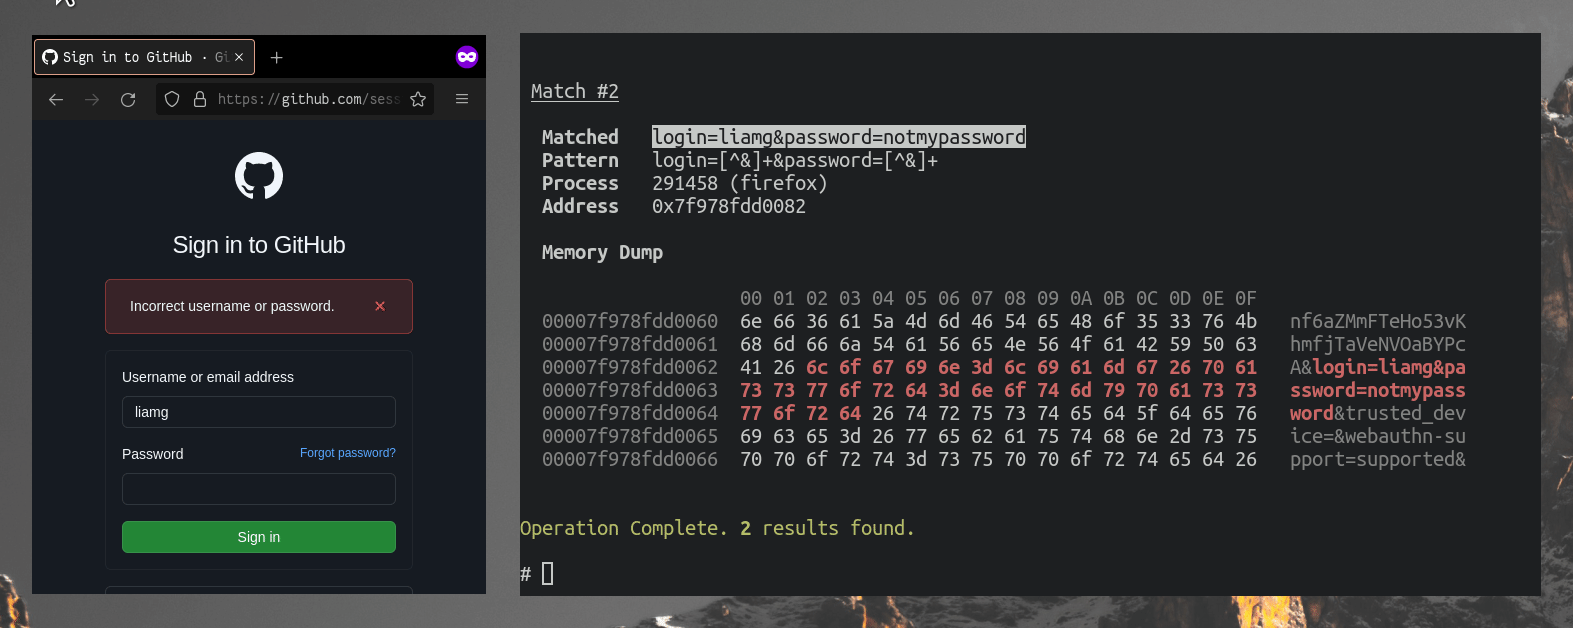 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
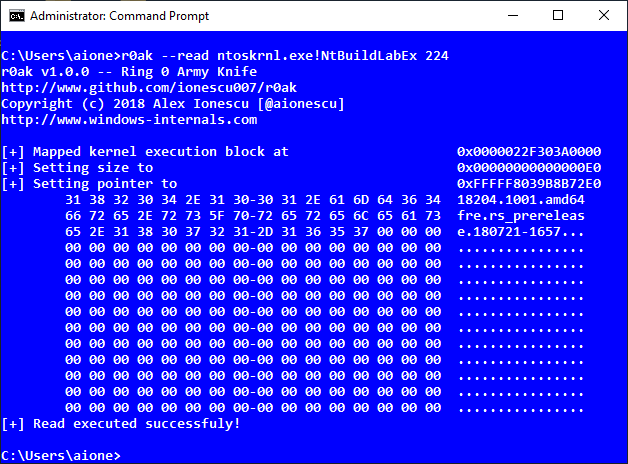 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework