
CVE-2025-7771
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
binary-exploitationexploitationmemory-forensics+3
1
lzty/cve-2025-7771Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 rainbowdynamix/ghostkatz
Dump LSASS via physical memory read primitives in vulnerable kernel drivers
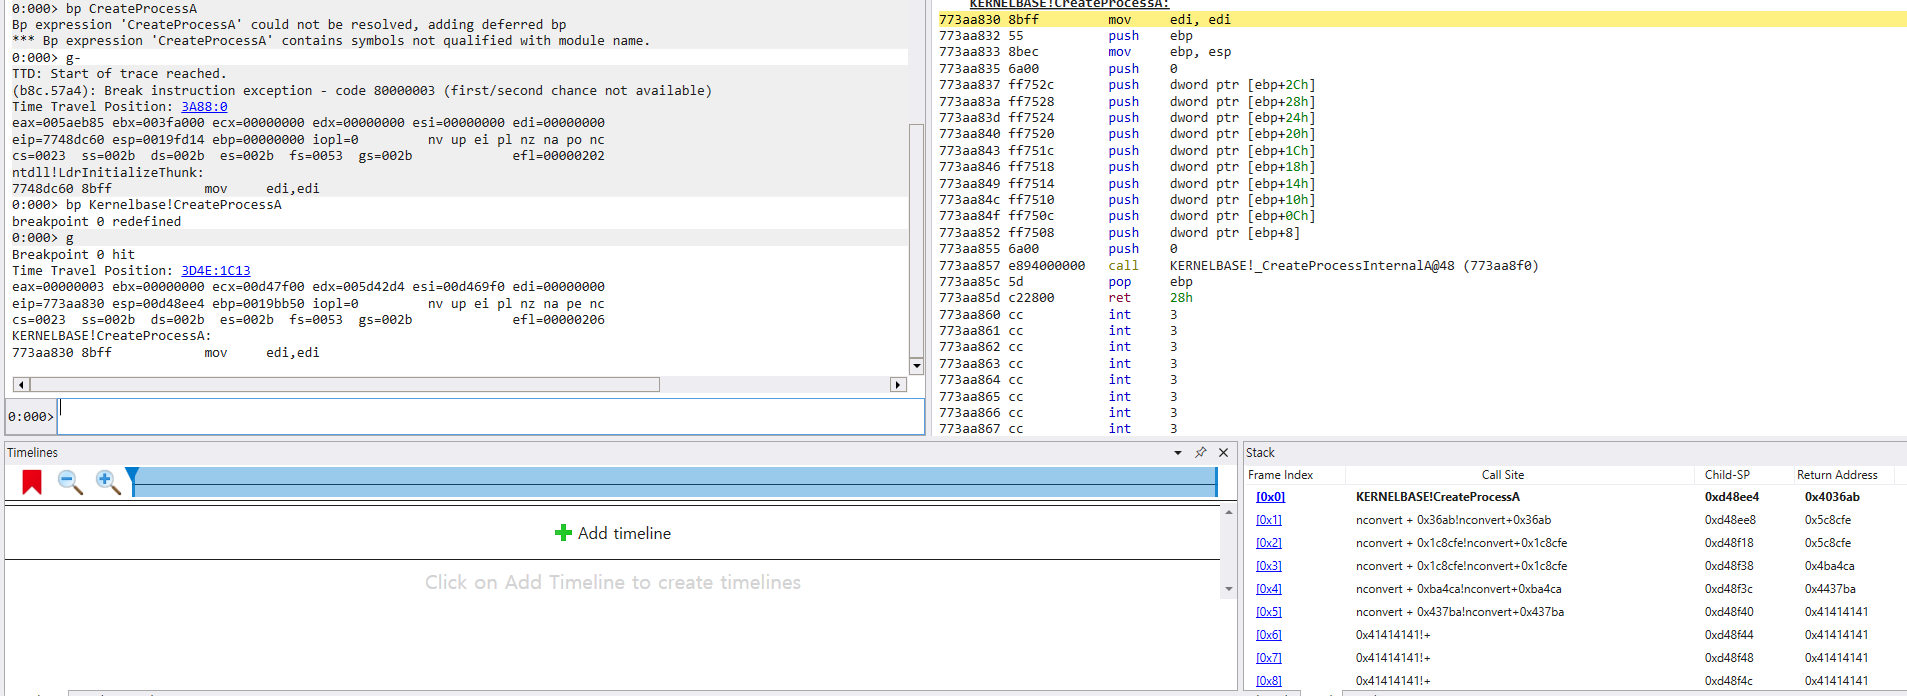 pwndorei/cve-2024-22532
Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 erikdervishi03/cve-2026-31024
Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 jailbreaks/empty_list
empty_list - exploit for p0 issue 1564 (CVE-2018-4243) iOS 11.0 - 11.3.1 kernel r/w
 spawn451/cve-2025-8061-exploit
Exploit LnvMSRIO.sys vulnerable driver
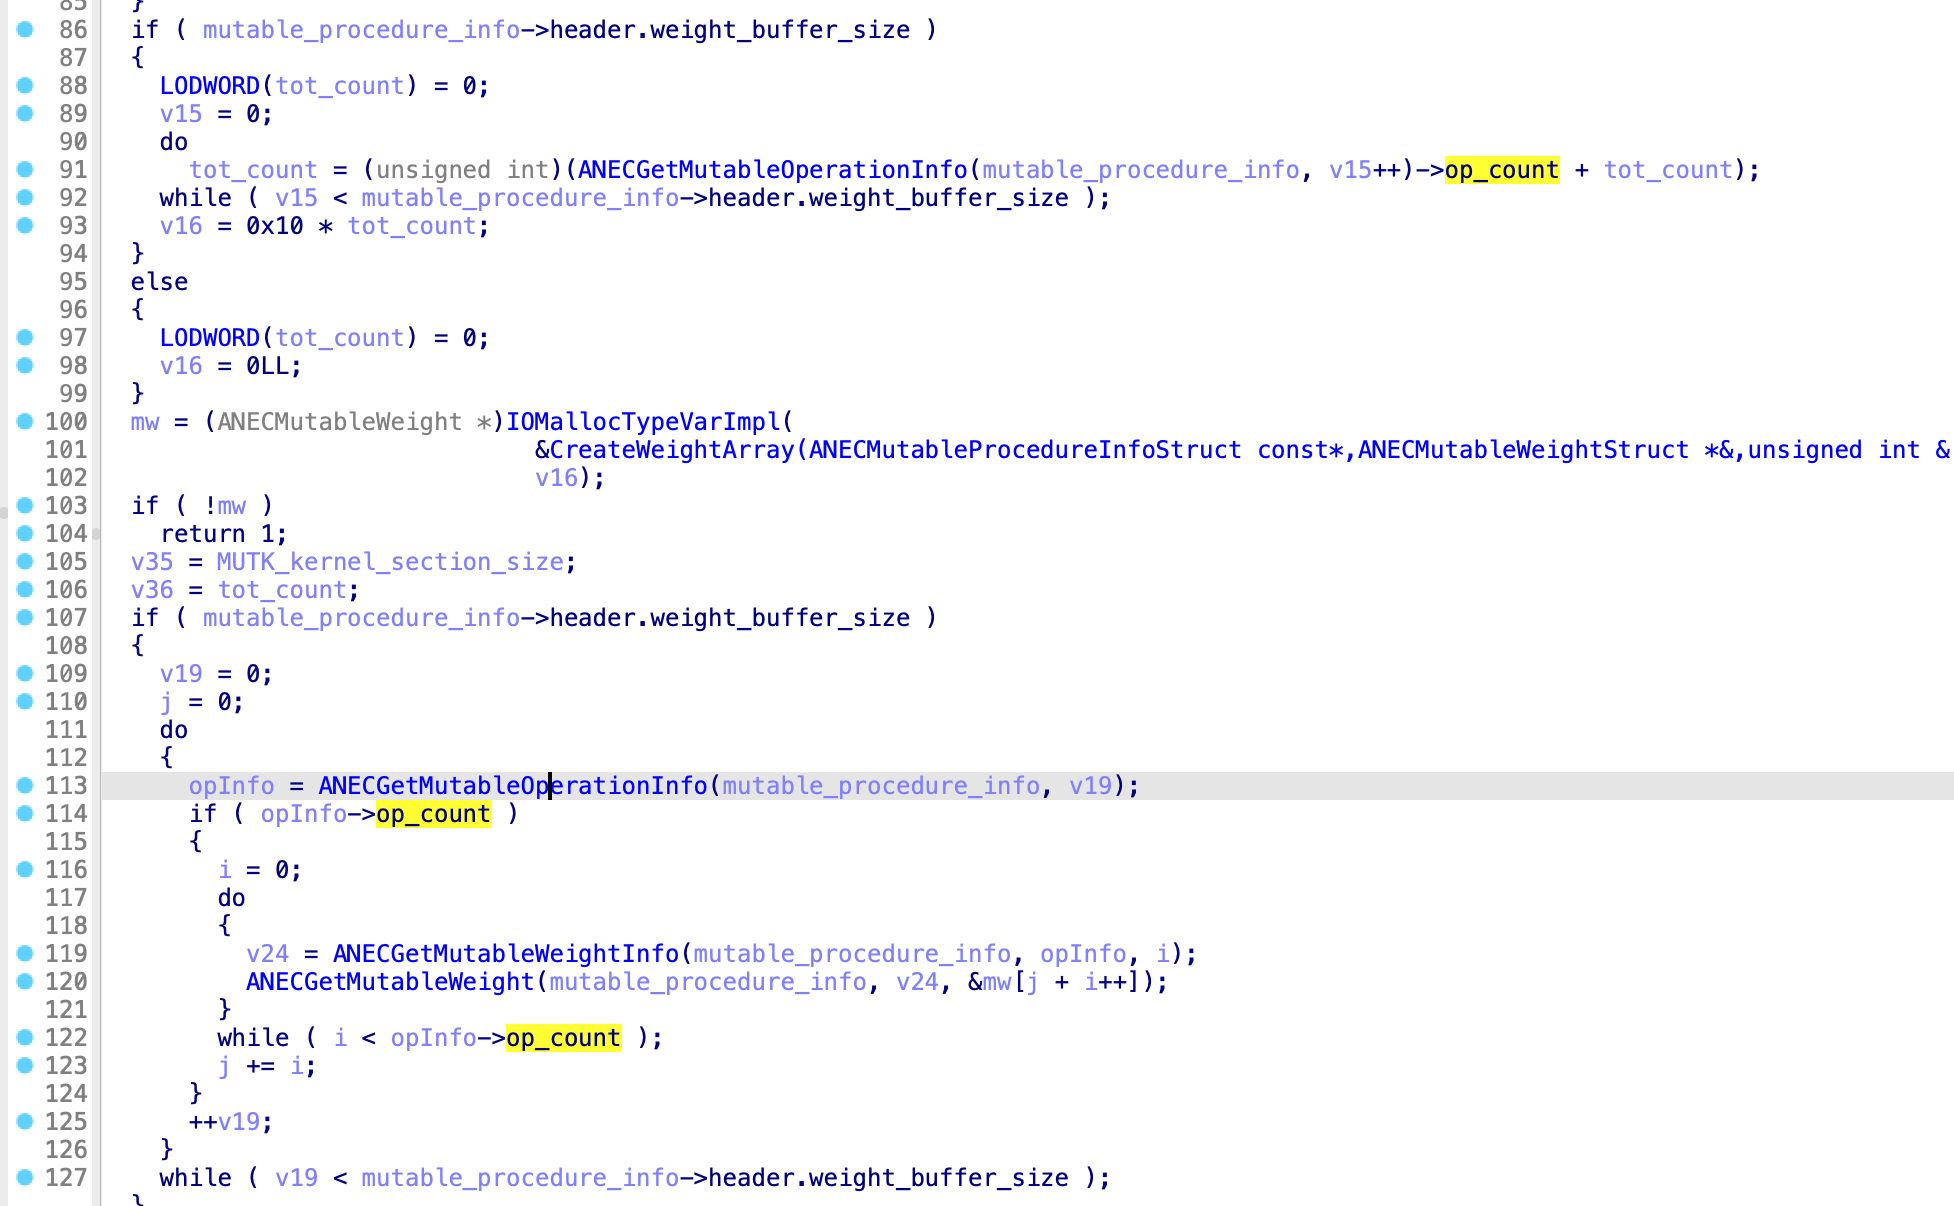 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
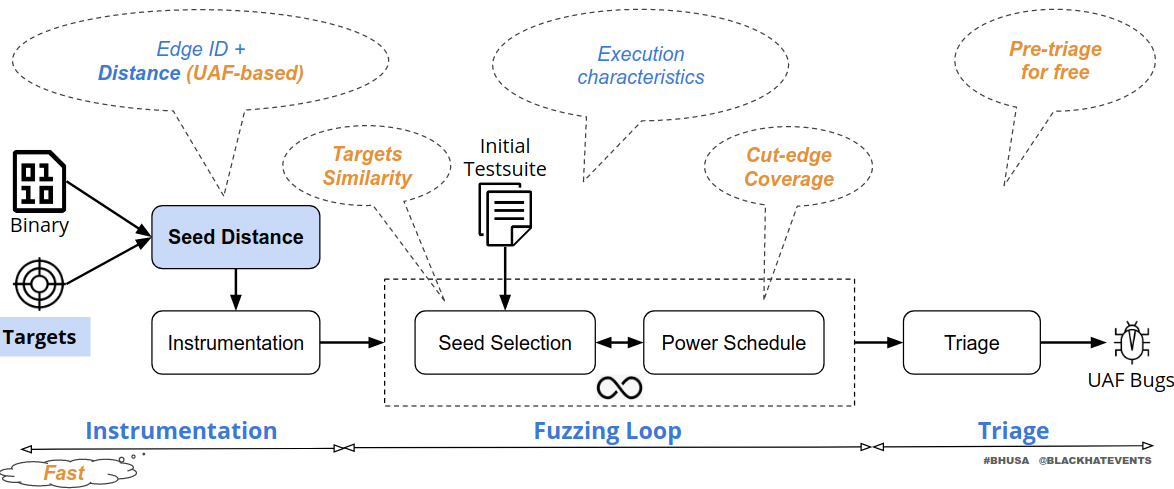 strongcourage/uafuzz
Binary-level directed fuzzer specialized in detecting Use-After-Free vulnerabilities via ordering-aware input metrics and static analysis, enabling…
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
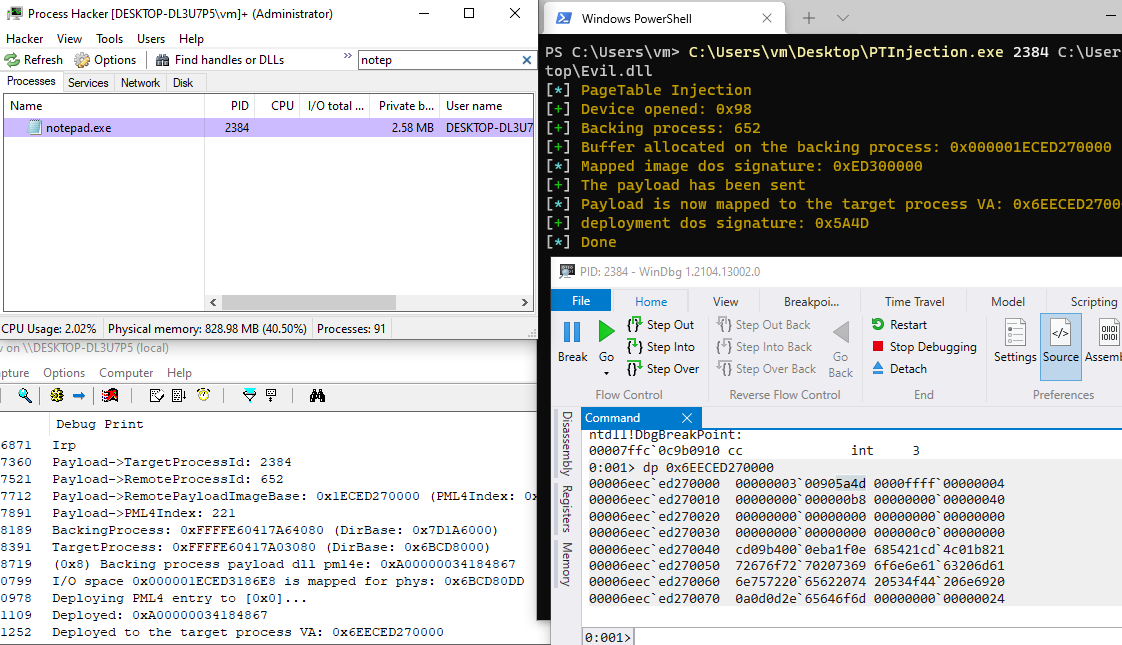 kkent030315/pagetableinjection
Code Injection, Inject malicious payload via pagetables pml4.
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215