

IRTriage
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
digital-forensicsforensicsincident-response+1
ajmartel/irtriageIncident Response Triage - Windows Evidence Collection for Forensic Analysis
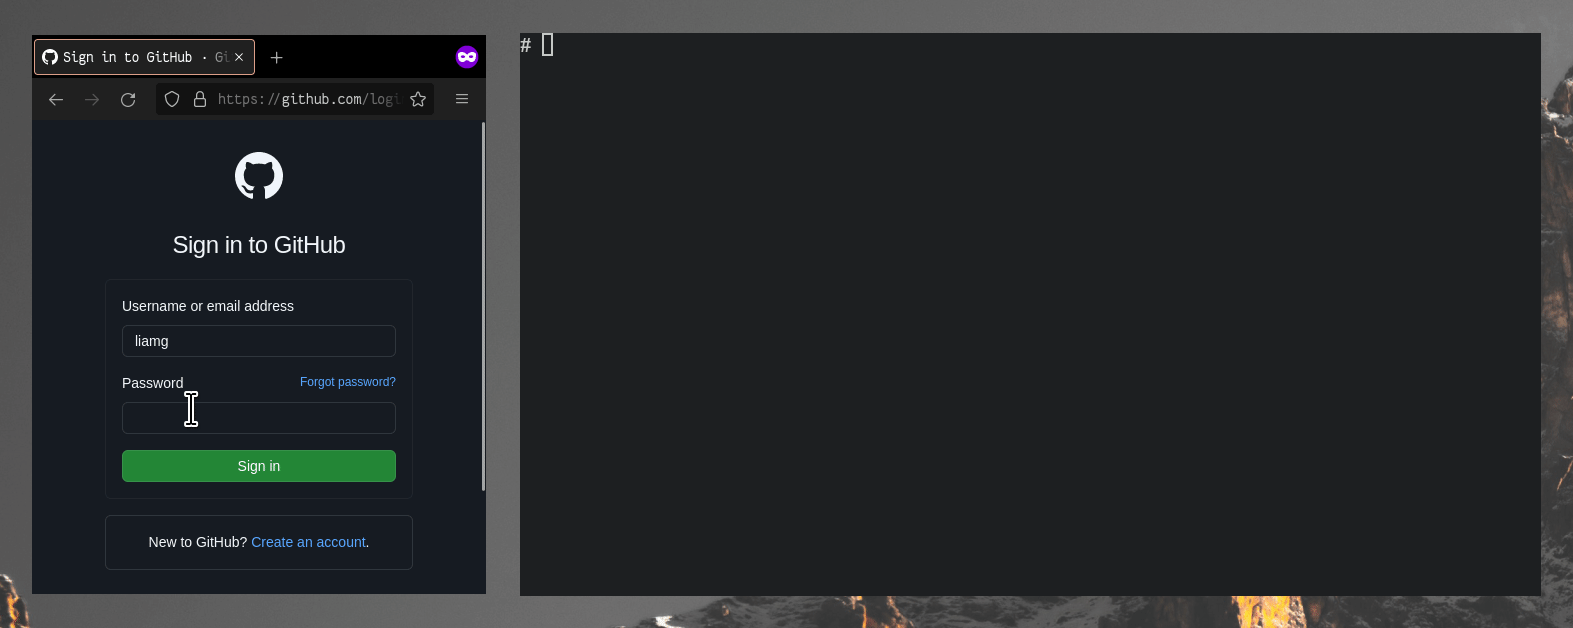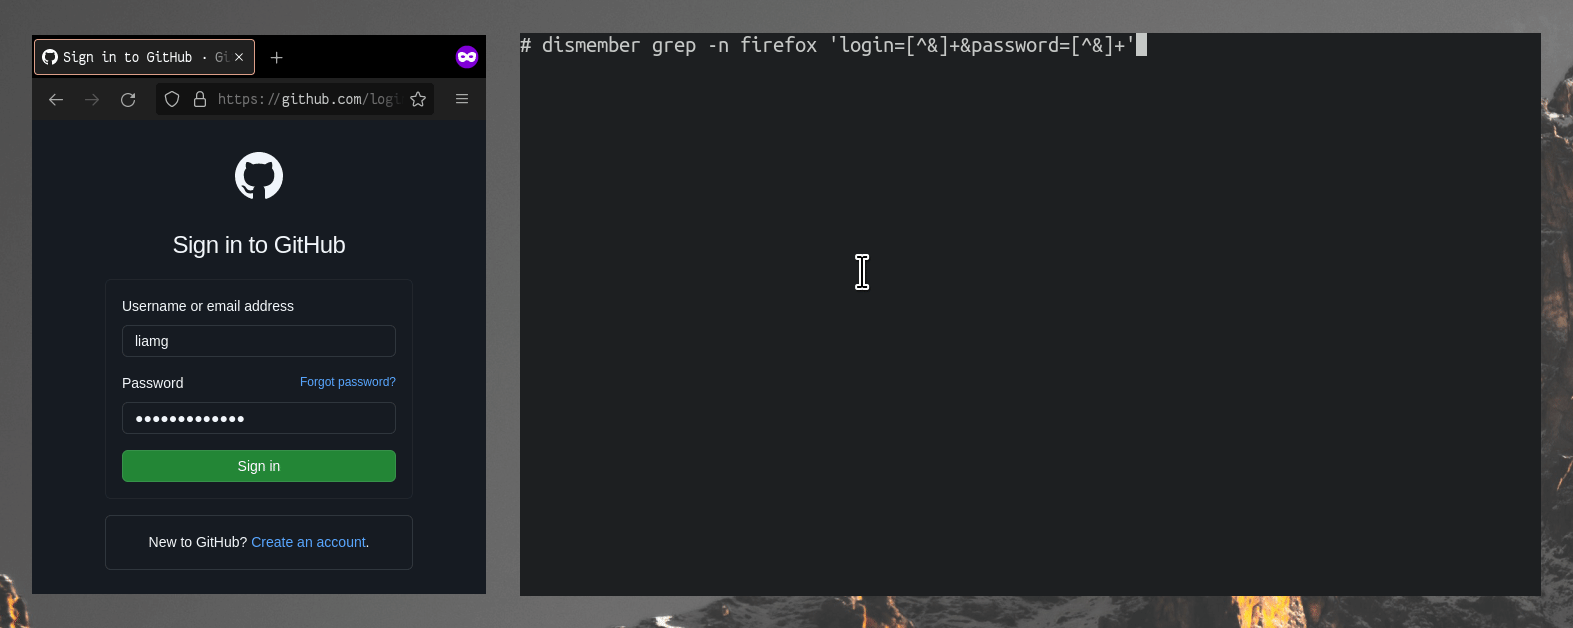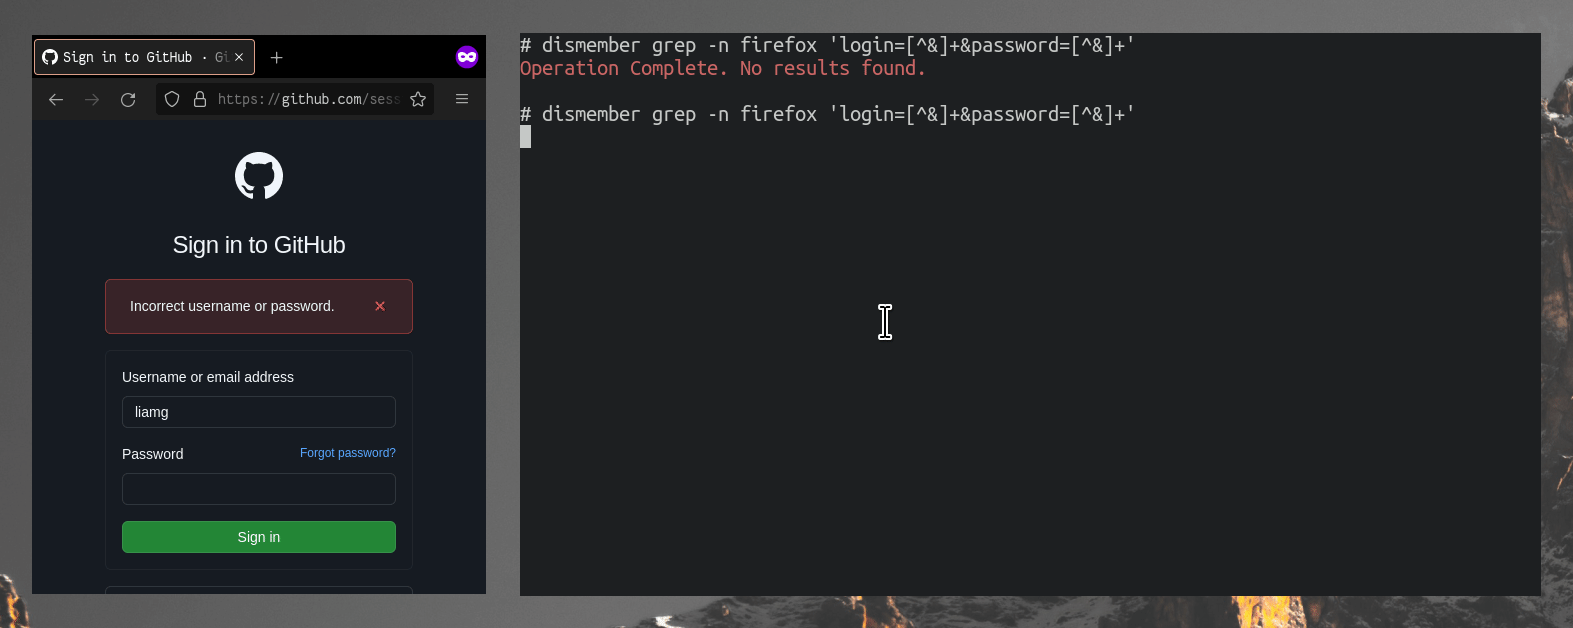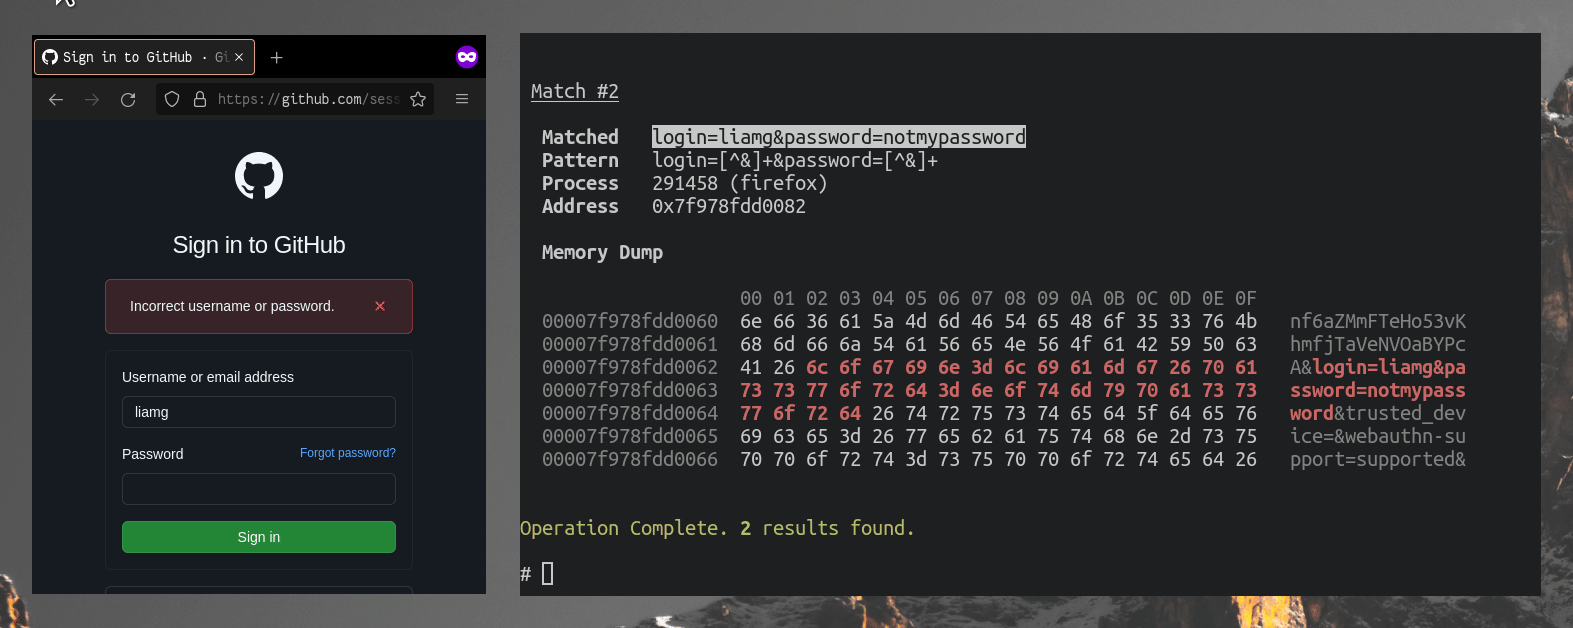 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 nickcano/xenoscan
Open source memory scanner written in C++
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
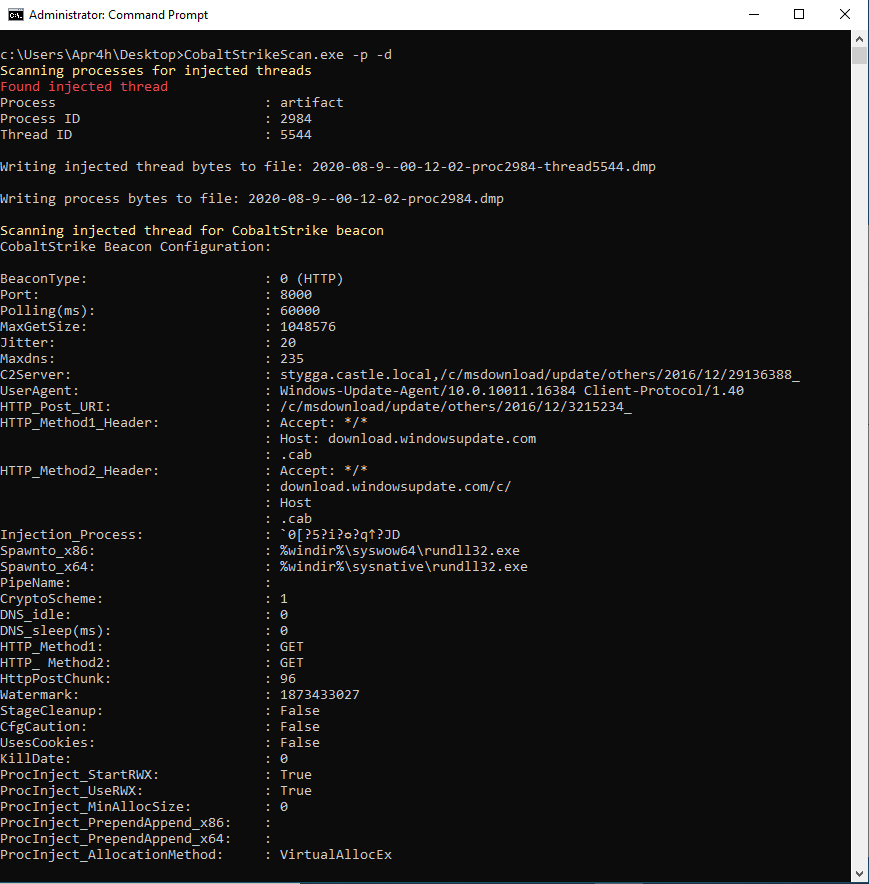 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.
 cristianzsh/forensictools
Collection of forensic tools
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 volatilityfoundation/volatility
An advanced memory forensics framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
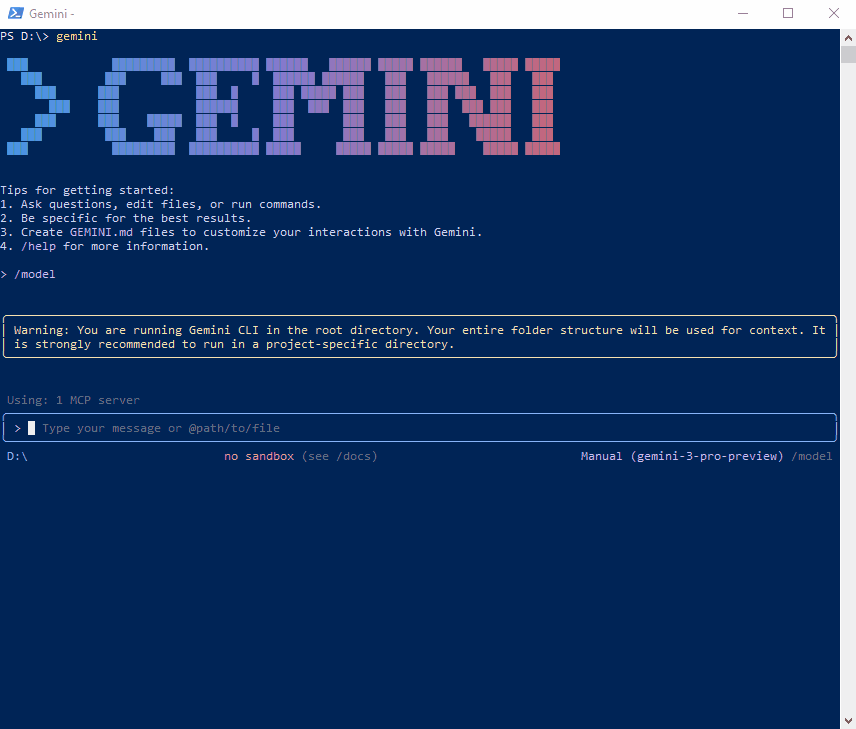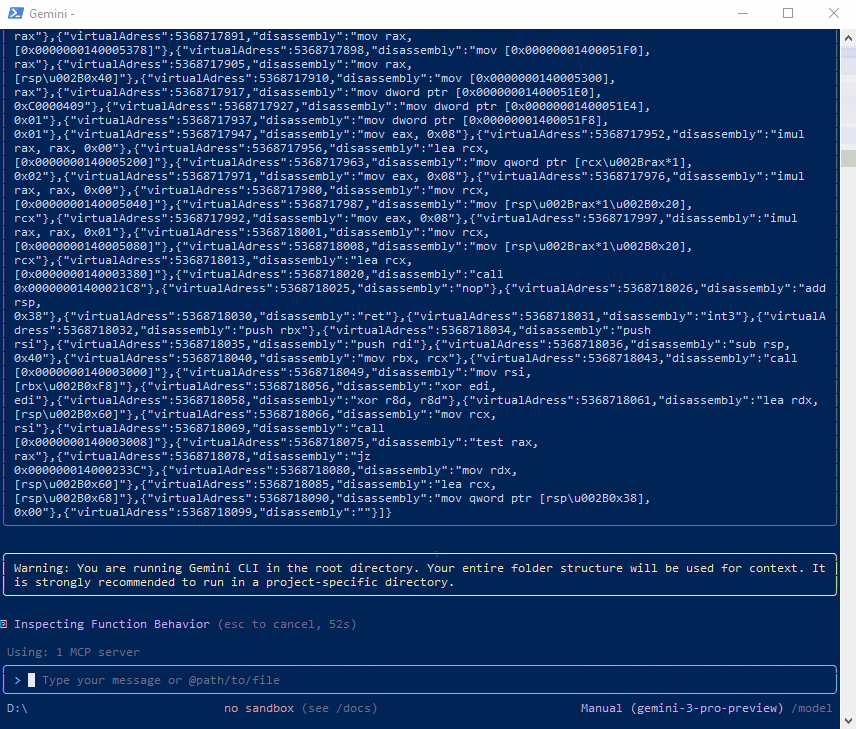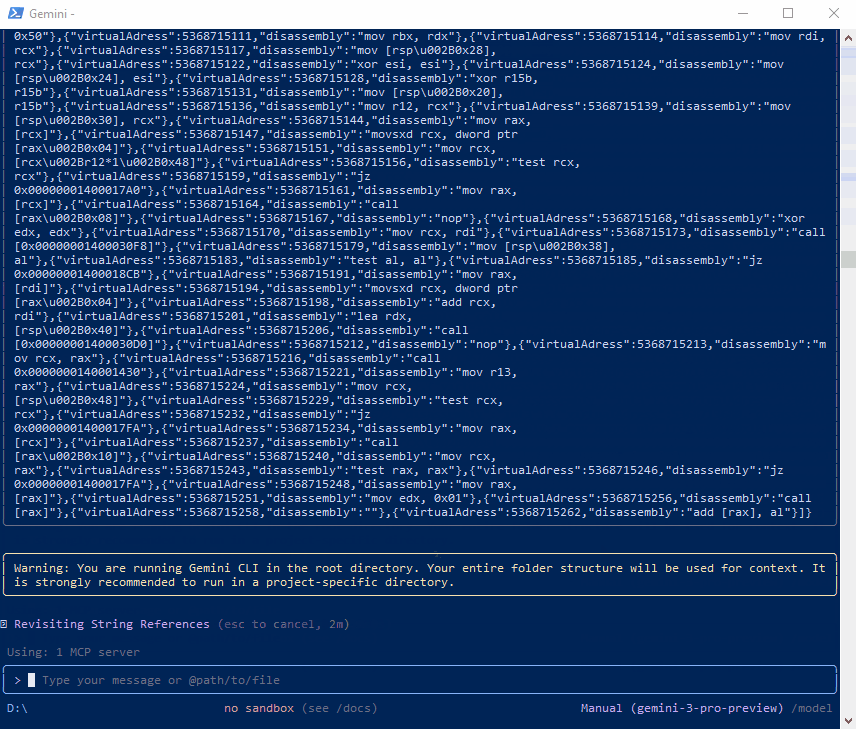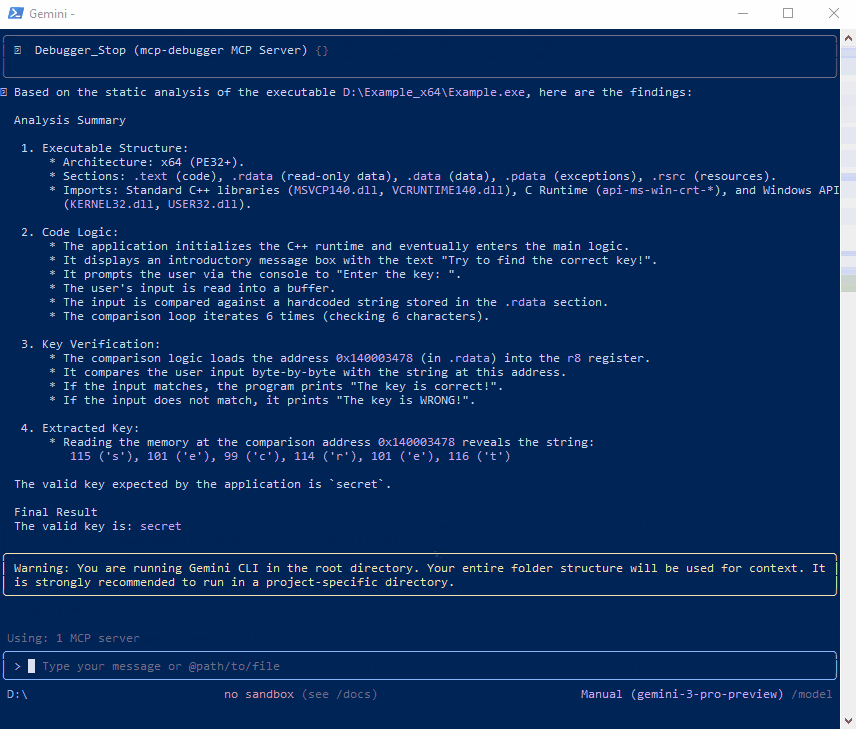 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
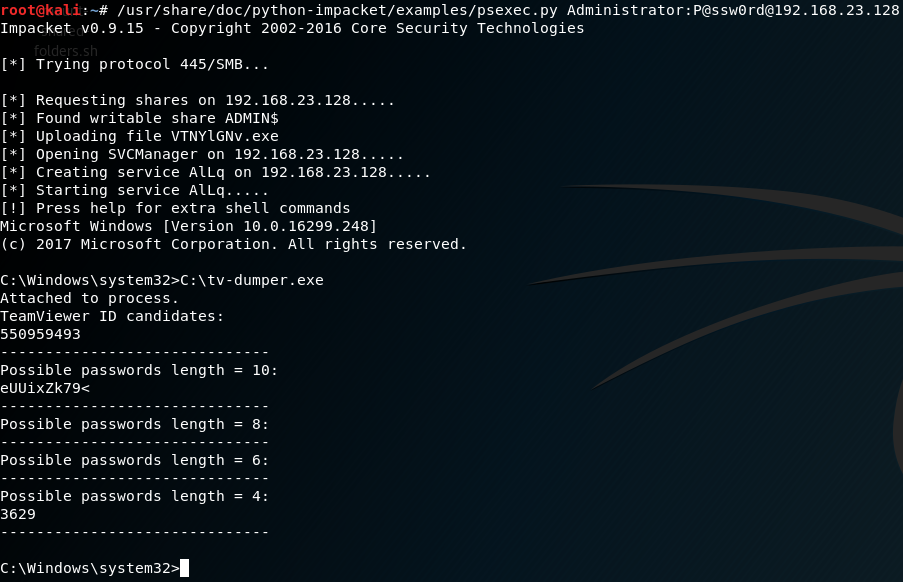 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
 bazad/ctl_ctloutput-leak
CVE-2017-13868: Information leak of uninitialized kernel heap data in XNU.
 3ndg4me/cve-2016-6415-benigncertain-monitor
Re-implementation of VirtueSecurity's benigncertain-monitor