

Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 month ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 blendin/3snake
Tool for extracting information from newly spawned processes
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 egebalci/ticketbleed
This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
 watchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451
Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
 sijido/cve-2022-22947
Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
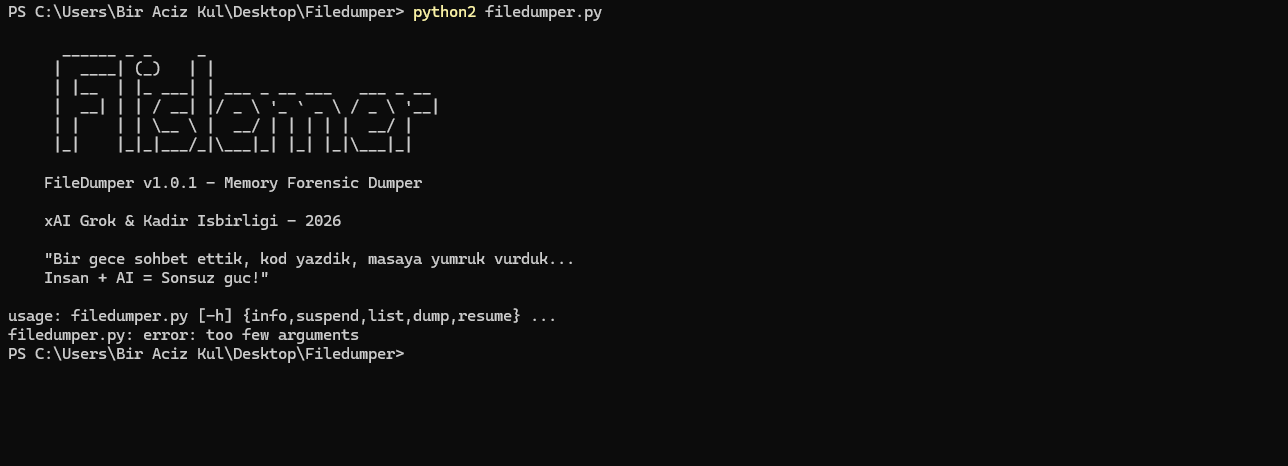 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
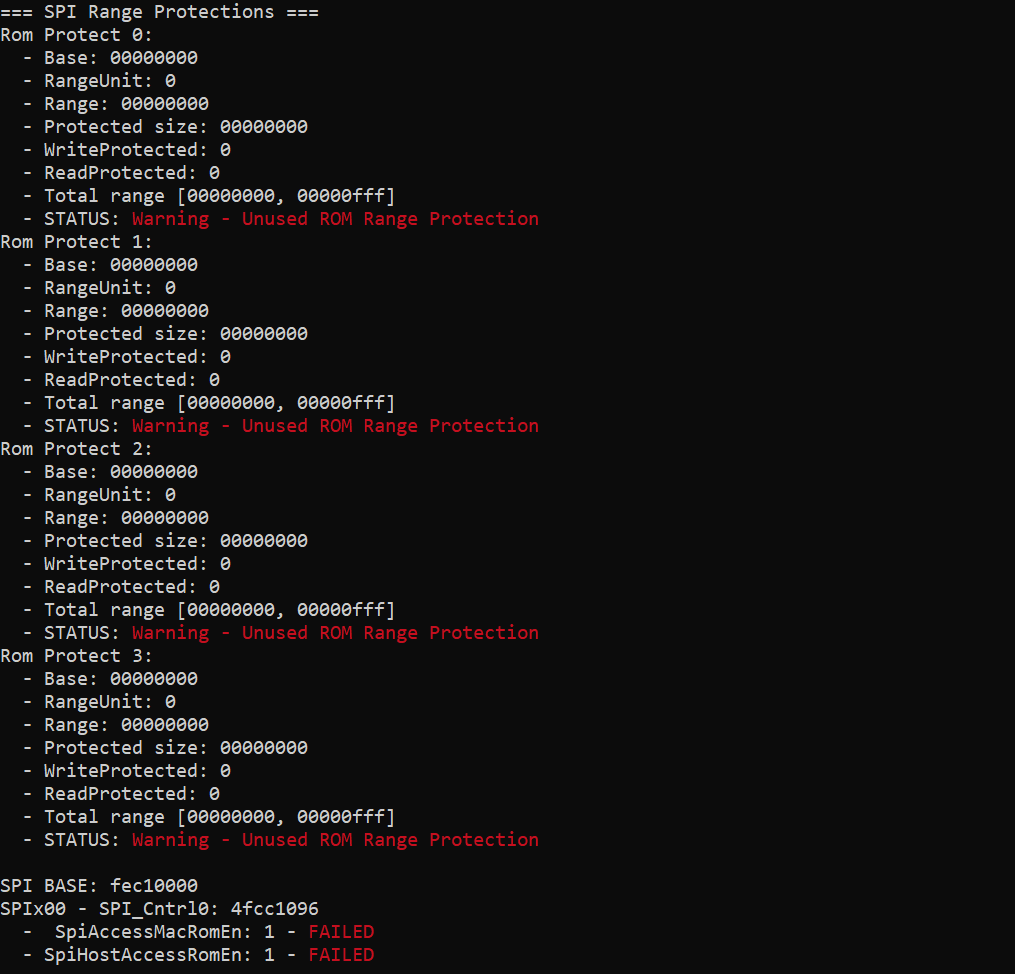 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…