
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
521
5 years ago
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

anomaly-detectionbinary-analysisdigital-forensics+3
614 years ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

digital-forensicsforensicsioc-management+3
8492 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
672 months ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8164 months ago
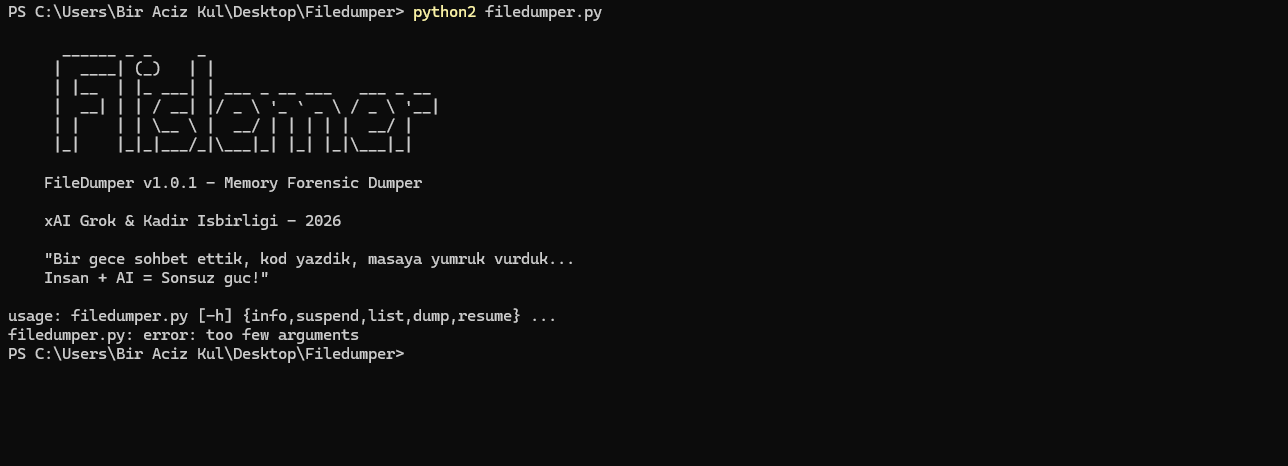
Filedumper preview

Filedumper

GitHubseyyidkadir/filedumper

Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…

data-recoverydigital-forensicsforensics+3
18 months ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.4k2 months ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k9h 54m ago
memhunter preview

memhunter

GitHubmarcosd4h/memhunter

Live hunting of code injection techniques

defensive-toolsincident-responsemalware-analysis+1
3837 years ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
915 months ago
MemTracer preview

MemTracer

GitHubmayhamad/memtracer

Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
digital-forensicsforensicsmalware-analysis+1
644 years ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…

binary-analysisdebuggersdigital-forensics+9
442 years ago
linux-explorer preview
Archived

linux-explorer

GitHubintezer/linux-explorer

Easy-to-use live forensics toolbox for Linux endpoints

digital-forensicsforensicsincident-response+7
4042 years ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
awesome-dfir-skills preview

awesome-dfir-skills

GitHubtsale/awesome-dfir-skills

A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
3234 months ago
gsscred-move-uaf preview

gsscred-move-uaf

GitHubbazad/gsscred-move-uaf

CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.

binary-exploitationexploitationios-security+2
78 years ago
CVE-2022-0435-Poc preview

CVE-2022-0435-Poc

GitHubspydomain/cve-2022-0435-poc

Stack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.

binary-exploitationexploitationmemory-forensics+2
17 months ago