
artifacts-kit
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
228
forrest-orr/artifacts-kitPseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 ntgabrielgomes/cve-2023-20564
Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 fi01/libget_user_exploit
Kernel memory read exploit leveraging CVE-2013-6282 for local privilege escalation on affected Linux systems.
 argp/cve-2011-3026-firefox
Example of exploiting CVE-2011-3026 on Firefox (Linux/x86)
 adamkadaban/cve-2024-30085
Proof-of-concept exploit for CVE-2024-30085, a heap-based buffer overflow in the Windows CLDLFT driver leading to local privilege escalation on…
 amberchalia/norm-edr
Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
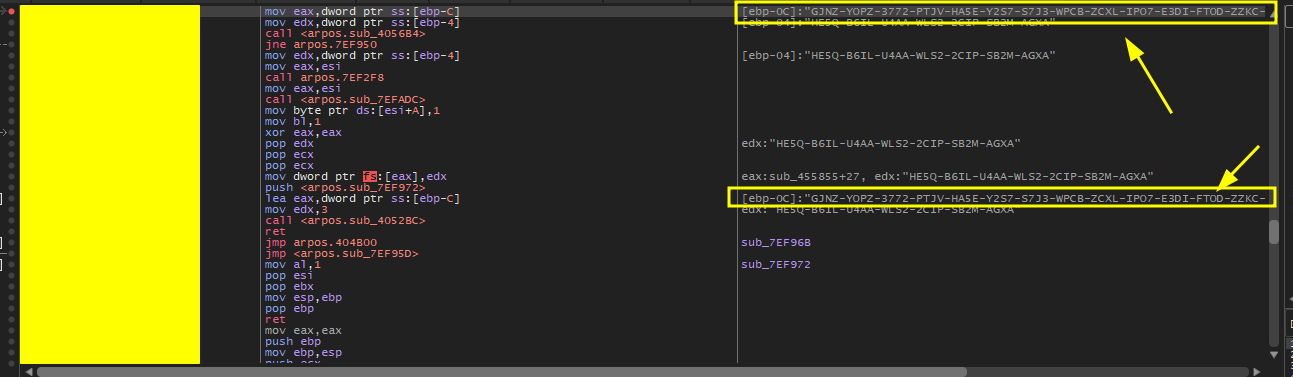 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
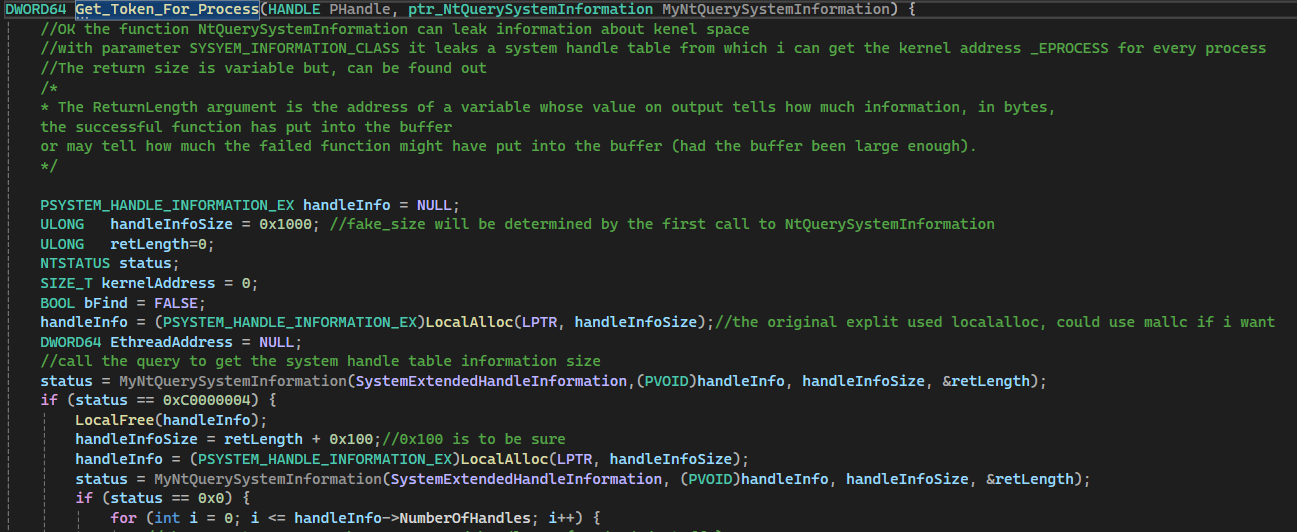 emilc3978/cve-2022-37969poc
Tutorial of CVE-2022-37969 with focus on the methodology of Kernel exploitation, not CVE's internal causes
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 spydomain/cve-2022-0435-poc
Stack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 skelsec/pypykatz
Mimikatz implementation in pure Python
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.