Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
107 results
CVE-2023-32784-kdbxpassdmp preview

CVE-2023-32784-kdbxpassdmp

GitHubamperclock/cve-2023-32784-kdbxpassdmp

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
digital-forensicsexploitationforensics+3
5 months ago
CVE-2025-50422 preview

CVE-2025-50422

GitHublandw-hub/cve-2025-50422

Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…

data-recoverydigital-forensicsexploitation+3
16 months ago
DMA-ProcessDumper preview

DMA-ProcessDumper

GitHubgmh5225/dma-processdumper

Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
4 years ago
CVE-2023-32784 preview

CVE-2023-32784

GitHubdawnl3ss/cve-2023-32784

Retrieve the master password of a keepass database <= 2.53.1

exploitationforensicsmemory-forensics+2
3 years ago
volatility preview
Archived

volatility

GitHubvolatilityfoundation/volatility

An advanced memory forensics framework

digital-forensicsforensicsincident-response+4
8.1k1 year ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

digital-forensicsforensicsincident-response+3
2.0k6 years ago
miniDumpReader preview

miniDumpReader

GitHubgmh5225/minidumpreader

Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…

binary-analysisdigital-forensicsforensics+3
3 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
6101 month ago
bios_memimage preview
Archived

bios_memimage

GitHubdbrant/bios_memimage

RAM imaging utility.

digital-forensicsincident-responsememory-forensics
910 years ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k22 days ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

data-recoverydigital-forensicsdisk-forensics+5
1.2k1 day ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8245 months ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4895 years ago
nightHawkResponse preview

nightHawkResponse

GitHubbiggiesmallsag/nighthawkresponse

Incident Response Forensic Framework

digital-forensicsdisk-forensicsforensics+7
6076 years ago
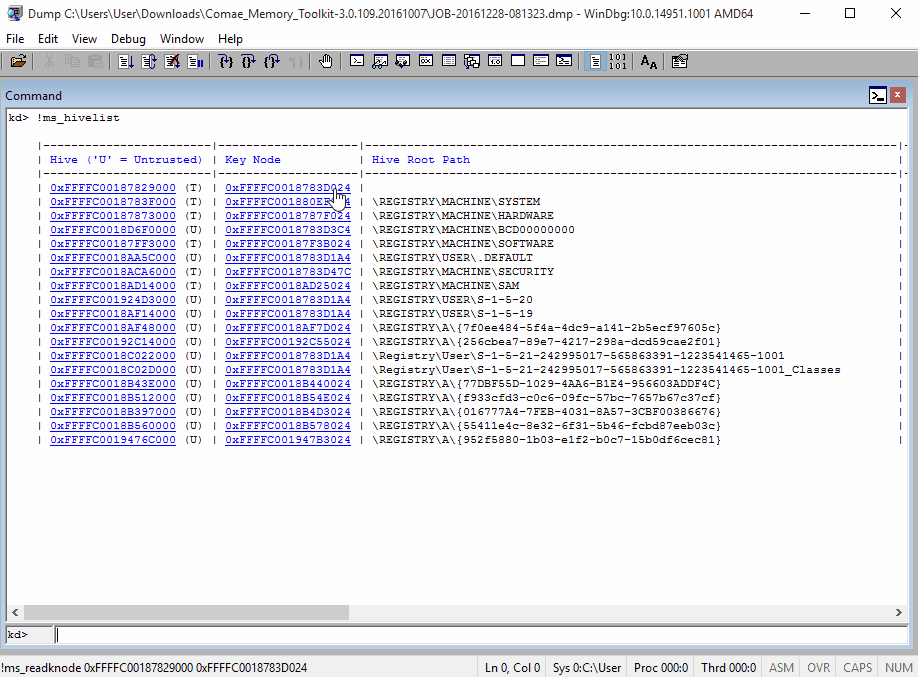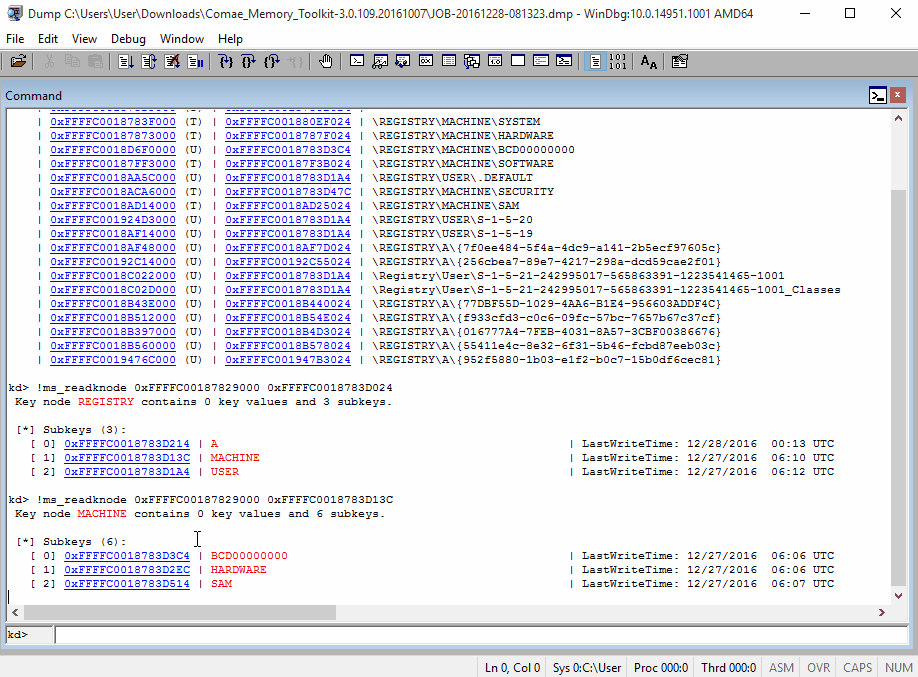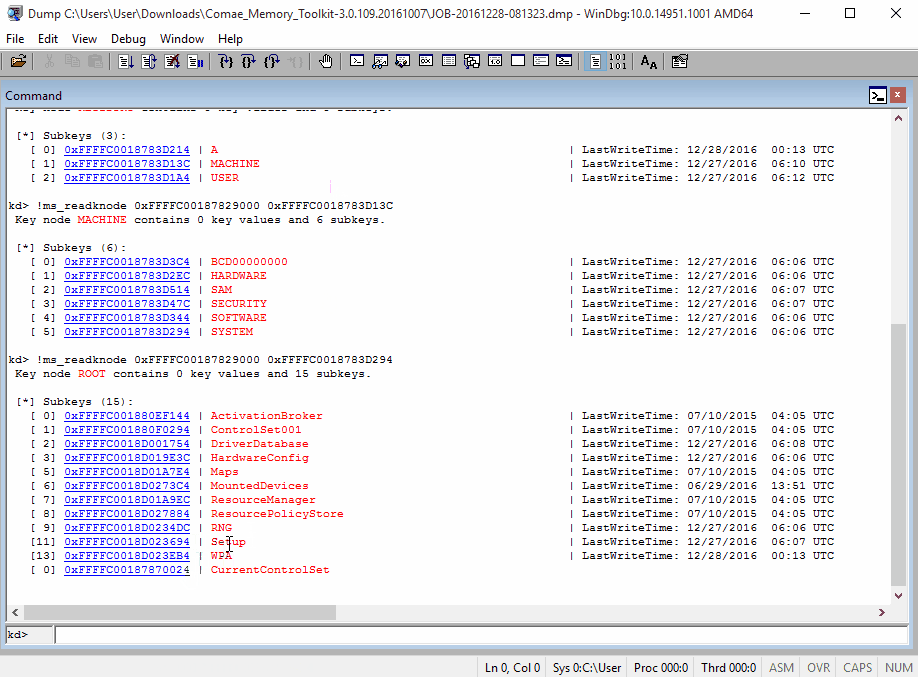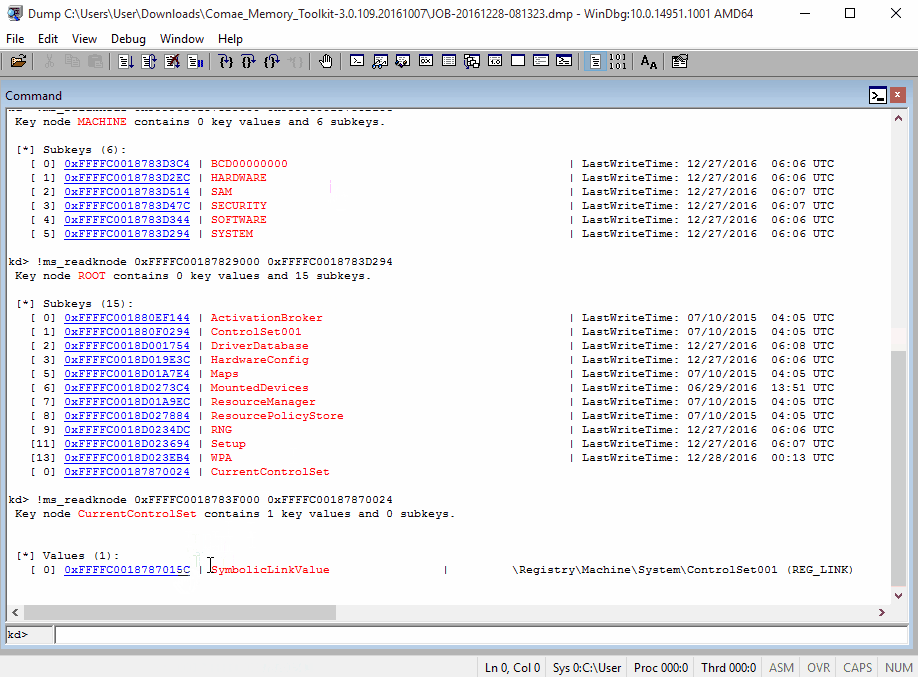
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5165 years ago
SwishDbgExt preview

SwishDbgExt

GitHubmagnetforensics/swishdbgext

Incident Response & Digital Forensics Debugging Extension

debuggersdigital-forensicsincident-response+3
3997 years ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
916 months ago
Previous123456Next
