
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
652 results
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
218
8 days ago
dismember preview

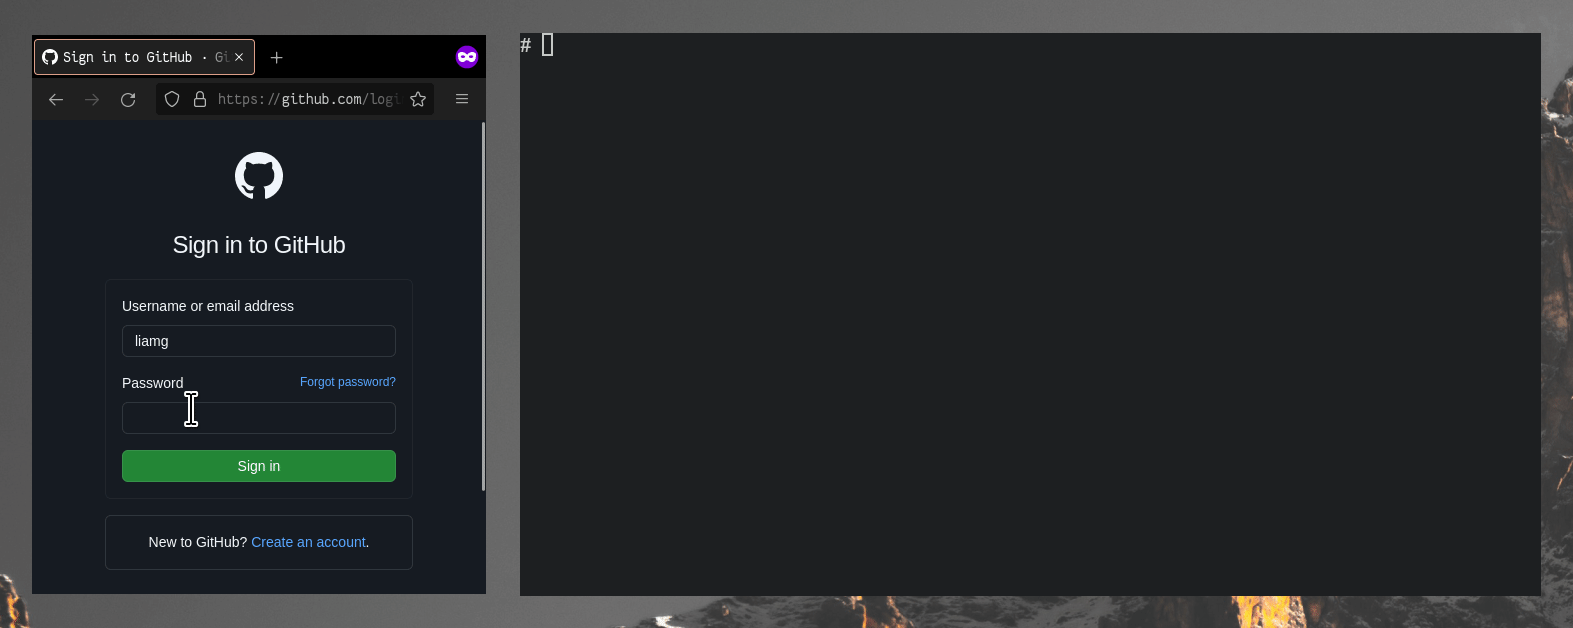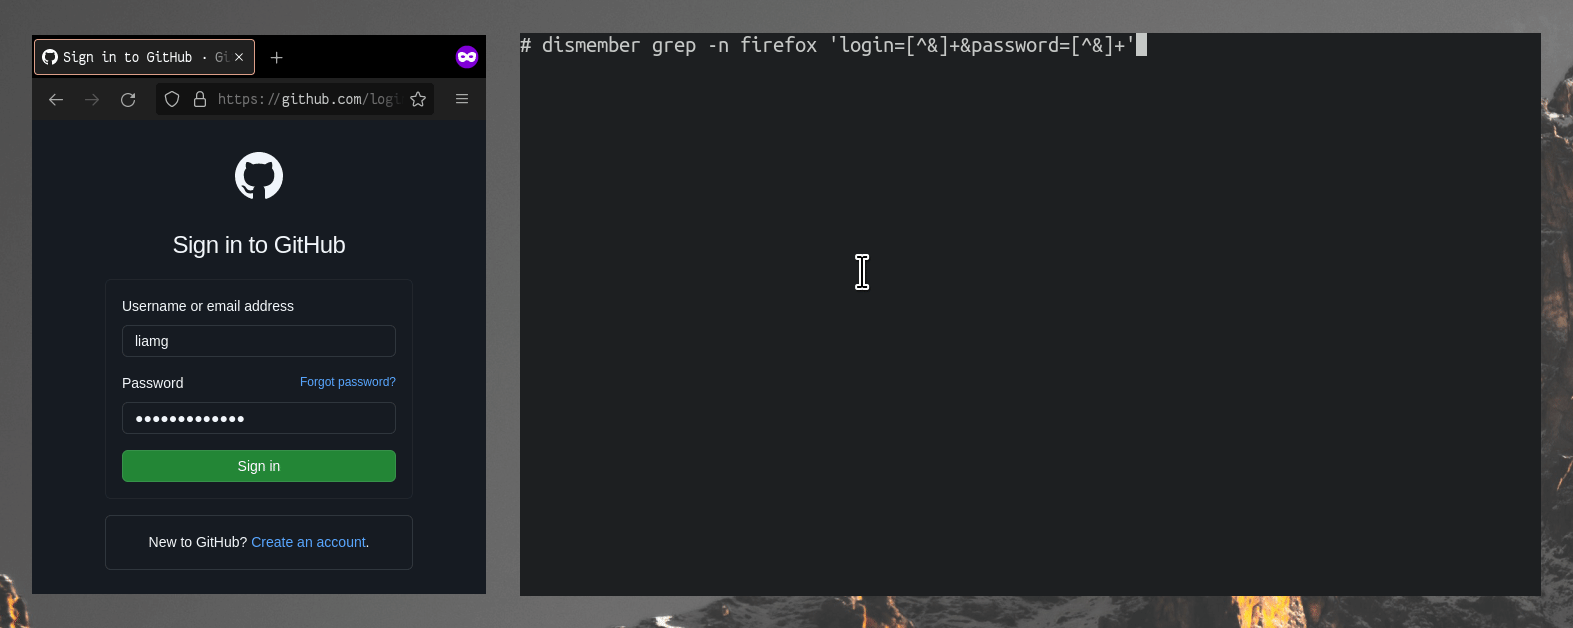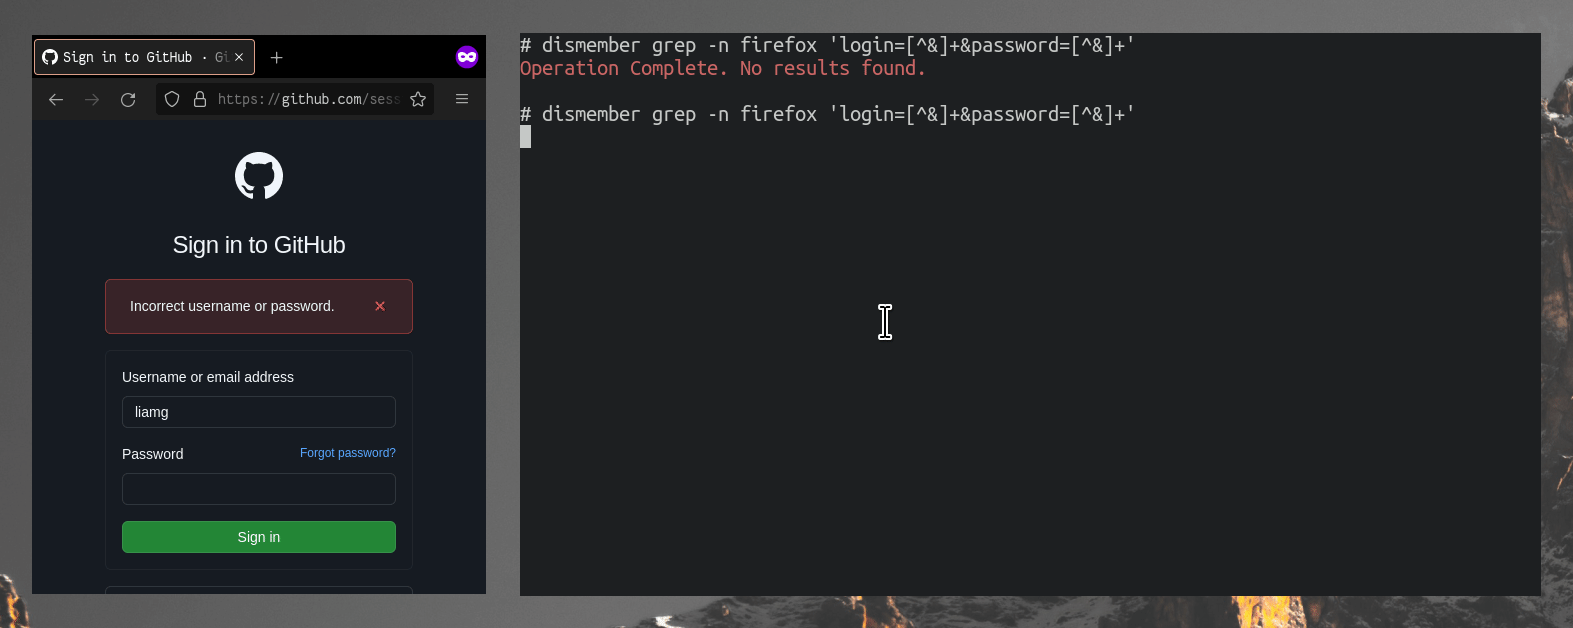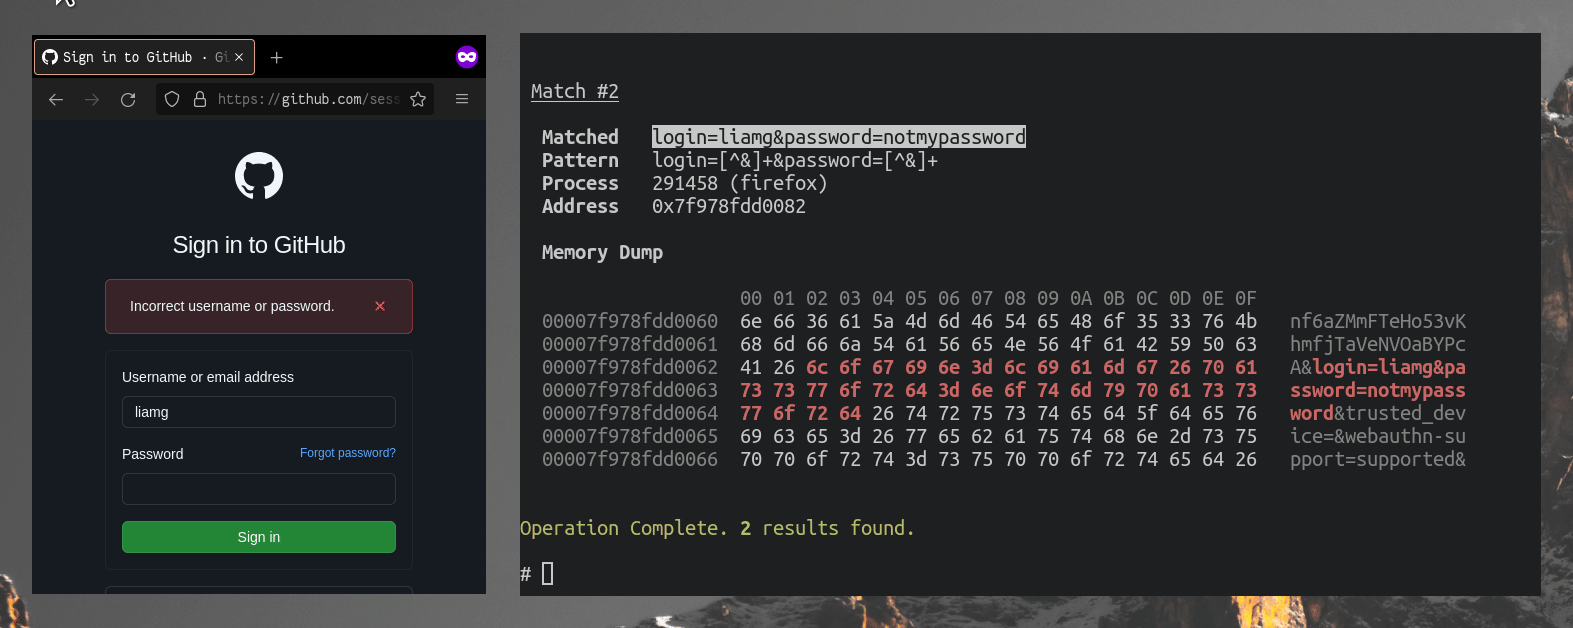
dismember

GitHubliamg/dismember

:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
ctfforensicsinformation-gathering+2
6754 years ago
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecting & Hunting for IOCs with gusto and style
digital-forensicsforensicsincident-response+6
2386 years ago
heaptrace preview

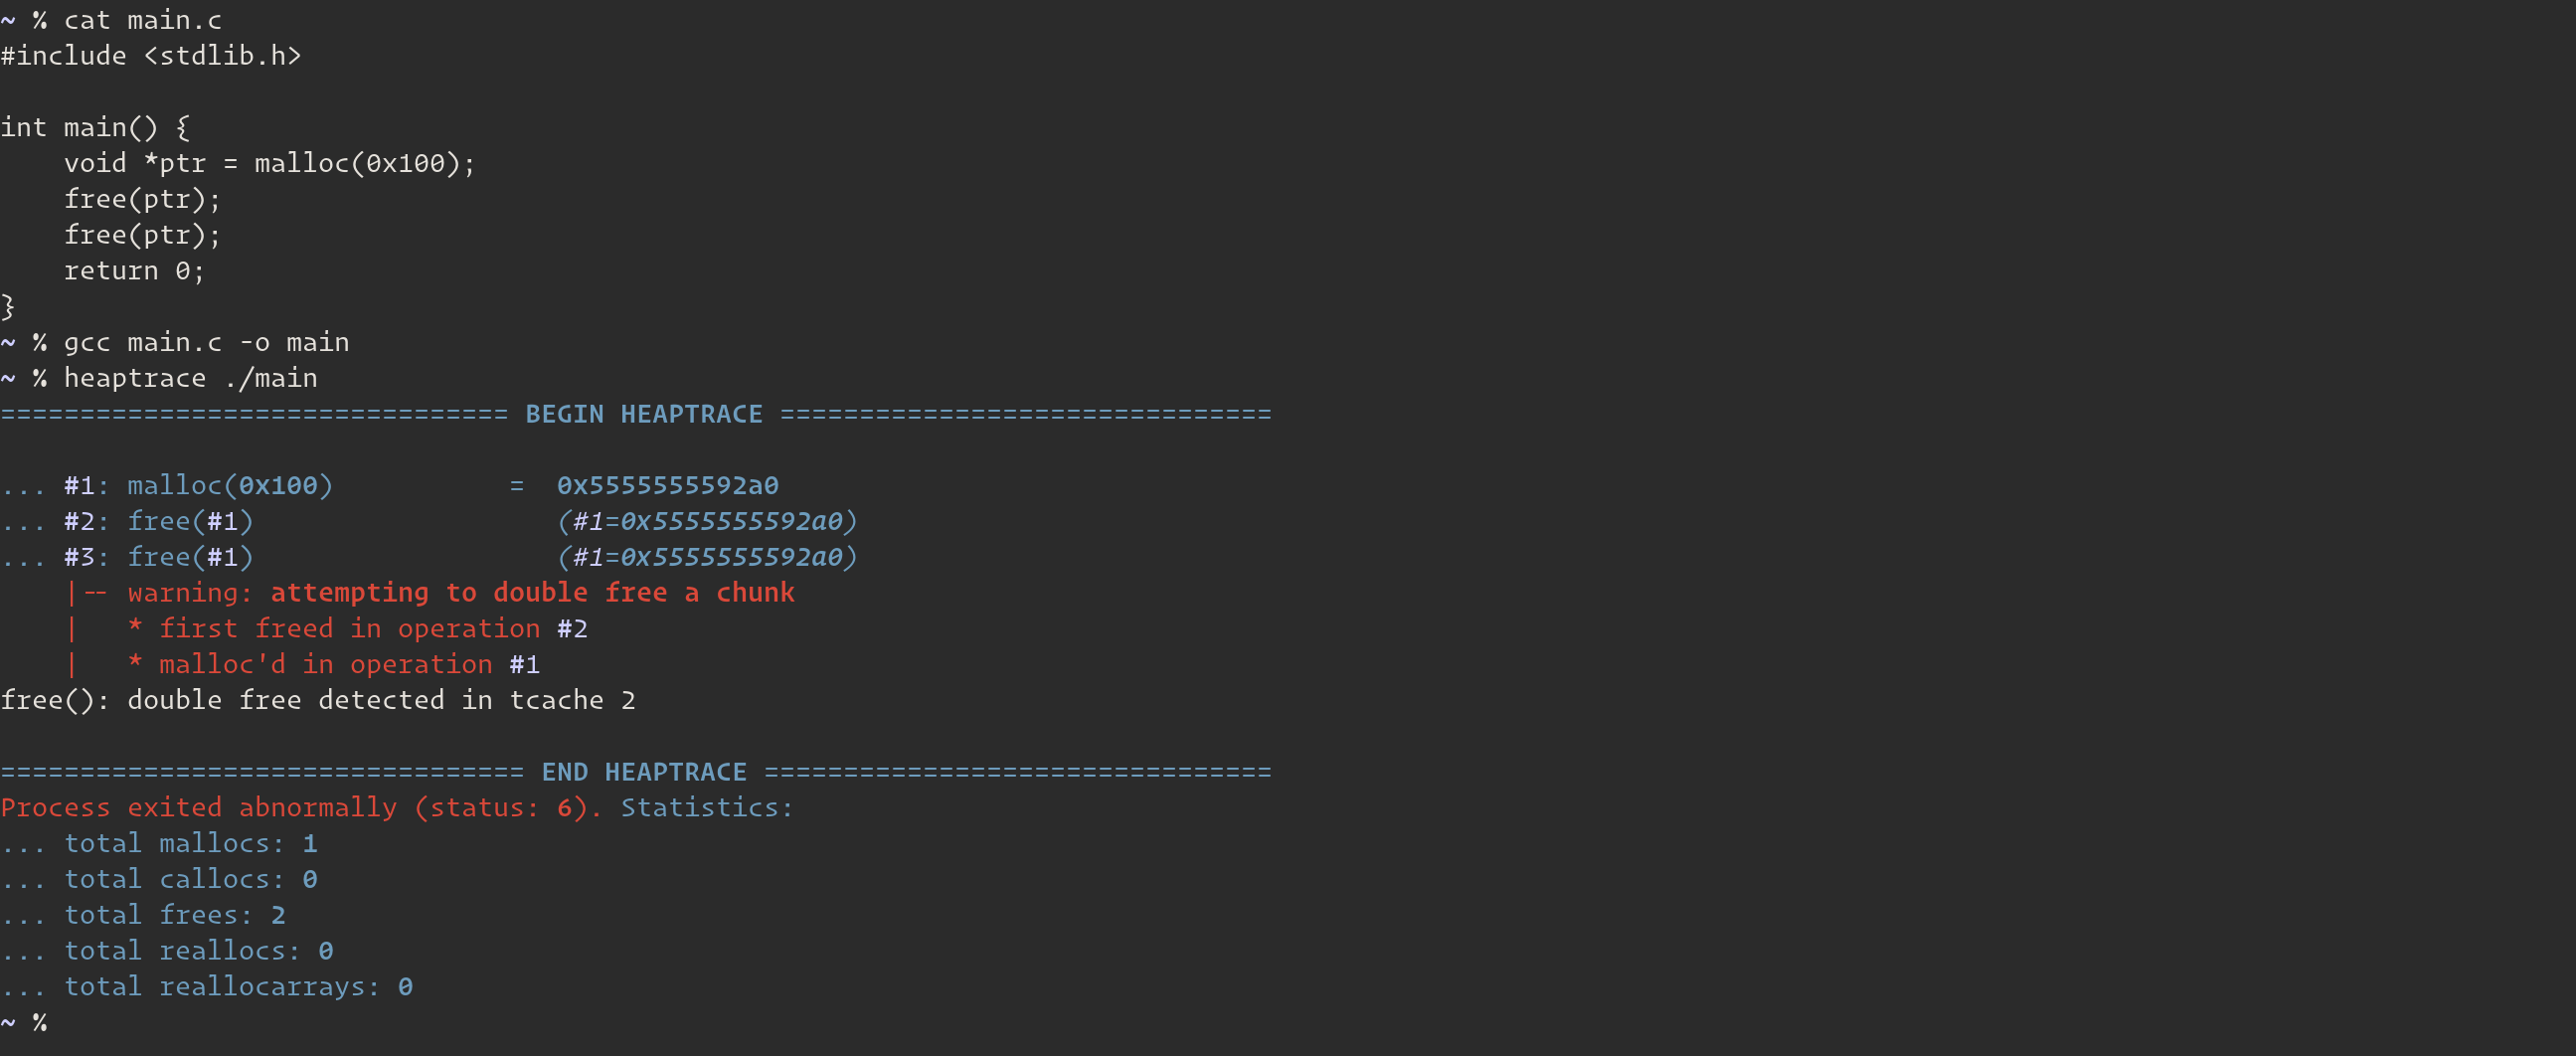
heaptrace

GitHubarinerron/heaptrace

helps visualize heap operations for pwn and debugging
binary-analysisctfdebuggers+1
3303 years ago
CVE-2018-17182 preview

CVE-2018-17182

GitHubjas502n/cve-2018-17182

Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
binary-exploitationexploitationmemory-forensics+2
1307 years ago
CyberPipe preview

CyberPipe

GitHubdwmetz/cyberpipe

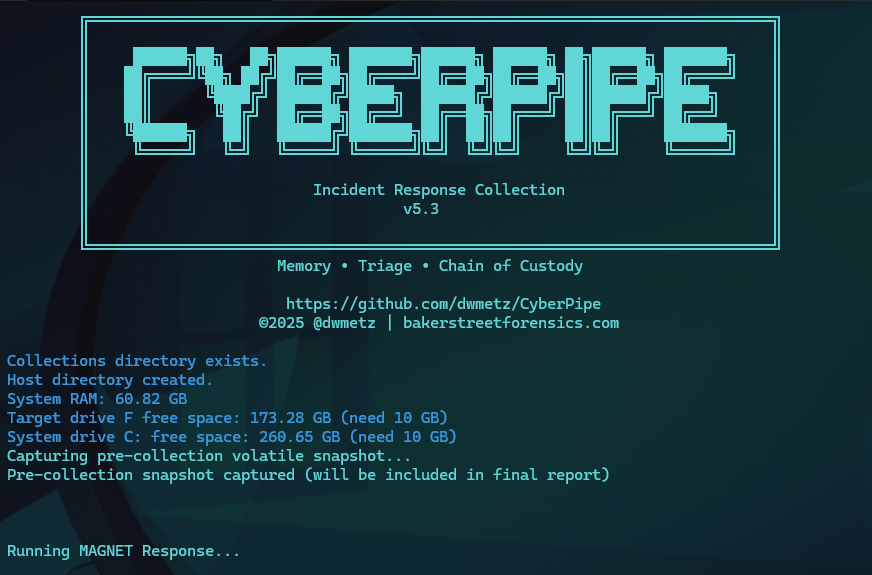
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
digital-forensicsdisk-forensicsforensics+2
3479 months ago
CVE-2022-37969 preview

CVE-2022-37969

GitHubfortra/cve-2022-37969

Proof-of-concept exploit for CVE-2022-37969, a Windows Common Log File System driver local privilege escalation. Demonstrates heap spray, token…
binary-exploitationexploitationmemory-forensics+2
1343 years ago
r0ak preview

r0ak

GitHubharryanon/r0ak

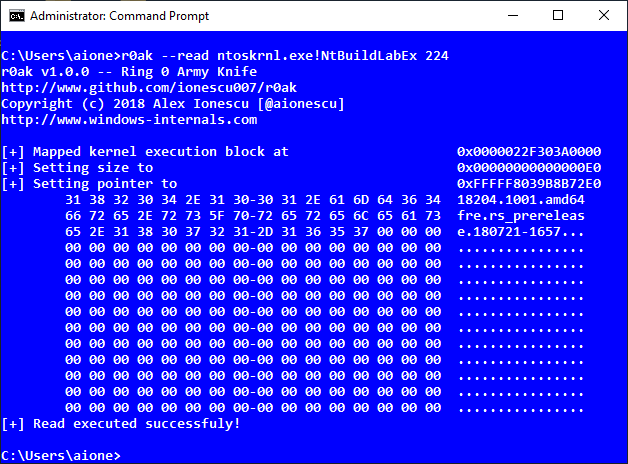
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…

binary-exploitationdebuggersexploitation+5
1088 years ago
zombieant preview

zombieant

GitHubdsnezhkov/zombieant

Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
memory-forensicspayload-developmentpost-exploitation+2
2267 years ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
18514 days ago
LiMEaide preview

LiMEaide

GitHubkd8bny/limeaide

A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.
digital-forensicsforensicsmemory-forensics
1577 years ago
java-stager preview

java-stager

GitHubcornerpirate/java-stager

A PoC Java Stager which can download, compile, and execute a Java file in memory.
command-and-controldynamic-code-analysiseducation+7
1078 years ago
NovaHypervisor preview

NovaHypervisor

GitHubidov31/novahypervisor

Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
defensive-toolshardware-securityids-ips-evasion+2
2764 months ago
TiEtwAgent preview

TiEtwAgent

GitHubxuanxuan0/tietwagent

PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
defensive-toolseducationmalware-analysis+1
2995 years ago
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
binary-analysisfirmware-analysisfuzzing+3
2221 year ago
cve-2019-2215 preview

cve-2019-2215

GitHubkangtastic/cve-2019-2215

Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
android-securitybinary-exploitationdebuggers+4
1376 years ago
ulexecve preview

ulexecve

GitHubanvilsecure/ulexecve

Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
exploitationmemory-forensicspenetration-testing+3
2172 years ago
DotDumper preview

DotDumper

GitHubadvanced-threat-research/dotdumper

An automatic unpacker and logger for DotNet Framework targeting files

binary-analysisdebuggersdynamic-analysis-sandboxing+4
2643 years ago
Previous1…456…37Next