
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
722 results
invoker preview
Archived

invoker

GitHubivan-sincek/invoker

Penetration testing utility and antivirus assessment tool.

binary-analysiseducationexploitation+6
312
3 years ago
bios_memimage preview
Archived

bios_memimage

GitHubdbrant/bios_memimage

RAM imaging utility.

digital-forensicsincident-responsememory-forensics
910 years ago
EDRSandblast-GodFault preview
Archived

EDRSandblast-GodFault

GitHubgabriellandau/edrsandblast-godfault

EDRSandblast-GodFault

defensive-toolsexploitationmemory-forensics+4
2733 years ago
CVE-2022-21971 preview
Archived

CVE-2022-21971

GitHub0vercl0k/cve-2022-21971

PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"

binary-exploitationdebuggersexploitation+3
3024 years ago
linux-explorer preview
Archived

linux-explorer

GitHubintezer/linux-explorer

Easy-to-use live forensics toolbox for Linux endpoints

digital-forensicsforensicsincident-response+7
4052 years ago
PPLdump preview
Archived

PPLdump

GitHubitm4n/ppldump

Dump the memory of a PPL with a userland exploit
binary-exploitationexploitationmemory-forensics+3
8934 years ago
pe_tree preview
Archived

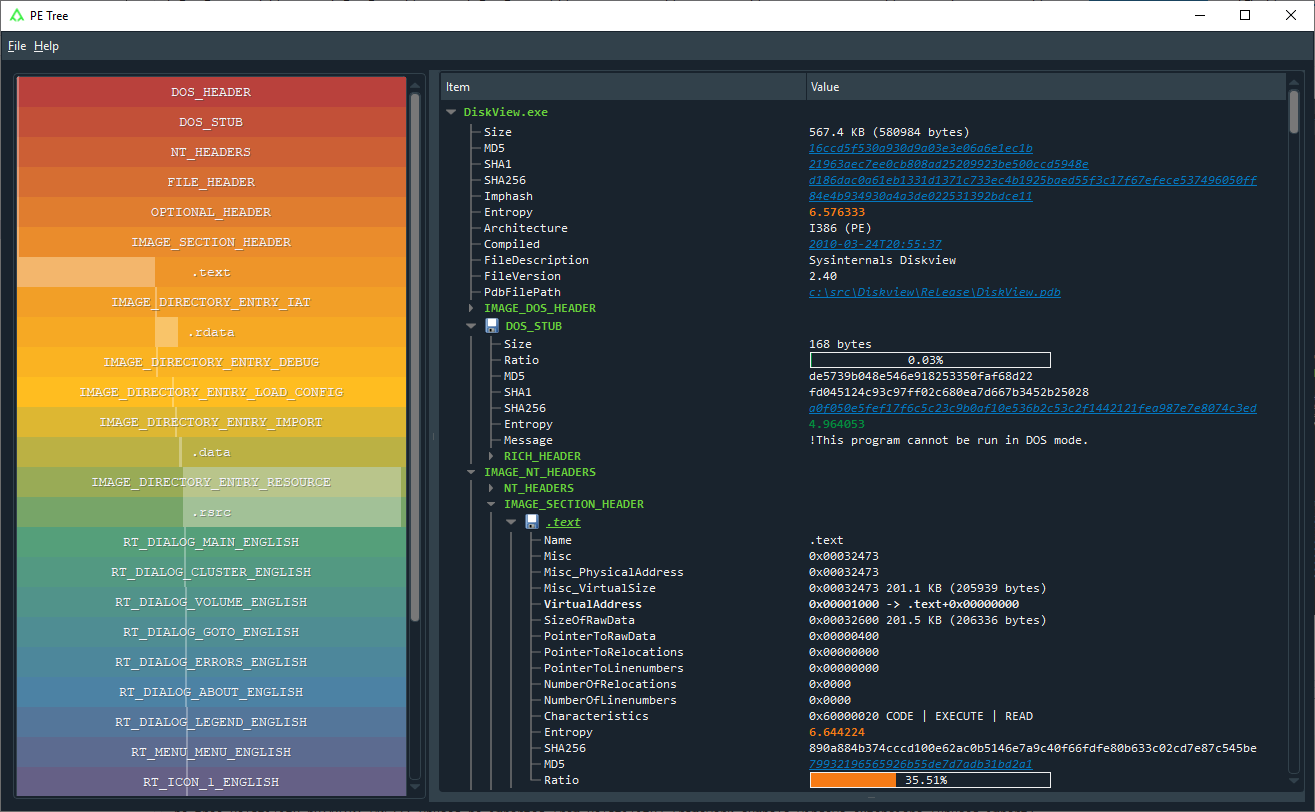
pe_tree

GitHubblackberry/pe_tree

Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
1.3k4 years ago
mig preview
Archived

mig

GitHubmozilla/mig

Distributed & real time digital forensics at the speed of the cloud

configuration-auditingdigital-forensicsdisk-forensics+6
1.2k7 years ago
MCPTrace preview

MCPTrace

GitHubkowntaewook/mcptrace

Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
ai-securitydigital-forensicsforensics+5
78 days ago
meltdown preview
Archived

meltdown

GitHubisec-tugraz/meltdown

Proof-of-concept demos and libkdump library demonstrating the Meltdown microarchitectural attack, leaking kernel and physical memory on vulnerable…
binary-exploitationcryptographydata-exfiltration+5
4.2k4 years ago
Nginx-chain-Rift-Poolslip preview

Nginx-chain-Rift-Poolslip

GitHuby198nt/nginx-chain-rift-poolslip

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

binary-exploitationeducationexploitation+7
145 months ago
varc preview
Archived

varc

GitHubcado-security/varc

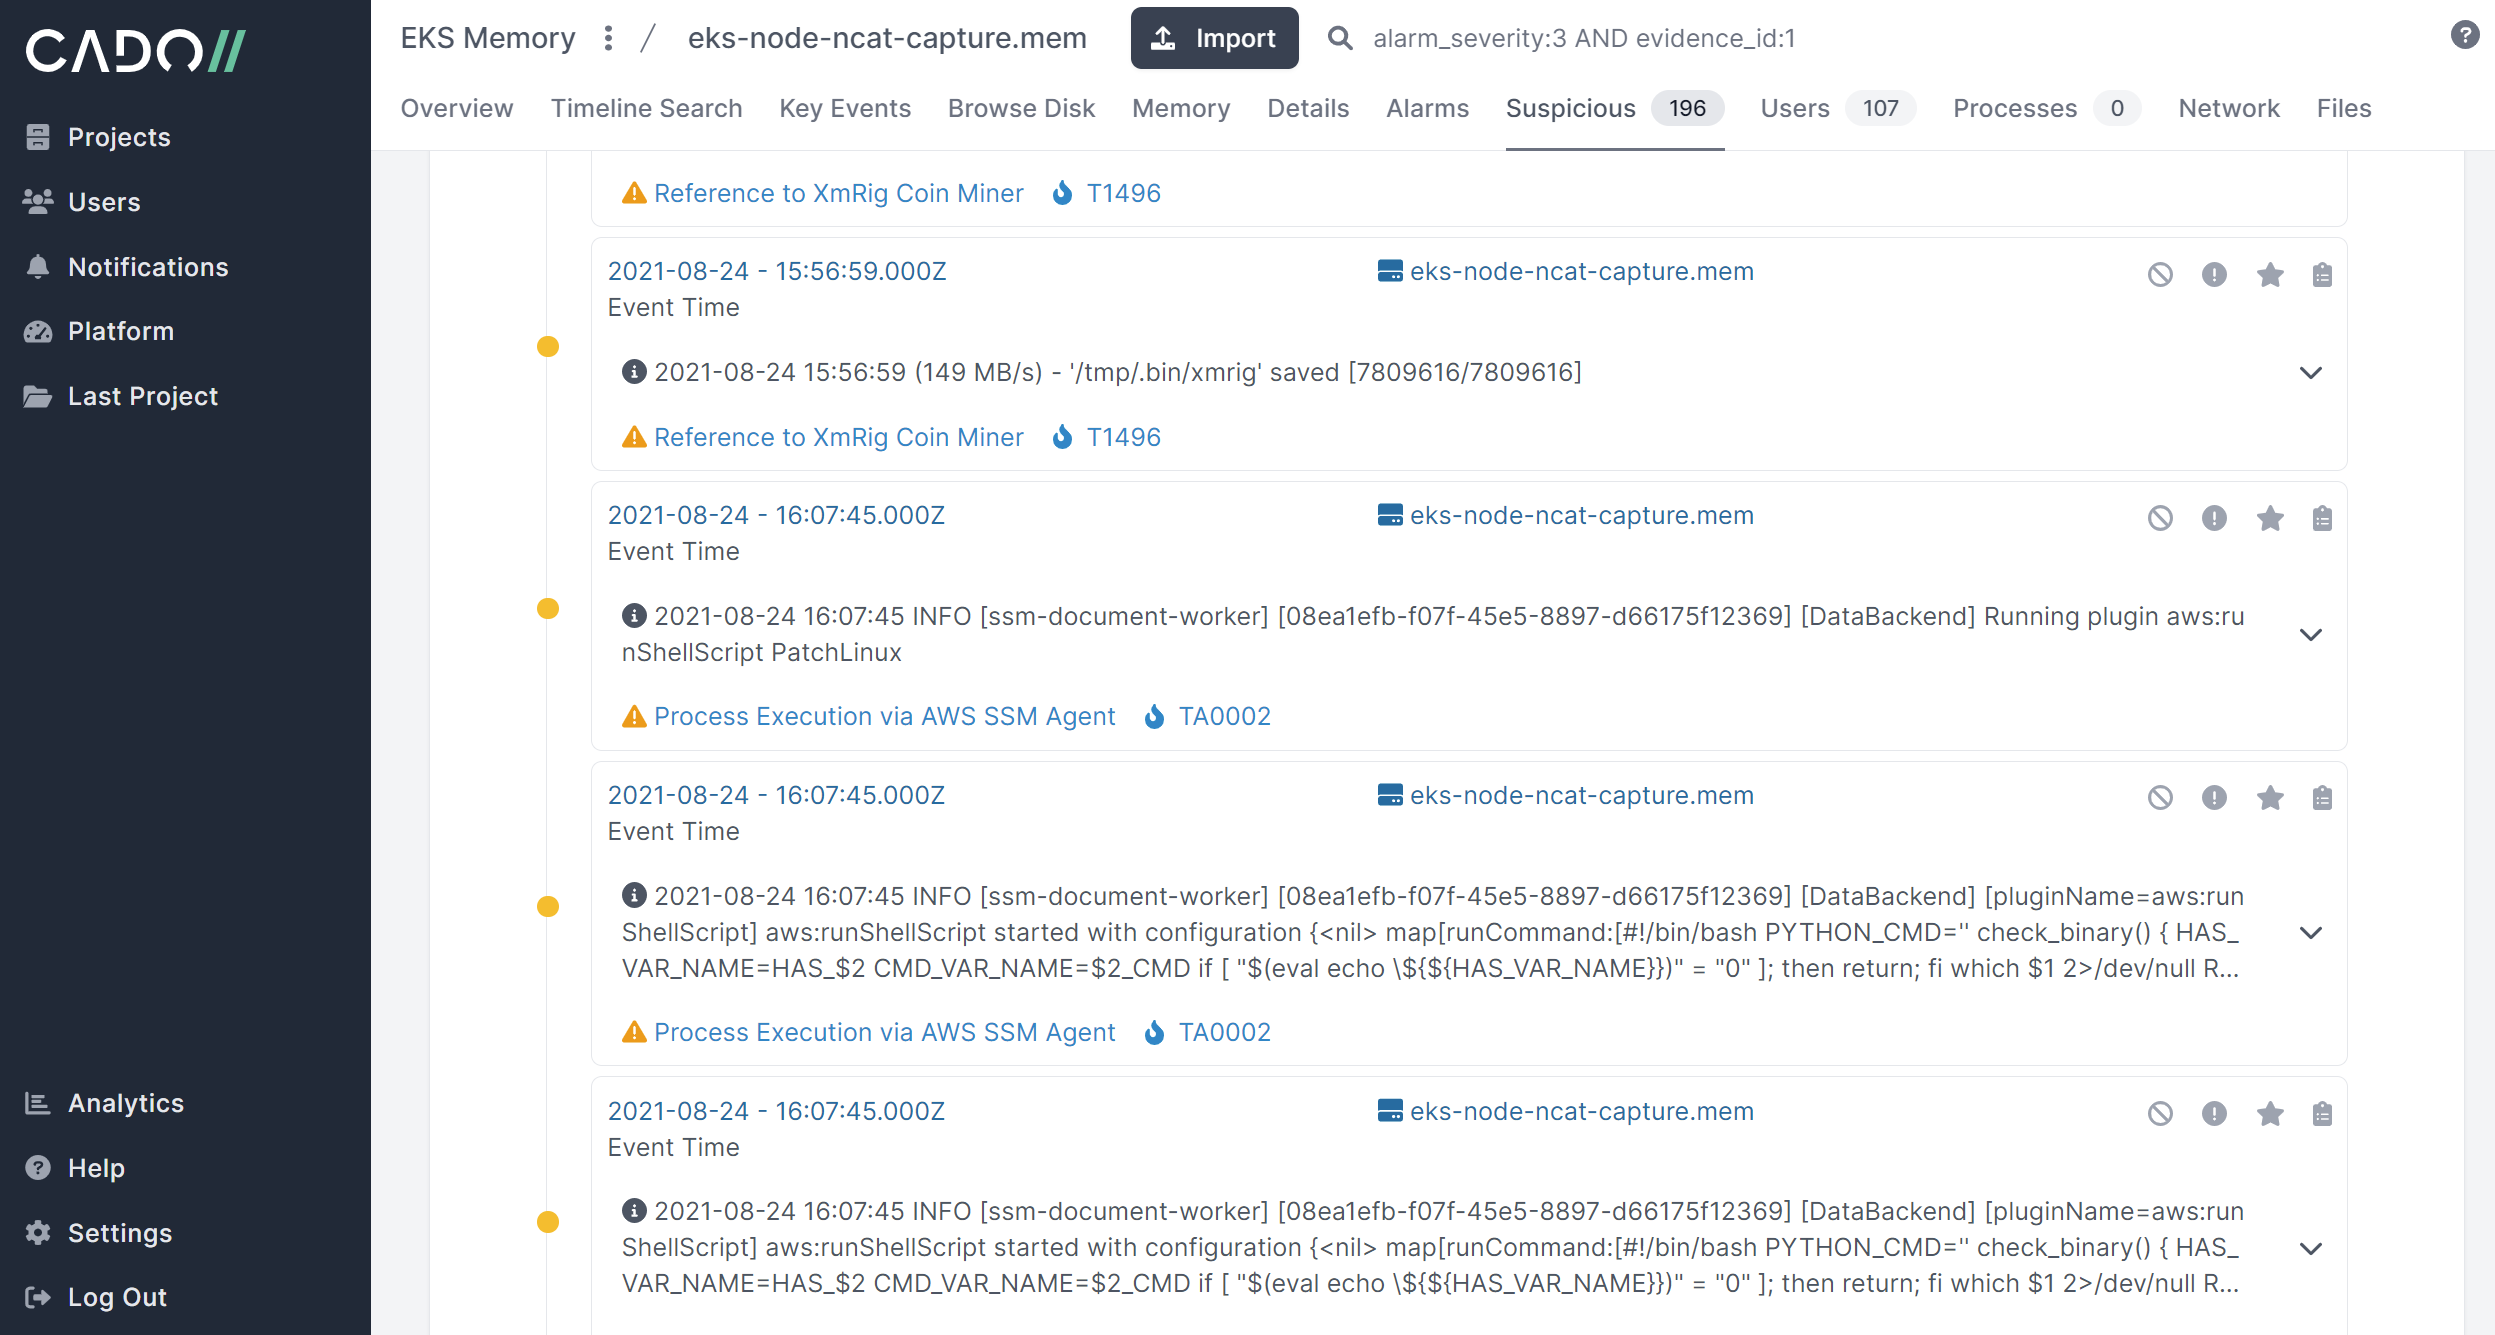
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…

cloud-securitycontainer-securitydigital-forensics+3
2541 year ago
CVE-2021-32537 preview
Archived

CVE-2021-32537

GitHub0vercl0k/cve-2021-32537

PoC for CVE-2021-32537: an out-of-bounds memory access that leads to pool corruption in the Windows kernel.
binary-exploitationexploitationmemory-forensics+1
555 years ago
CVE-2020-1206-POC preview
Archived

CVE-2020-1206-POC

GitHubjamf/cve-2020-1206-poc

CVE-2020-1206 Uninitialized Kernel Memory Read POC
binary-exploitationeducationexploitation+3
1446 years ago
illusion-rs preview
Archived

illusion-rs

GitHubmemn0ps/illusion-rs

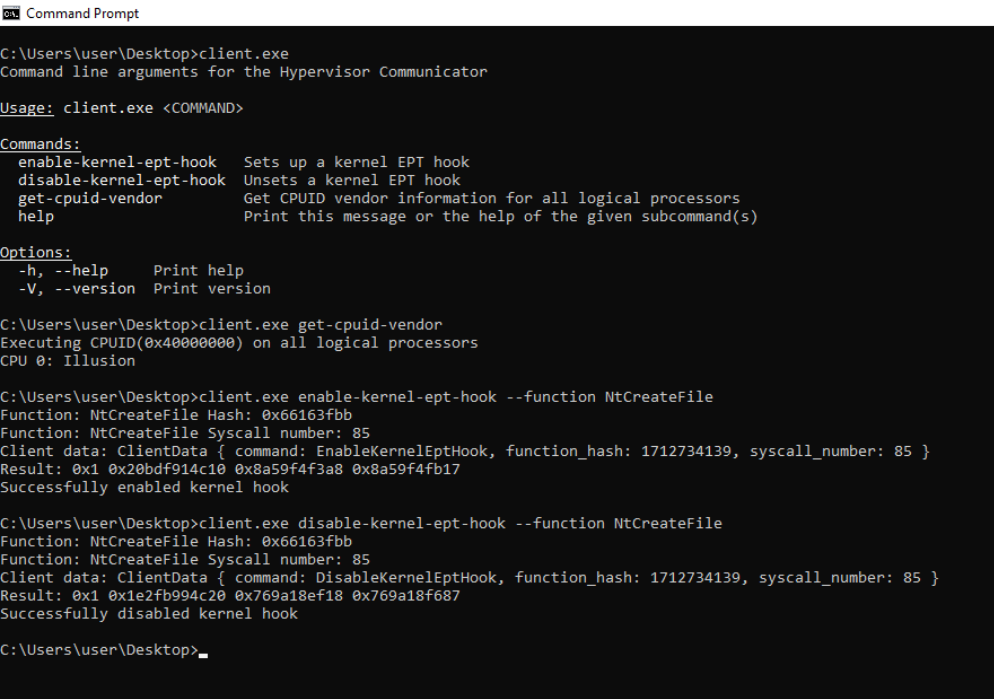
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
binary-analysisdefensive-toolshardware-security+7
4145 months ago
rip_raw preview
Archived

rip_raw

GitHubcado-security/rip_raw

Rip Raw is a small tool to analyse the memory of compromised Linux systems.
data-recoverydigital-forensicsforensics+3
1334 years ago
CVE-2022-21974 preview
Archived

CVE-2022-21974

GitHub0vercl0k/cve-2022-21974

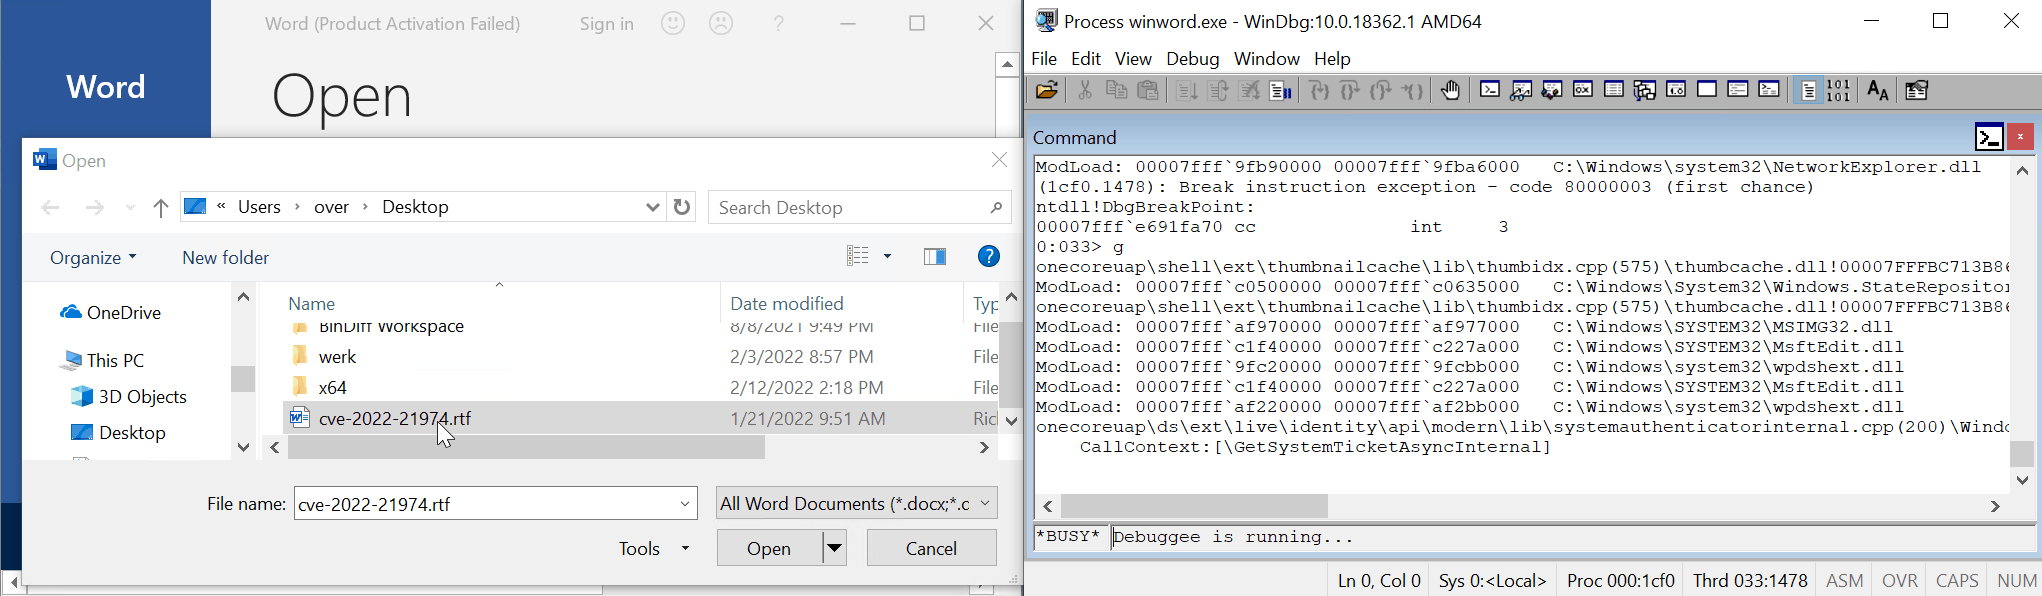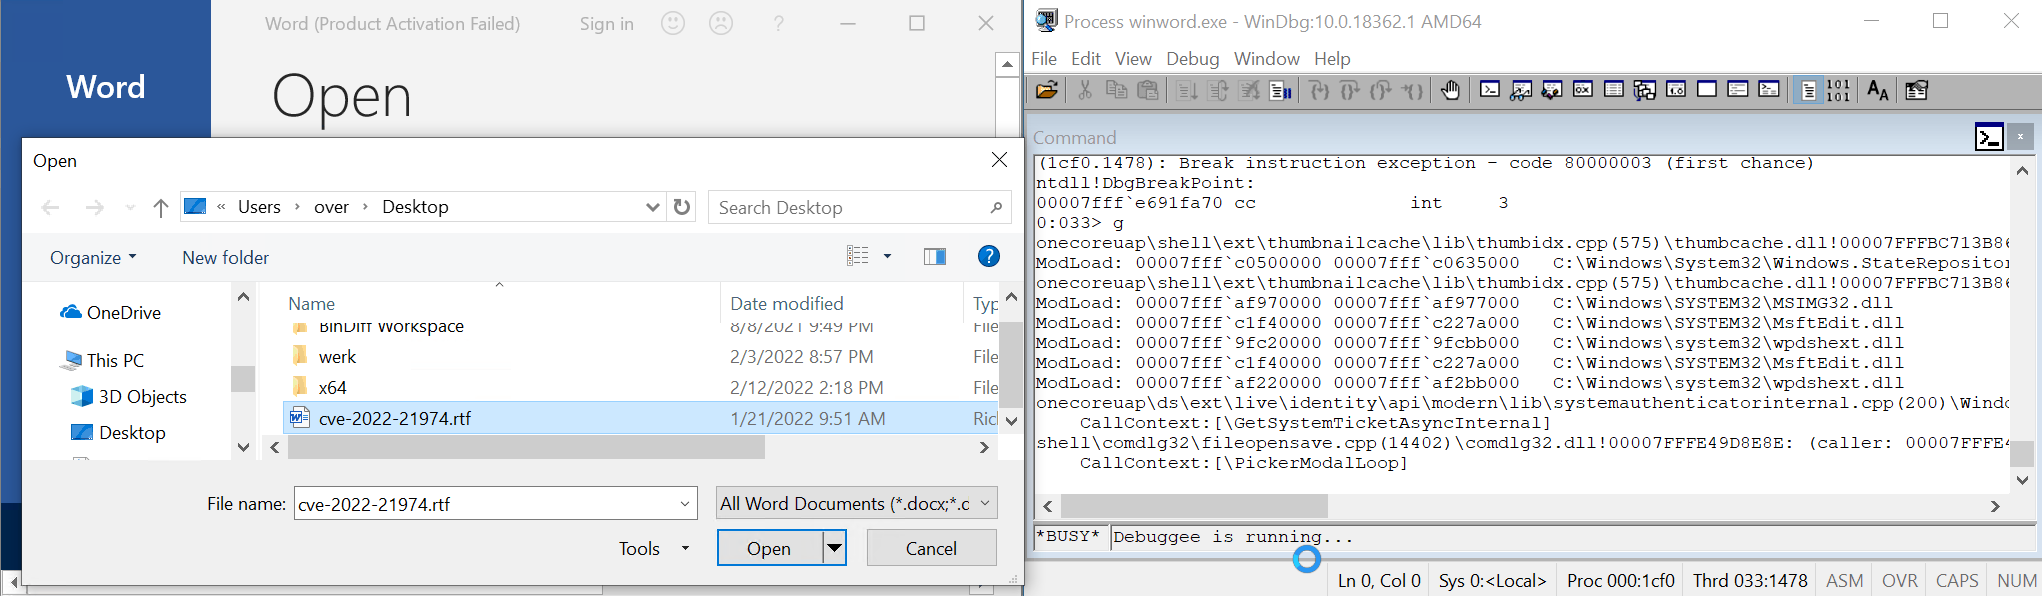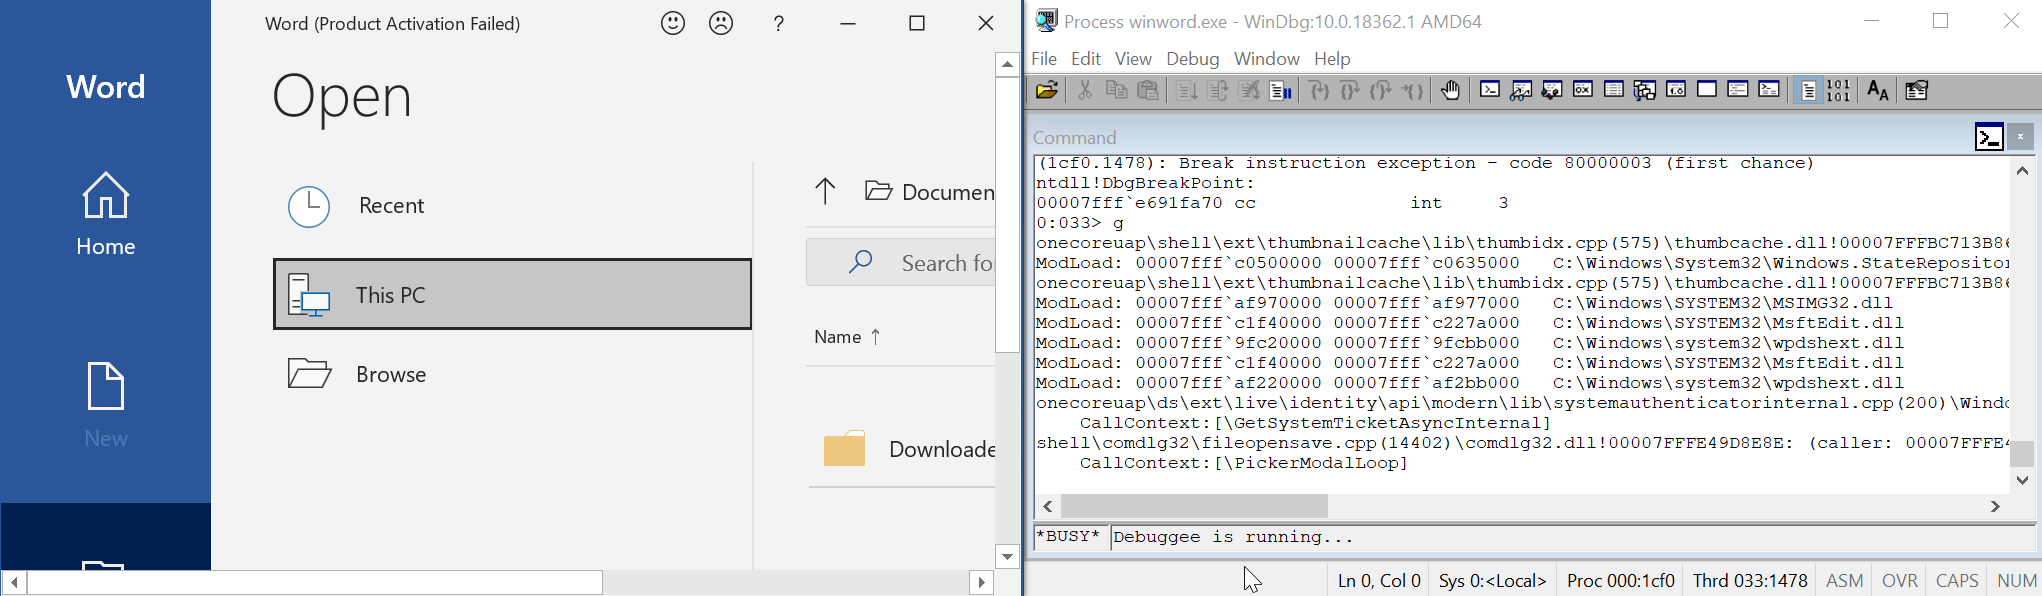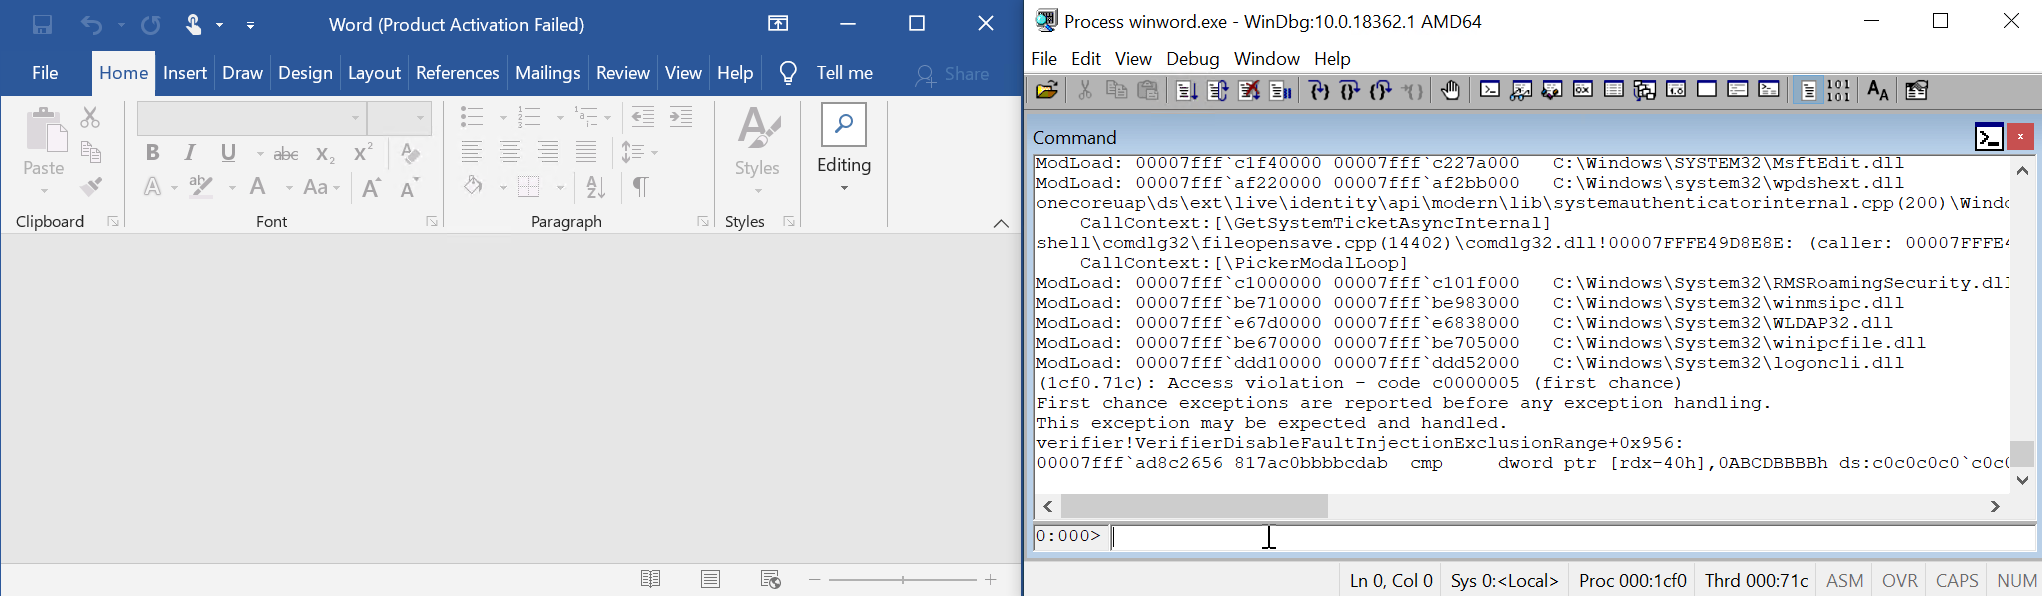
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
binary-exploitationdebuggersexploitation+3
574 years ago
pass-ta-key preview

pass-ta-key

GitHub0rcruxe/pass-ta-key

PoC that extracts the Google Password Manager Security Domain Secret from Chrome process memory and decrypts synced GPM passkey ECDSA P-256 private…

digital-forensicsencryption-decryption-toolsexploitation+3
274 days ago
Previous1…394041Next