watchTowr-vs-Netscaler-CVE-2026-8451

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…

This tool demonstrates CVE-2026-38194, a vulnerability in Teledyne Digital Imaging Sapera Memory Manager (v9.0.0.0 and below). The CORMEM.SYS kernel…

Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.

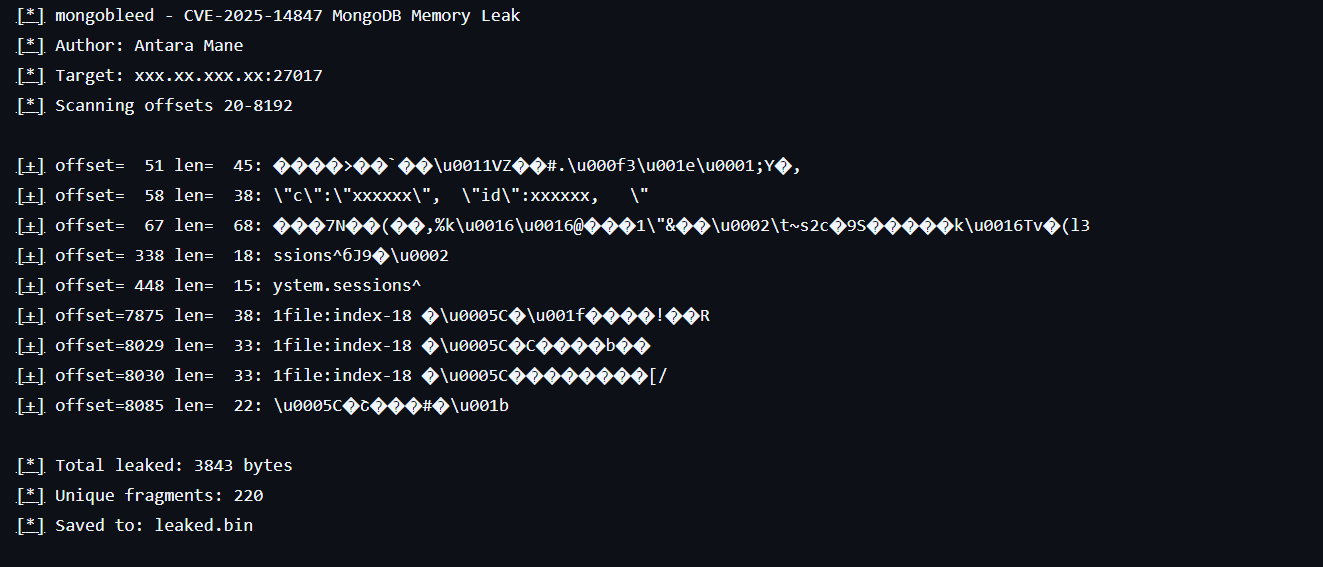
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…

CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…

Educational research tool demonstrating CVE-2025-14847 memory disclosure in MongoDB's BSON decompression. Simulates bounds-checking failures and…

MongoBleed: CVE-2025-14847 Memory Leak Discovery Tool

Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…

A frida tool to dump dex in memory to support security engineers analyzing malware.

Penetration testing utility and antivirus assessment tool.

Rip Raw is a small tool to analyse the memory of compromised Linux systems.

Finding secrets in kernel and user memory

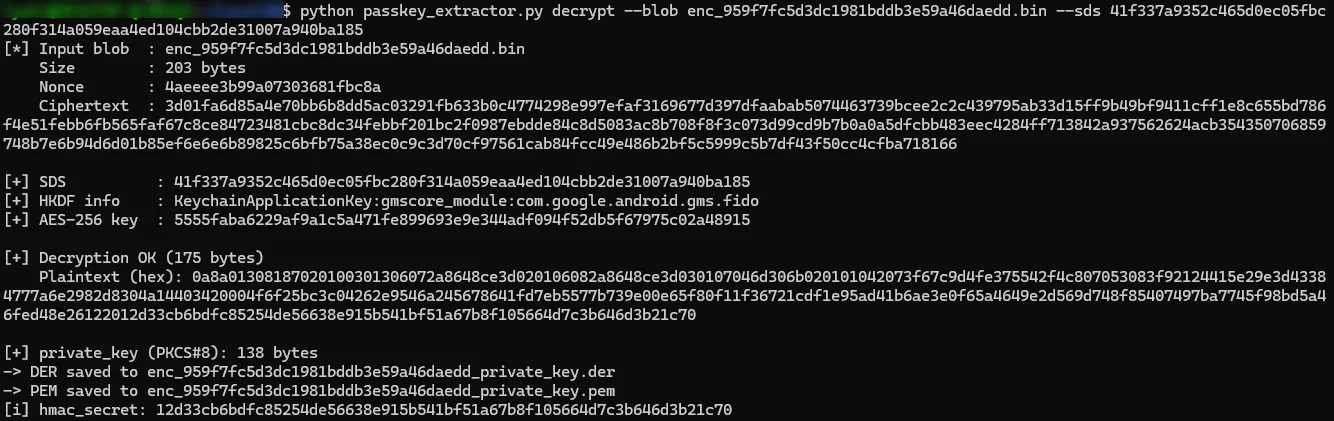
PoC that extracts the Google Password Manager Security Domain Secret from Chrome process memory and decrypts synced GPM passkey ECDSA P-256 private…

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…


Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

This is the development tree. Production downloads are at: