CVE-2019-19012
 tarantula-team/cve-2019-19012
An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
binary-analysisexploitationfuzzing+3
tarantula-team/cve-2019-19012An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
 bl4ck5un/cve-2013-2072
Buffer overflow in the Python bindings for the xc_vcpu_setaffinity call in Xen
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 volatilityfoundation/volatility
An advanced memory forensics framework
 dbrant/bios_memimage
RAM imaging utility.
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 csrxamfi/cve-2026-65330
Perl proof-of-concept exploit demonstrating a use-after-free in the NECP trie, with a heap spray option for triggering the kernel memory corruption.
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
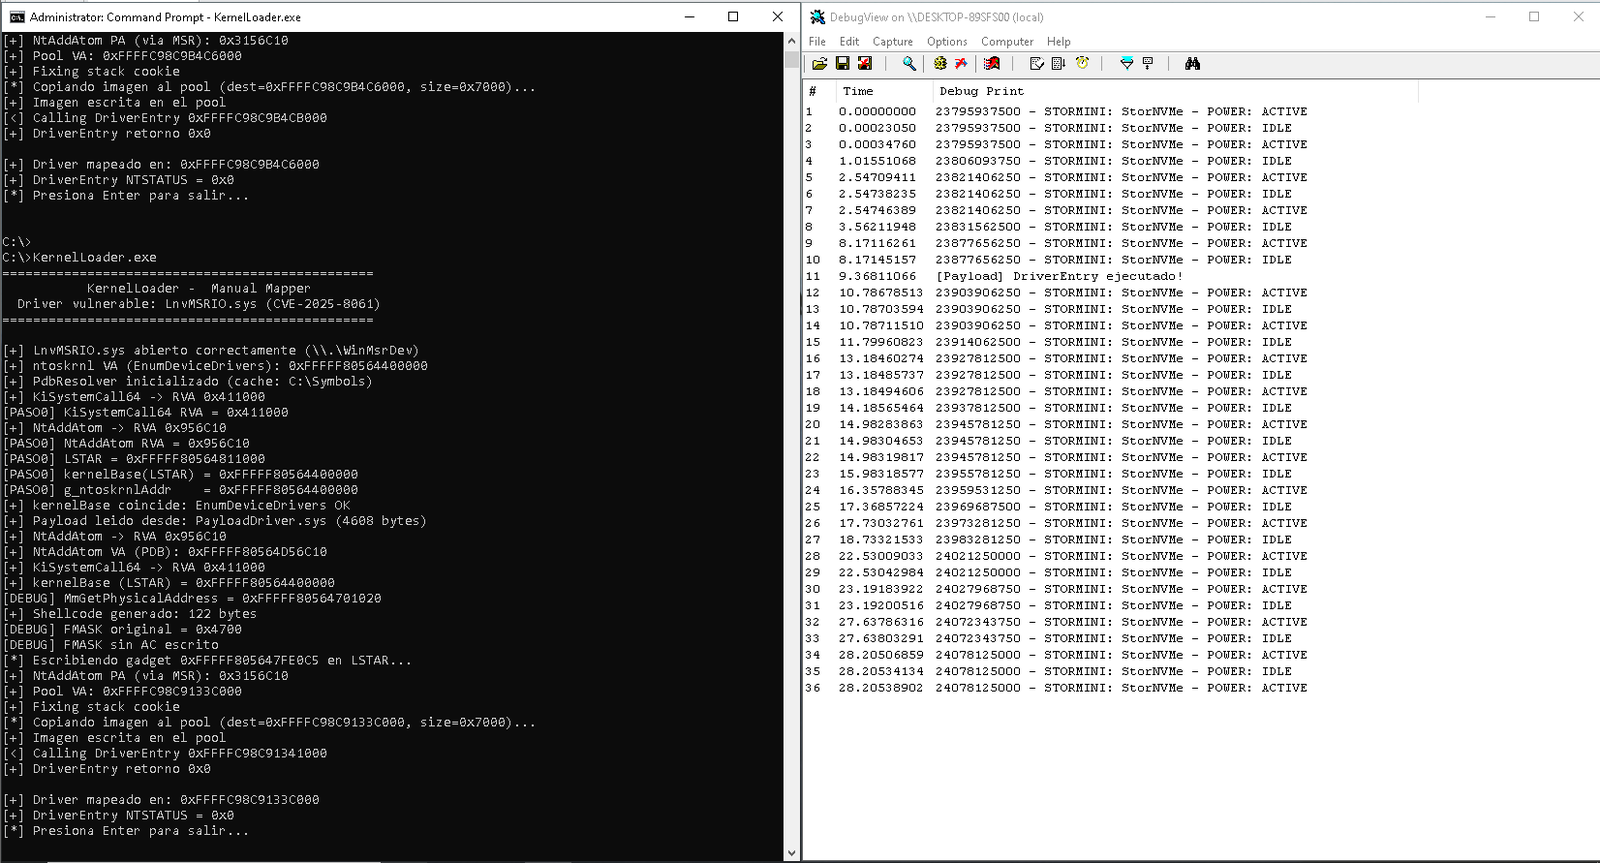 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 0vercl0k/cve-2021-32537
PoC for CVE-2021-32537: an out-of-bounds memory access that leads to pool corruption in the Windows kernel.
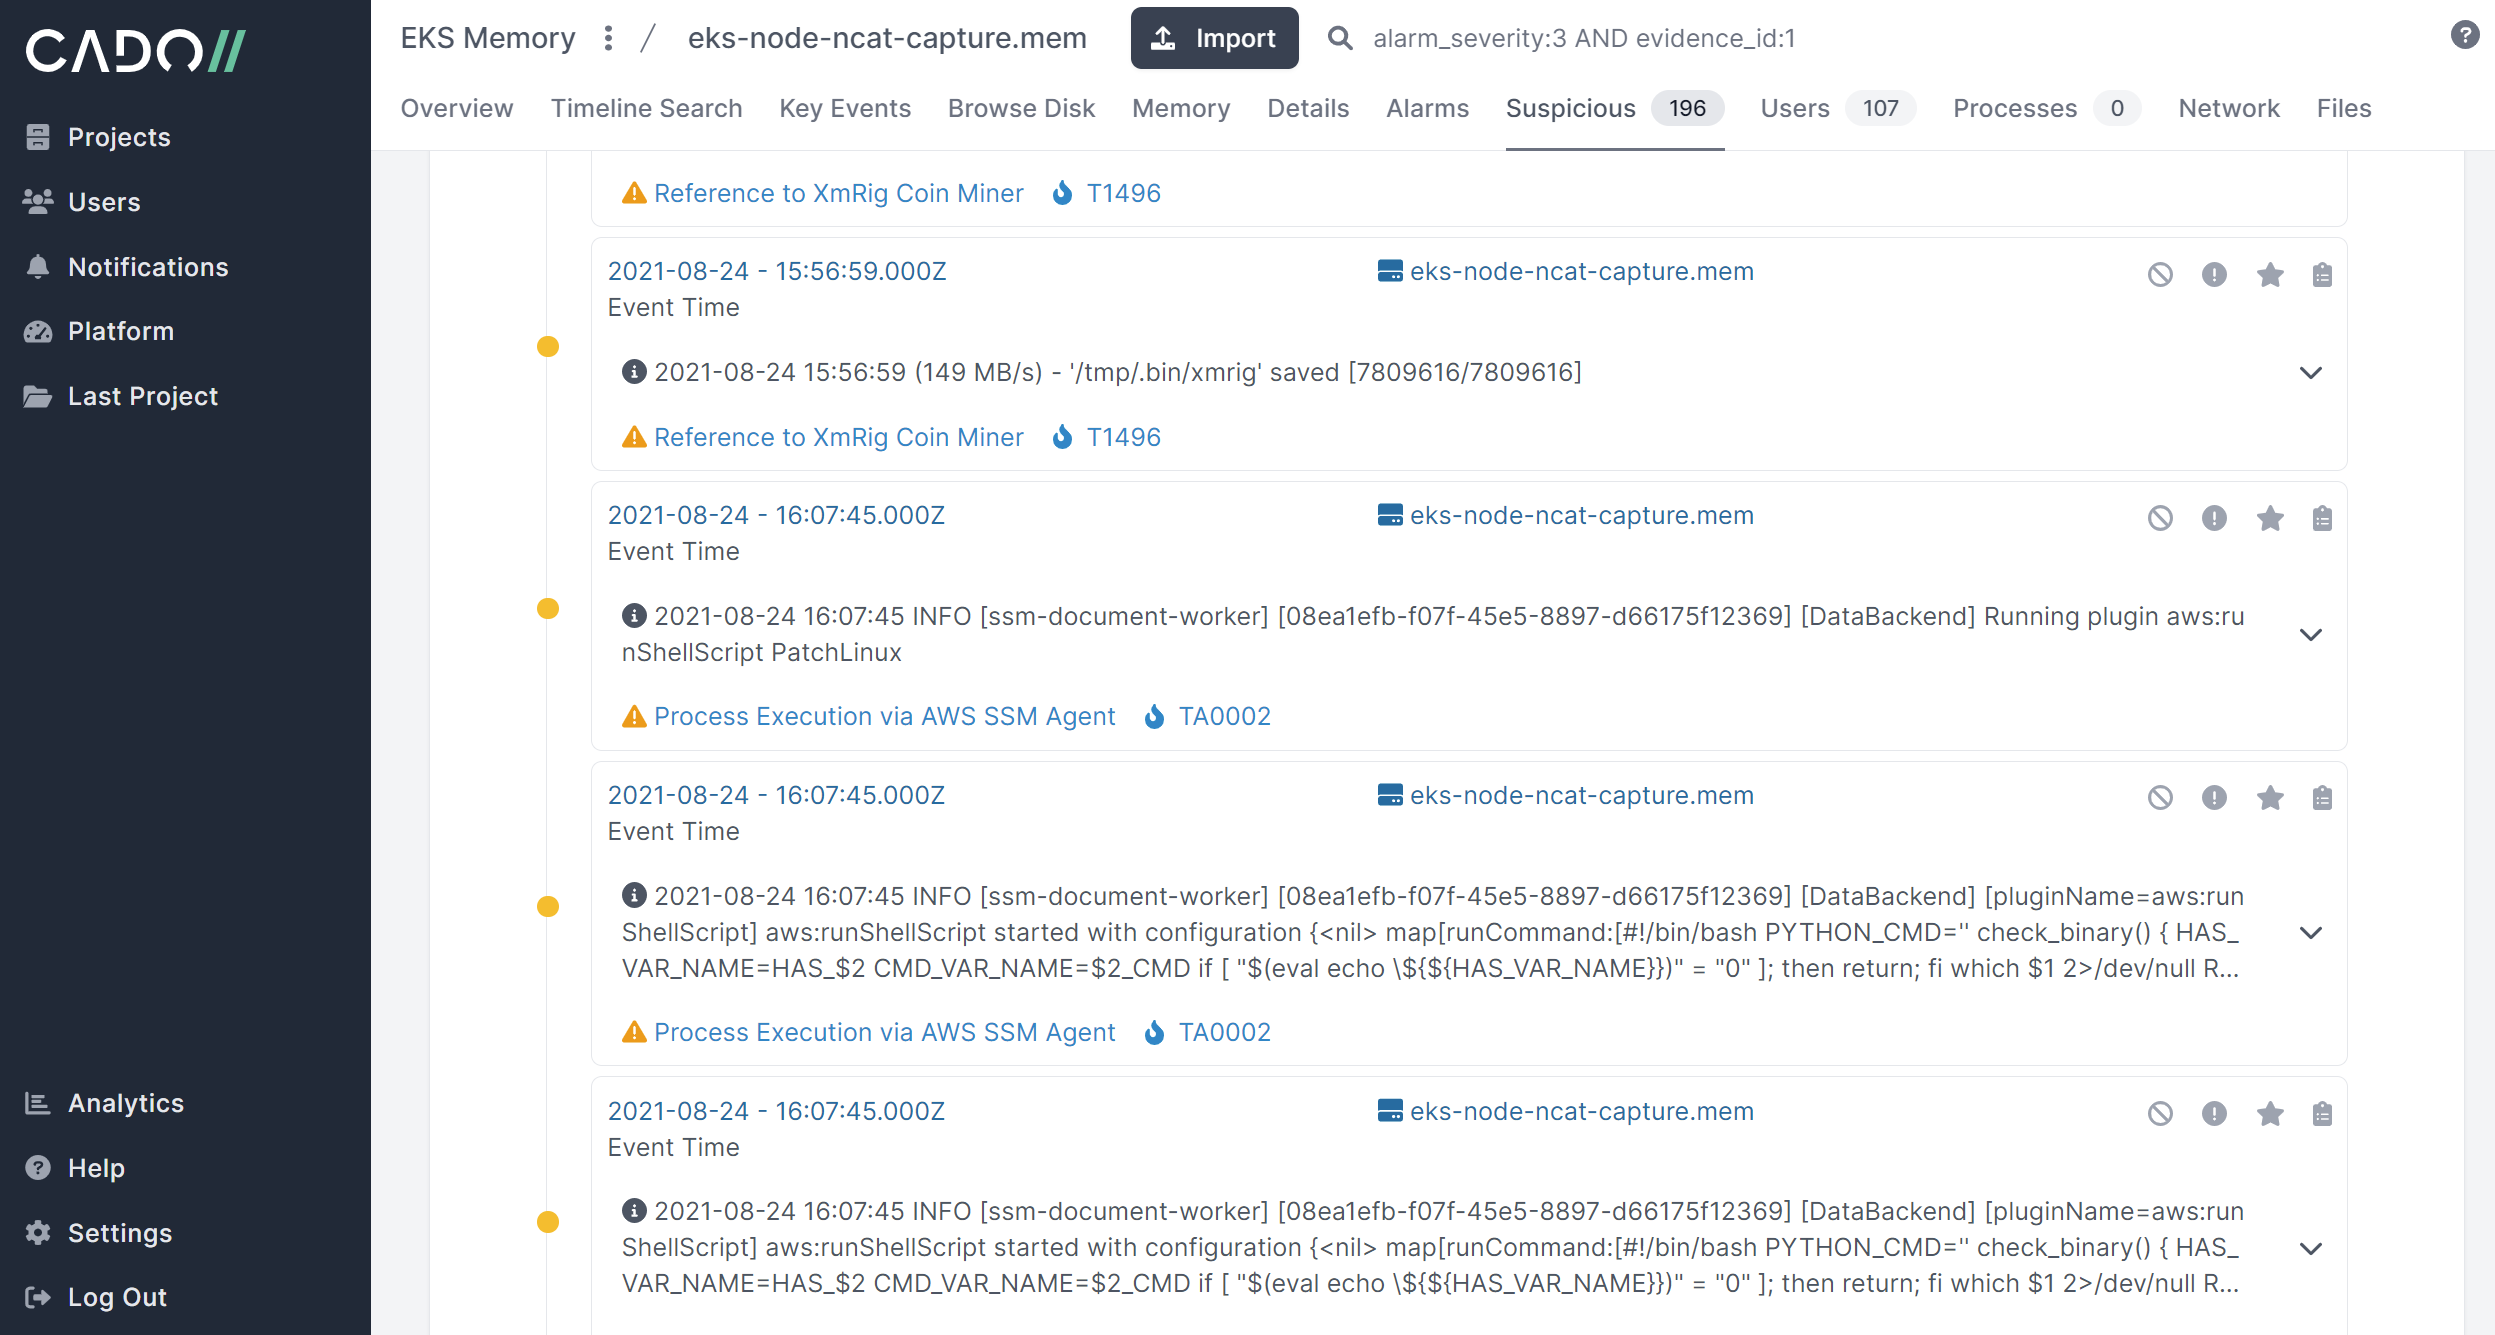 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.