

Archived
EDRSandblast-GodFault
 gabriellandau/edrsandblast-godfault
EDRSandblast-GodFault
defensive-toolsexploitationmemory-forensics+4
271
gabriellandau/edrsandblast-godfaultEDRSandblast-GodFault
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 isec-tugraz/meltdown
Proof-of-concept demos and libkdump library demonstrating the Meltdown microarchitectural attack, leaking kernel and physical memory on vulnerable…
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
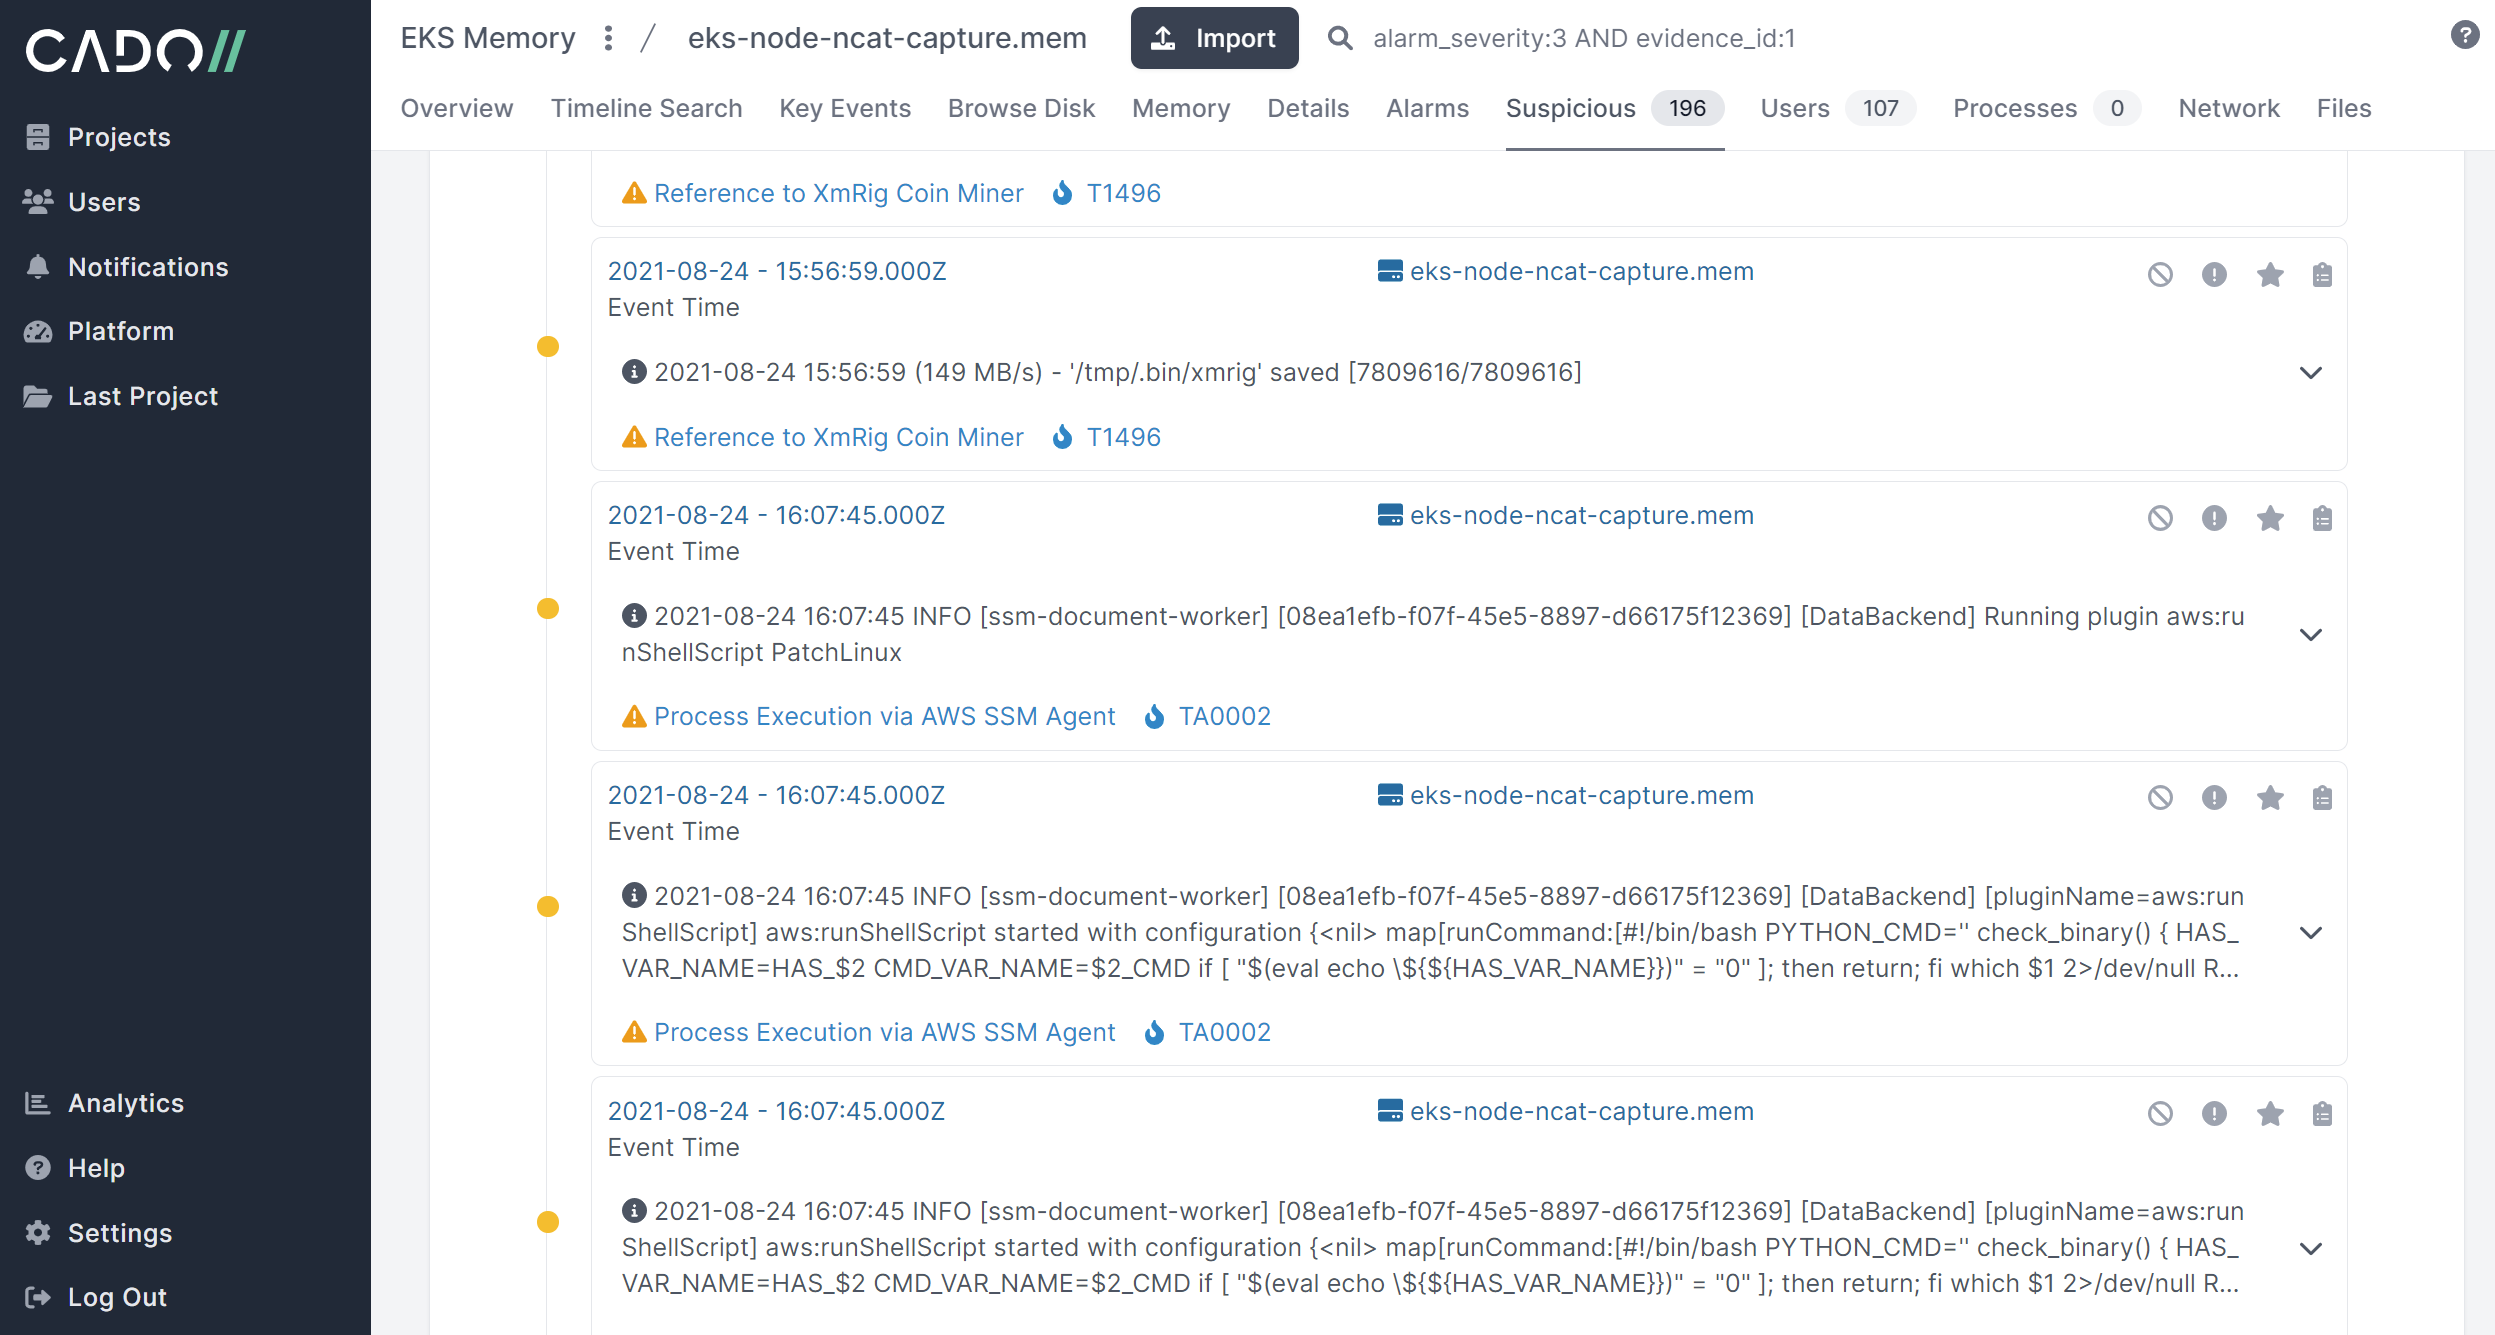 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 ntfargo/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
 itm4n/ppldump
Dump the memory of a PPL with a userland exploit
 504ensicslabs/damm
Differential Analysis of Malware in Memory
 memn0ps/illusion-rs
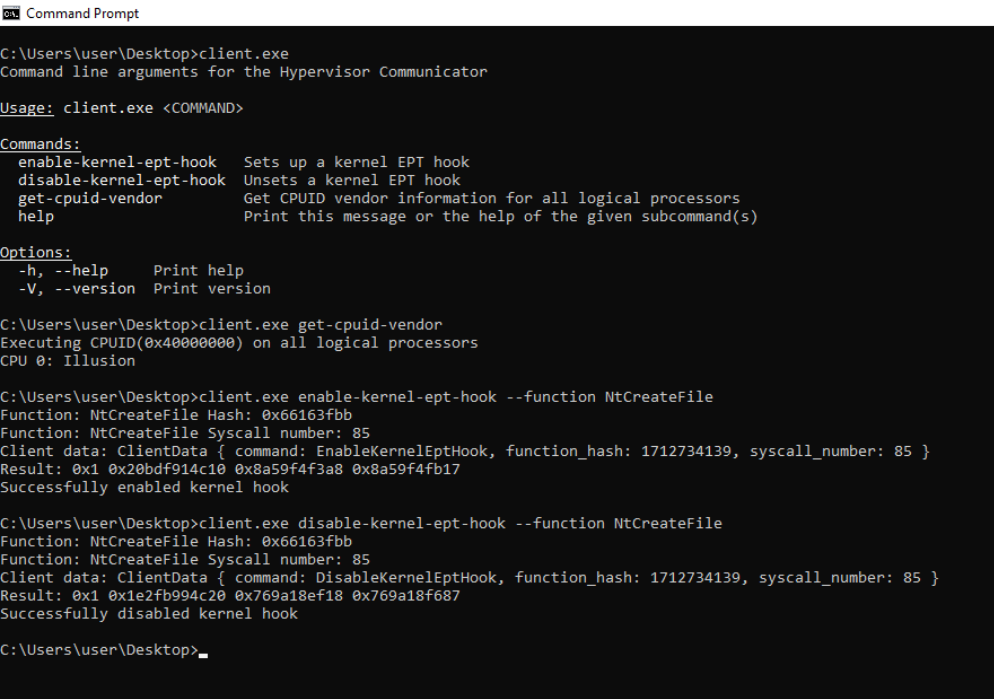
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)