
CVE-2023-6931
 k0n9-log/cve-2023-6931
CVE-2023-6931 kernel panic PoC
binary-exploitationeducationexploitation+2
2
k0n9-log/cve-2023-6931CVE-2023-6931 kernel panic PoC
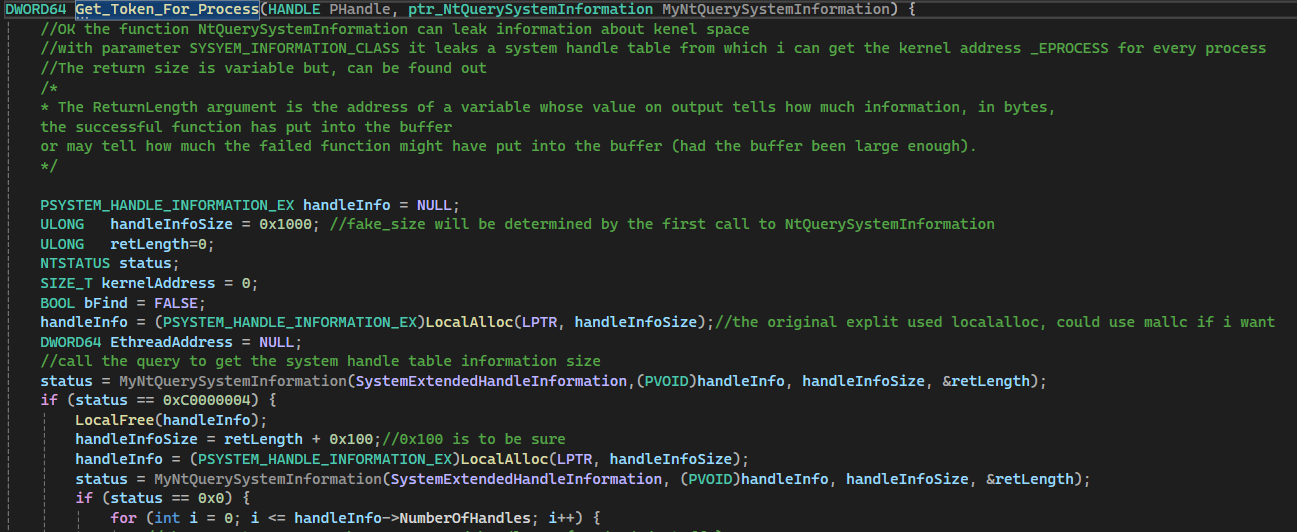 emilc3978/cve-2022-37969poc
Tutorial of CVE-2022-37969 with focus on the methodology of Kernel exploitation, not CVE's internal causes
 smarttfoxx/cve-2025-60791
Easywork Enterprise 2.1.3.354 is vulnerable to Cleartext Storage of Sensitive Information in Memory. The application leaves valid device-bound…
 ngtuonghung/cve-2021-3156
POC for CVE-2021-3156 - Heap-based buffer overflow in sudo
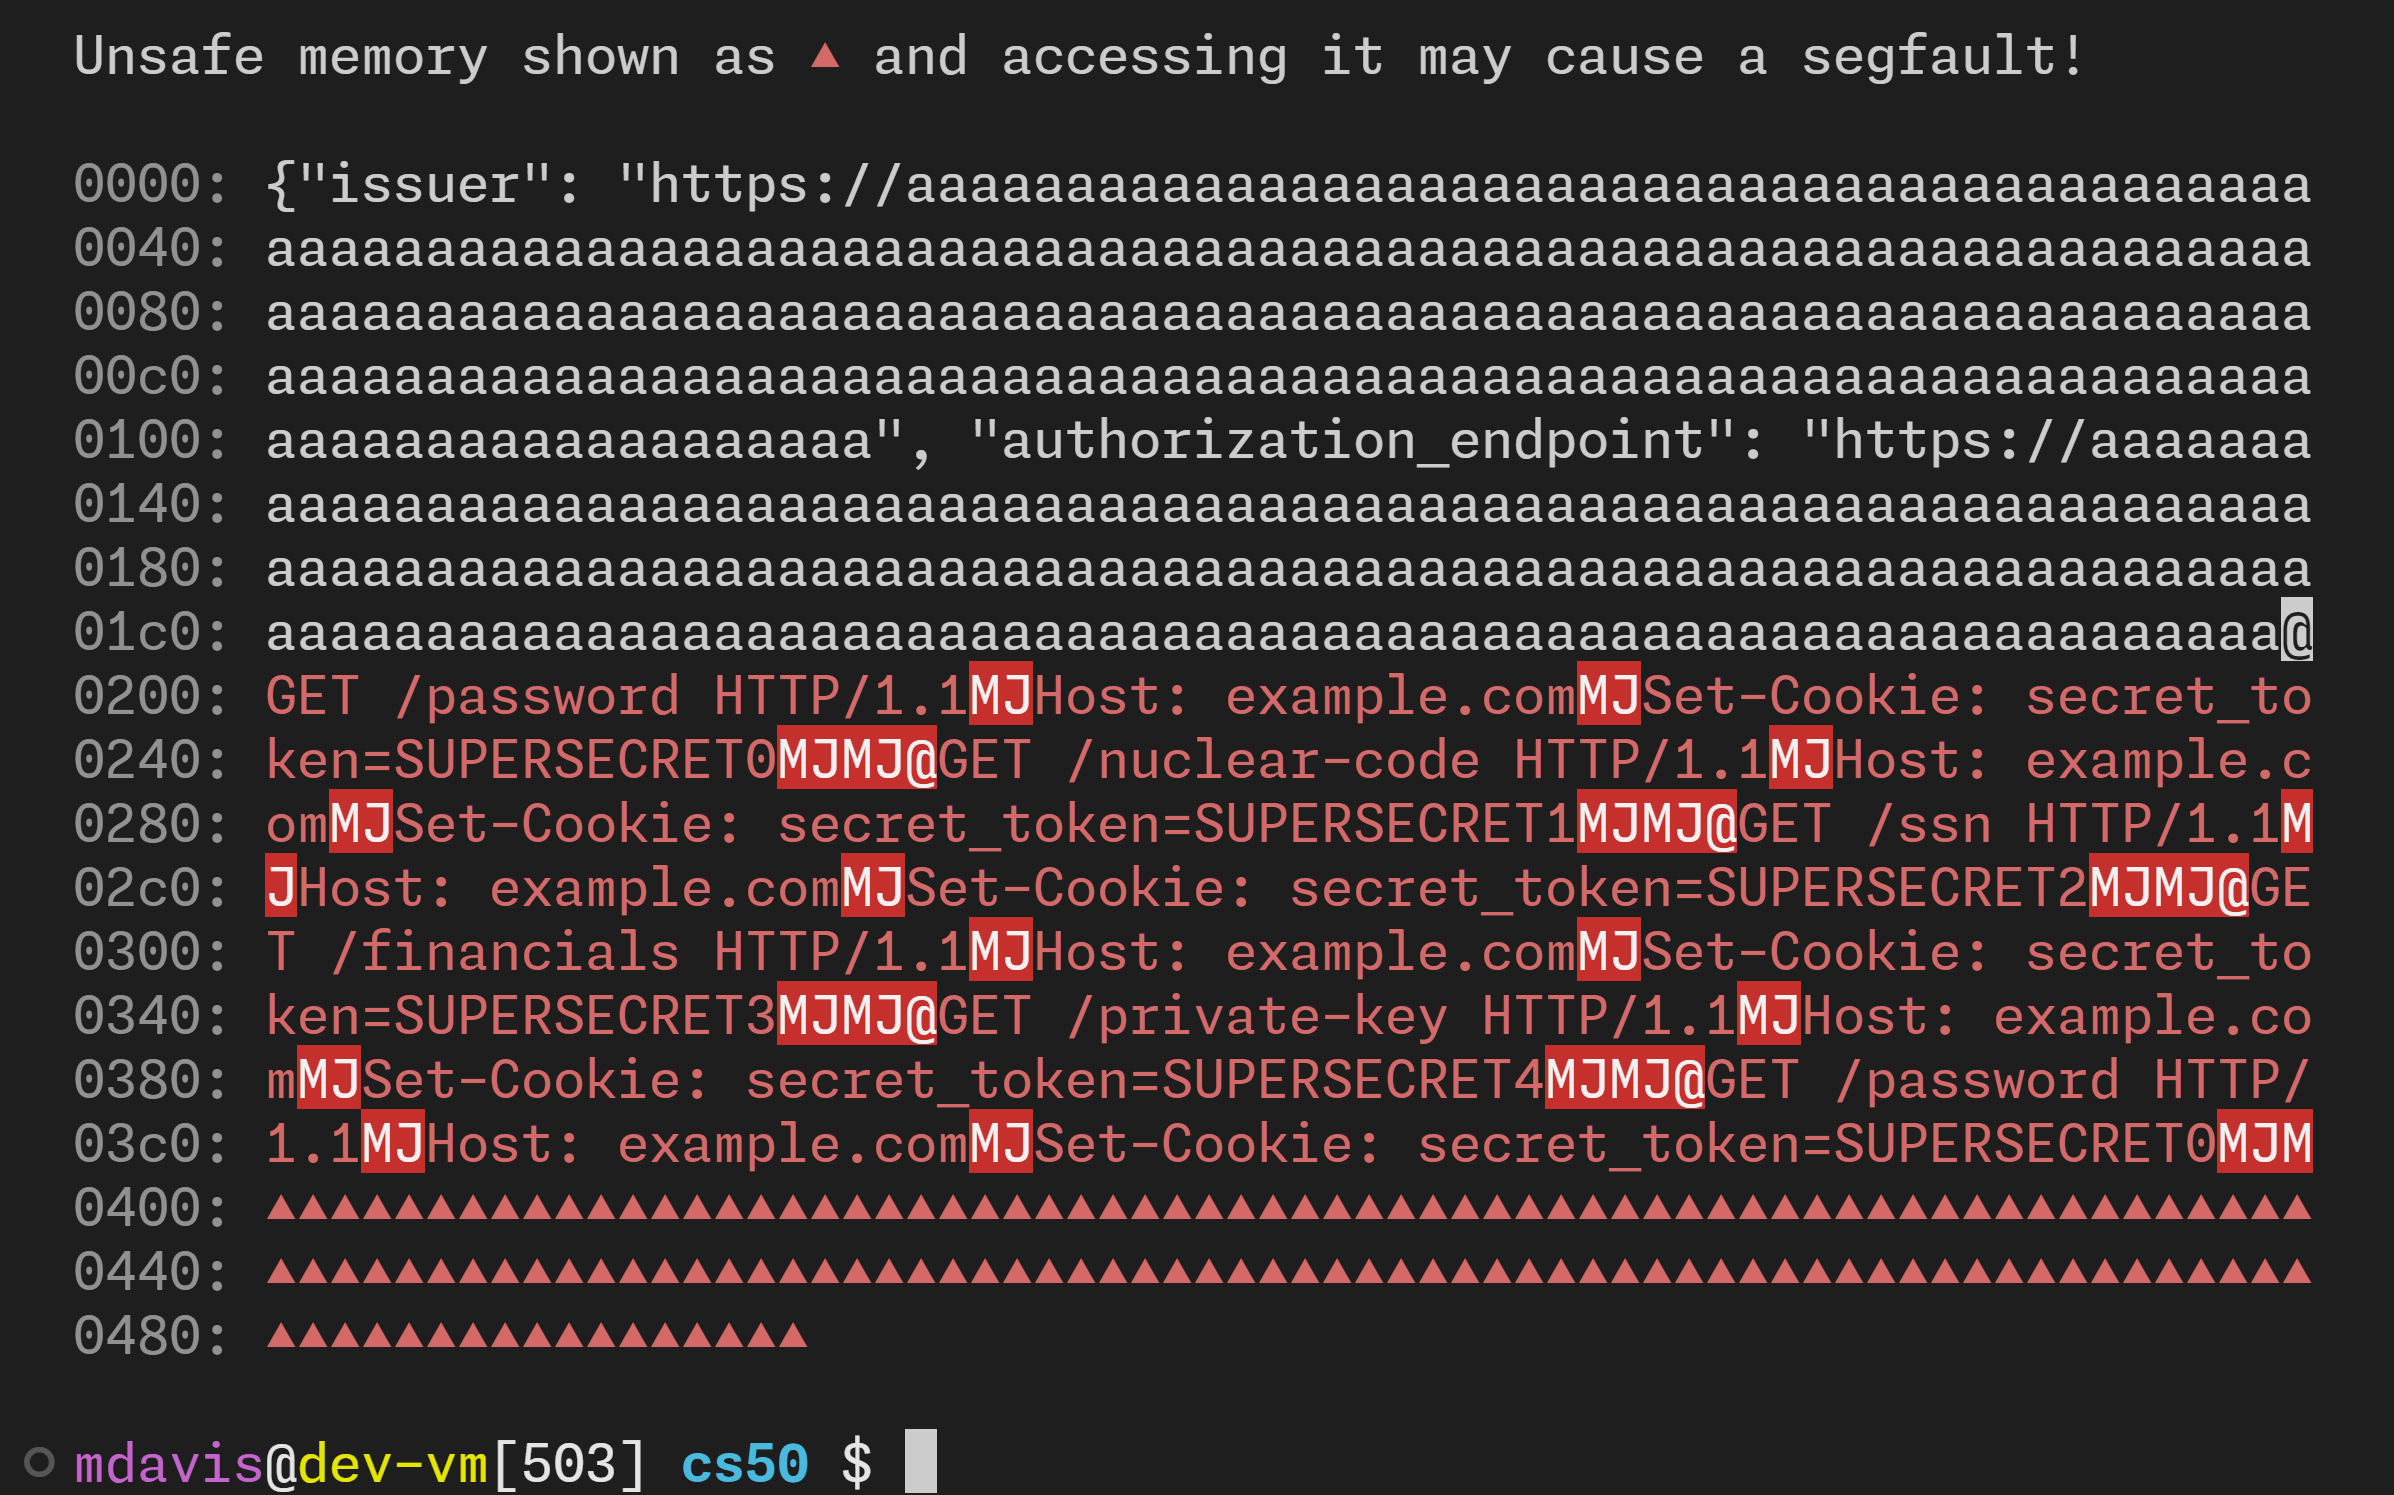 morganwdavis/overread
Simulates CVE-2023-4966 Citrix Bleed overread bug
 eaea0001/servu-cve-2026-28318-poc
SolarWinds Serv-U CVE-2026-28318: unauthenticated Content-Encoding: deflate crash. Root-cause analysis (invalid free of an interior pointer -> heap…
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 quasarbinary/cve-2024-43630-poc
NtCopyFileChunk stack buffer overflow POC
 muhammedhussein17/libheif-cve-2026-50142
CVE-2026-50142 — Heap allocation vulnerability in libheif HEIF sequence parser
 akrachli/cve-2024-29050
CVE-2024-29050 is a vulnerability found in the Windows Cryptographic Services.
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 ledlight33/copyfail-dfir
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
 rat5ak/cve-2026-3805-curl-smb-uaf
CVE-2026-3805: Use-After-Free in curl SMB connection reuse - heap info disclosure
 valium007/qiomem
Toshiba Qiomem.sys vulnerable driver POC (CVE-2026-56129)
 faizan-khanx/cve-2024-38063
CVE-2024-38063 - Remotely Exploiting The Kernel Via IPv6
 spiralbl0ck/sidechannel-cve-2022-38029
SIDECHANNEL+CVE-2022-38029
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …