
ghost-hoock
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
android-securitybinary-exploitationexploitation+6
1
deaurity/ghost-hoockGhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
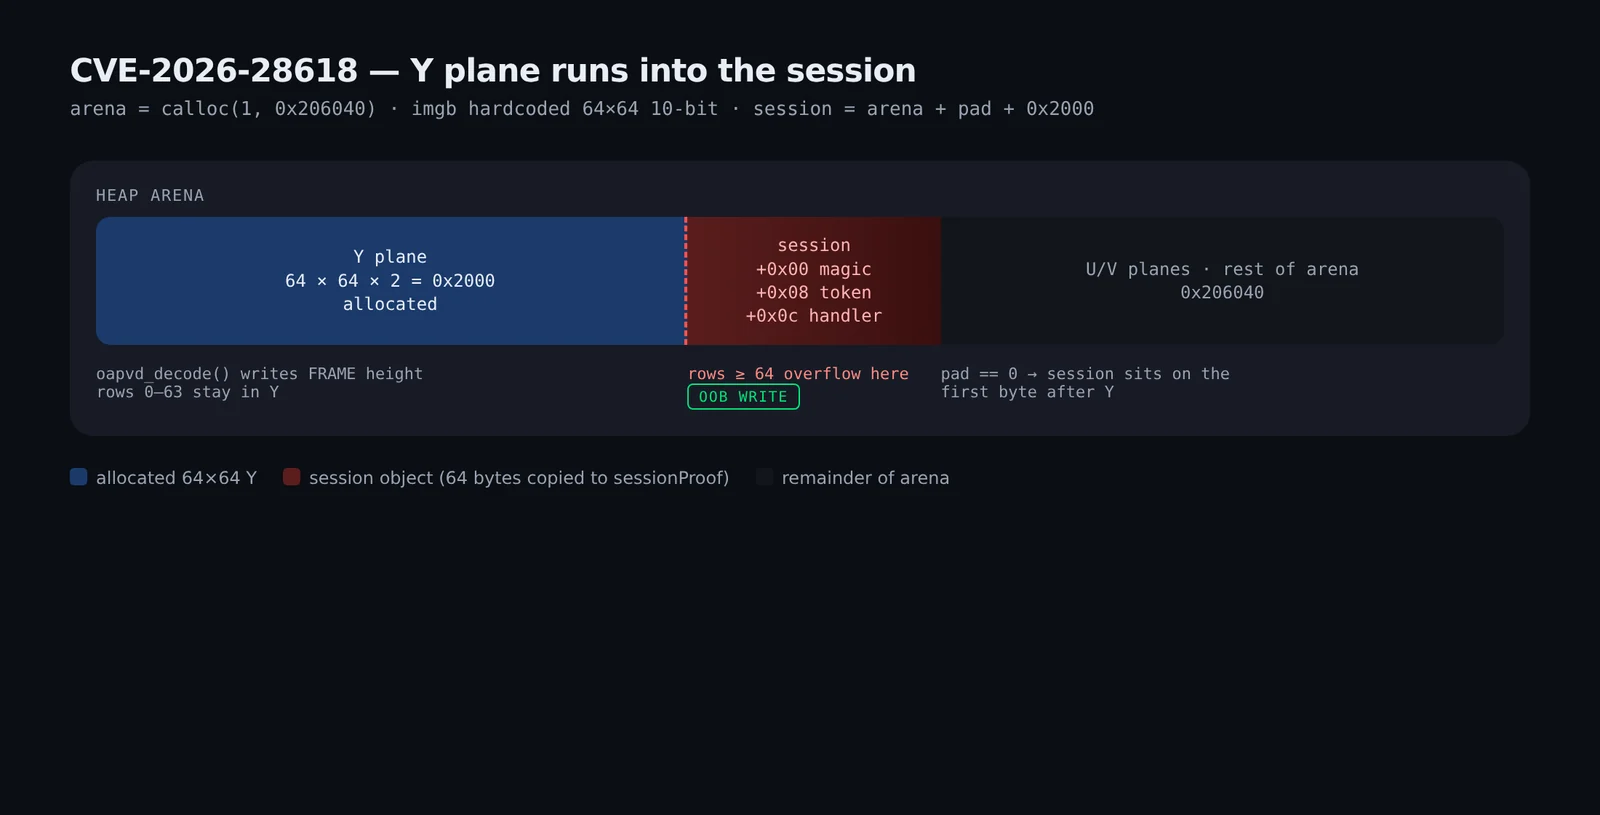 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 rootxsushant/citrix-netscaler-memory-leak-cve-2025-5777
Update the old POC of CVE-2025-5777 Citrix NetScaler Memory leak
 natleoj/cve-2019-11933
Heap corruption in WhatsApp's media picker
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
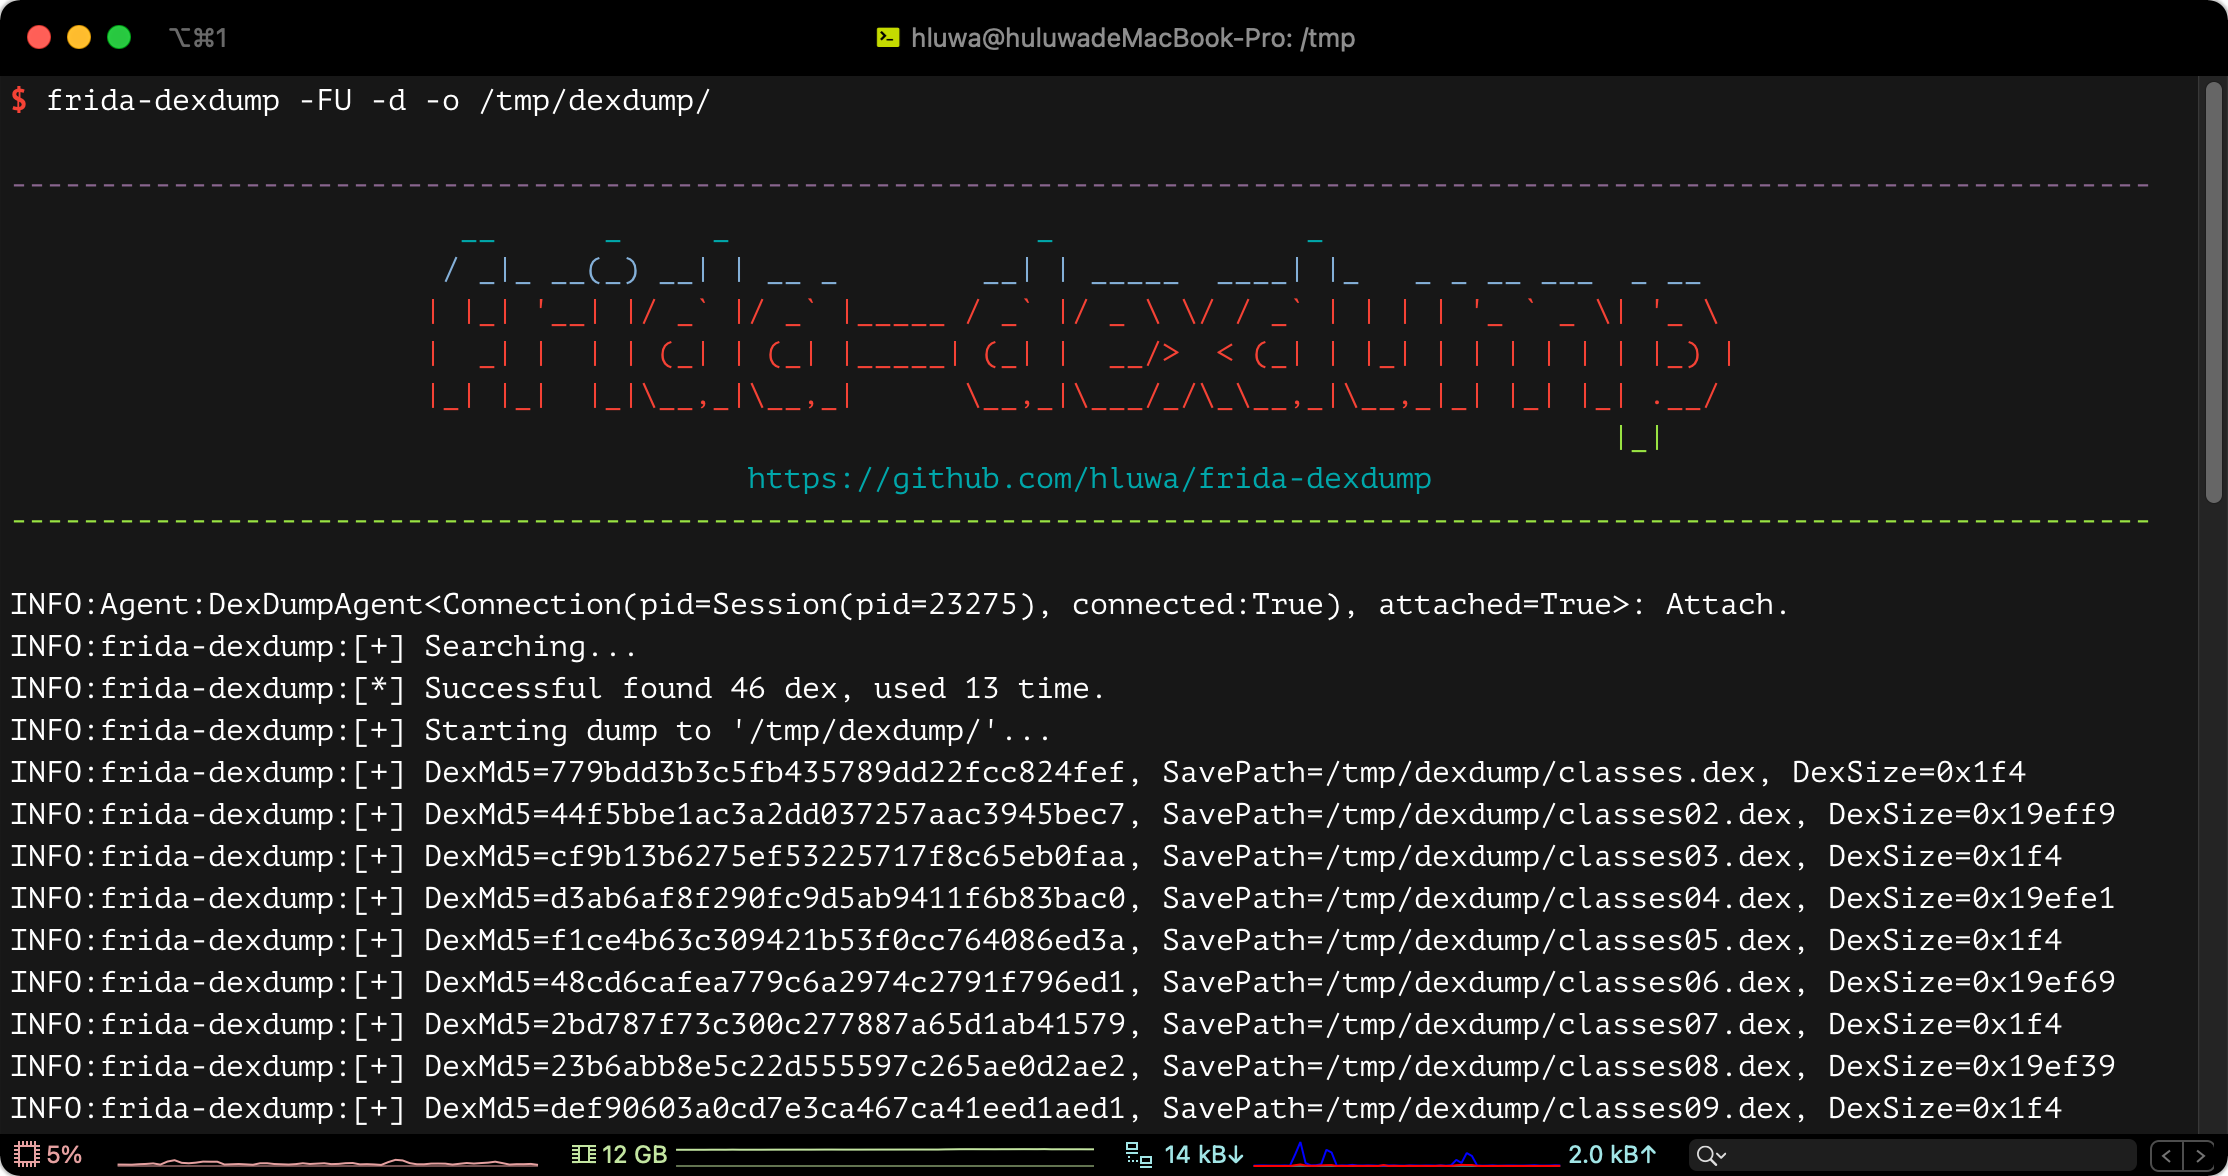 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.