NTDLL-Unhook
 hwbp/ntdll-unhook
proper ntdll .text section unhooking via native api. unlike other unhookers this doesnt leave 2 ntdlls loaded. x86/x64/wow64 supported.
malware-analysismemory-forensicspenetration-testing+2
56
hwbp/ntdll-unhookproper ntdll .text section unhooking via native api. unlike other unhookers this doesnt leave 2 ntdlls loaded. x86/x64/wow64 supported.
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 t-tani/yama-dev
Yet Another Memory Analyzer for malware detection
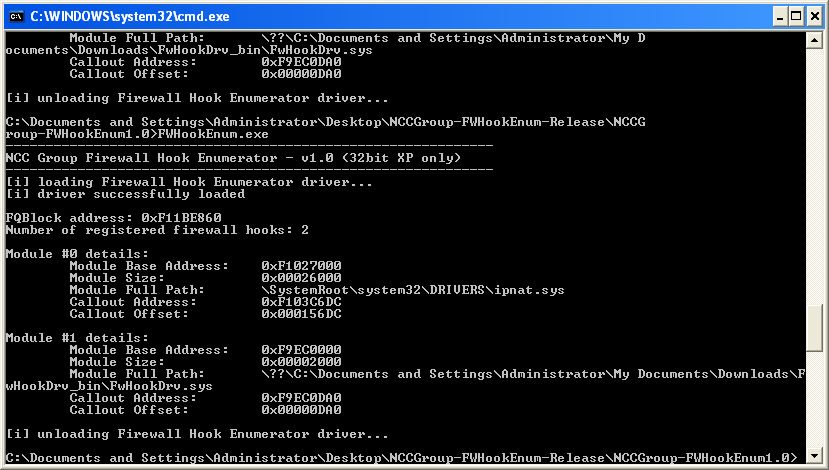 nccgroup/windowsfirewallhookdriverenumeration
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
 withsecurelabs/memory-carving-scripts
Scripts for extracting useful information from infected memory dumps
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 bedazzlinghex/memory-analysis
Contains tools to perform malware and forensic analysis in Memory
 volatilityfoundation/volatility
An advanced memory forensics framework