

patriot
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
164
joe-desimone/patriotIn-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 smolfiddle/sentinelnav
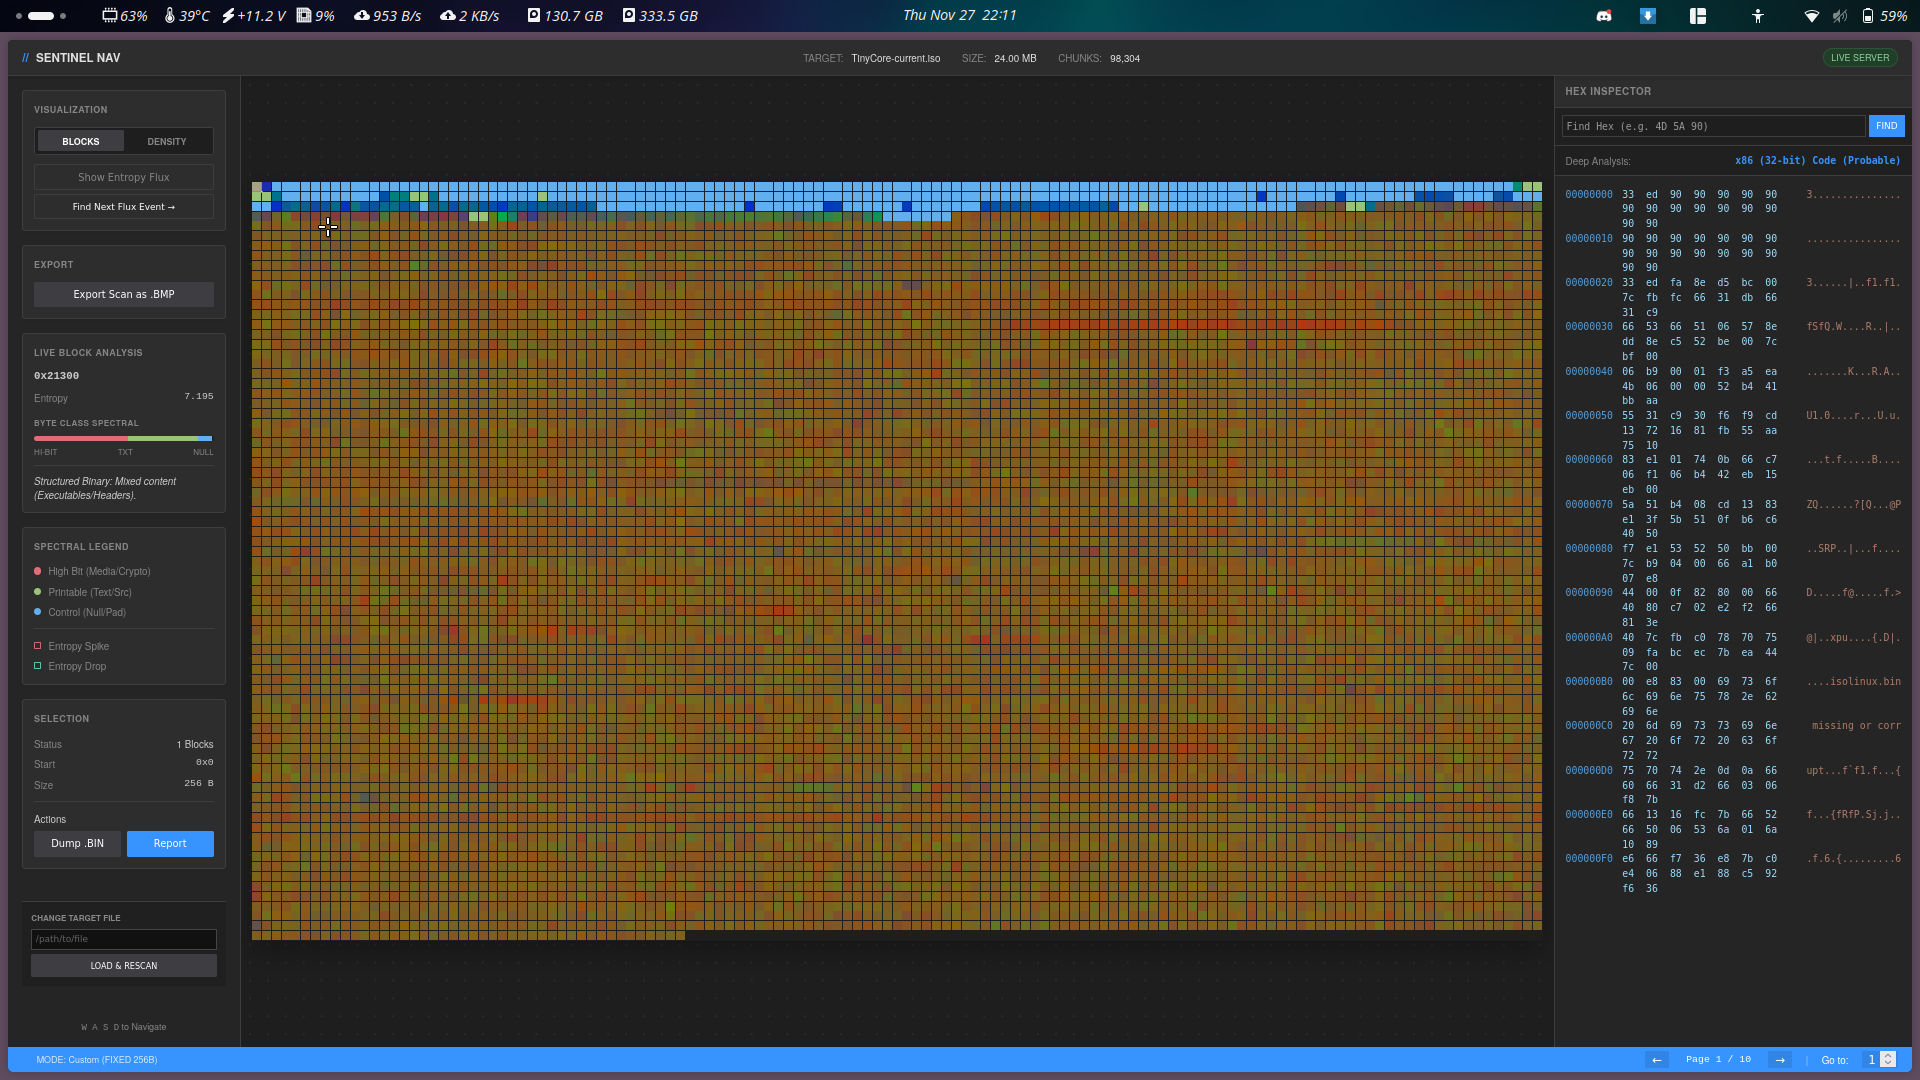
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
 ekknod/amdryzenmastercheat
Exploit tool leveraging CVE-2020-12928 (AMD RyzenMaster driver) for game memory manipulation and anti-cheat bypass on Windows 10 with AMD Ryzen CPUs.
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 egebalci/ticketbleed
This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 hamza-megahed/volatility-gui
GUI for Volatility forensics tool written in PyQT5
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…