

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k8 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 angr/angr
A powerful and user-friendly binary analysis platform!
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
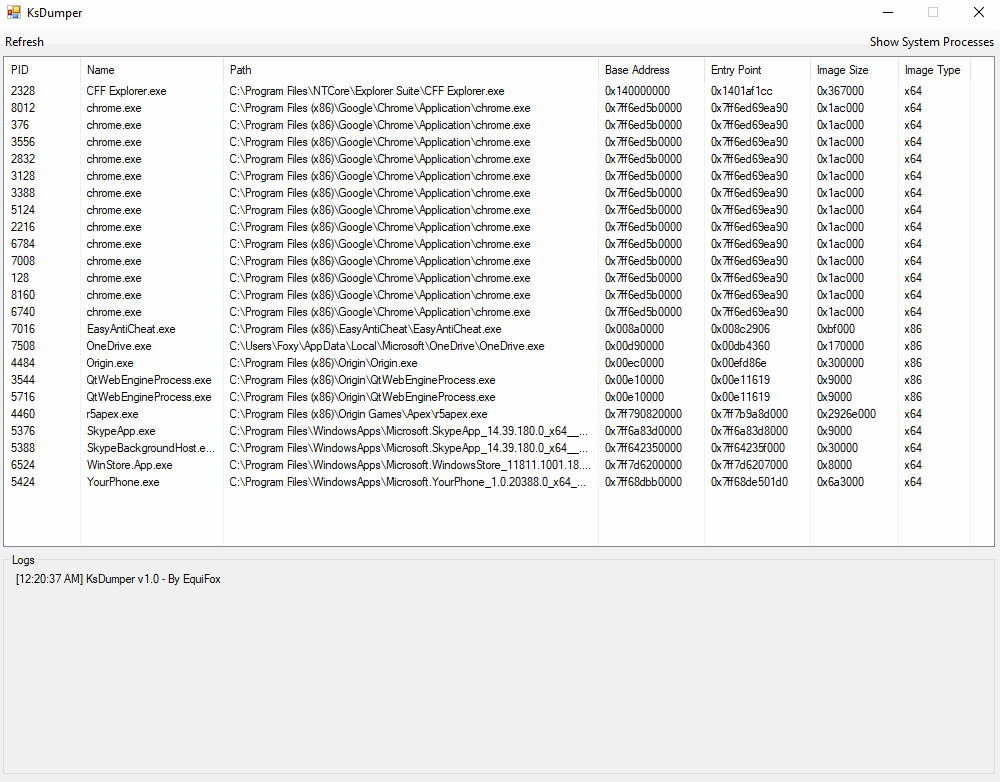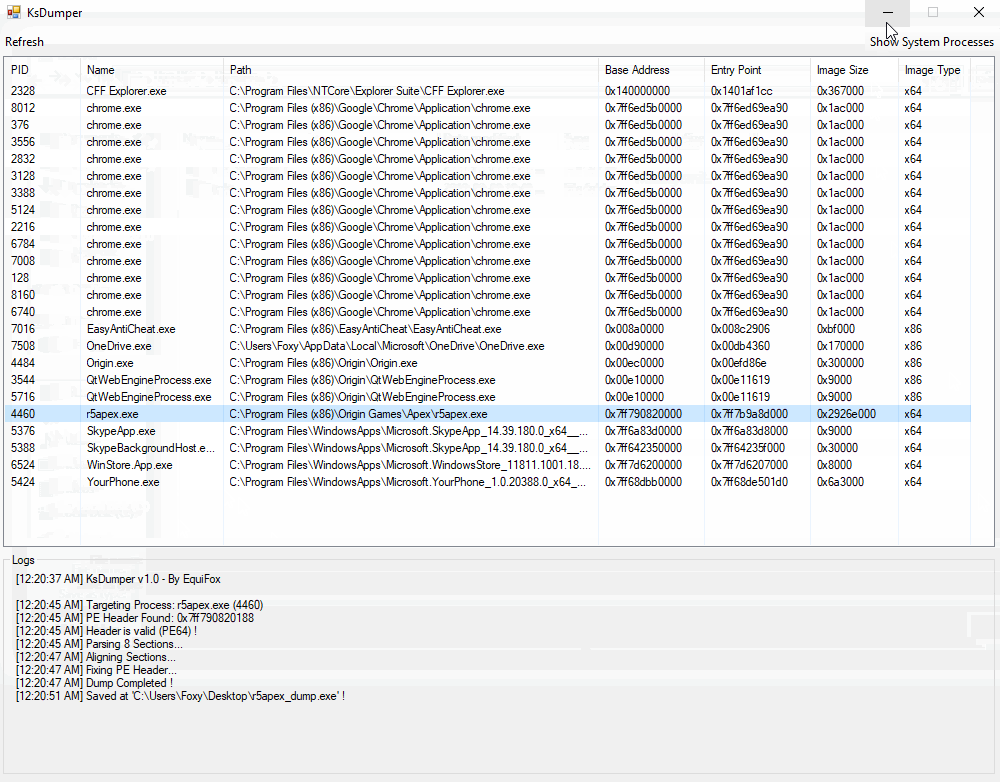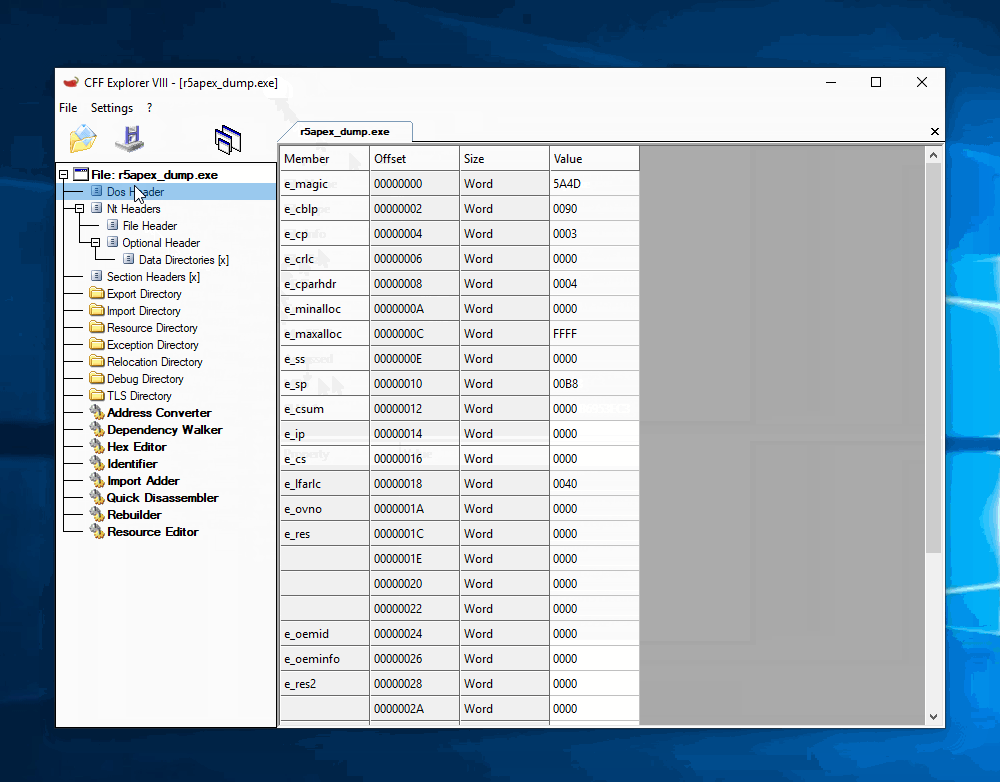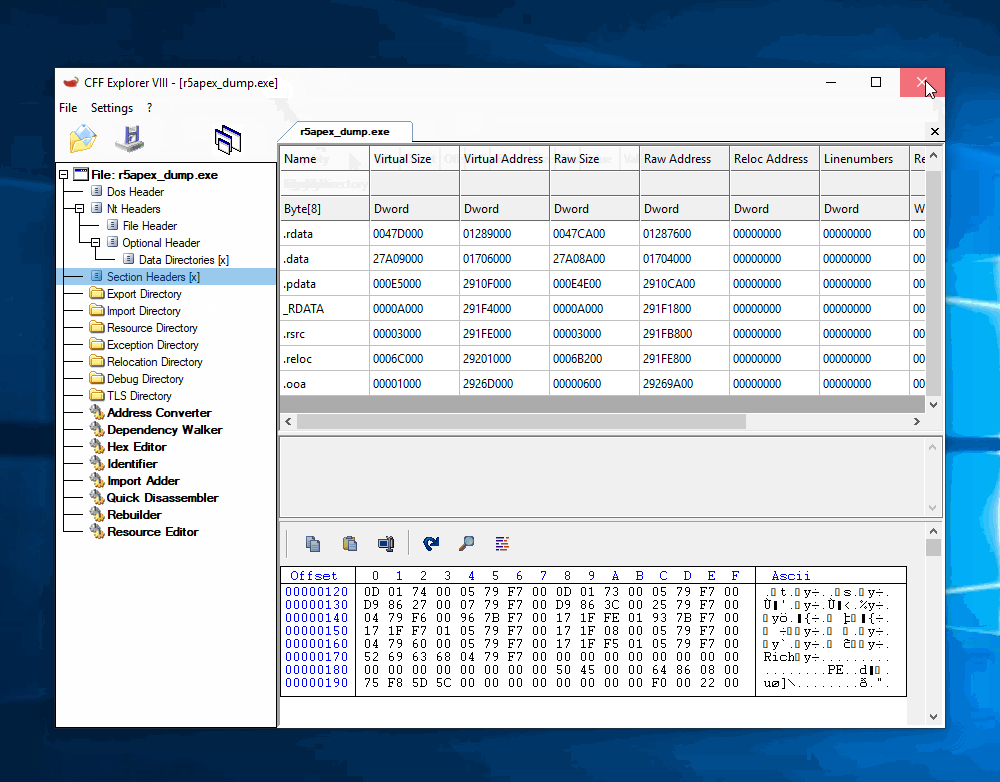 equifox/ksdumper
Dumping processes using the power of kernel space !
 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 leesh3288/cve-2025-32023
PoC & Exploit for CVE-2025-32023 / PlaidCTF 2025 "Zerodeo"
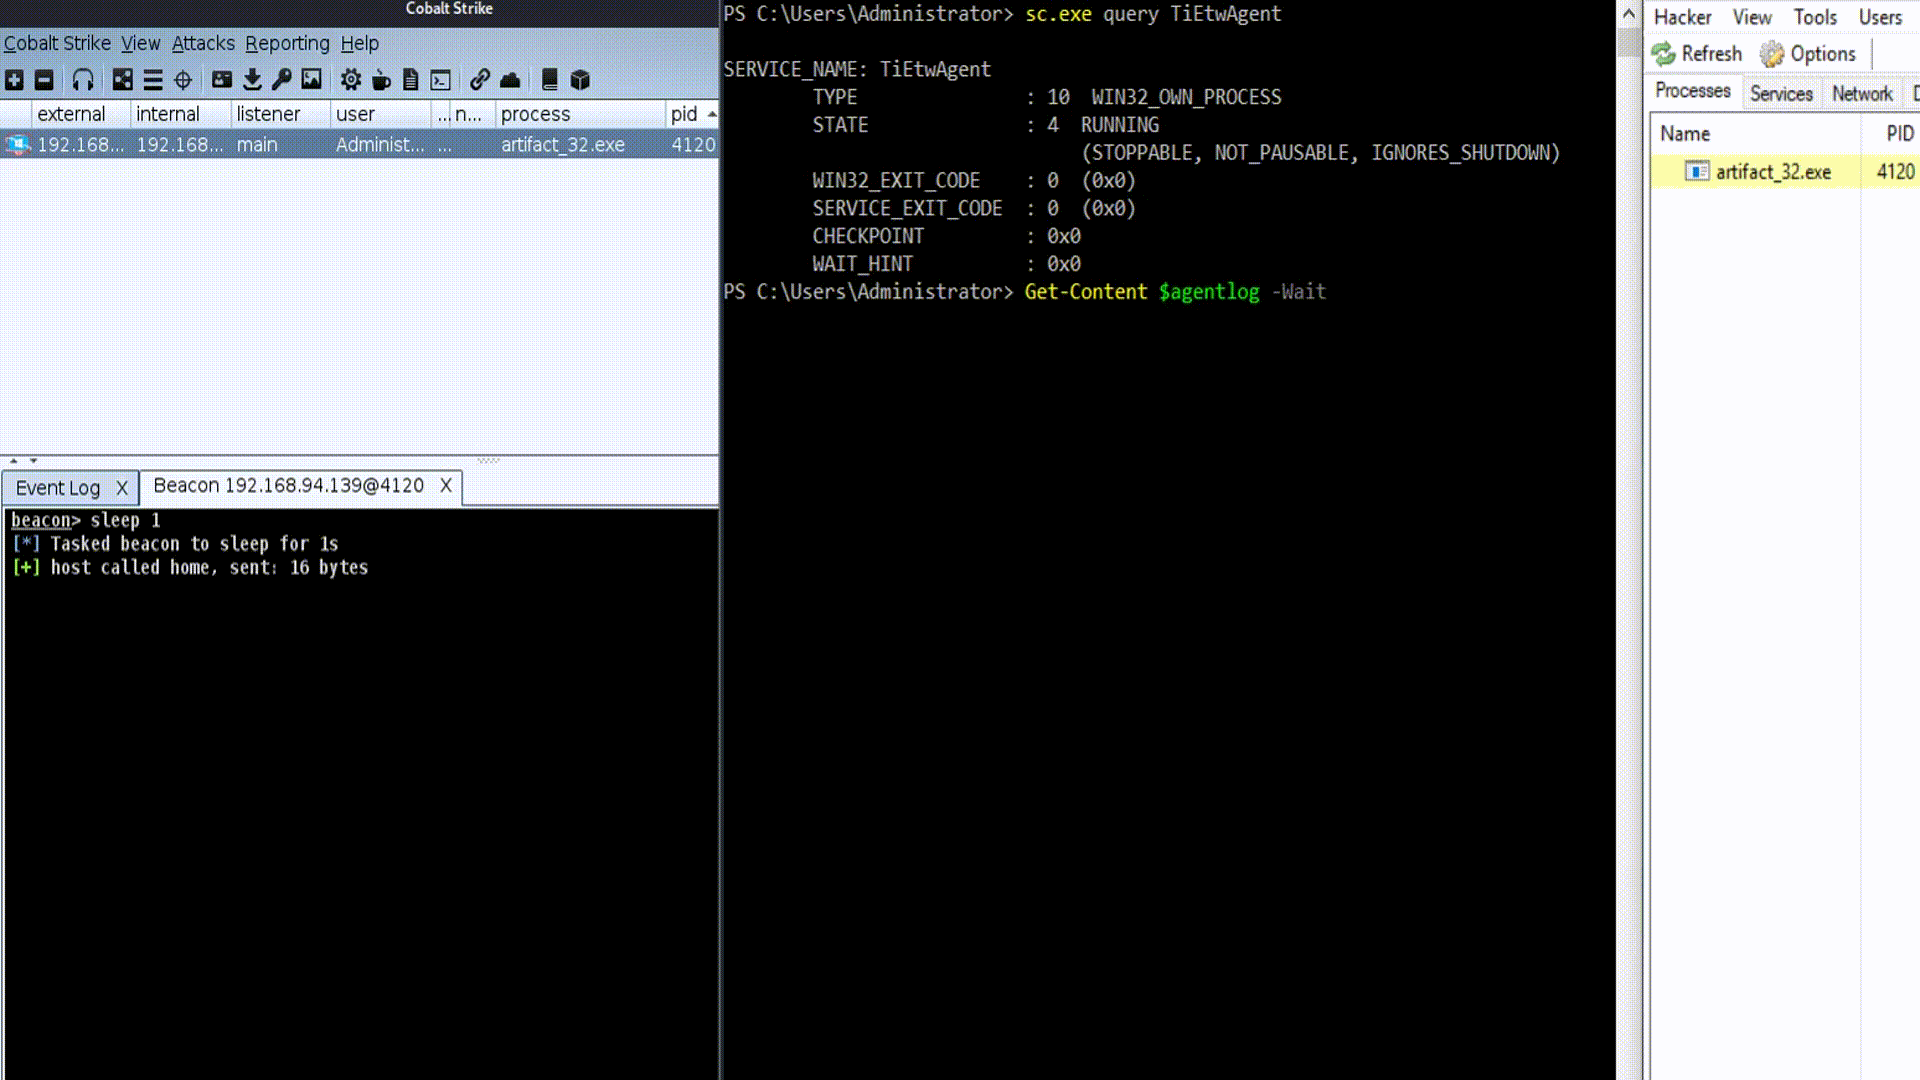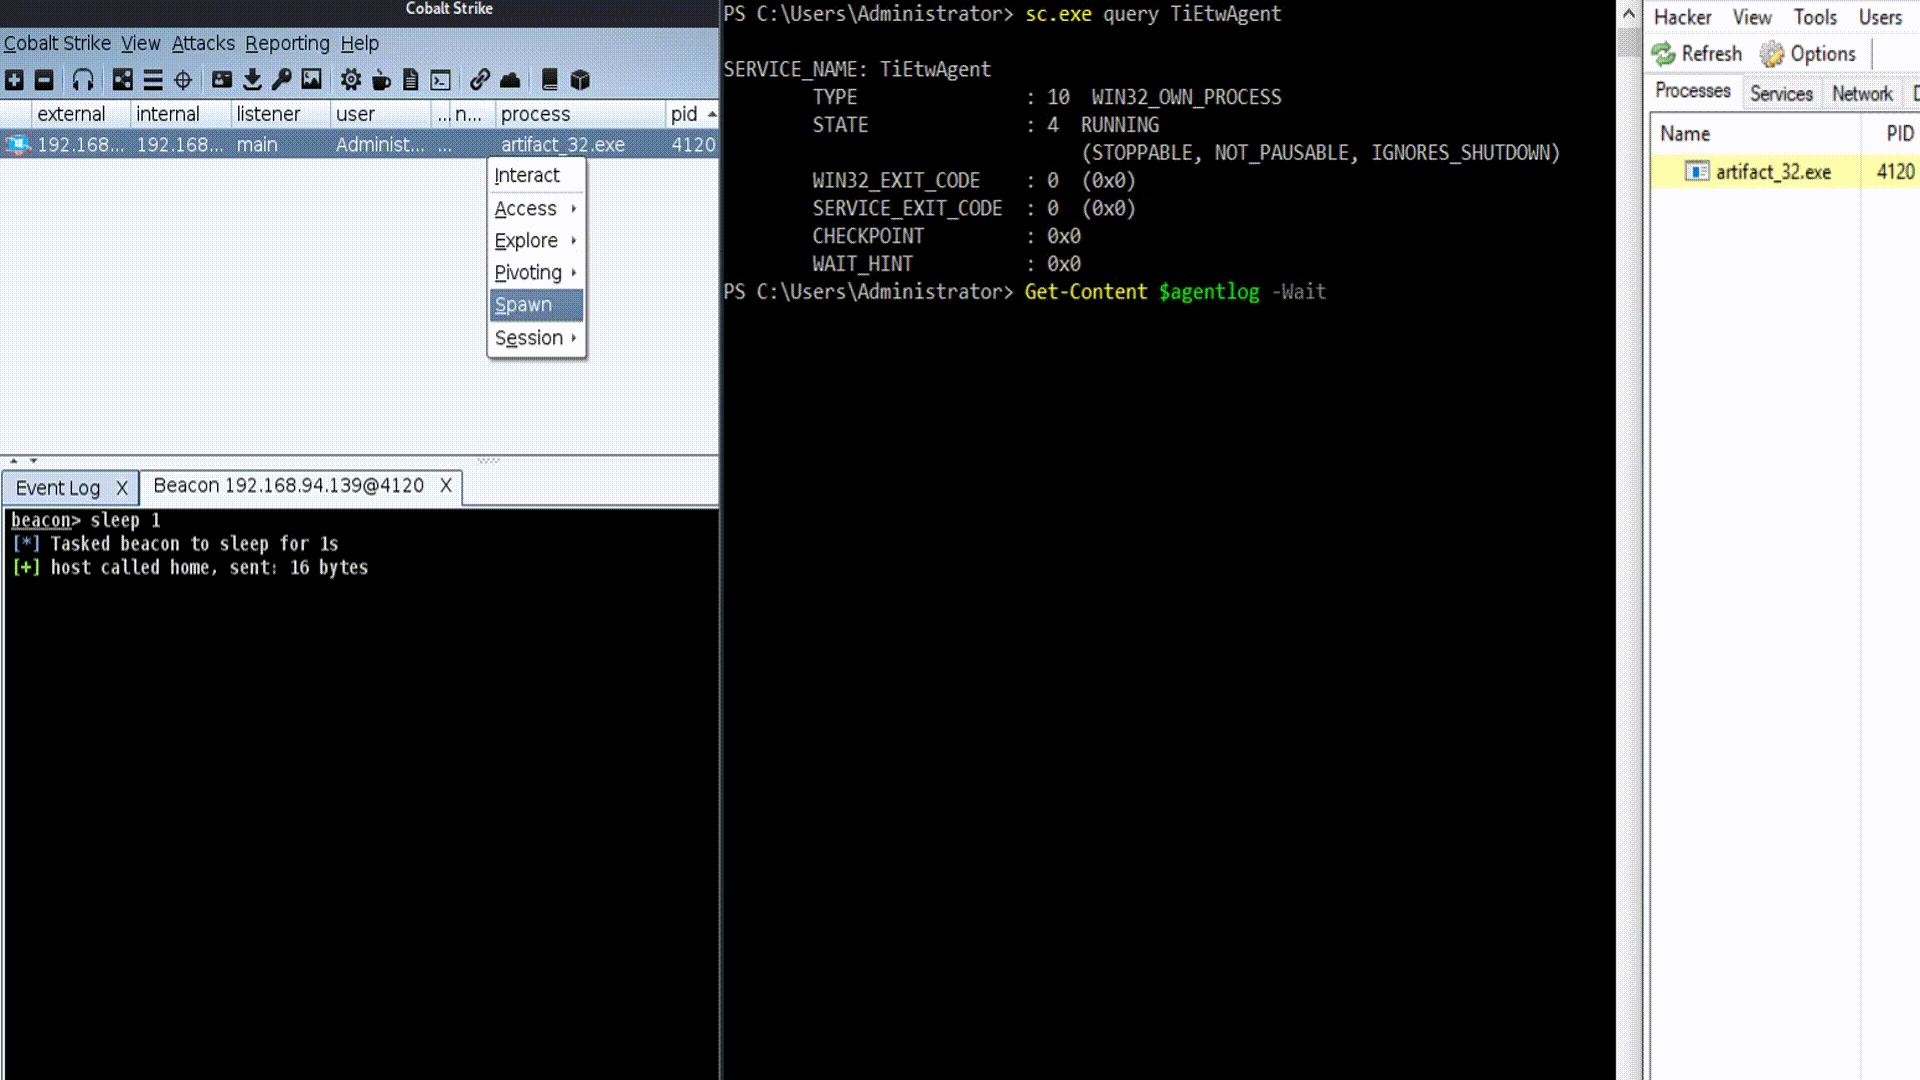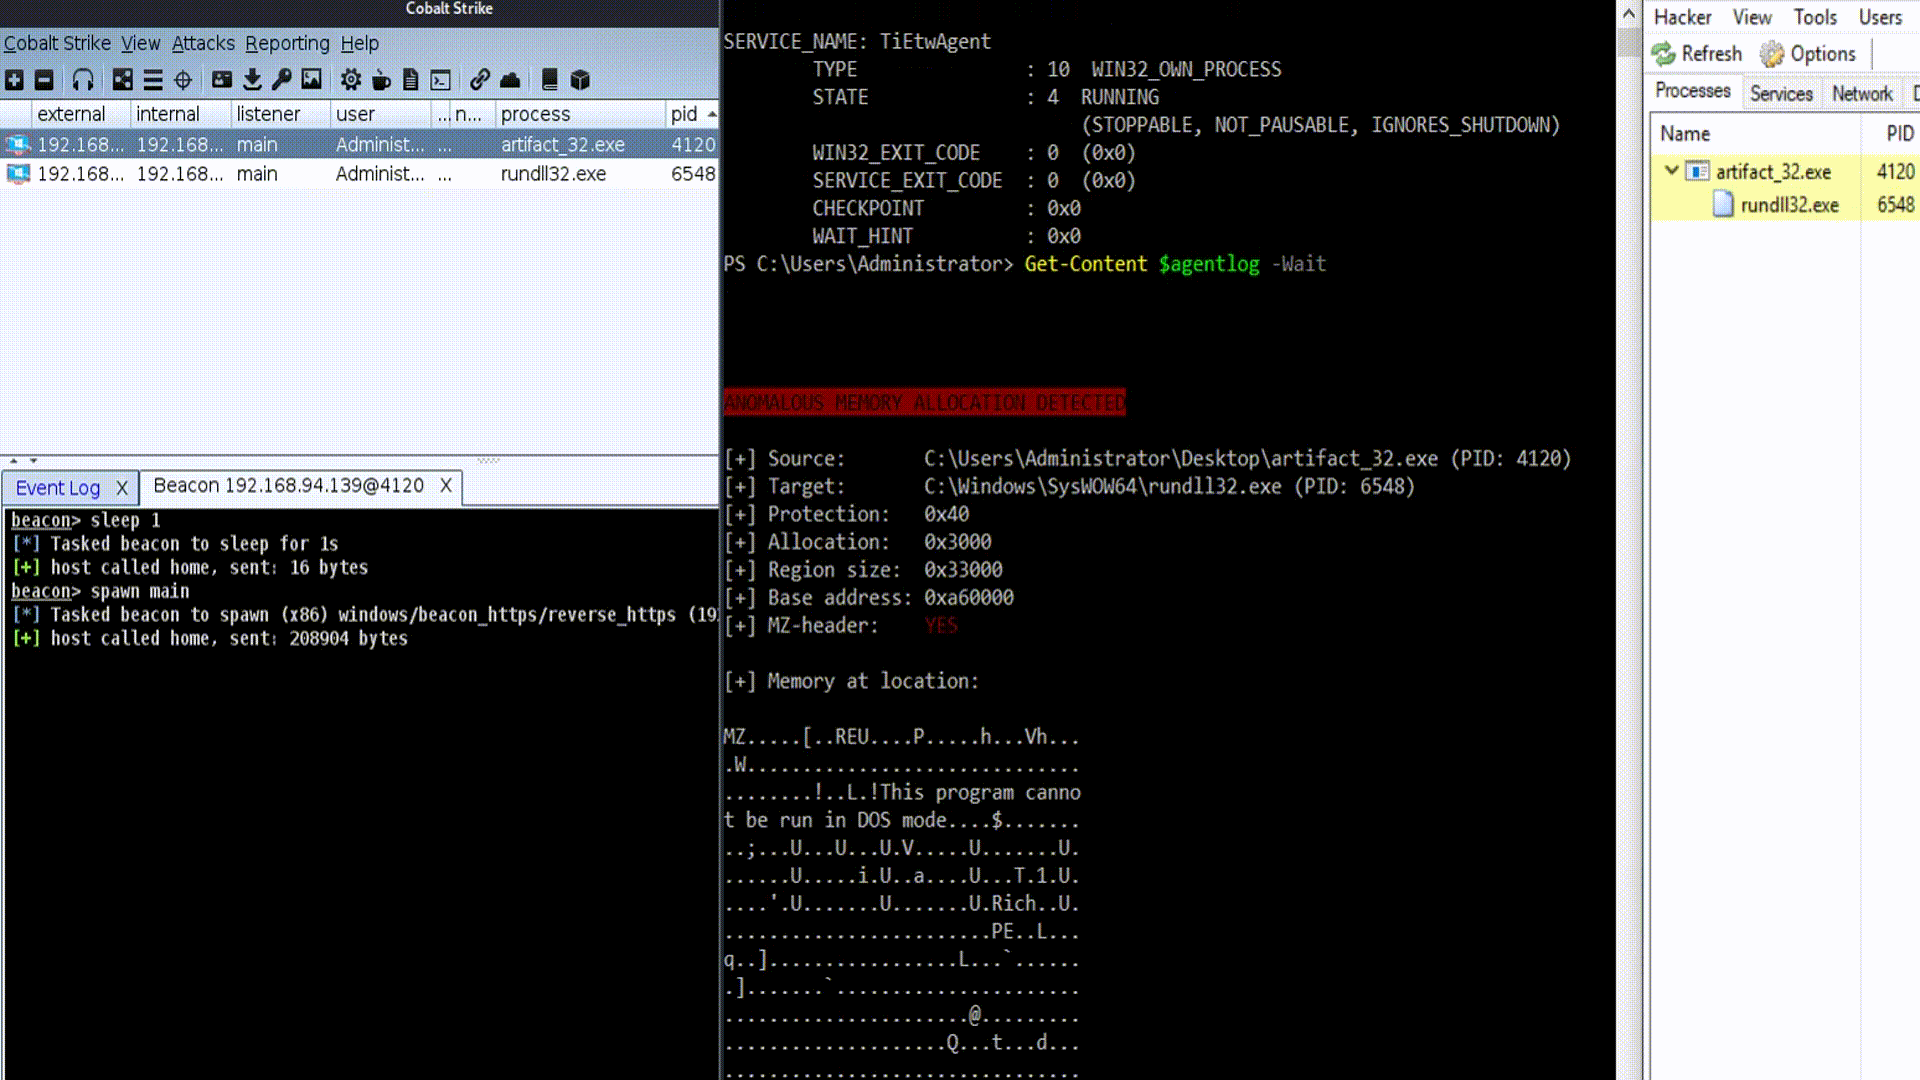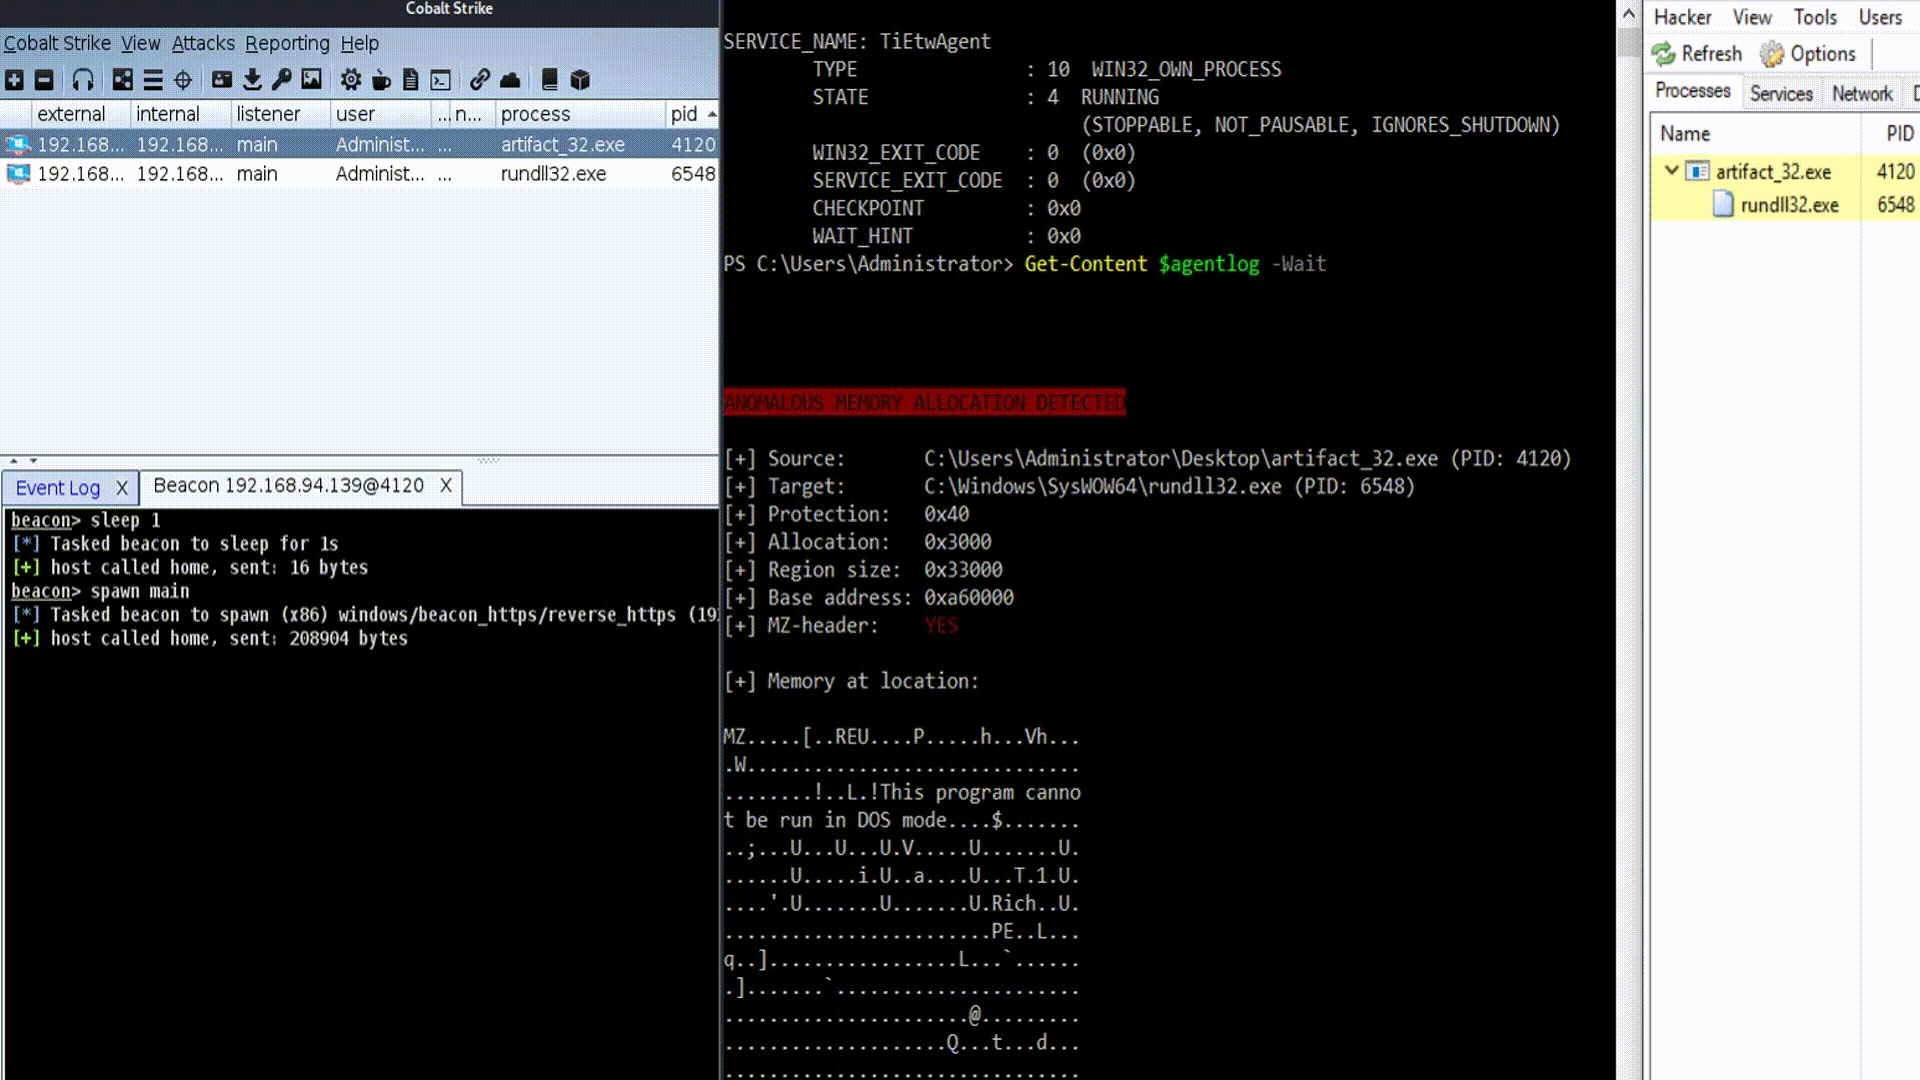 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
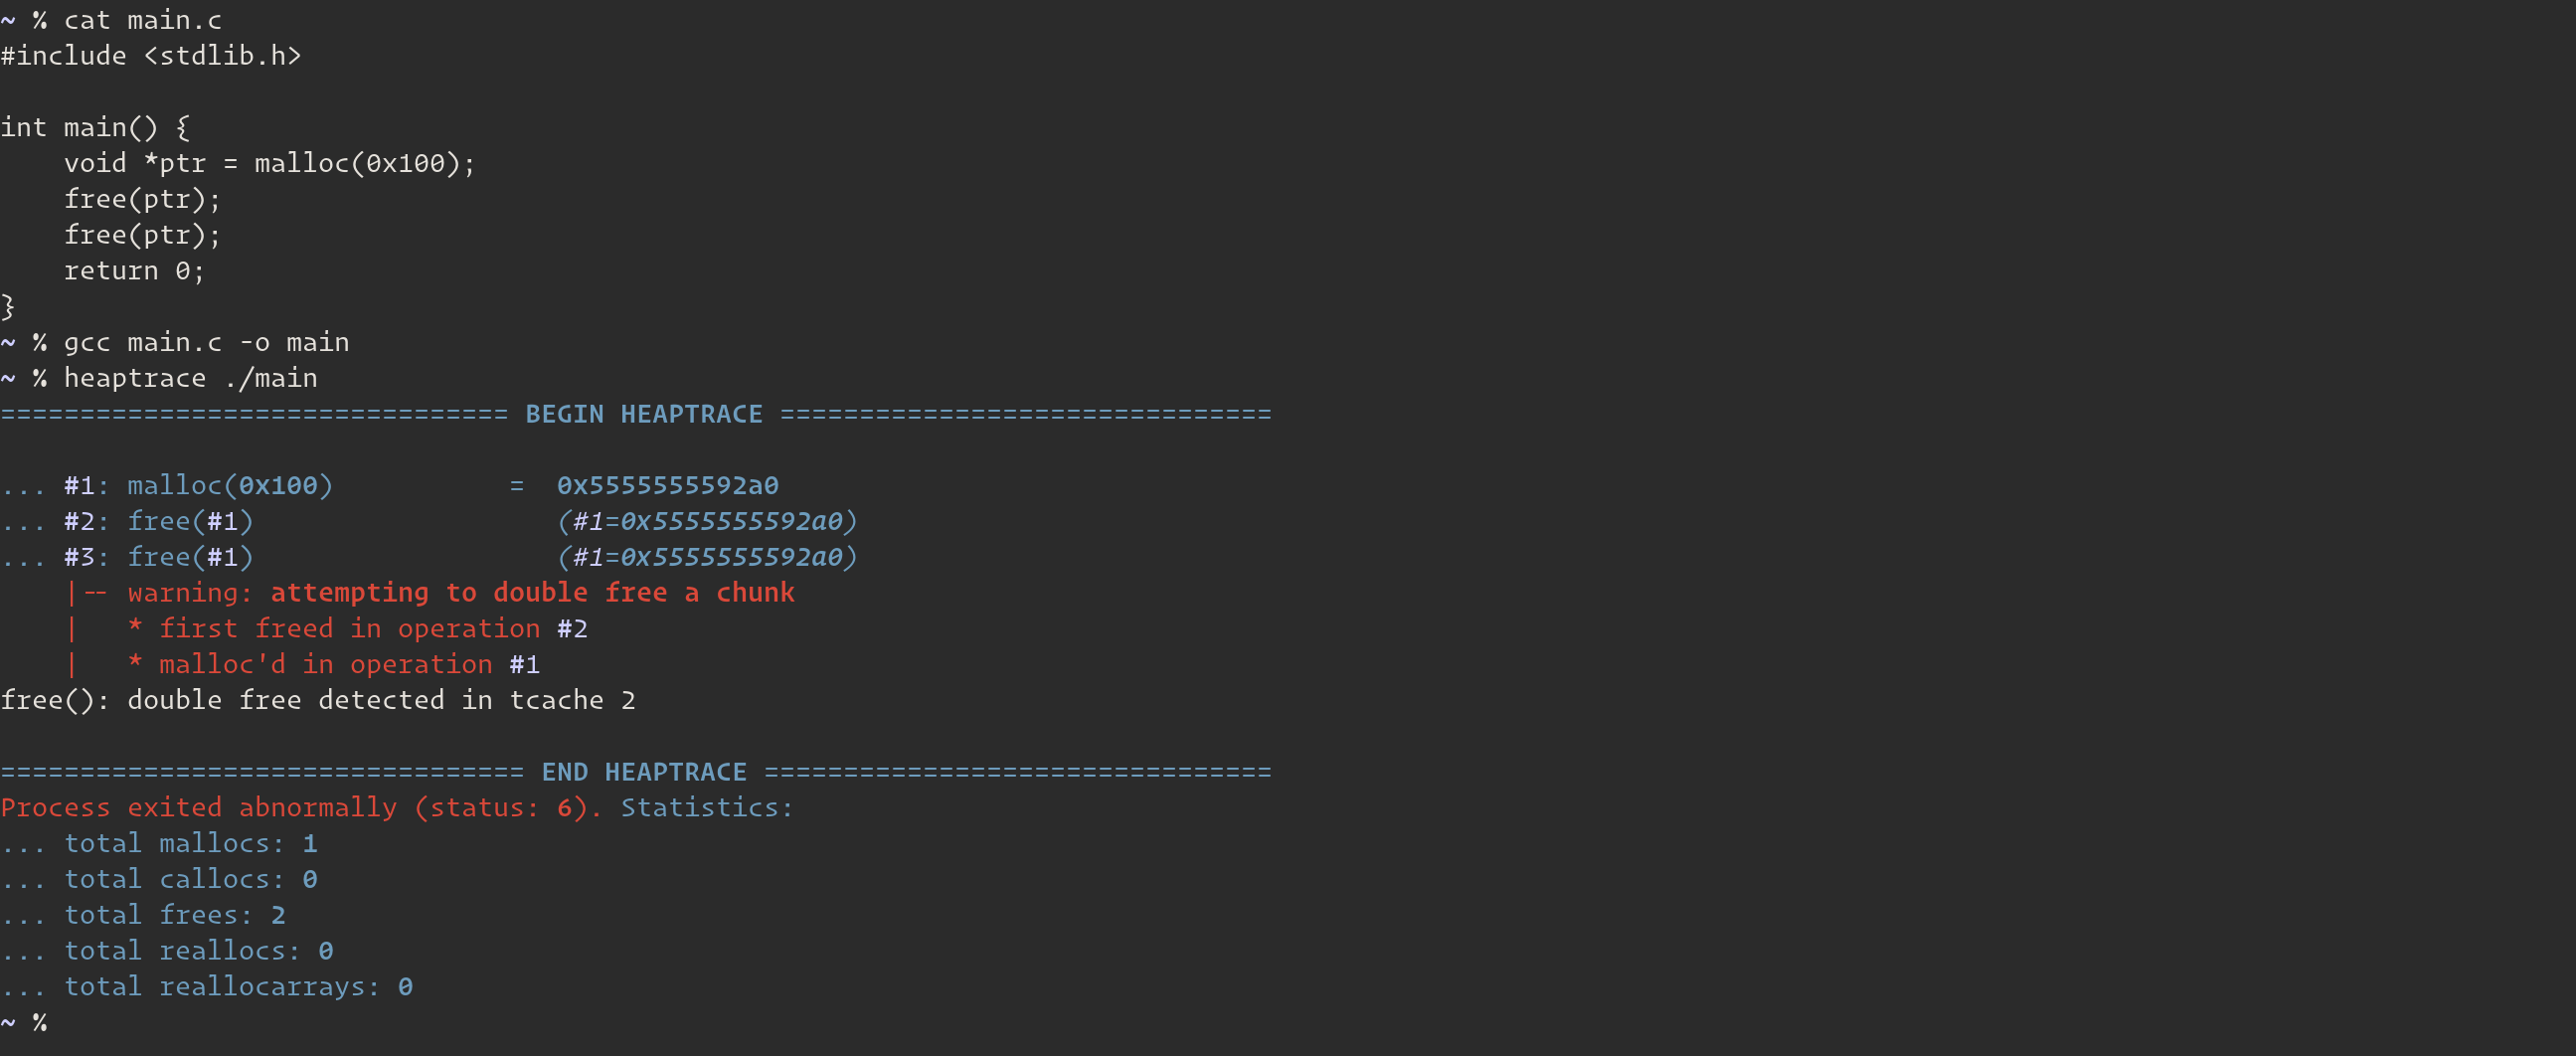 arinerron/heaptrace
helps visualize heap operations for pwn and debugging
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
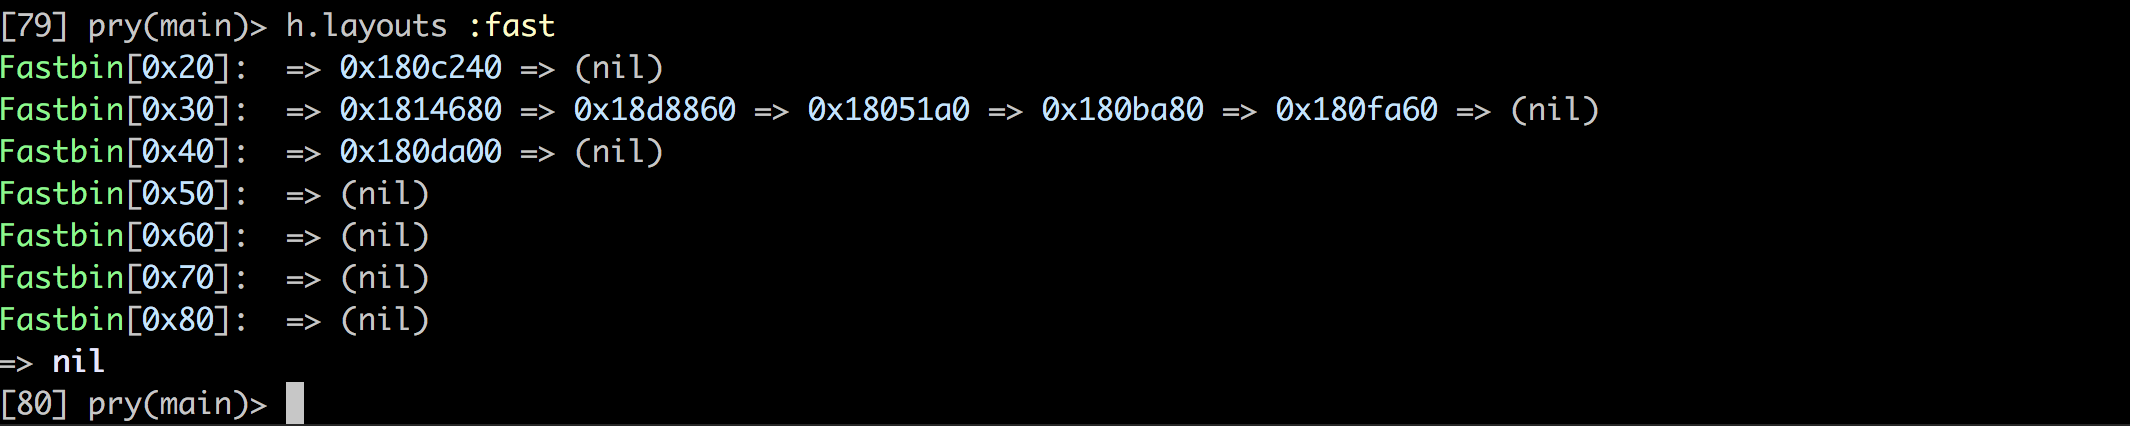 david942j/heapinfo
An interactive memory info for pwning / exploiting
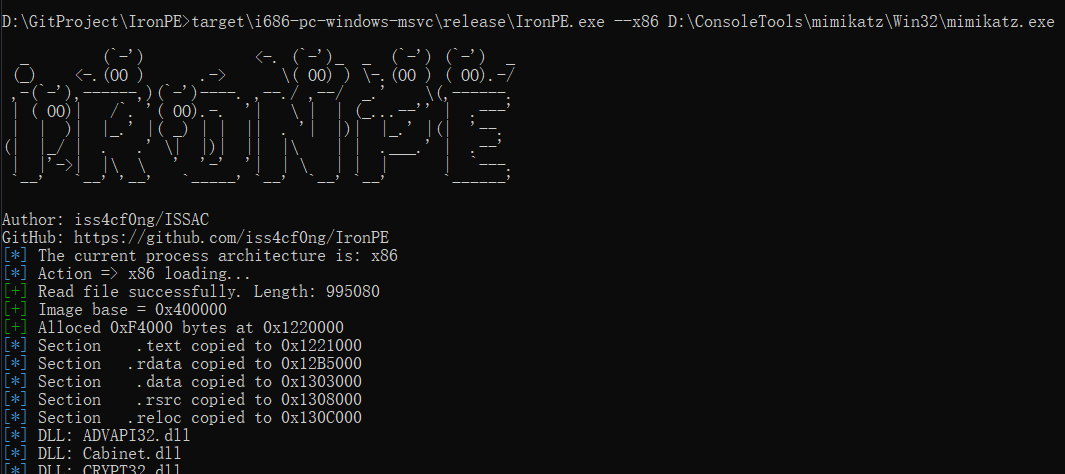 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome