

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
197 results
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

data-recoverydigital-forensicsdisk-forensics+7
3.4k
6 days ago
fibratus preview

fibratus

GitHubrabbitstack/fibratus

Security sensor for realtime threat detection and protection

defensive-toolsforensicsincident-response+3
2.5k3 days ago
jshookmcp preview

jshookmcp

GitHubvmoranv/jshookmcp

A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
ai-securitybinary-analysisdebuggers+9
2.1k12h 5m ago
mimikittenz preview

mimikittenz

GitHuborlyjamie/mimikittenz

A post-exploitation powershell tool for extracting juicy info from memory.
information-gatheringmemory-forensicspenetration-testing+1
1.9k6 years ago
drmemory preview

drmemory

GitHubdynamorio/drmemory

Memory Debugger for Windows, Linux, Mac, and Android
debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.7k10 months ago
mongobleed preview

mongobleed

GitHubjoe-desimone/mongobleed

Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
database-securityexploitationinformation-gathering+3
94310 months ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

digital-forensicsforensicsinformation-gathering+3
8567 years ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8075 months ago
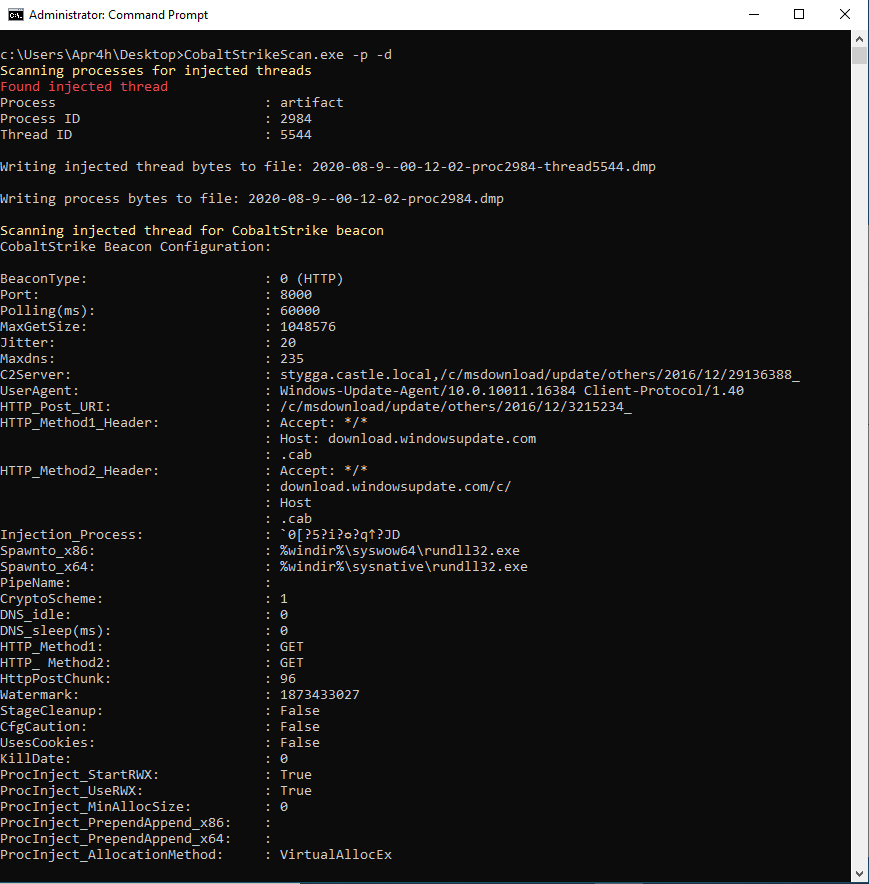
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9195 years ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6789 months ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5215 years ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
3041 month ago
XenoScan preview

XenoScan

GitHubnickcano/xenoscan

Open source memory scanner written in C++
binary-analysisdebuggersexploitation+2
3696 years ago
ghost preview

ghost

GitHubpandaadir05/ghost

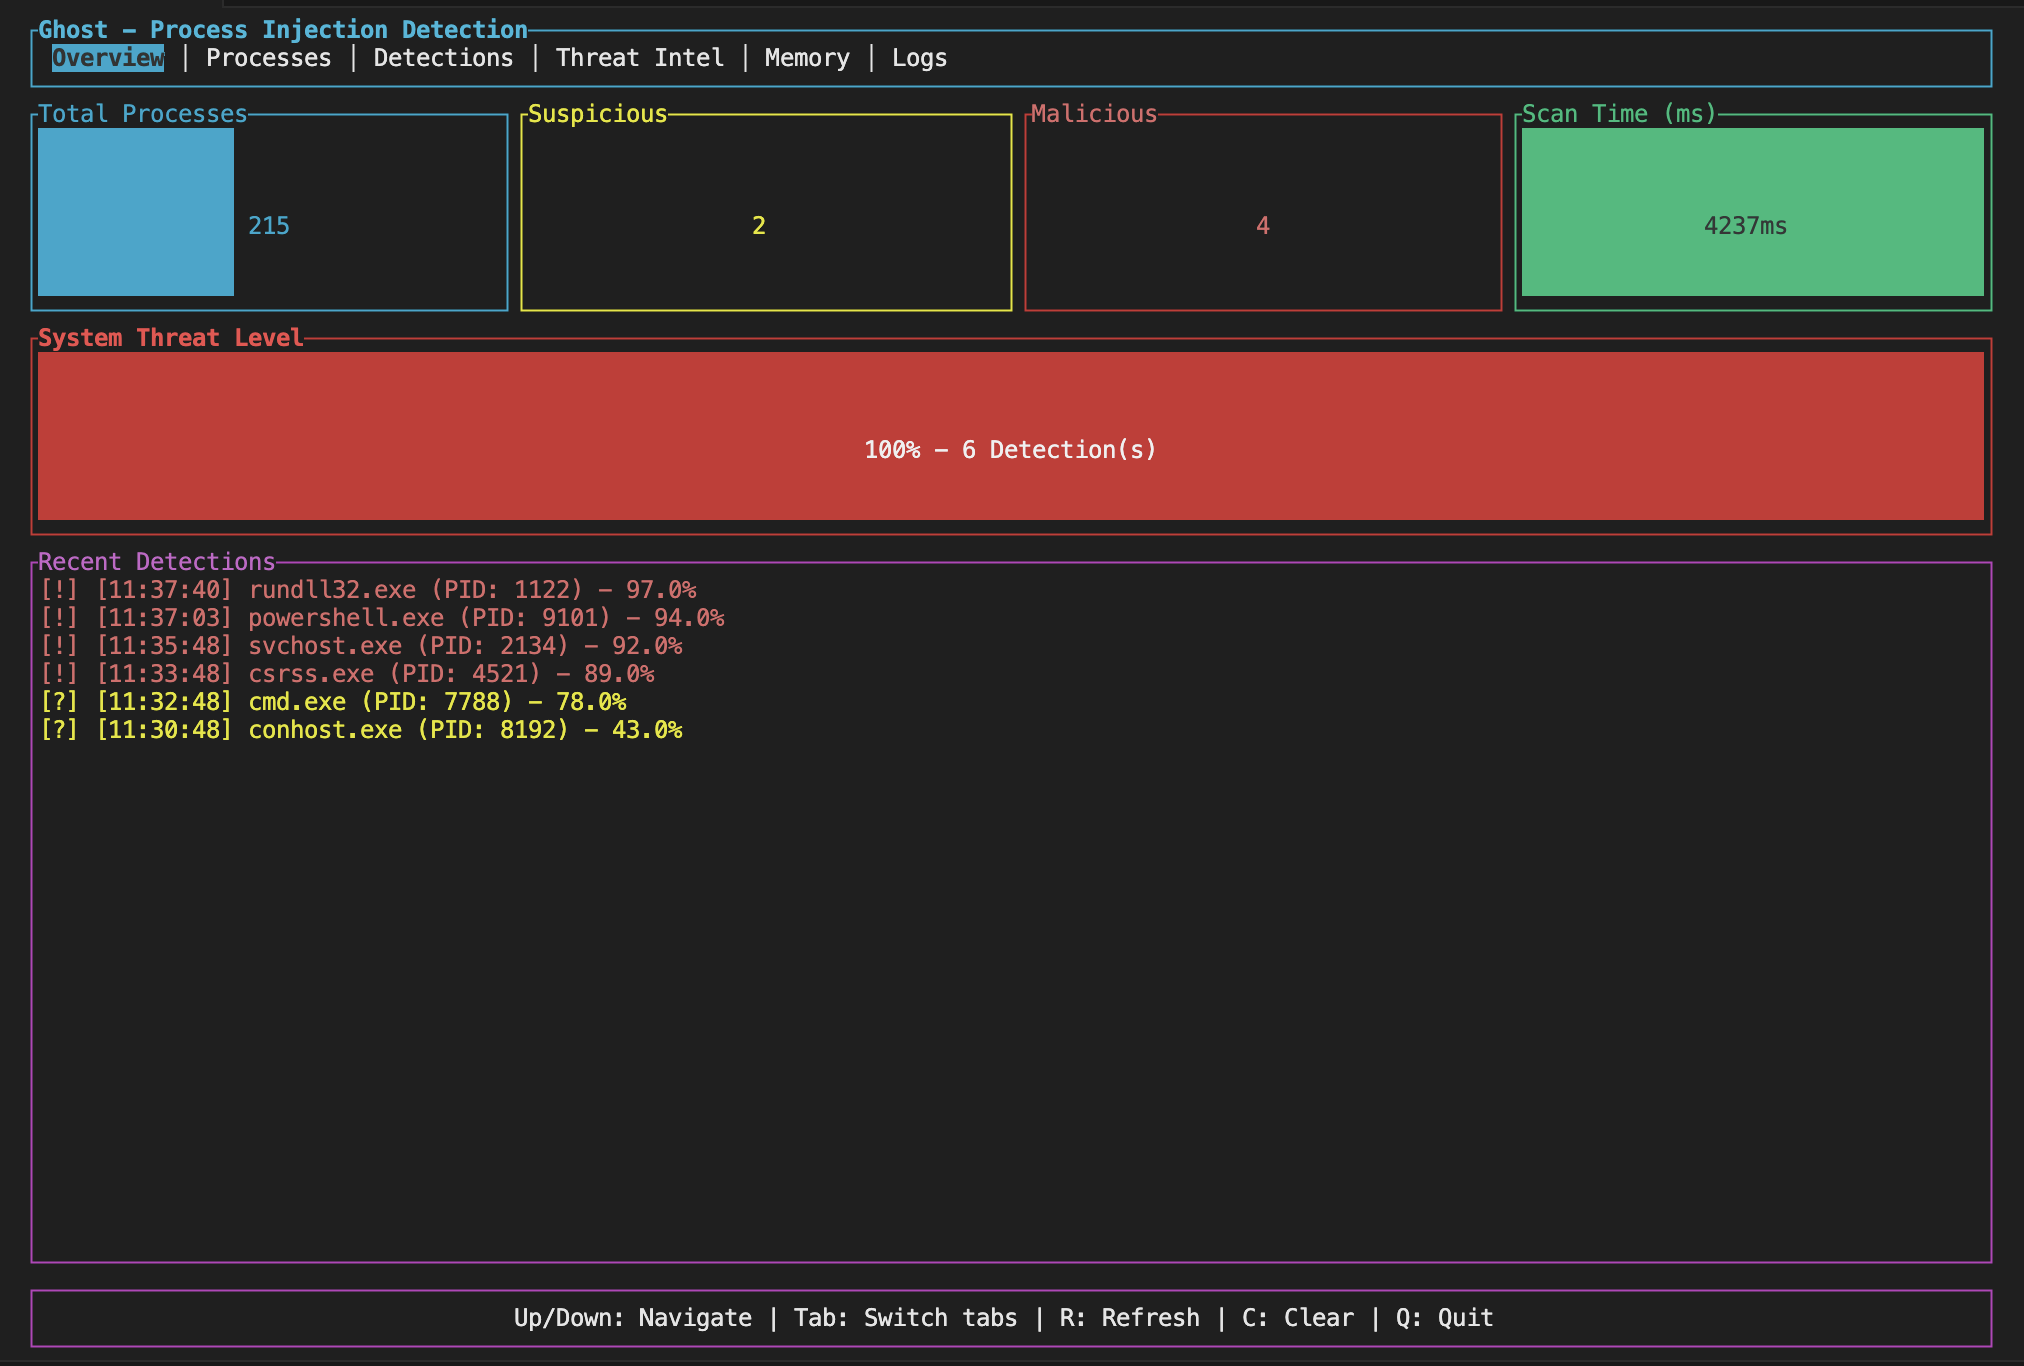
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3822 months ago
awesome-dfir-skills preview

awesome-dfir-skills

GitHubtsale/awesome-dfir-skills

A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
3215 months ago
dismember preview

dismember

GitHubliamg/dismember

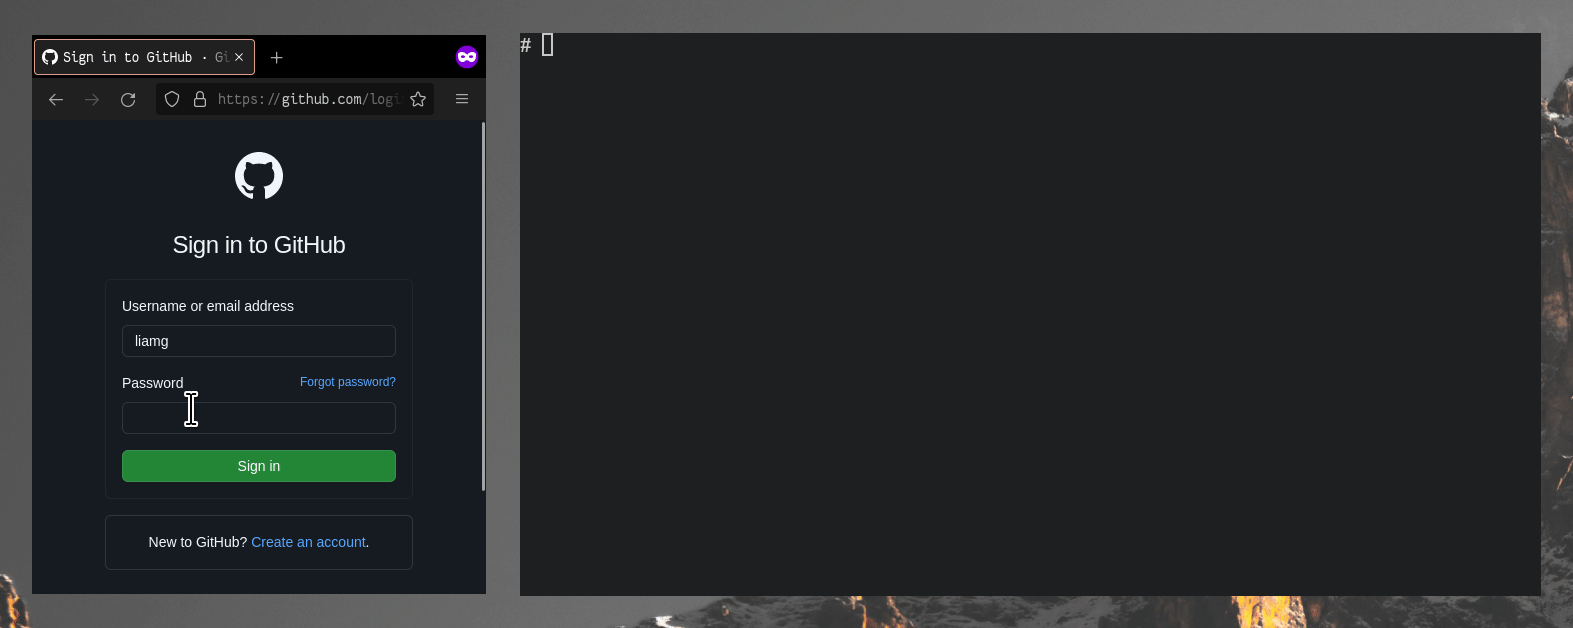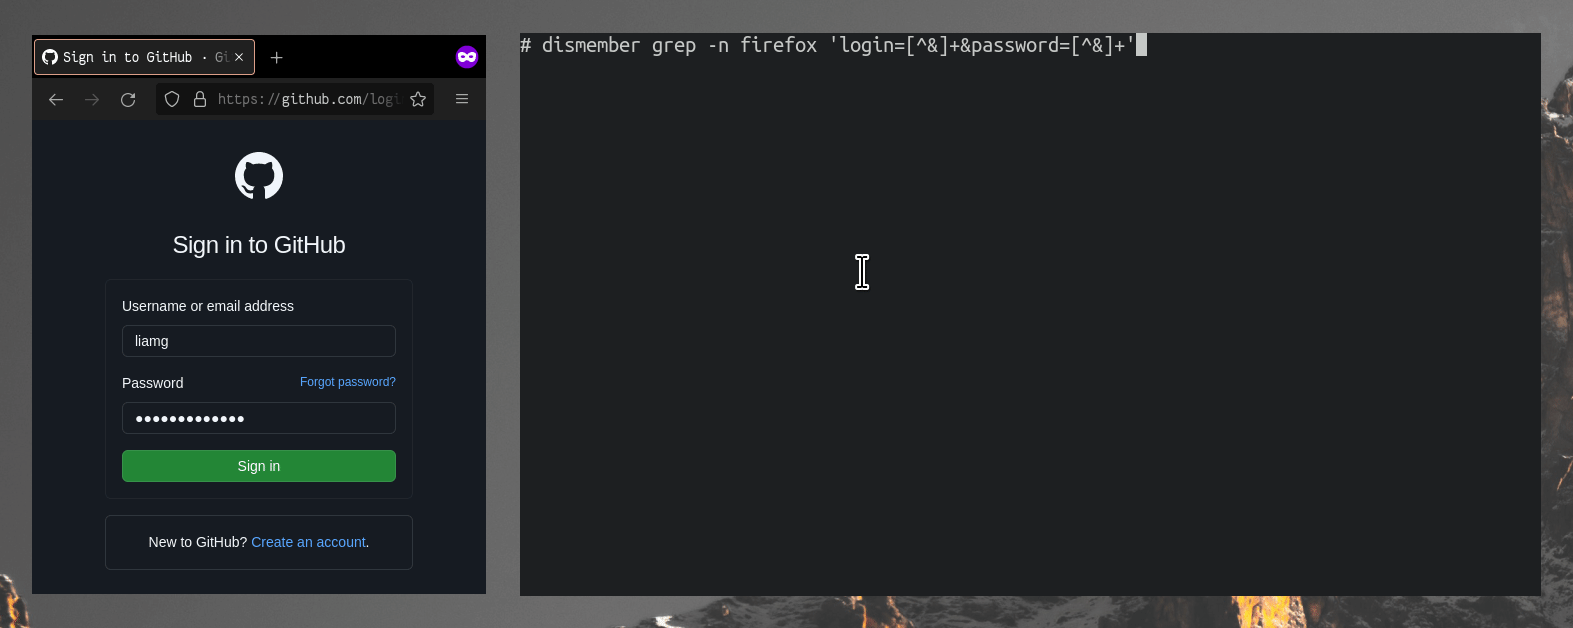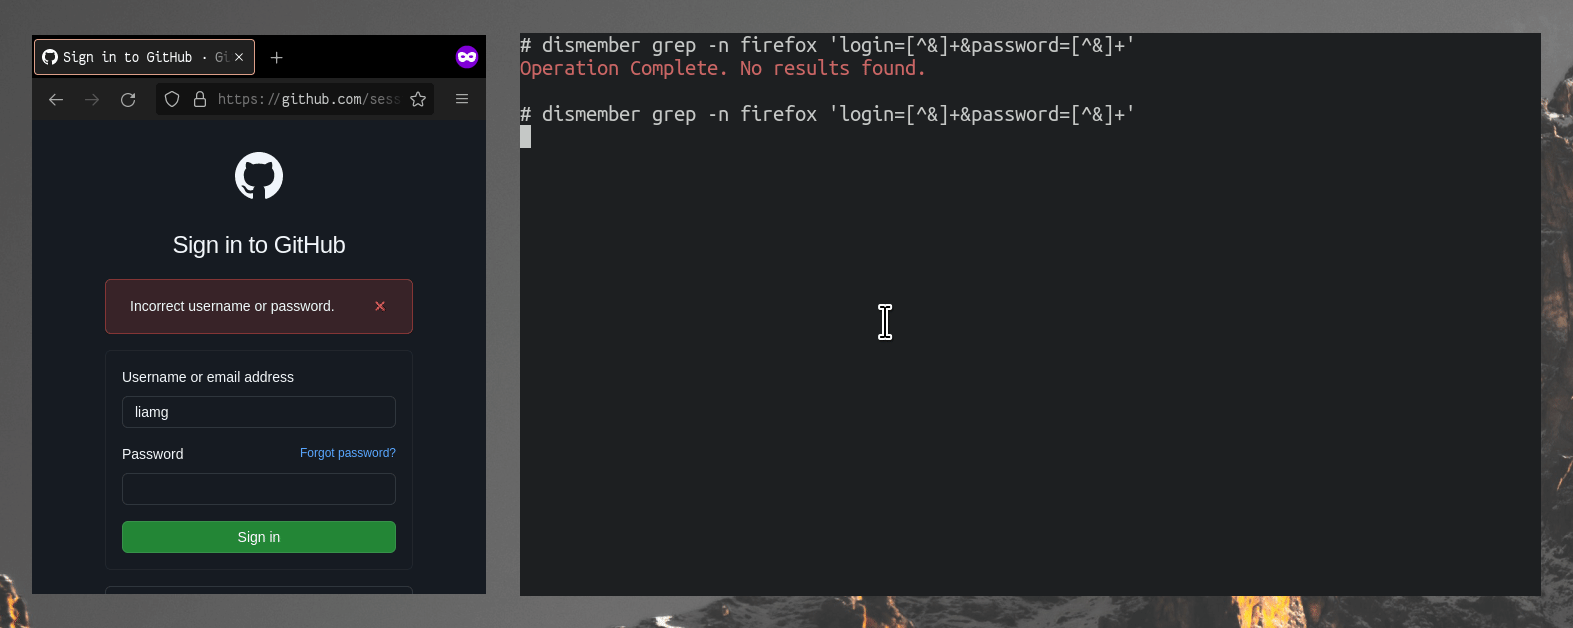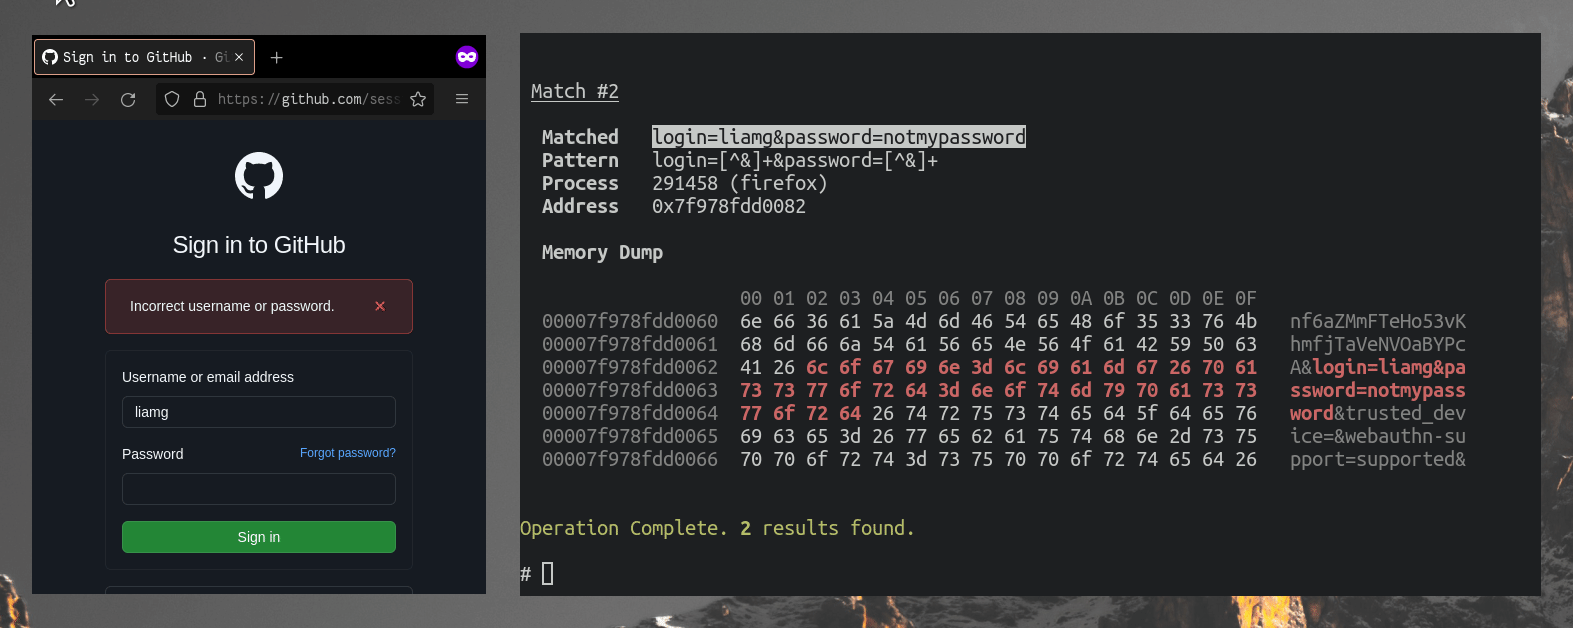
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
ctfforensicsinformation-gathering+2
6744 years ago
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecting & Hunting for IOCs with gusto and style
digital-forensicsforensicsincident-response+6
23820 days ago
CrossC2Kit preview

CrossC2Kit

GitHubcrossc2/crossc2kit

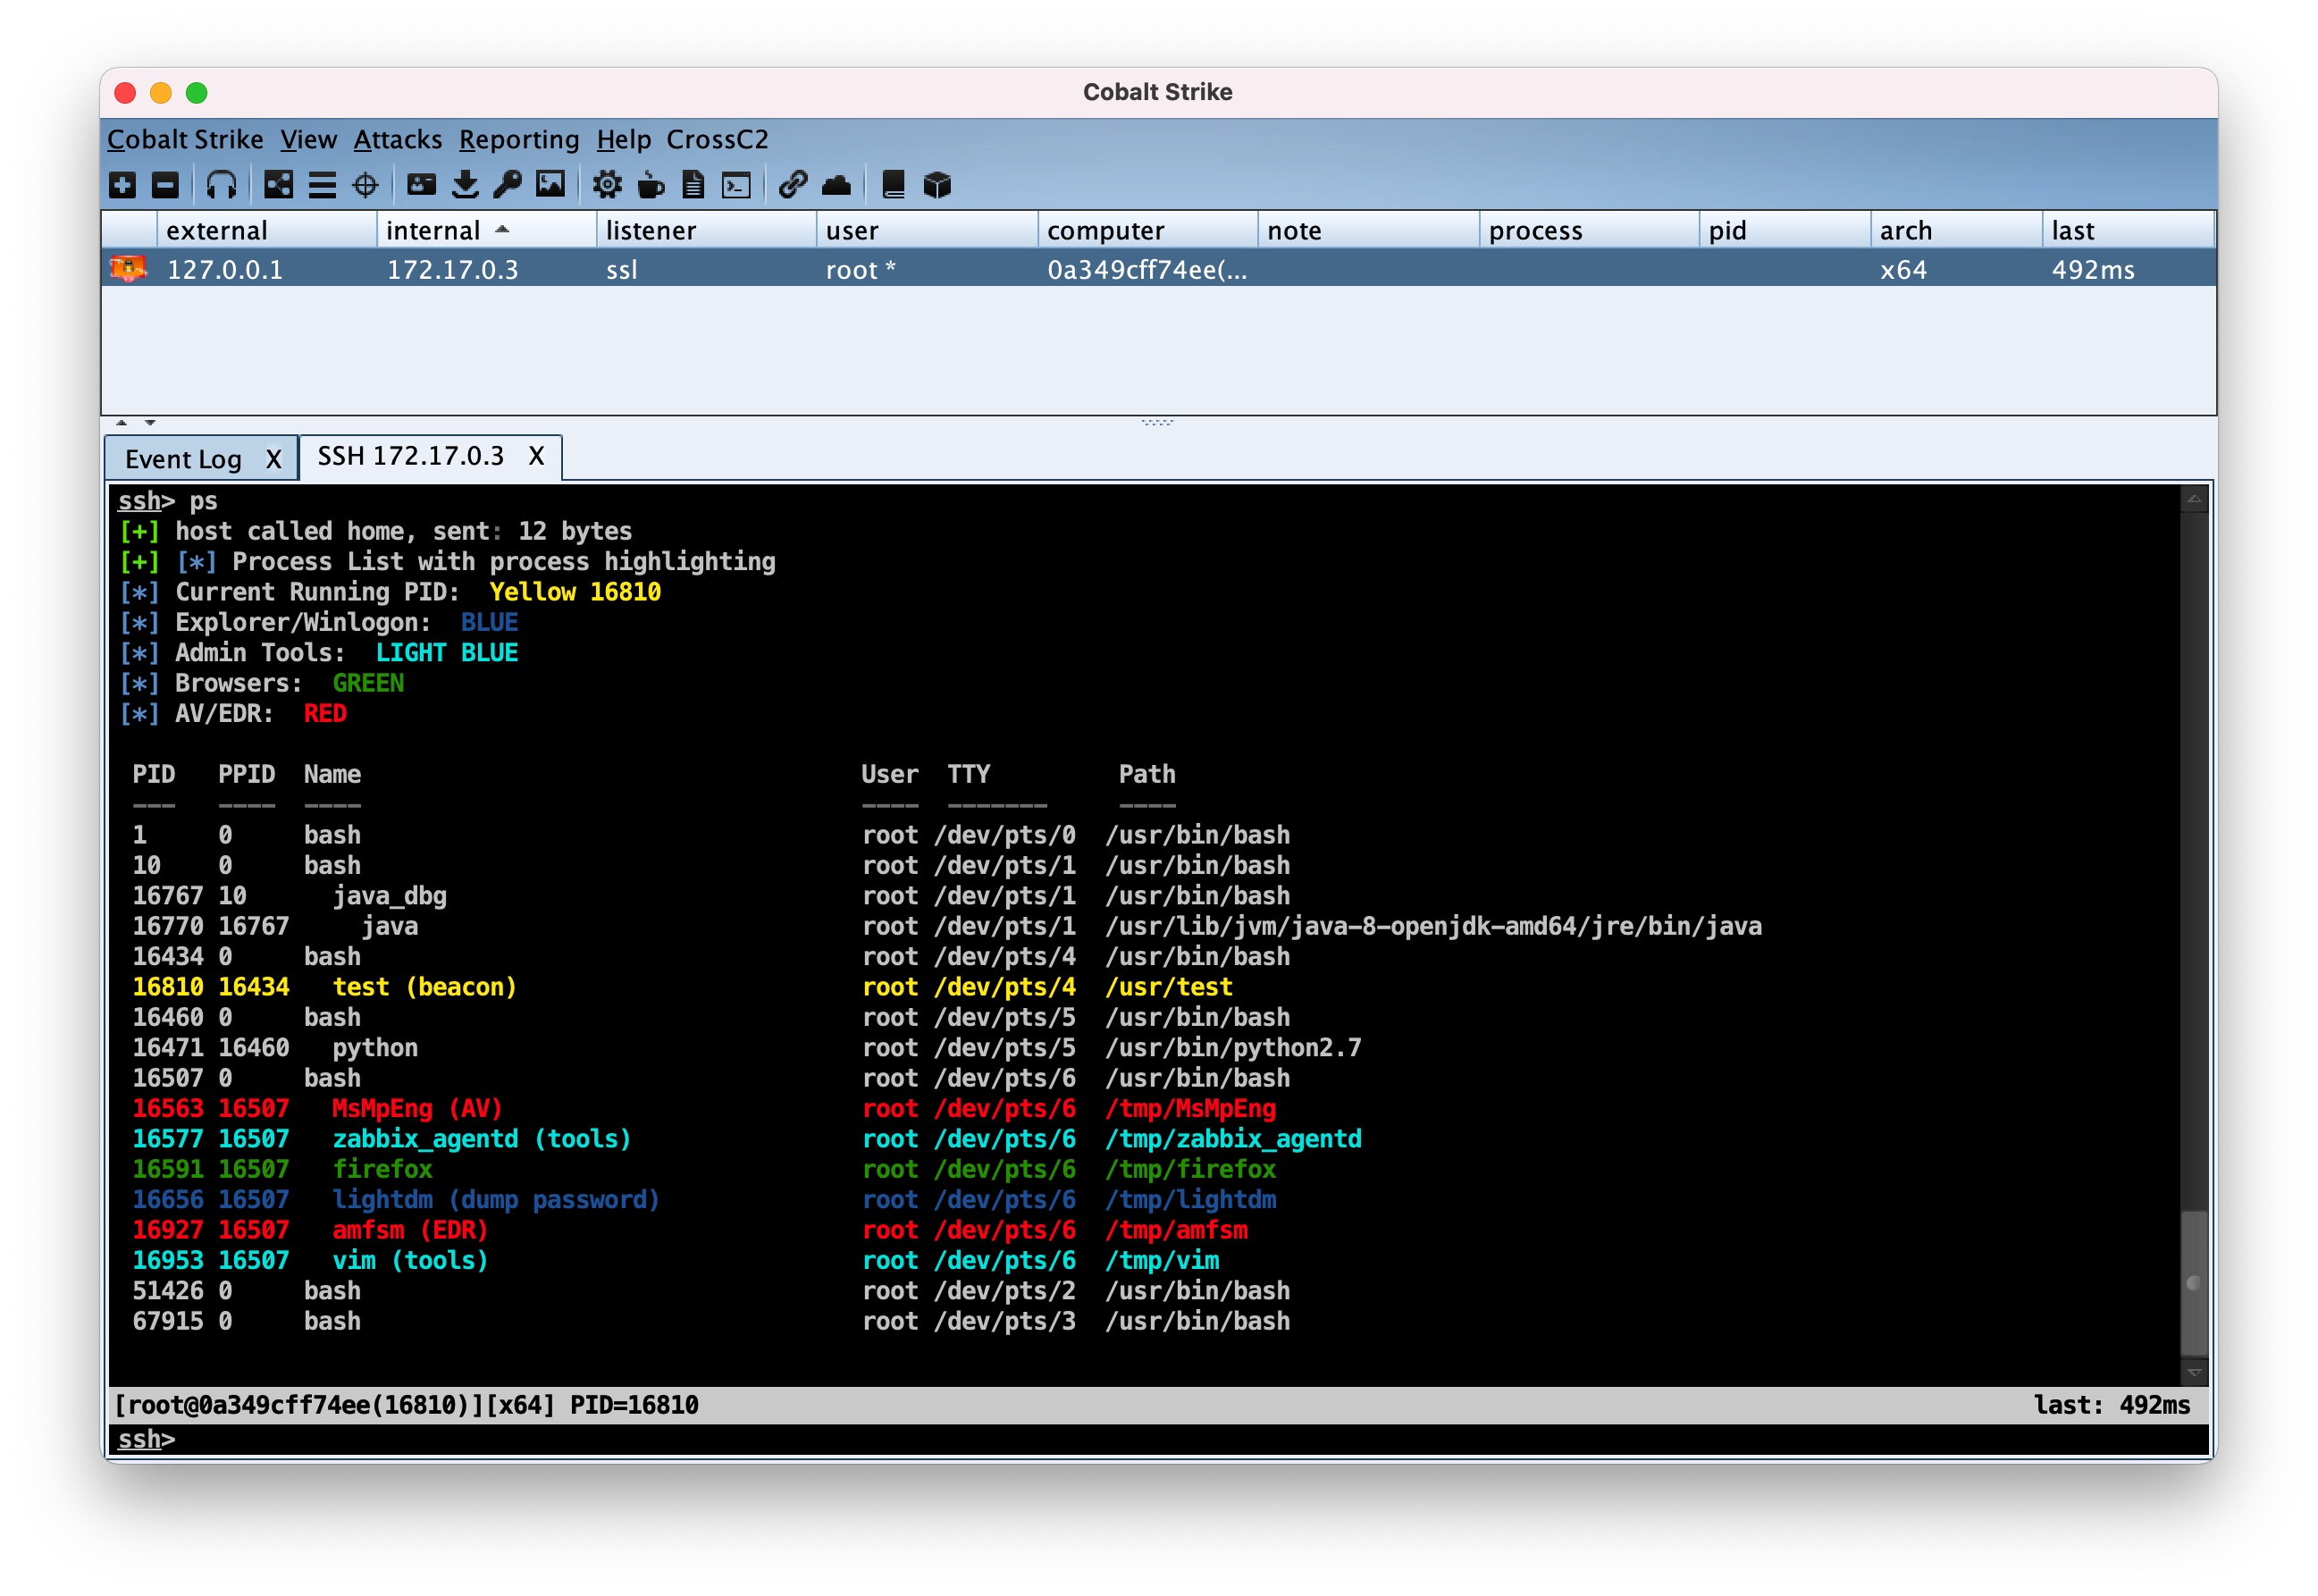
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

command-and-controlexploit-frameworksinformation-gathering+7
2293 years ago
Previous123…11Next