
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
104 results
inception preview

inception

GitHubcarmaa/inception

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
digital-forensicsexploitationhardware-security+6
1.6k
1 year ago
WinPmem preview

WinPmem

GitHubvelocidex/winpmem

The multi-platform memory acquisition tool.
digital-forensicsforensicsincident-response+1
1.1k11 months ago
extractTVpasswords preview

extractTVpasswords

GitHubvah13/extracttvpasswords

tool to extract passwords from TeamViewer memory using Frida

exploitationmemory-forensicspassword-cracking+3
4648 years ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8492 years ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5215 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk

android-securitybinary-analysismemory-forensics+2
43411 days ago
asatools preview

asatools

GitHubnccgroup/asatools

Main repository to pull all NCC Group Cisco ASA-related tool projects.
binary-analysisdebuggersembedded-systems-security+3
2398 years ago
dfirtriage preview

dfirtriage

GitHubtravisfoley/dfirtriage

Digital forensic acquisition tool for Windows based incident response.
digital-forensicsforensicsincident-response+1
3482 years ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
1267 years ago
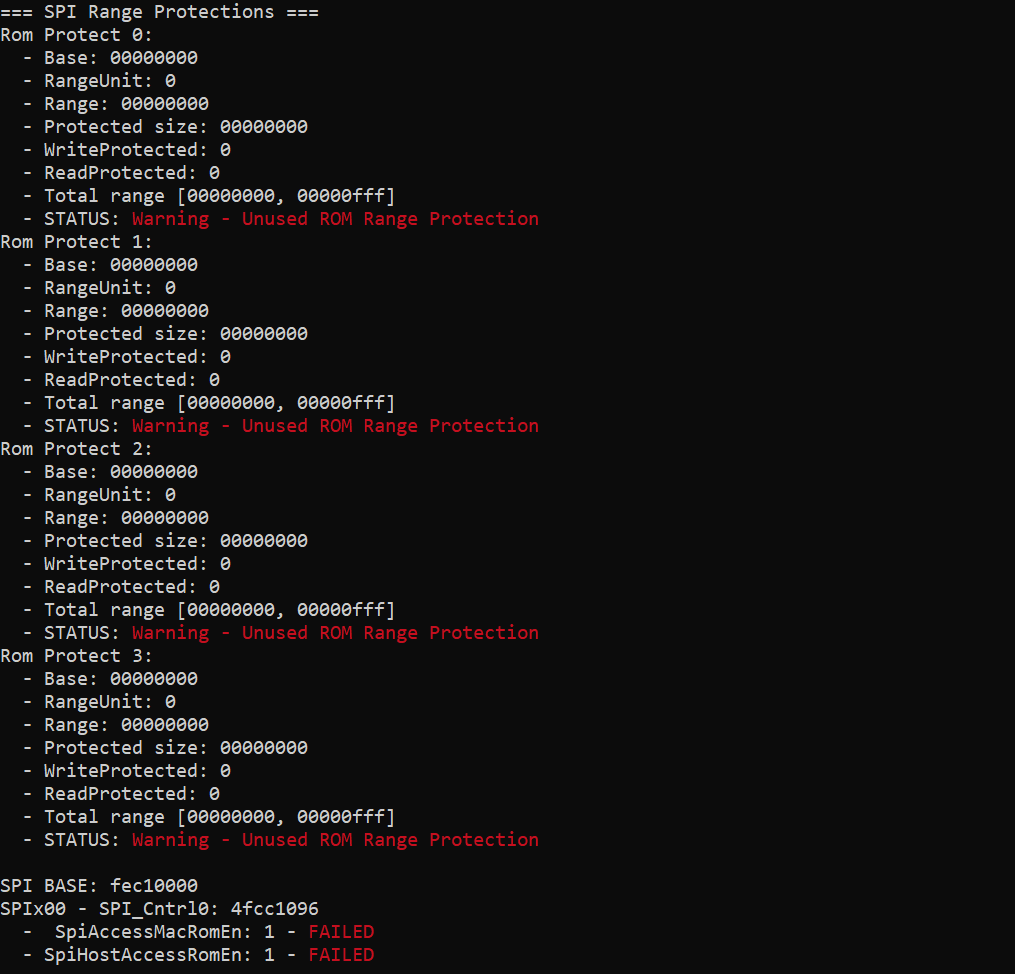
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
binary-analysisfirmware-analysisfuzzing+3
2221 year ago
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
memory-forensicspassword-attackspost-exploitation+1
2181 year ago
Squalr preview

Squalr

GitHubsqualr/squalr

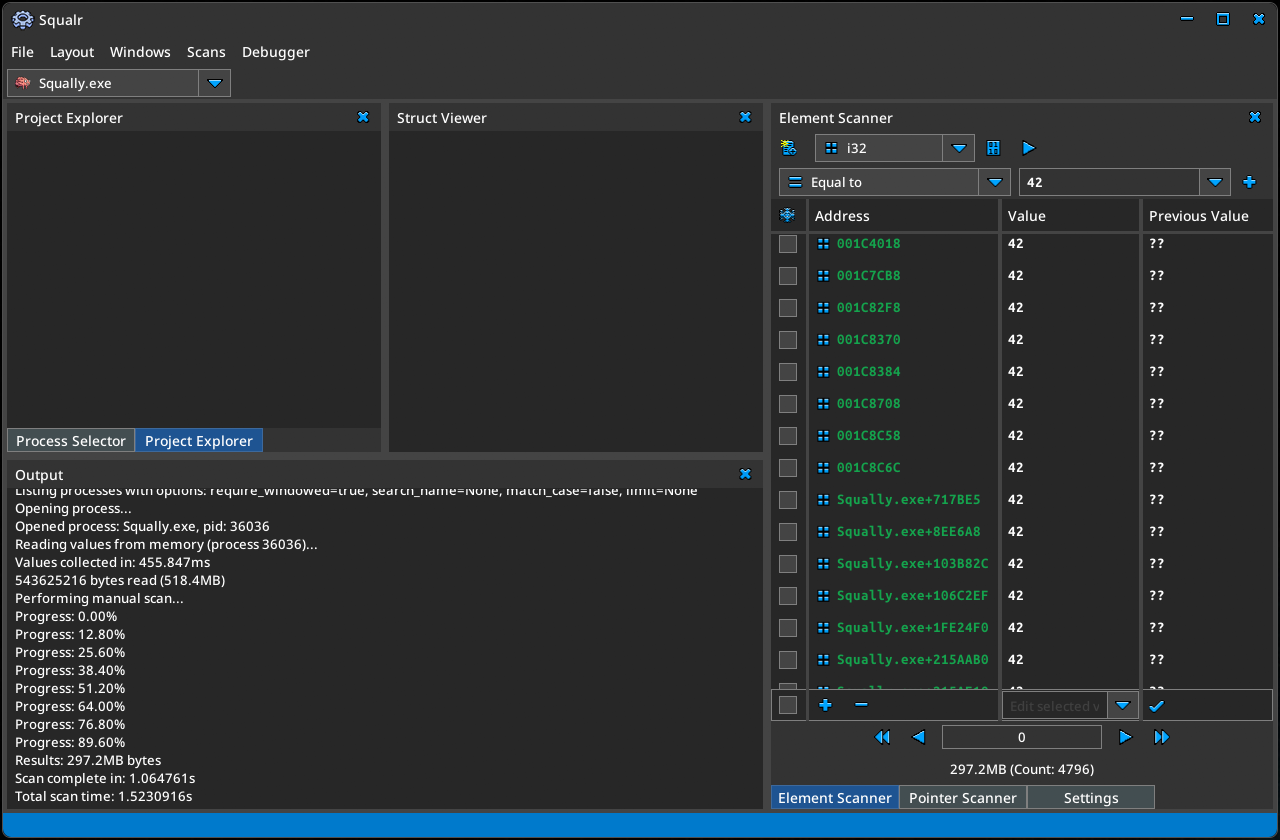
A generic game/software hacking tool written from the ground up in Rust.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
1803 months ago
ipa-medit preview

ipa-medit

GitHubsterrasec/ipa-medit

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

binary-analysisios-securitymemory-forensics+3
2111 year ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

anomaly-detectionbinary-analysisdefensive-tools+3
1654 years ago
AmdRyzenMasterCheat preview

AmdRyzenMasterCheat

GitHubekknod/amdryzenmastercheat

Exploit tool leveraging CVE-2020-12928 (AMD RyzenMaster driver) for game memory manipulation and anti-cheat bypass on Windows 10 with AMD Ryzen CPUs.
exploitationhardware-securitymemory-forensics+3
625 years ago
XBadManners preview

XBadManners

GitHubttffdd/xbadmanners

Tool for CVE-2018-16323

data-exfiltrationexploitationmemory-forensics+2
837 years ago
silph preview

silph

GitHubalmounah/silph

Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall

authenticationmemory-forensicspassword-cracking+3
1669 months ago
Previous123456Next