
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
162 results
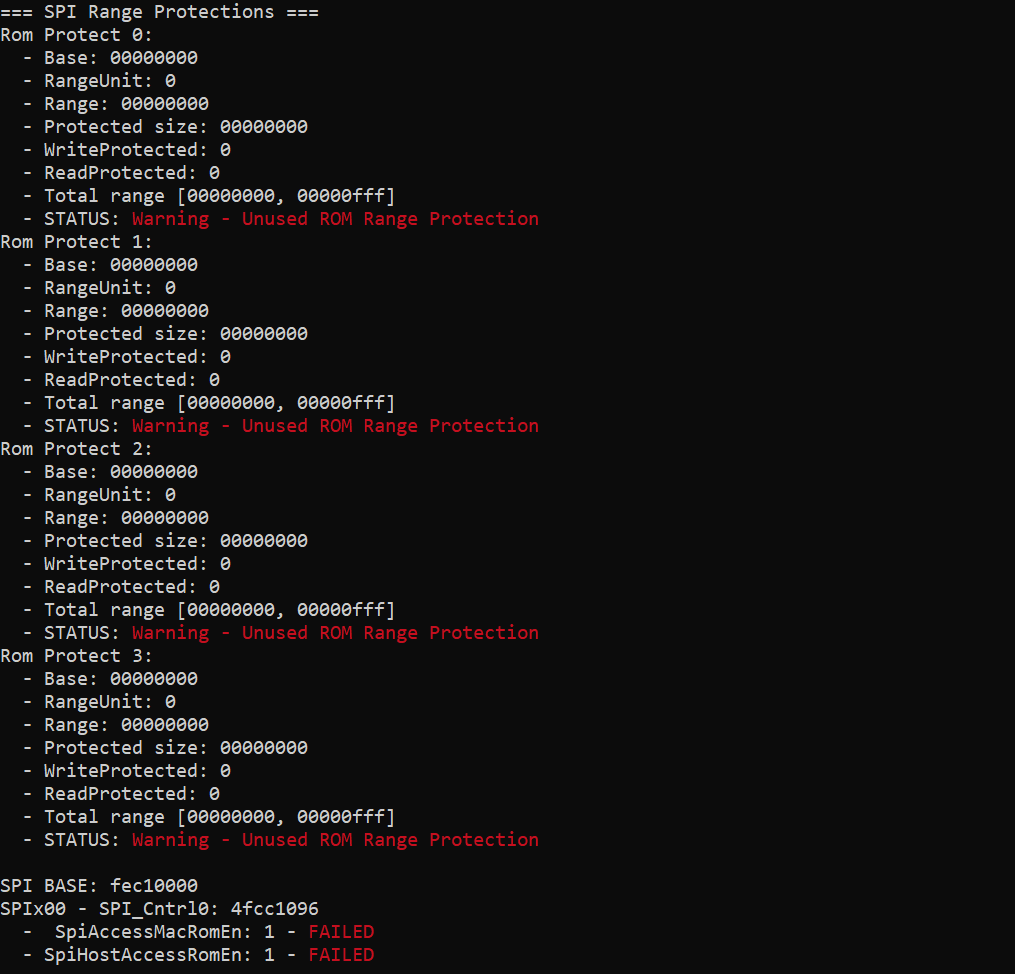
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
binary-analysisfirmware-analysisfuzzing+3
224
1 year ago
exploit-cve-2017-5715 preview

exploit-cve-2017-5715

GitHubopsxcq/exploit-cve-2017-5715

Spectre exploit
binary-exploitationexploitationhardware-security+3
548 years ago
rndis-co preview

rndis-co

GitHubszymonh/rndis-co

CVE-2022-25375 - Demo exploit of RNDIS USB Gadget
binary-exploitationexploitationhardware-security+2
84 years ago
CVE-2024-26817-amdkfd preview

CVE-2024-26817-amdkfd

GitHubmaherazzouzi/cve-2024-26817-amdkfd

Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
binary-exploitationexploitationhardware-security+2
72 years ago
cve-2023-31346-poc preview

cve-2023-31346-poc

GitHubfreax13/cve-2023-31346-poc

Proof-of-concept demonstrating memory leaks in AMD SEV-SNP firmware guest message headers and CPUID request, enabling extraction of sensitive guest…

binary-exploitationexploitationfirmware-analysis+3
13 years ago
gef preview

gef

GitHubhugsy/gef

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k2 months ago
zombieant preview

zombieant

GitHubdsnezhkov/zombieant

Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
memory-forensicspayload-developmentpost-exploitation+2
2267 years ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
1901 month ago
LiMEaide preview

LiMEaide

GitHubkd8bny/limeaide

A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.

digital-forensicsforensicsmemory-forensics
1577 years ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1212 years ago
umbra preview

umbra

GitHubymsniper/umbra

External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…

exploitationmemory-forensicsred-teaming+1
1816 days ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
253 months ago
security checks preview

security checks

GitLababdom.seada/security-checks

linux security checks

configuration-auditingdefensive-toolsdigital-forensics+8
7 months ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.5k10 days ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool
debuggersdynamic-analysis-sandboxingincident-response+2
3.1k6 days ago
drmemory preview

drmemory

GitHubdynamorio/drmemory

Memory Debugger for Windows, Linux, Mac, and Android

debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.8k10 months ago
LiME preview

LiME

GitHubjtsylve/lime

Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.

digital-forensicsforensicsincident-response+2
2.1k6 months ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…

digital-forensicsforensicsincident-response+1
1.1k2 days ago
Previous123…9Next