
CVE-2019-2215
 atorninja/cve-2019-2215
PoC and analysis of CVE-2019-2215, a use-after-free in Android Binder, with kernel instrumentation and exploit tuning for affected Samsung devices.
android-securitybinary-exploitationexploitation+2
4
atorninja/cve-2019-2215PoC and analysis of CVE-2019-2215, a use-after-free in Android Binder, with kernel instrumentation and exploit tuning for affected Samsung devices.
 imeiplus/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
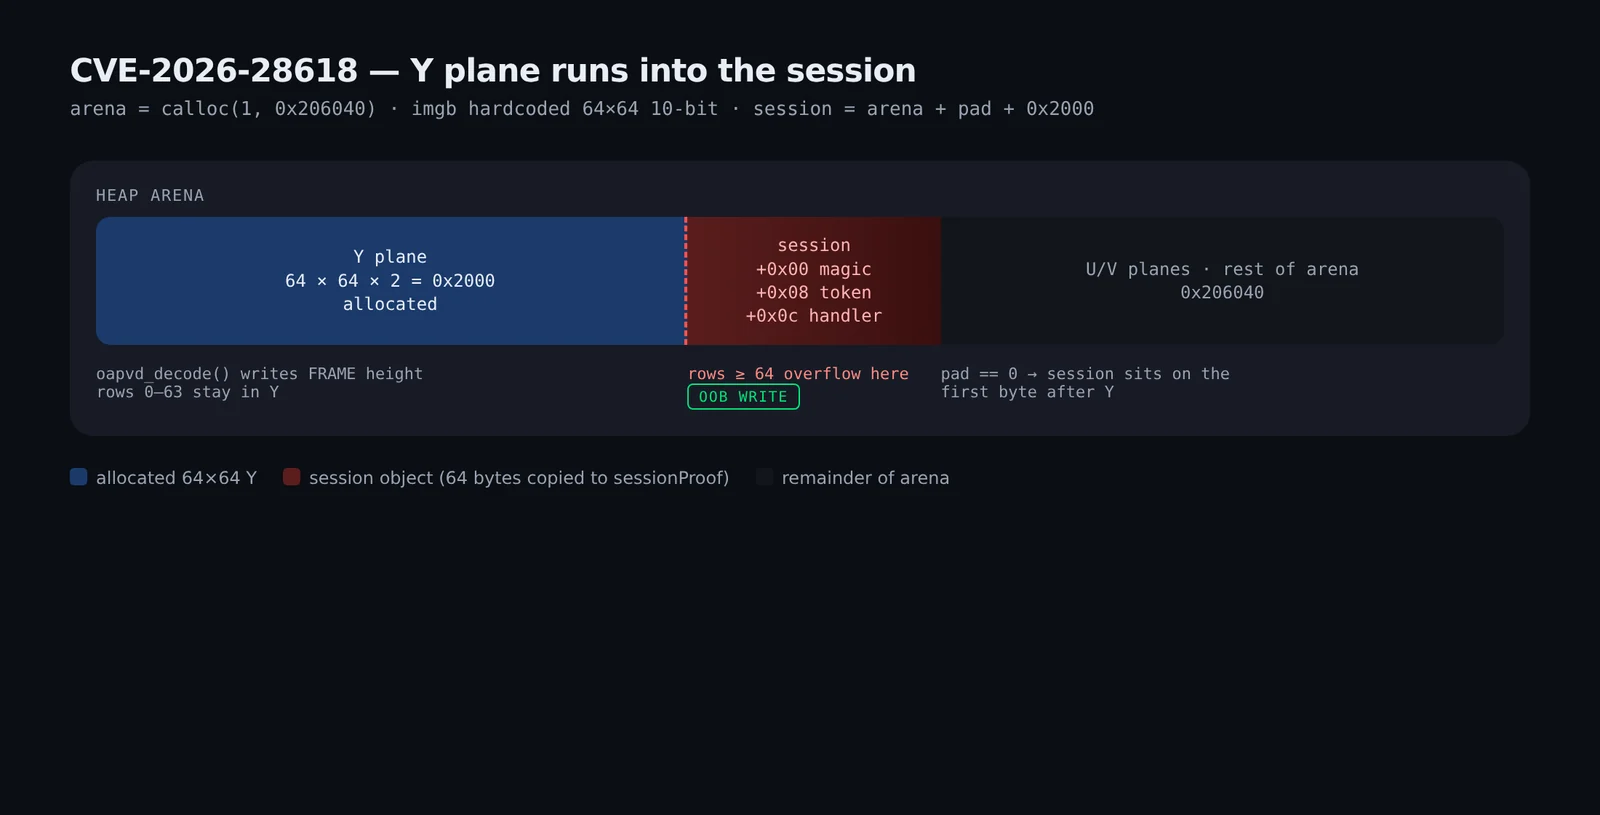 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 x3ero0/android712-blueborne
Android Blueborne RCE CVE-2017-0781
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 m4g1xx/cve-2024-36971
Poc for CVE-2024-36971
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 natleoj/cve-2019-11933
Heap corruption in WhatsApp's media picker
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
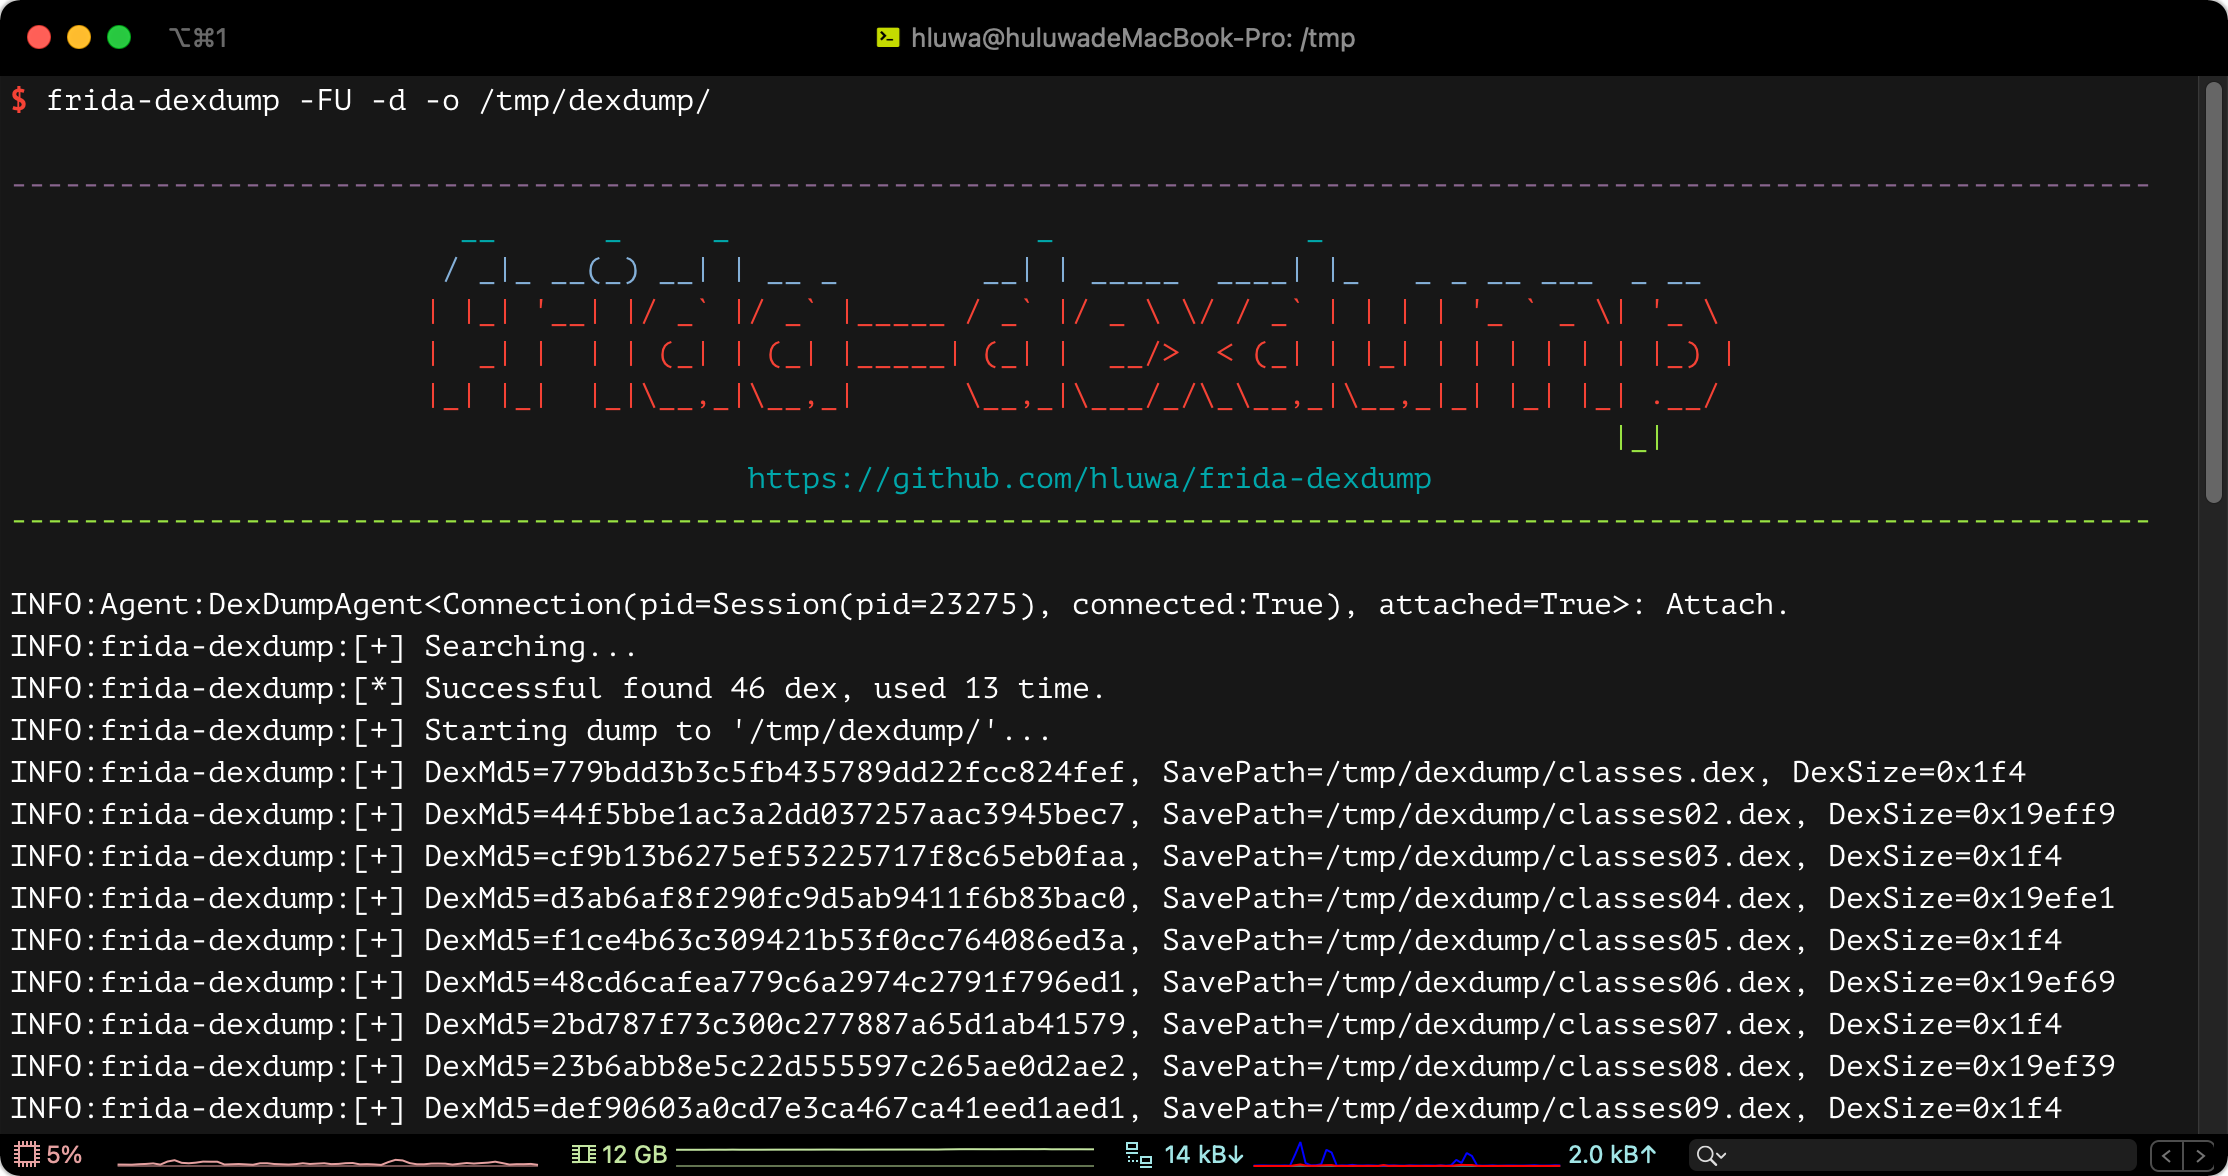 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.